Introduction
簡介
After completing this activity, you will know how to configure a Cisco Catalyst 9800 WLC to use WPA2 PSK for its existing open wireless network and how to verify the secure wireless network connection.
完成此活動後,您將了解如何設定 Cisco Catalyst 9800 WLC,讓其現有的開放式無線網路使用 WPA2 PSK,以及如何驗證安全的無線網路連線。
Topology
拓樸
Job Aid
工作輔助資料
Device Information
裝置資訊
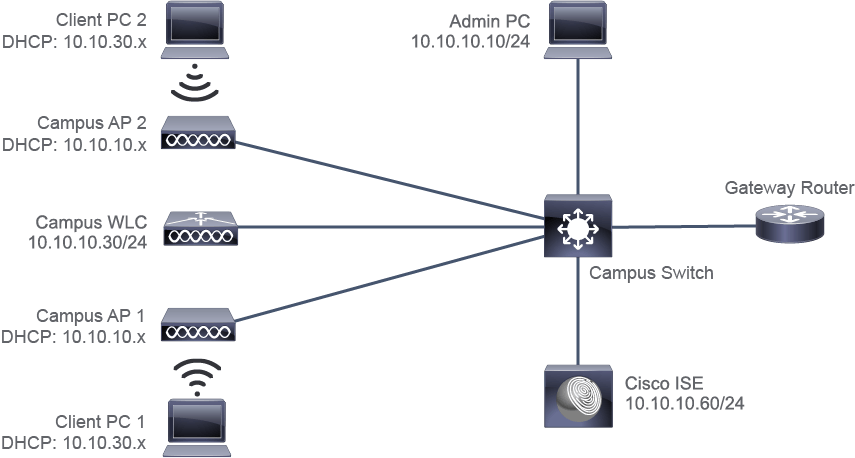
Device 裝置 | Username/Password 使用者名稱/密碼 | Management IP Address 管理 IP 位址 | Employee Network (VLAN 30, WLAN employee) IP Addresses 員工網路(VLAN 30,WLAN employee)IP 位址 |
Admin PC Admin PC | 10.10.10.10/24 10.10.10.10/24 | ||
Client PC 1 Client PC 1 | DHCP: 10.10.30.x/24 DHCP:10.10.30.x/24 | ||
Client PC 2 Client PC 2 | DHCP: 10.10.30.x/24 DHCP:10.10.30.x/24 | ||
Campus WLC Campus WLC | admin/1234QWer admin/1234QWer | 10.10.10.30/24 10.10.10.30/24 | 10.10.30.30/24 10.10.30.30/24 |
Campus AP 1 Campus AP 1 | DHCP: 10.10.10.x/24 DHCP:10.10.10.x/24 | ||
Campus AP 2 Campus AP 2 | DHCP: 10.10.10.x/24 DHCP:10.10.10.x/24 | ||
Cisco ISE Cisco ISE | 10.10.10.60/24 10.10.10.60/24 | ||
Gateway Router Gateway Router | 10.10.10.1/24 10.10.10.1/24 | 10.10.30.1/24 10.10.30.1/24 |
Task 1: Configure a WLAN to Use WPA2 PSK
任務 1:設定 WLAN 使用 WPA2 PSK
WPA2 provides a framework for authentication and encryption services in wireless networks.
WPA2 為無線網路提供驗證與加密服務的框架。
You will configure a Cisco Catalyst 9800 WLC to change an existing open (unauthenticated) WLAN to use WPA2 PSK using the WLC GUI.
您將使用 WLC GUI 設定 Cisco Catalyst 9800 WLC,將現有的開放式(未驗證)WLAN 改為使用 WPA2 PSK。
Activity
活動
Click the Play icon in the middle of the screen or the Play button on the player below the simulation screen to begin the simulation.
按一下畫面中央的 Play 圖示,或按一下模擬畫面下方播放器上的 Play 按鈕,開始模擬。
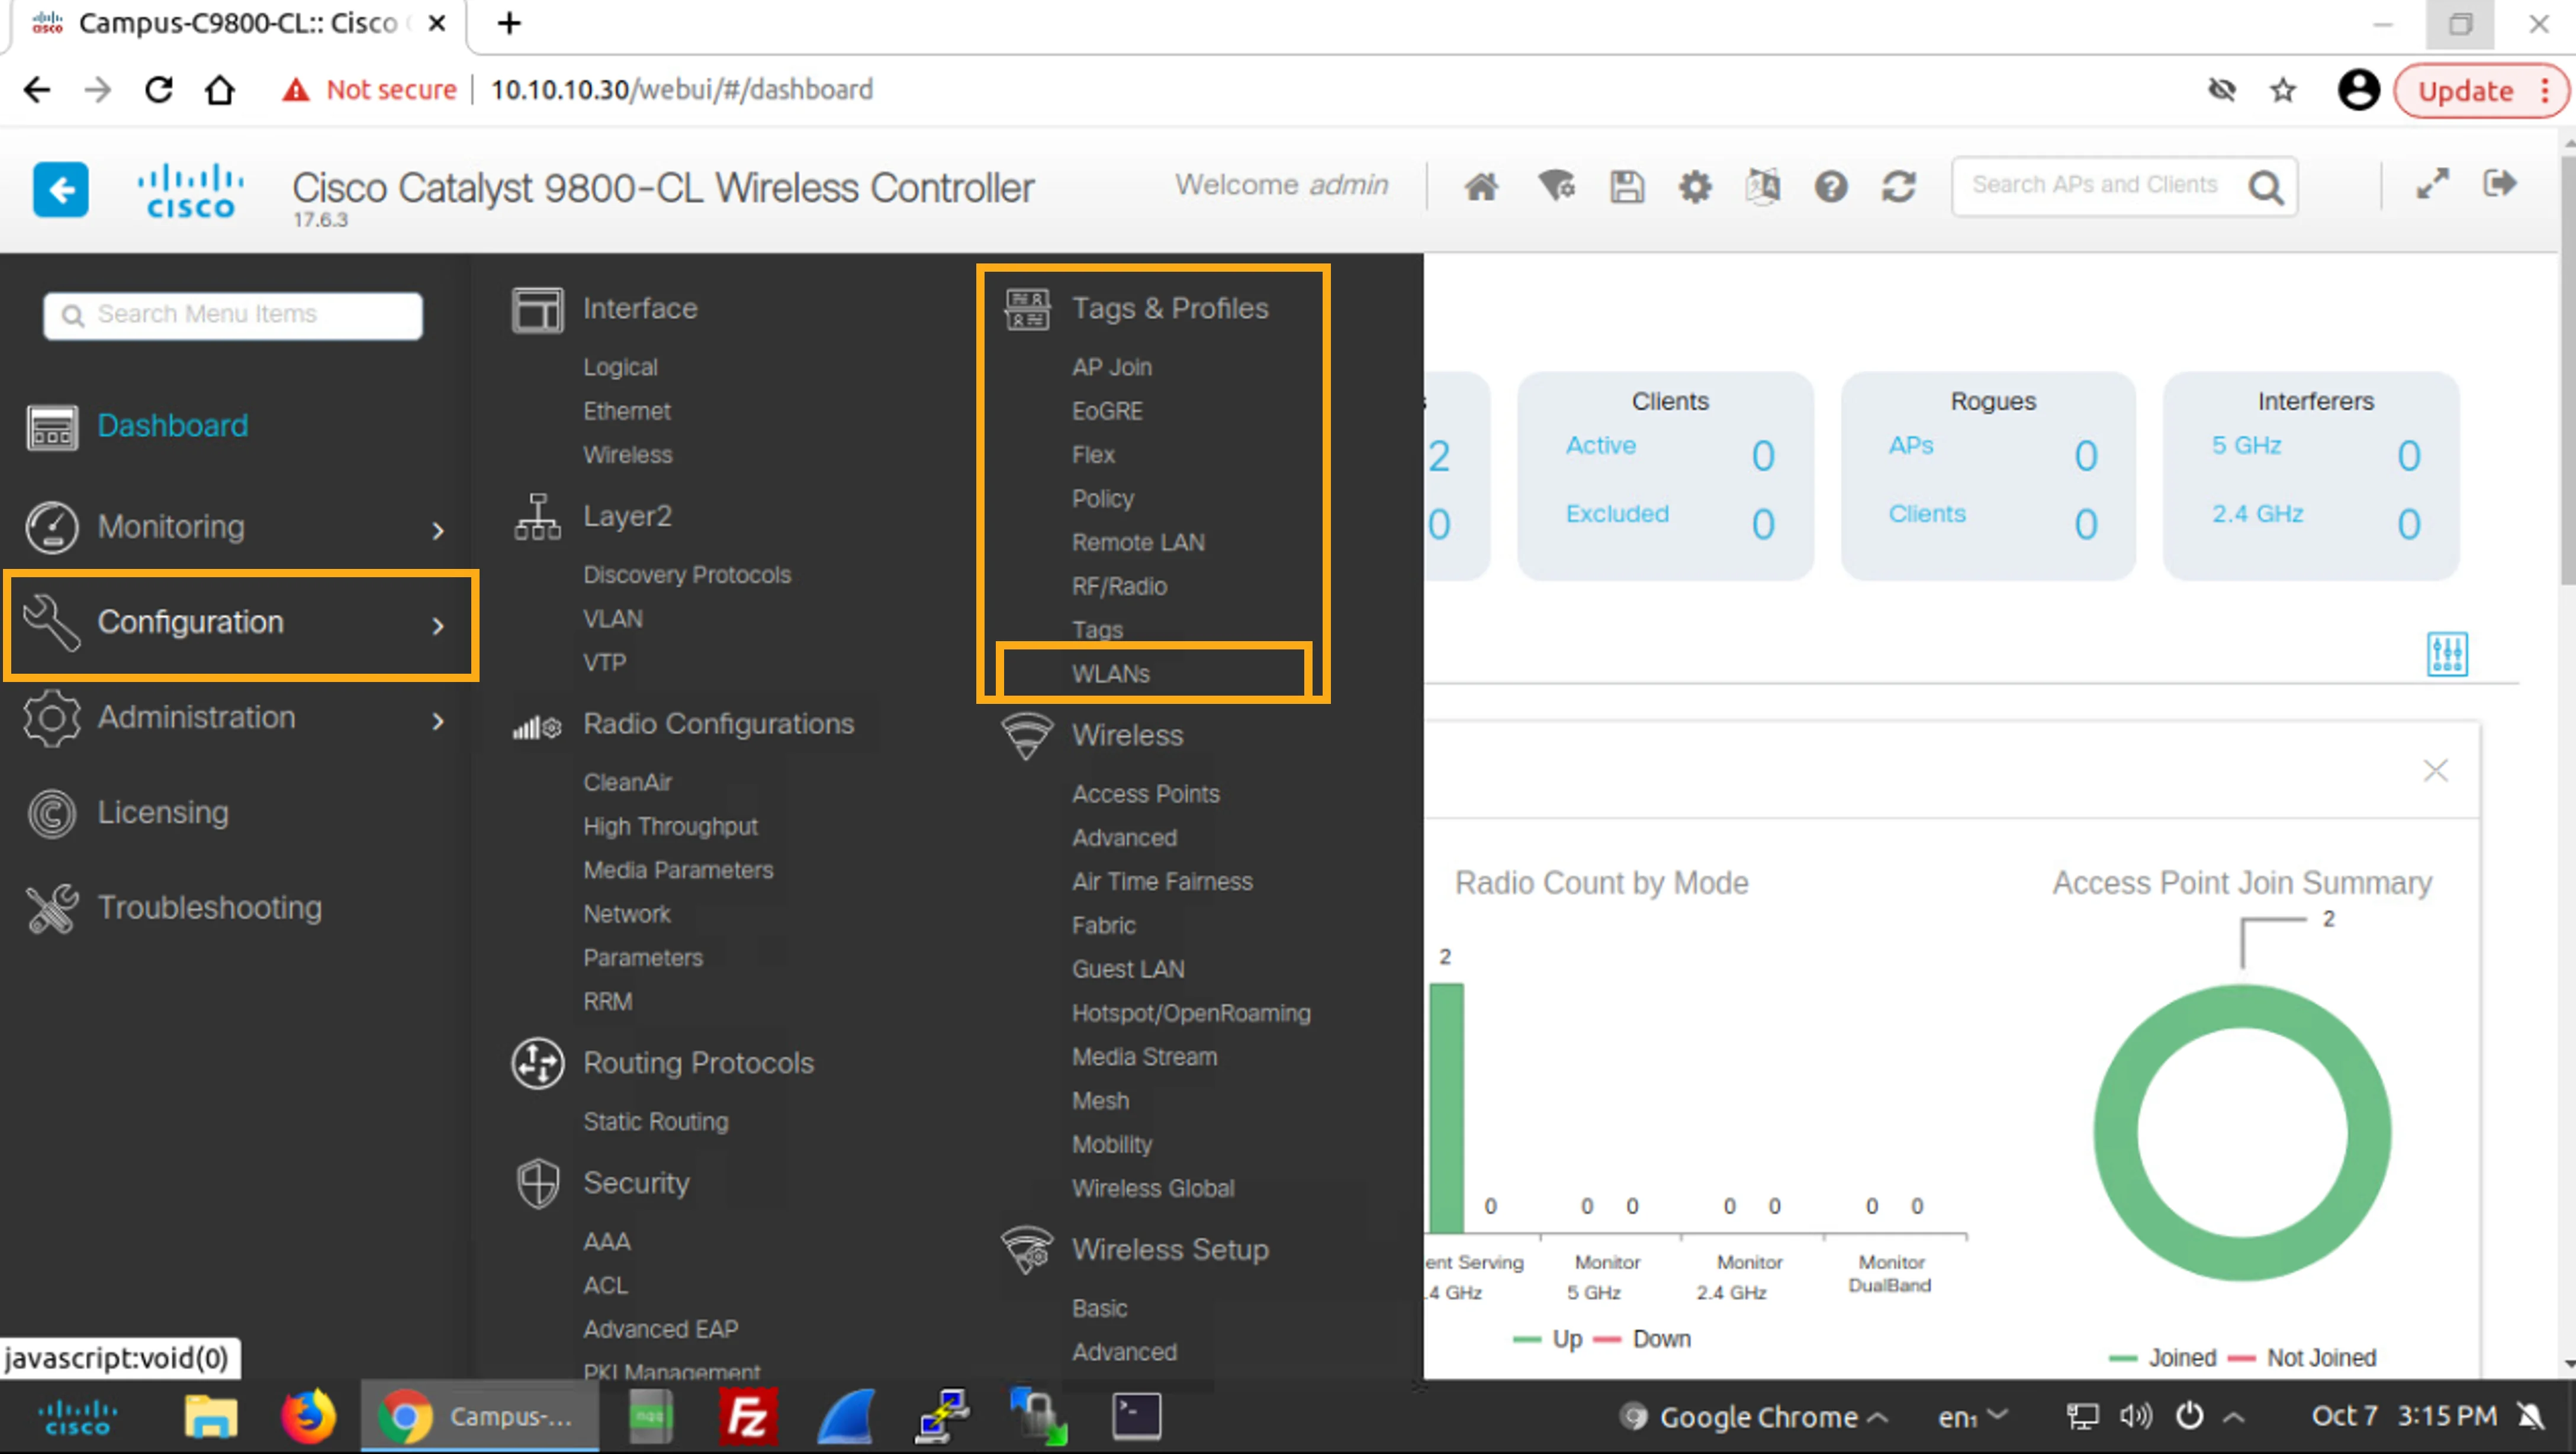
On the Admin PC, in the Campus WLC web GUI, choose Configuration > Tags & Profiles > WLANs.
在 Admin PC 上,於 Campus WLC 網頁 GUI 中,選擇 Configuration > Tags & Profiles > WLANs。
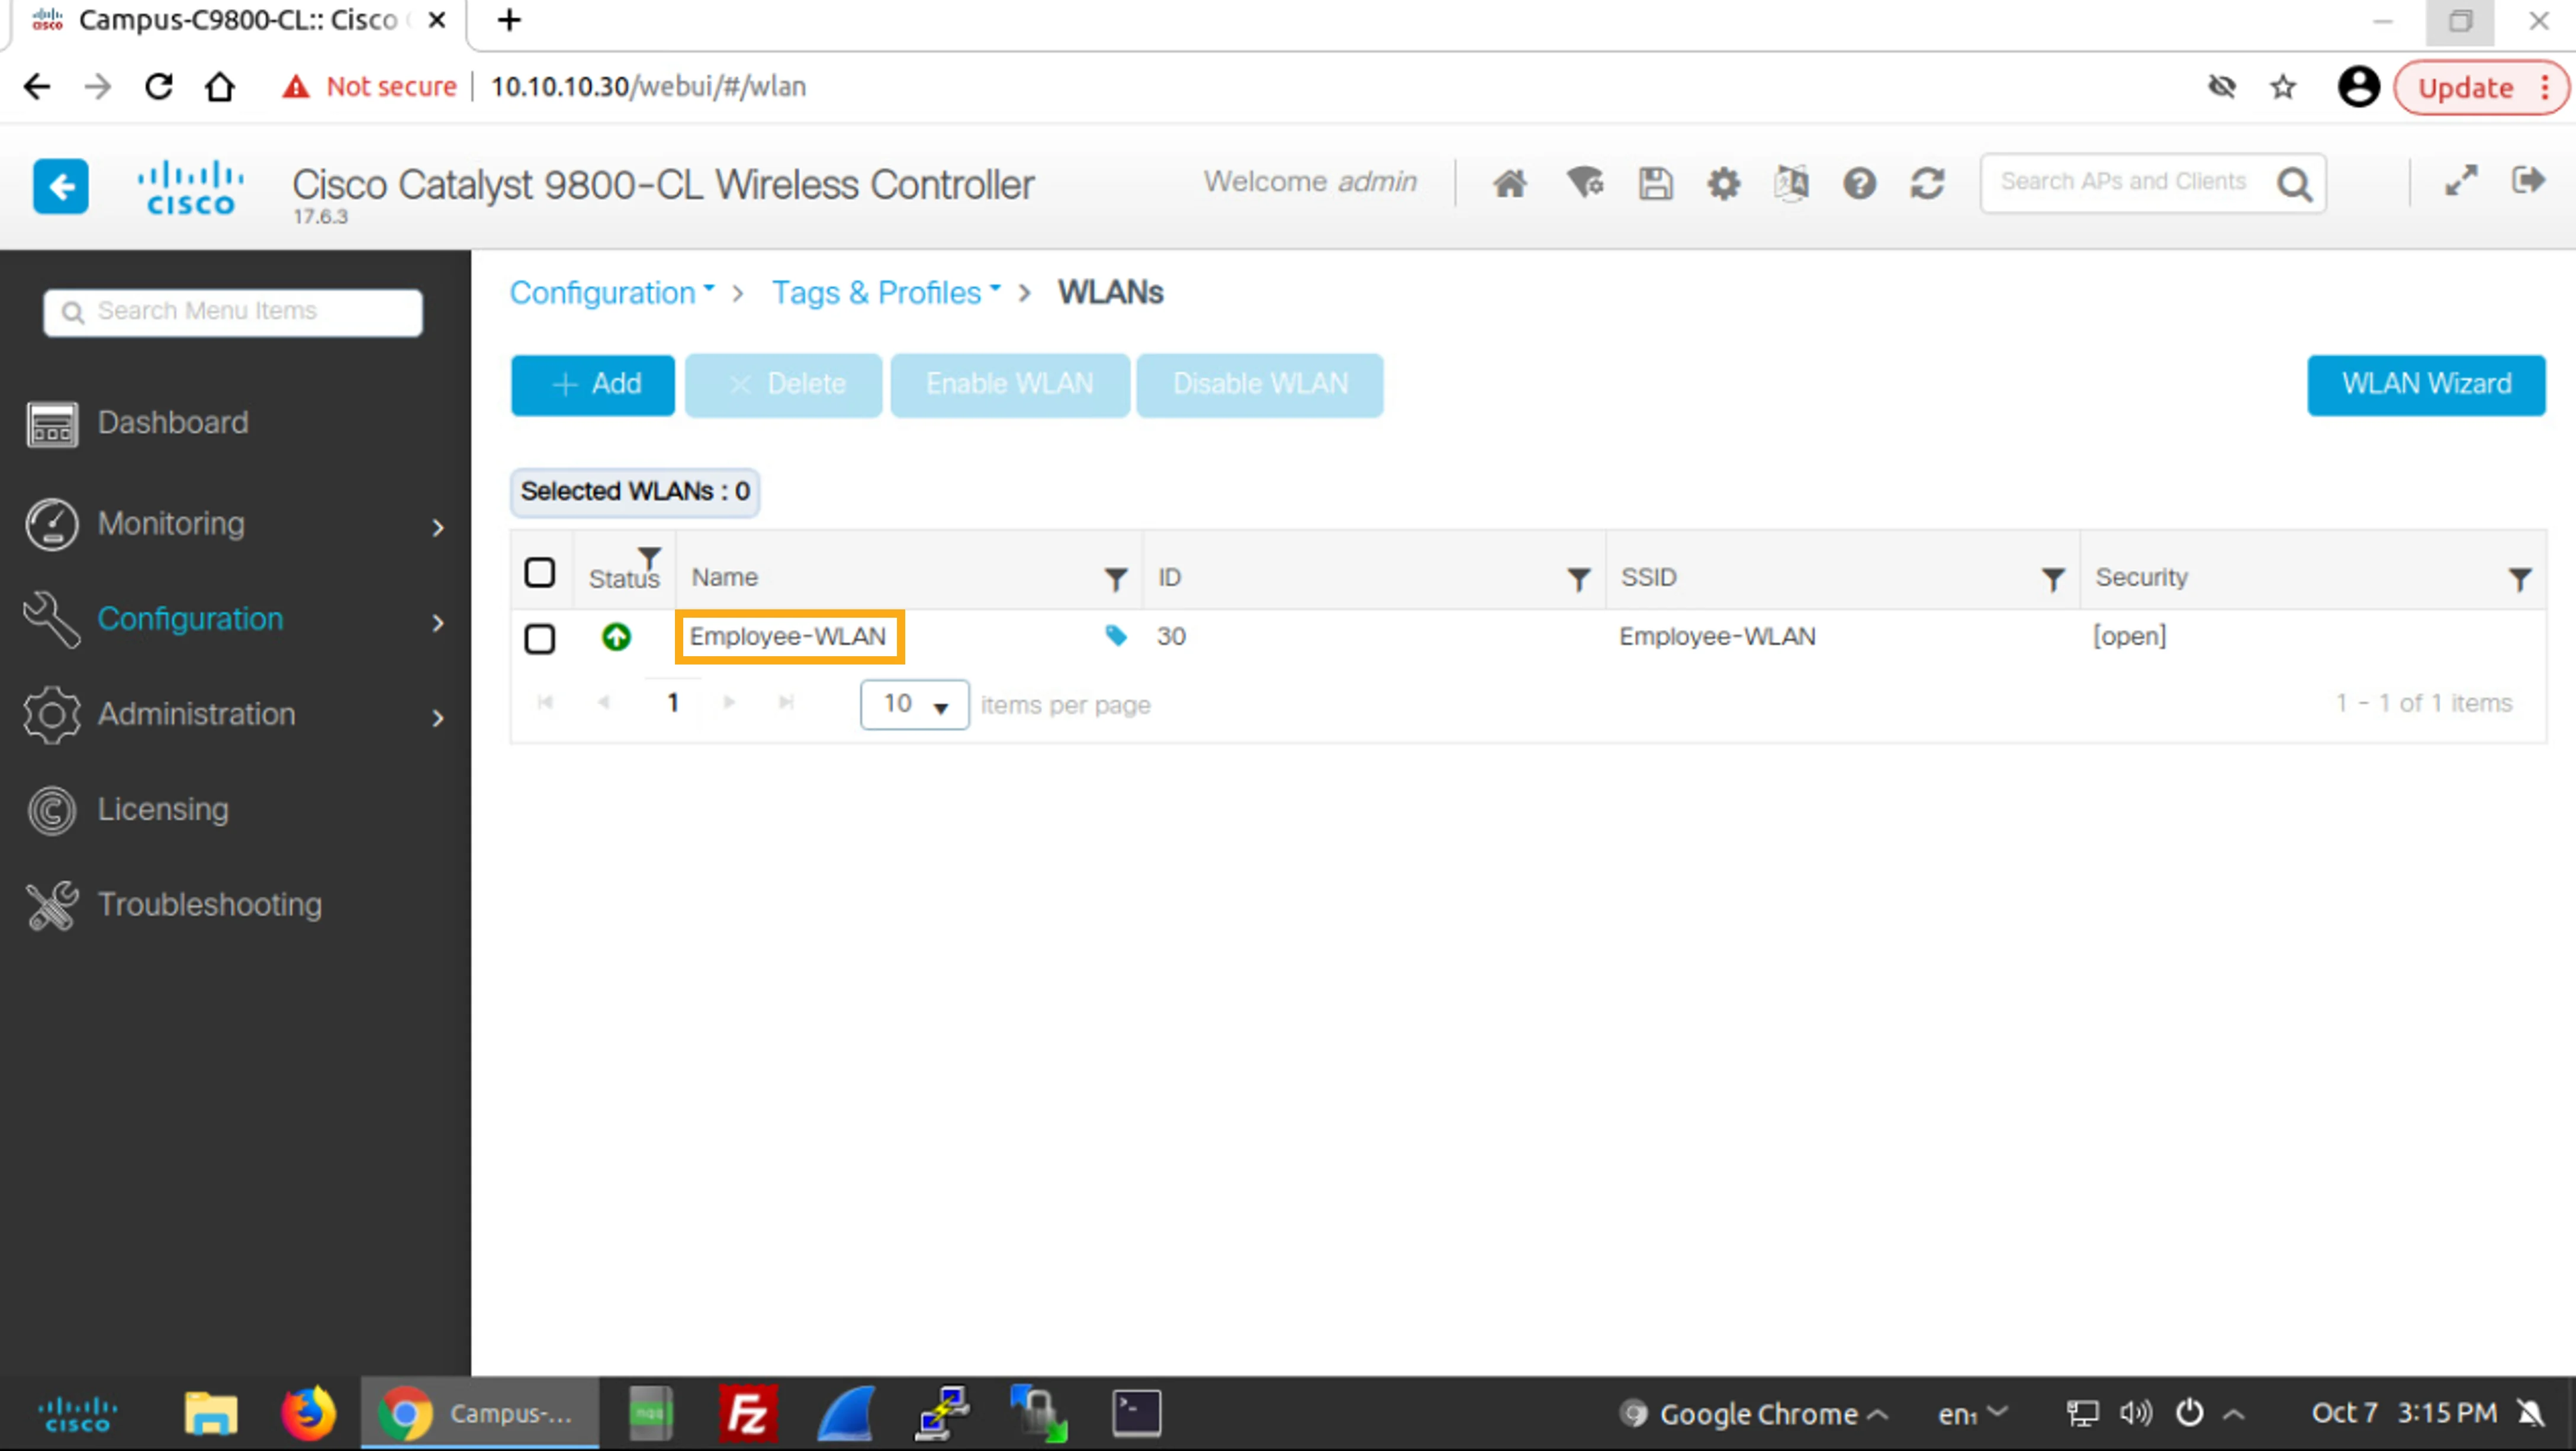
From the list of configured WLANs, click the name of the only available WLAN, the Employee-WLAN.
在已設定的 WLAN 清單中,按一下唯一可用的 WLAN 名稱 Employee-WLAN。
In the Edit WLAN window, click the Security tab.
在 Edit WLAN 視窗中,按一下 Security 標籤。
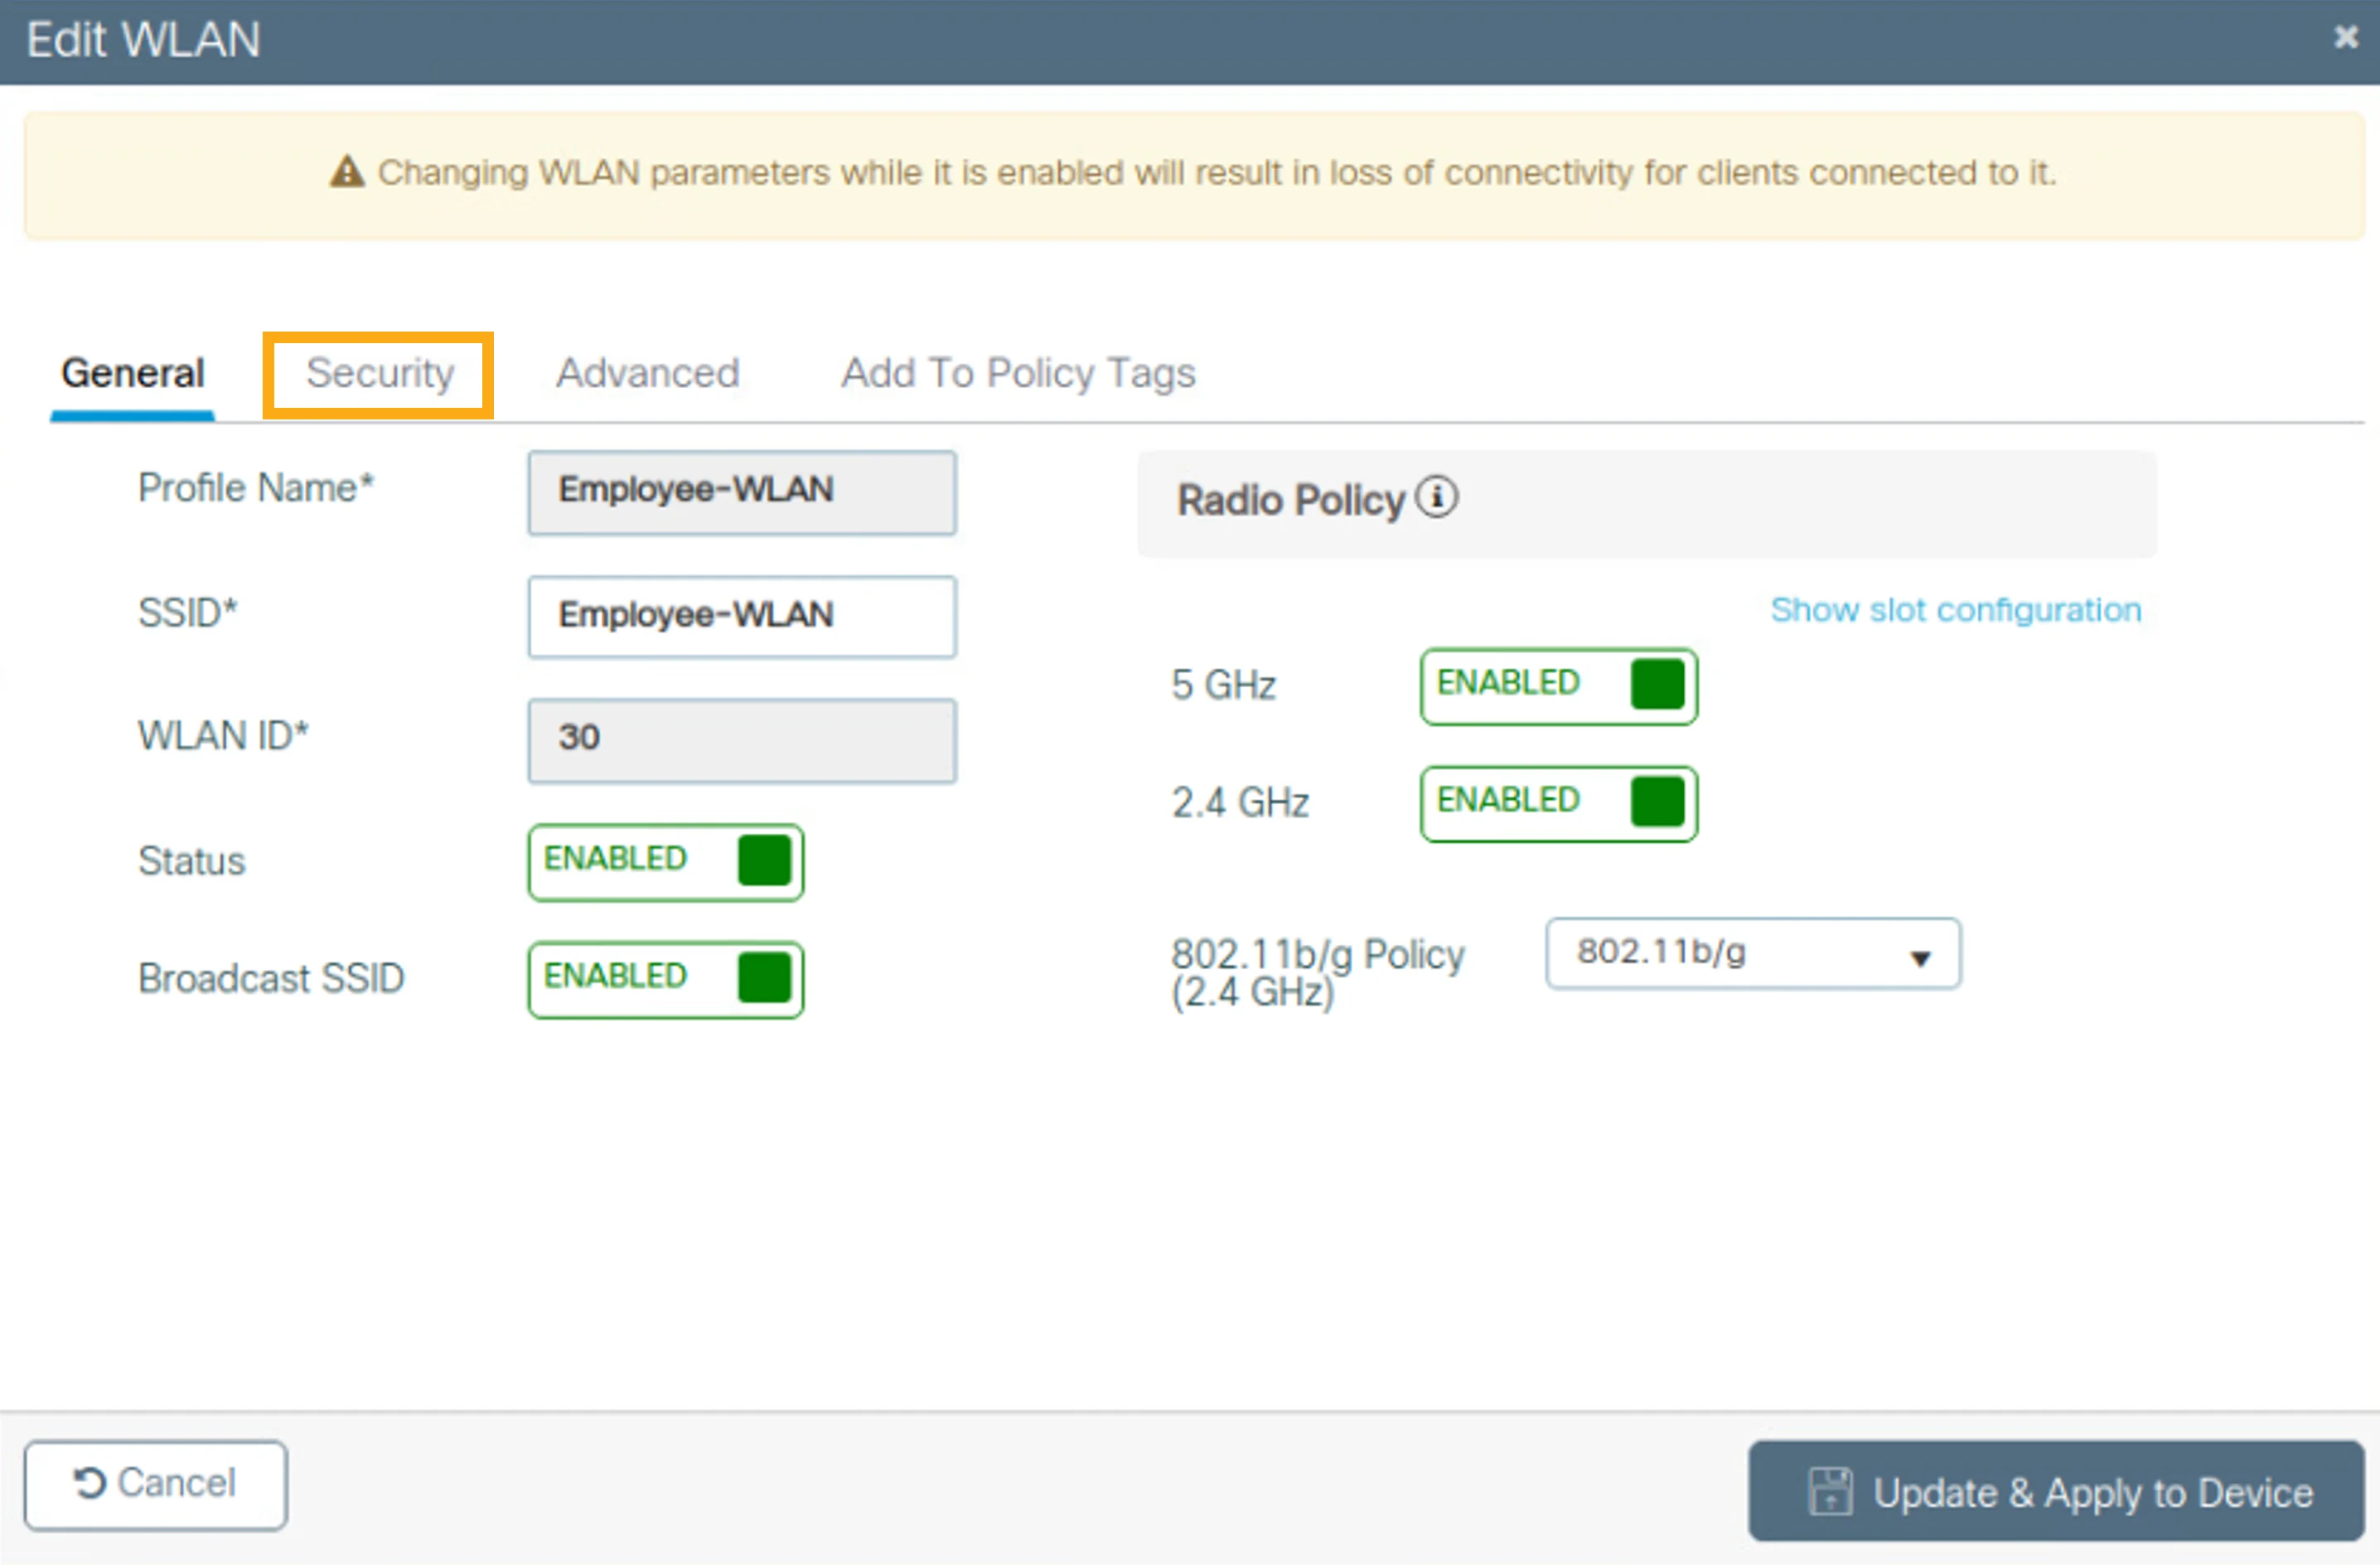
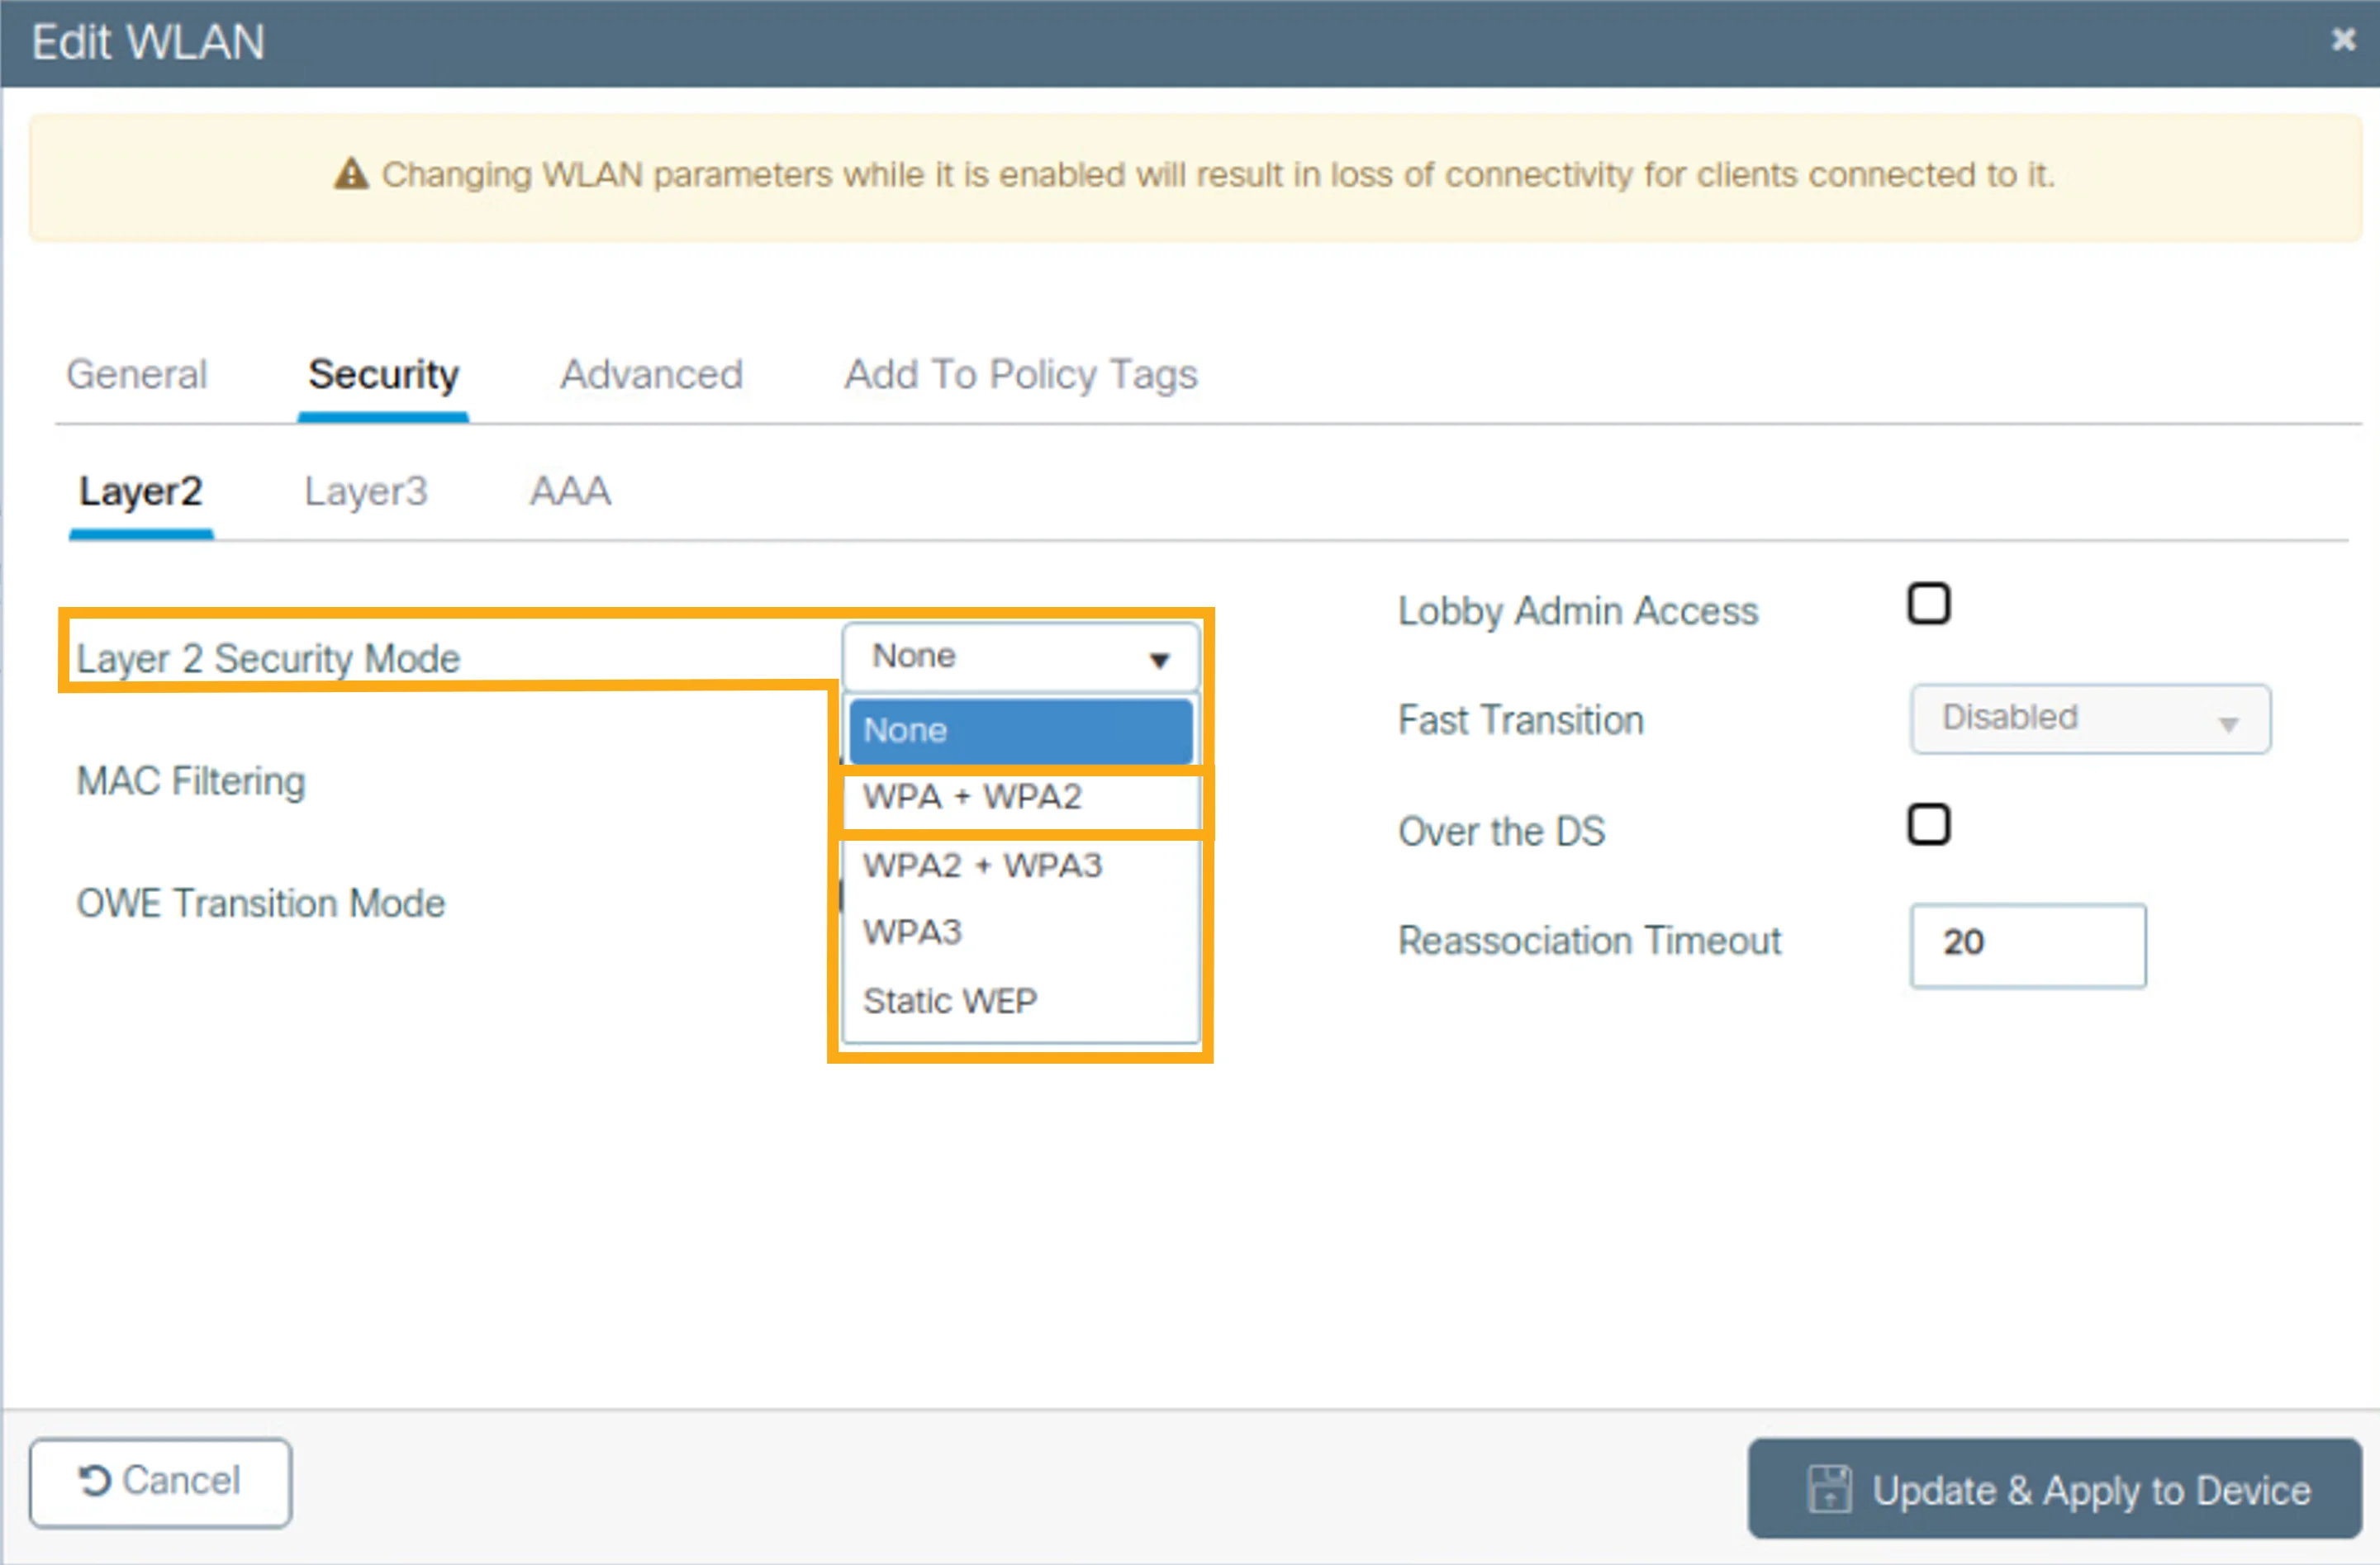
Configure the WLAN with the following security settings and apply the updates to the device.
以下列安全性設定值設定此 WLAN,並將更新套用至裝置。
Layer 2 Security Mode Layer 2 Security Mode | WPA + WPA2 WPA + WPA2 |
Auth Key Mgmt Auth Key Mgmt | Check the PSK check box 勾選 PSK 核取方塊 |
Pre-Shared Key Pre-Shared Key | Cisco123 Cisco123 |
In particular, perform the following procedure to configure these security settings and apply them:
請具體執行下列程序,以設定並套用這些安全性設定:
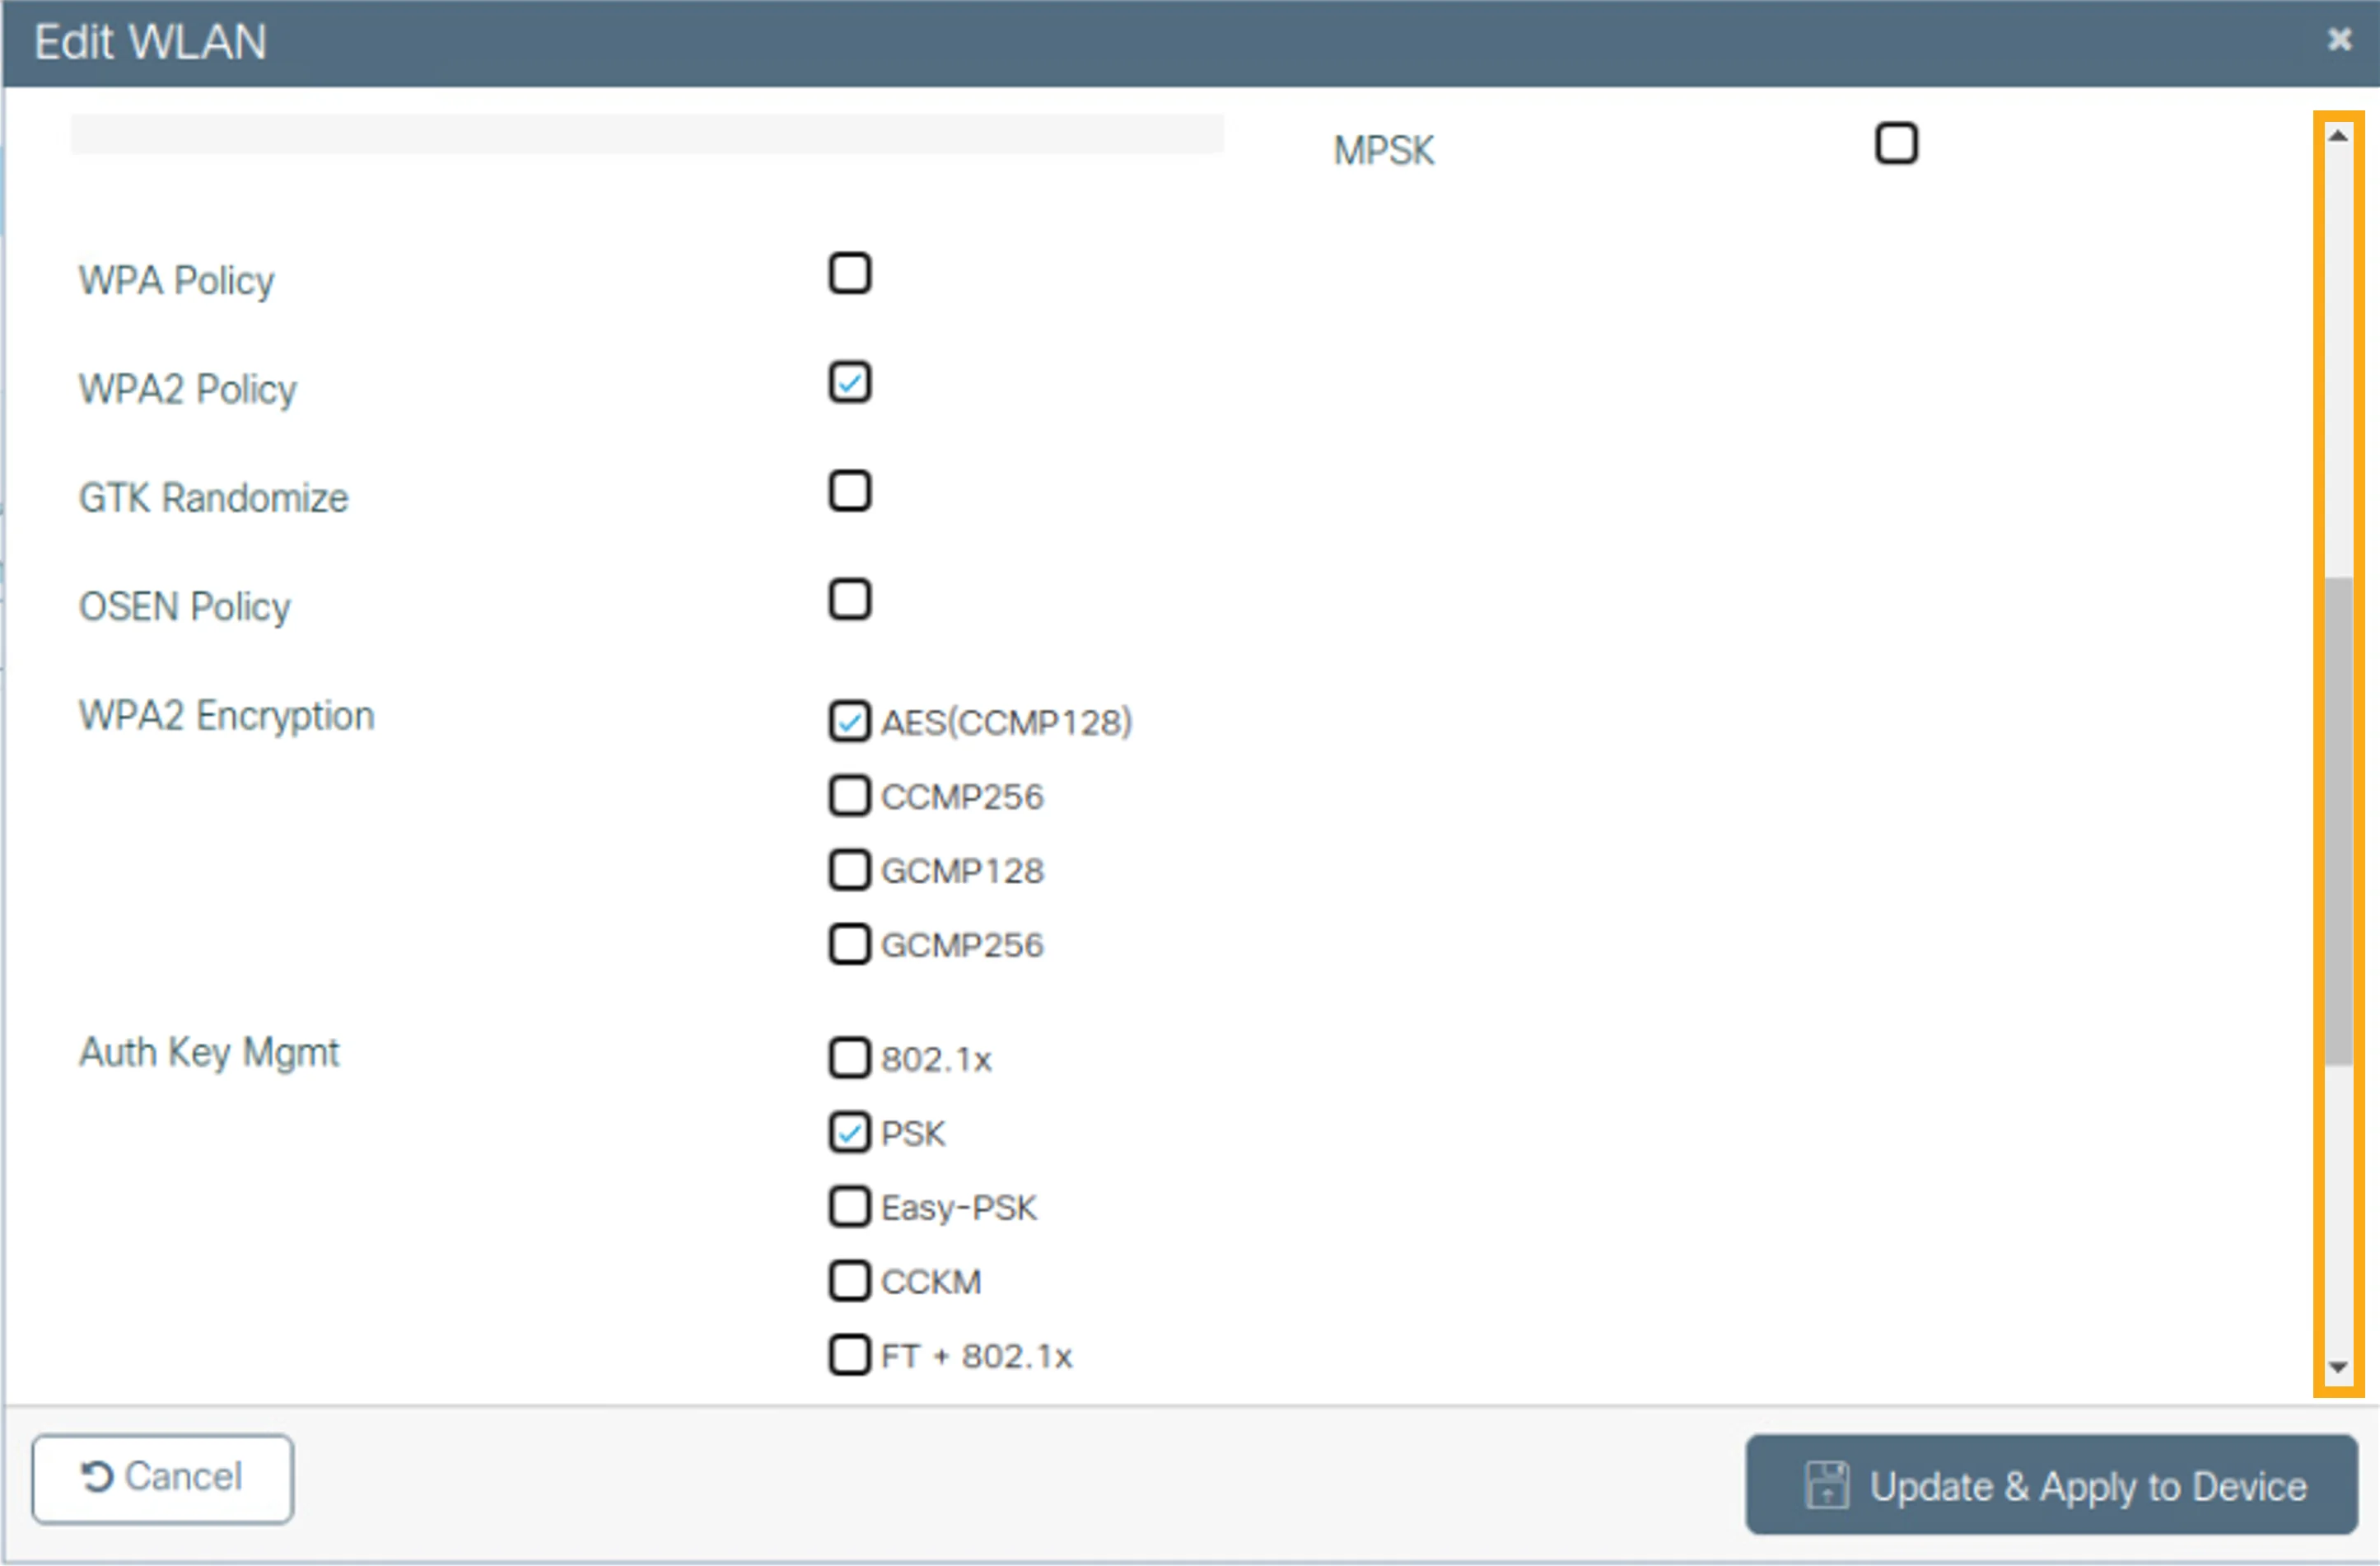
- In the Layer 2 Security Mode drop-down list, click WPA + WPA2.在 Layer 2 Security Mode 下拉式清單中,按一下 WPA + WPA2。
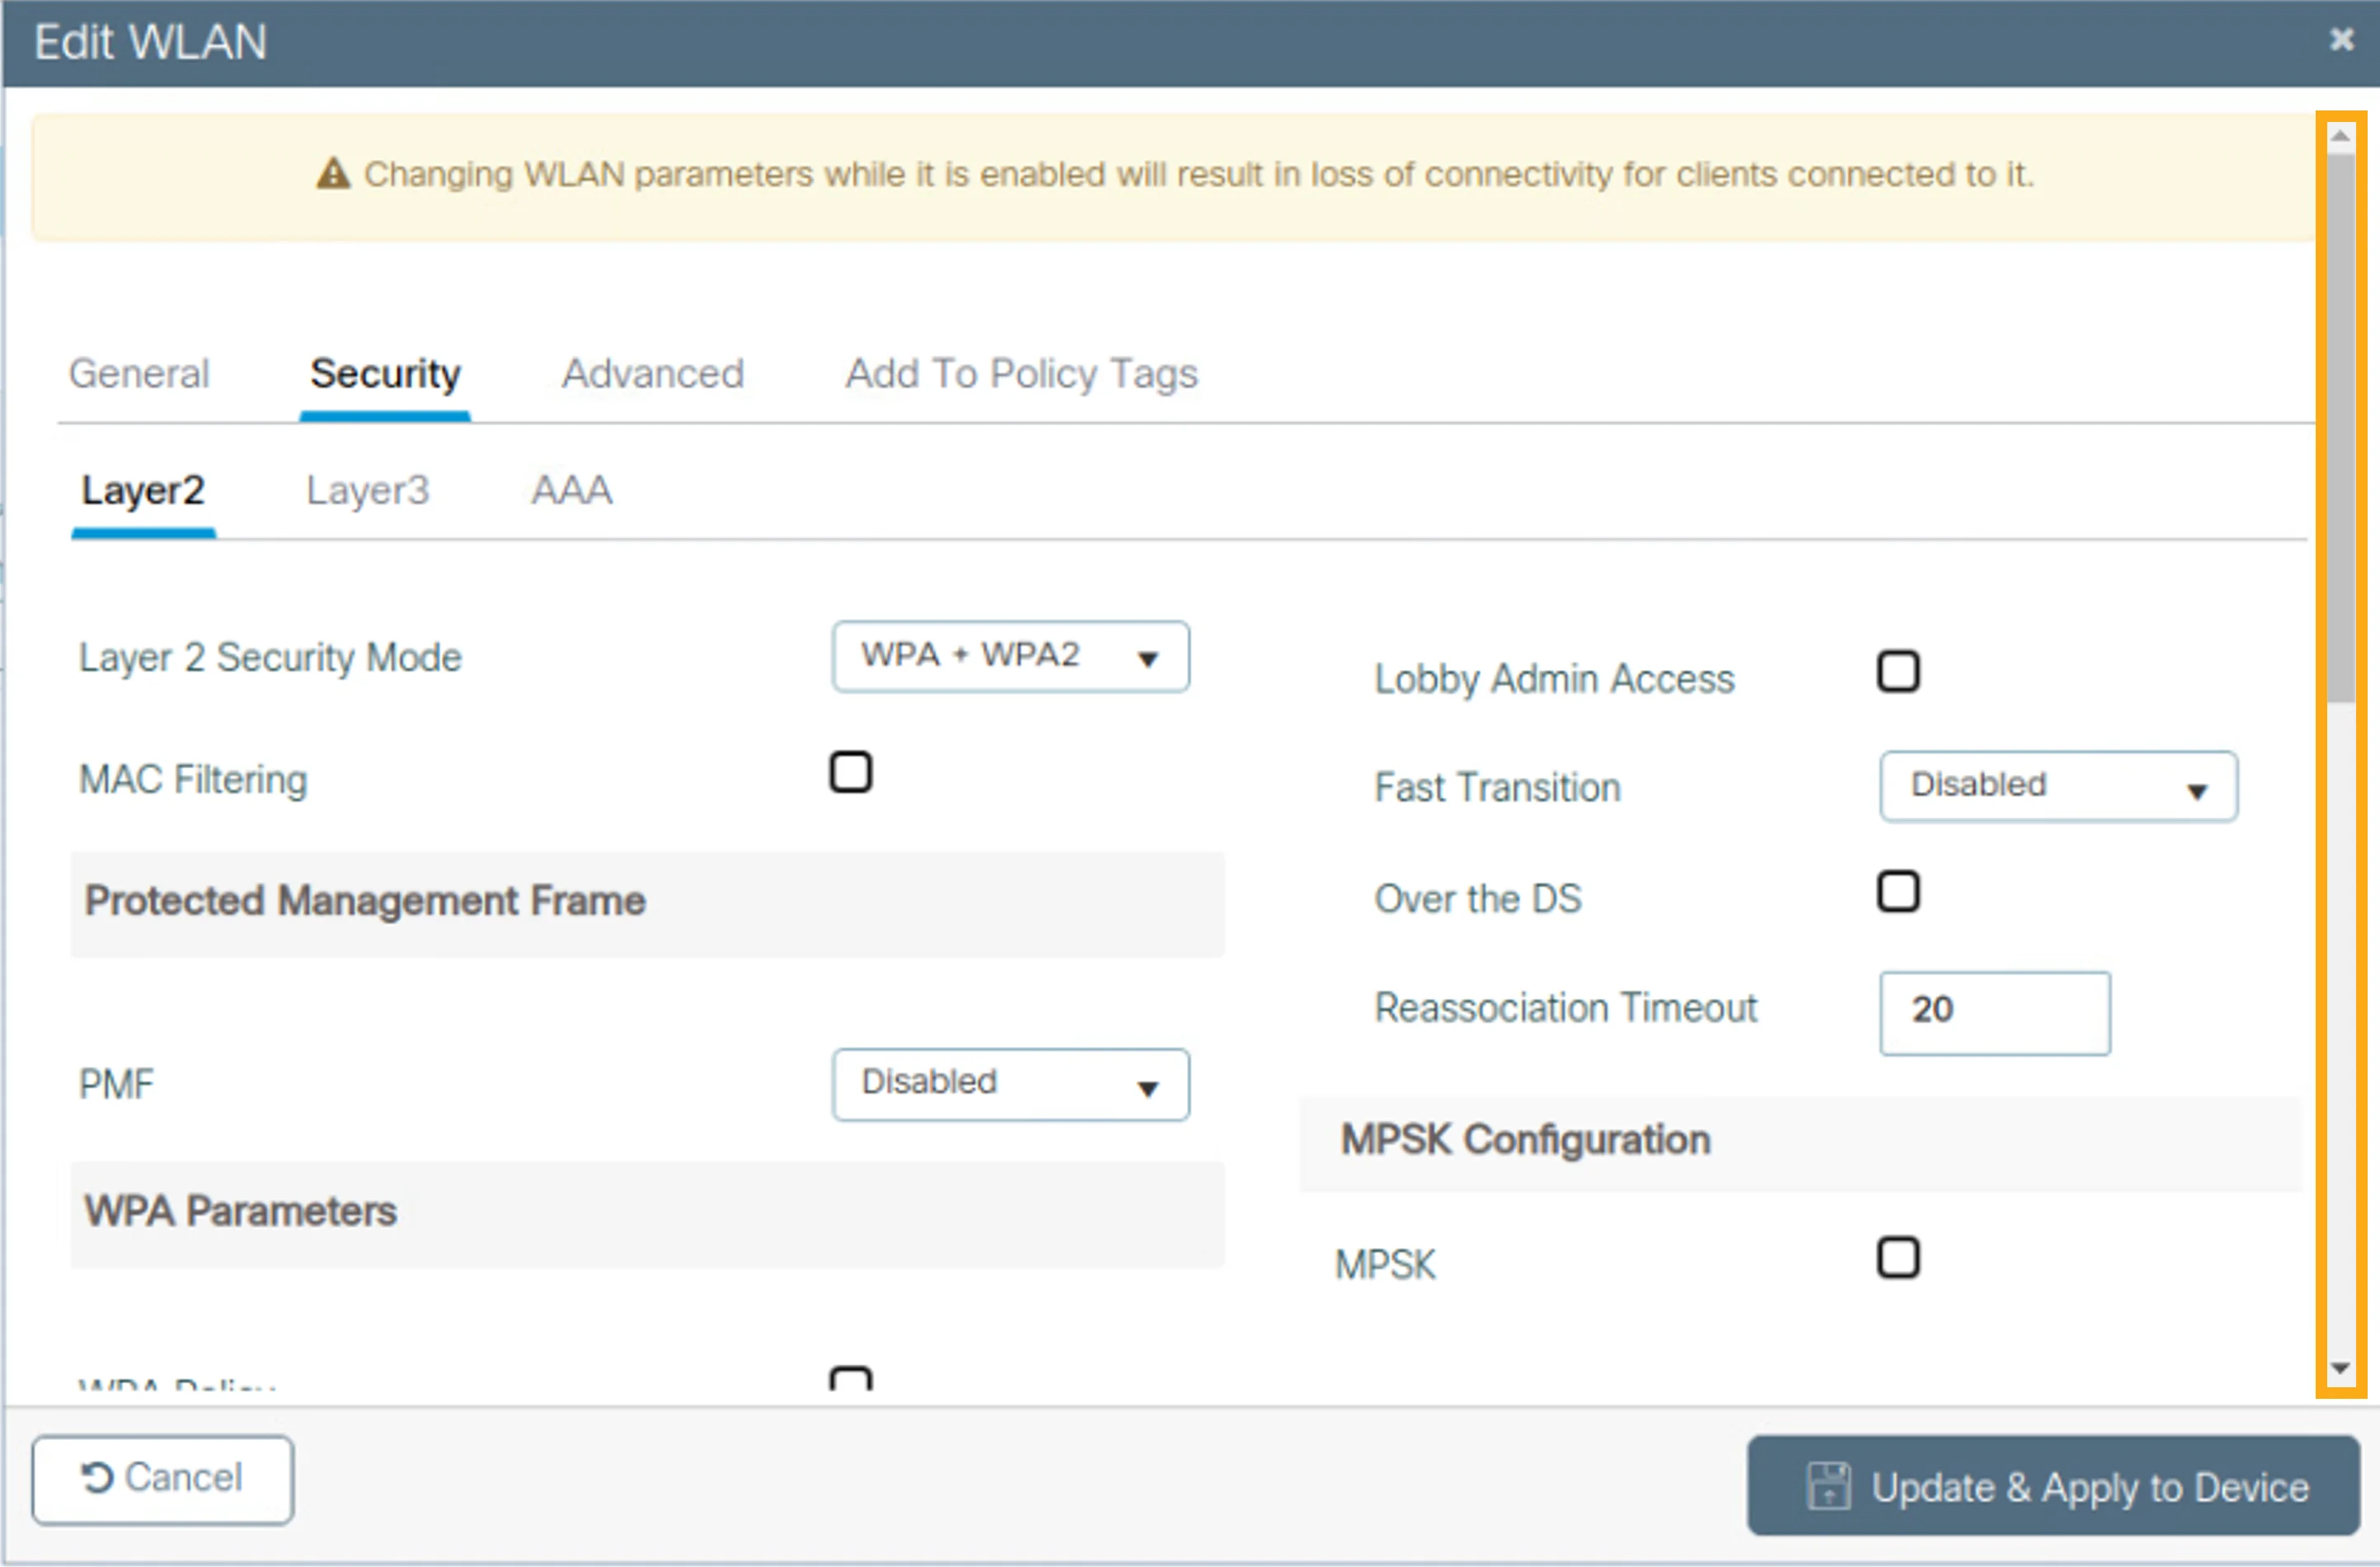
- Click in the scroll bar area to move down the page so that you can see the WPA2 and Authentication Key Management options.在捲軸區域按一下,向下捲動頁面,以便看到 WPA2 及 Authentication Key Management 選項。
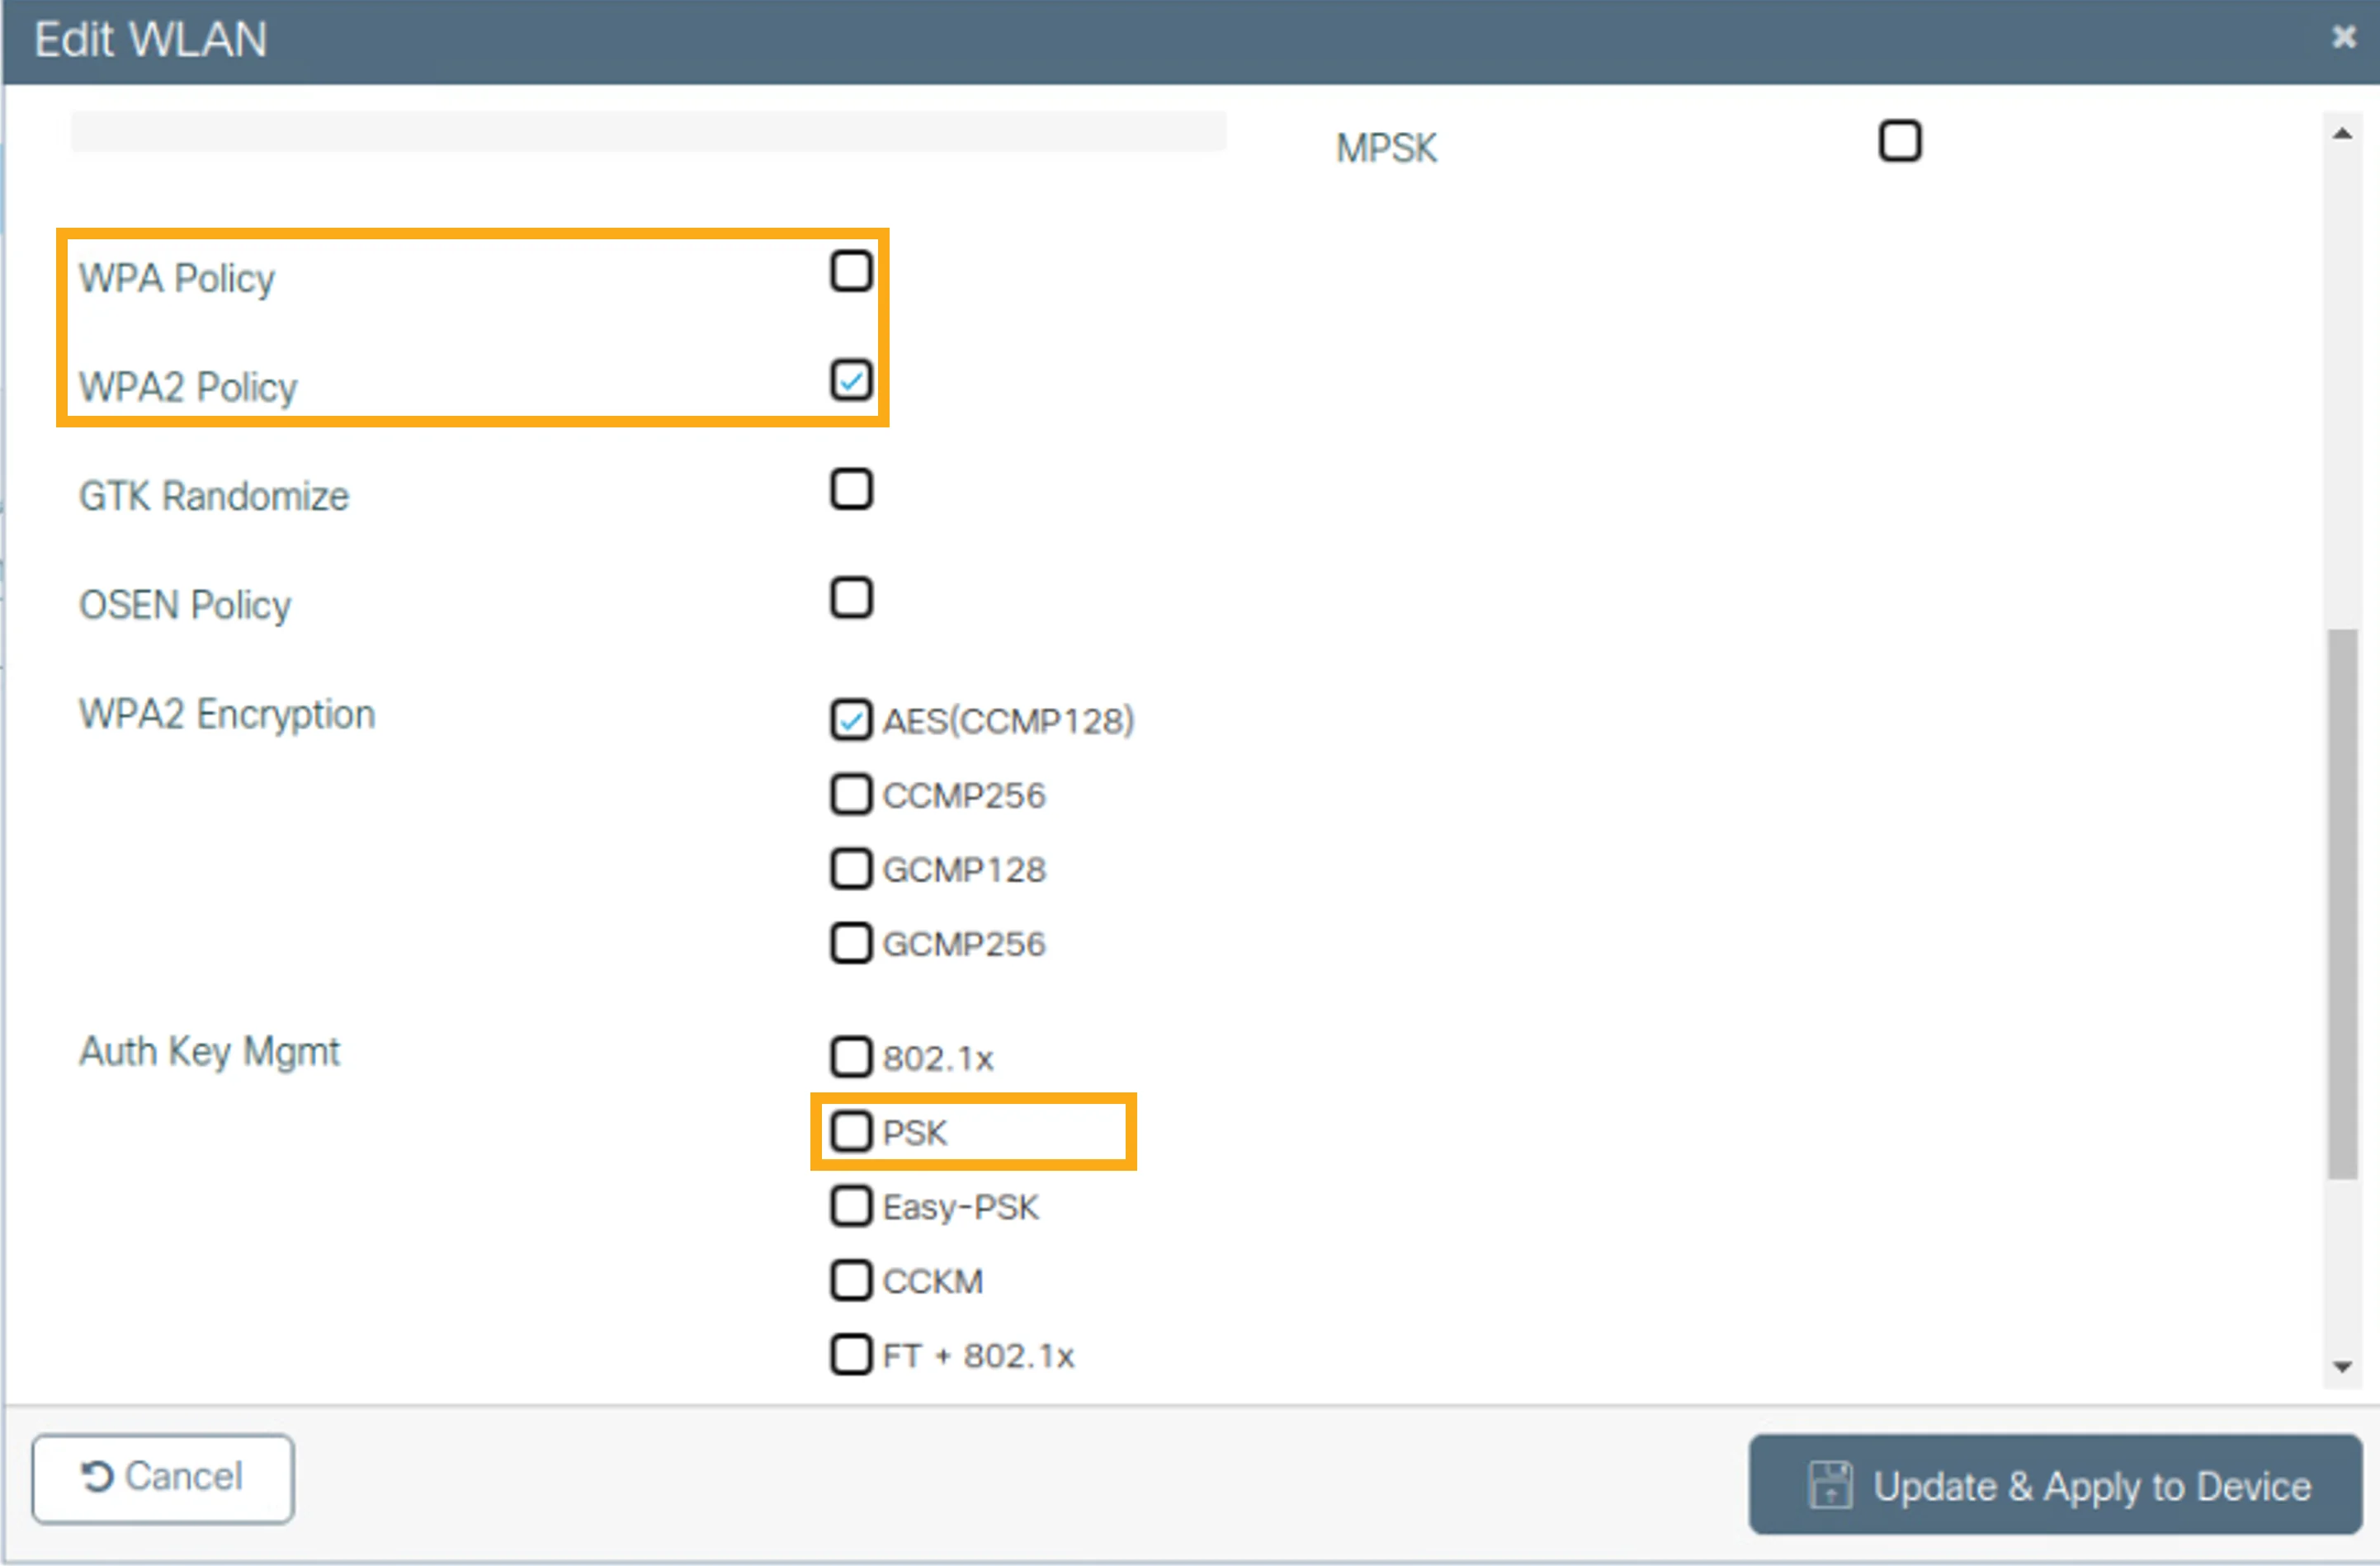
- Note that the WPA Policy is disabled and the WPA2 Policy is enabled. For the Authentication Key Management, or Auth Key Mgmt, field, check the PSK check box.請注意,WPA Policy 已停用,WPA2 Policy 已啟用。在 Authentication Key Management(即 Auth Key Mgmt)欄位中,勾選 PSK 核取方塊。
- Click in the scroll bar area to move to the bottom of the page.在捲軸區域按一下,移動到頁面底部。
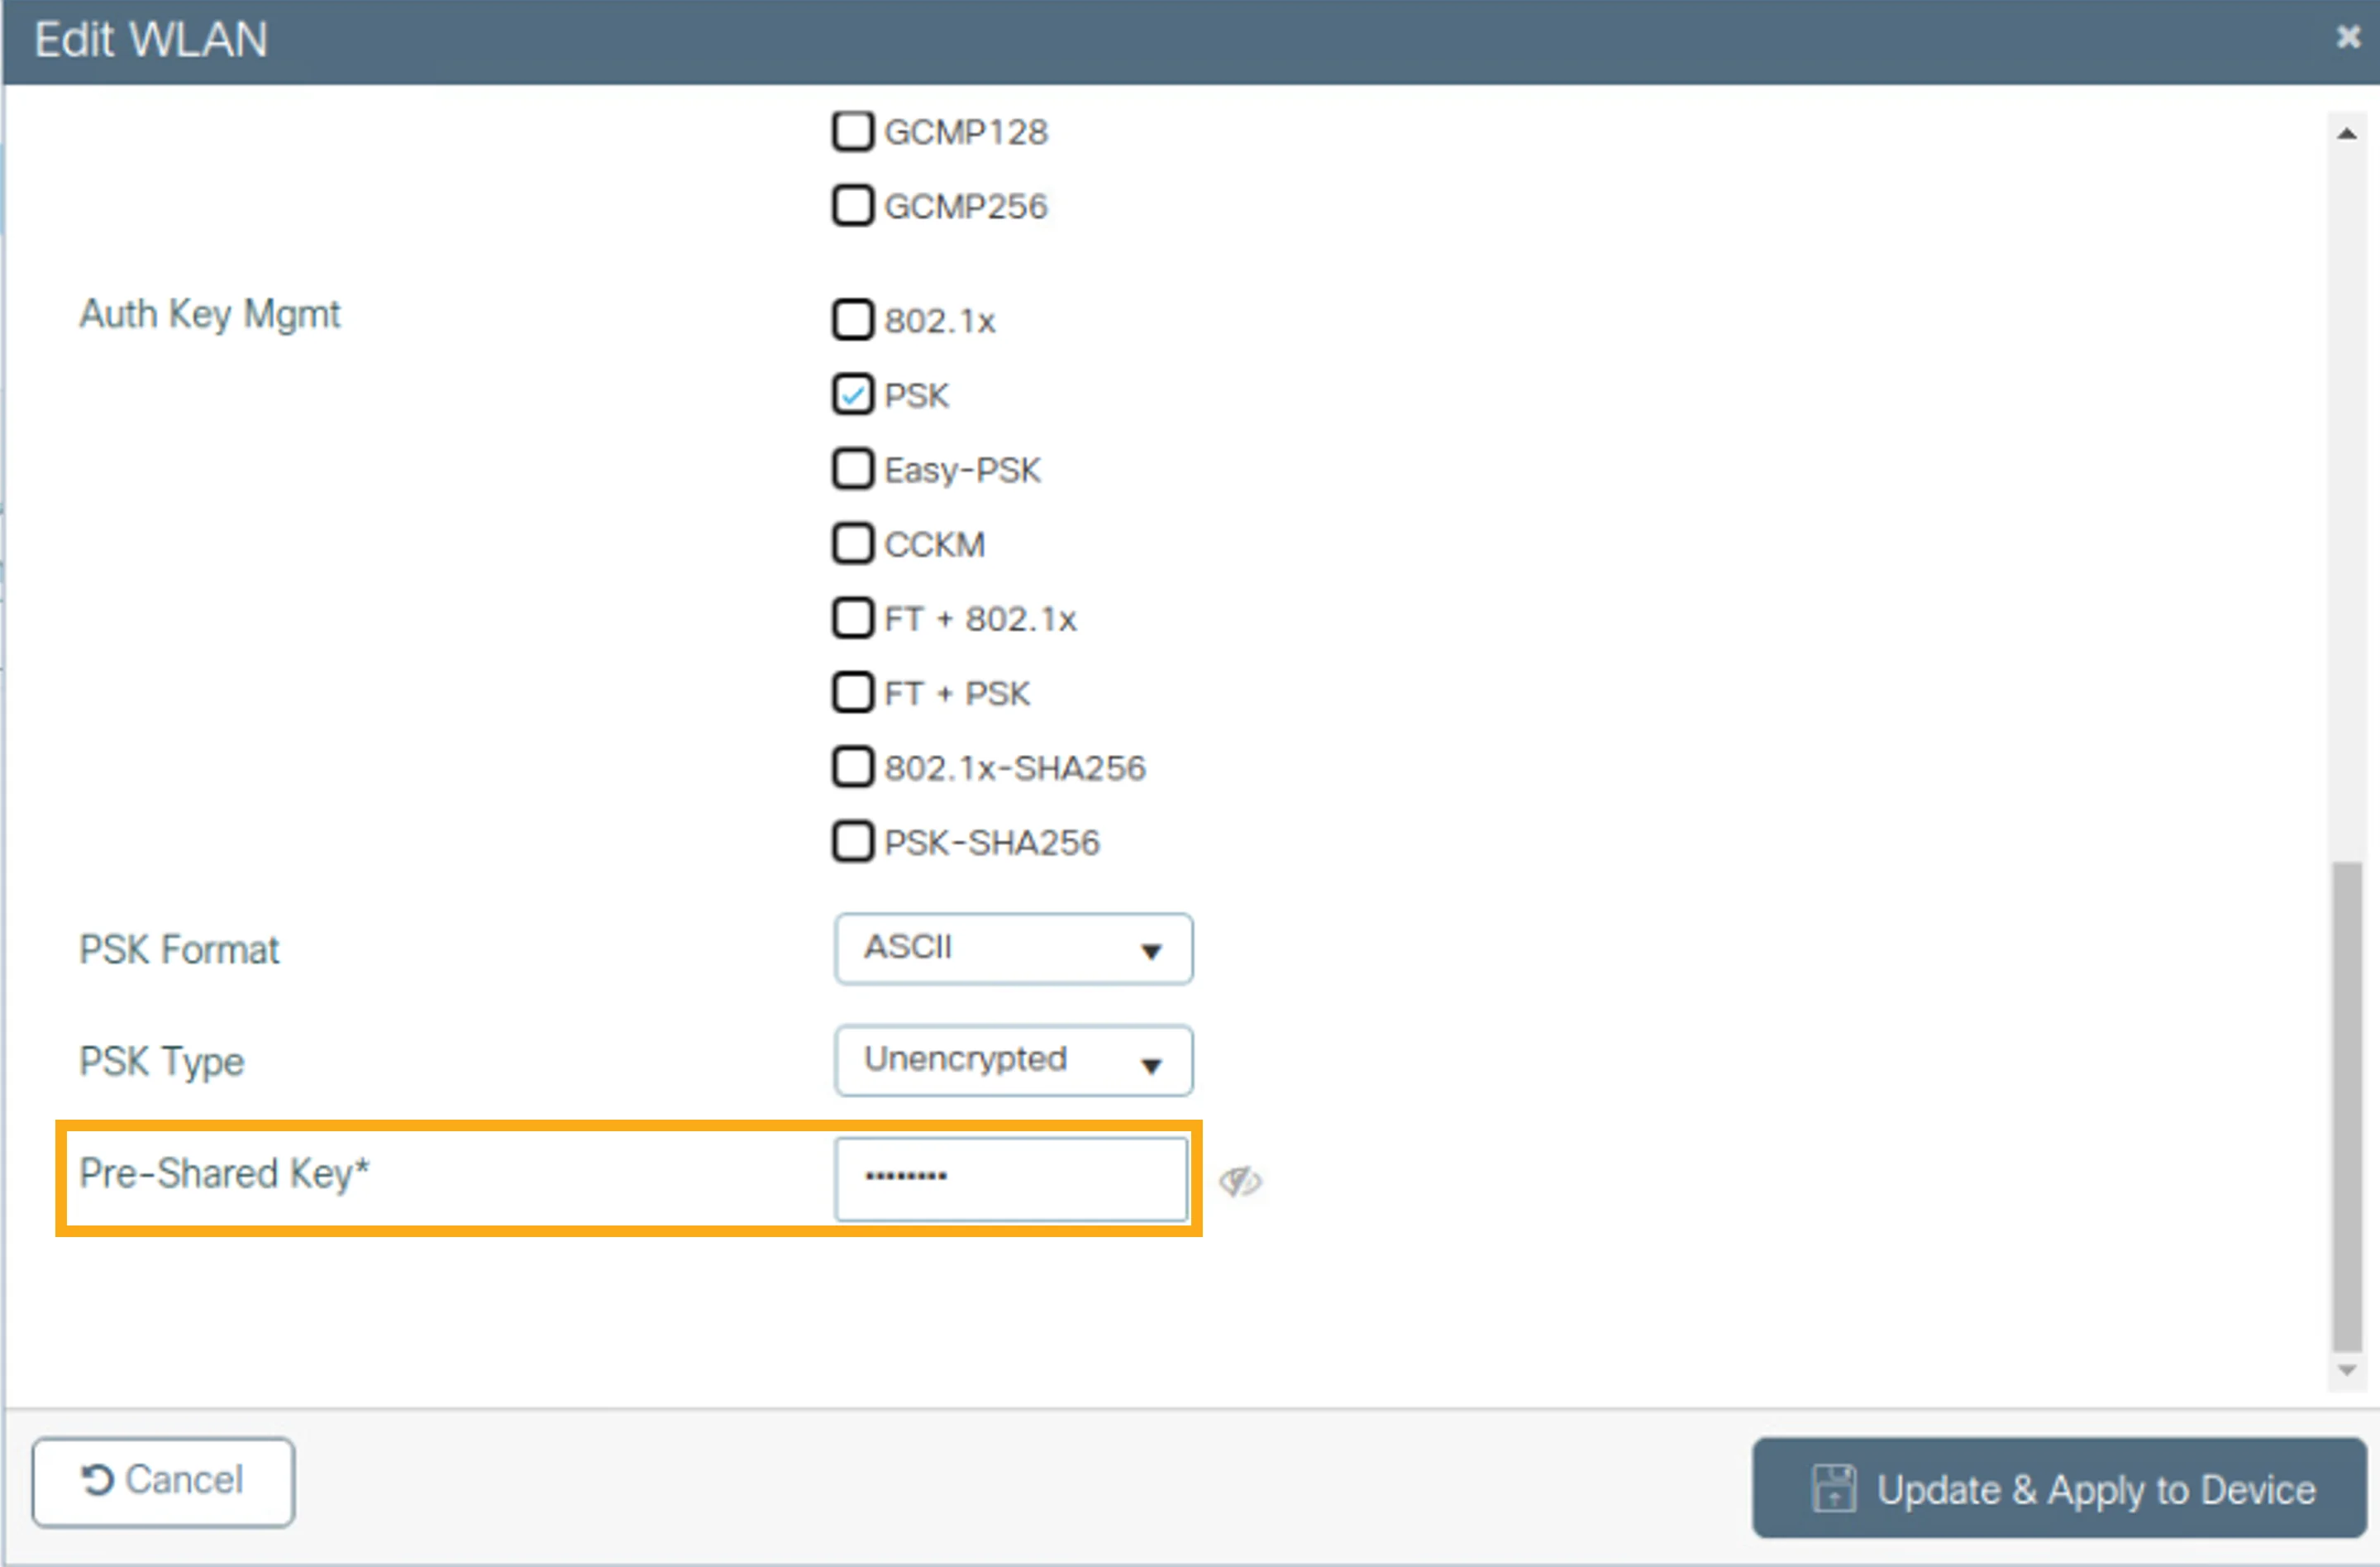
Validate the Pre-Shared Key and Apply the WLAN Security Changes
驗證預先共用金鑰並套用 WLAN 安全性變更
Note that asterisks are shown instead of the actual characters of the key. Verify that you entered the key correctly by clicking the eye symbolto the right of the key.
請注意,畫面顯示的是星號,而非金鑰的實際字元。按一下金鑰右側的 眼睛符號,驗證您輸入的金鑰是否正確。
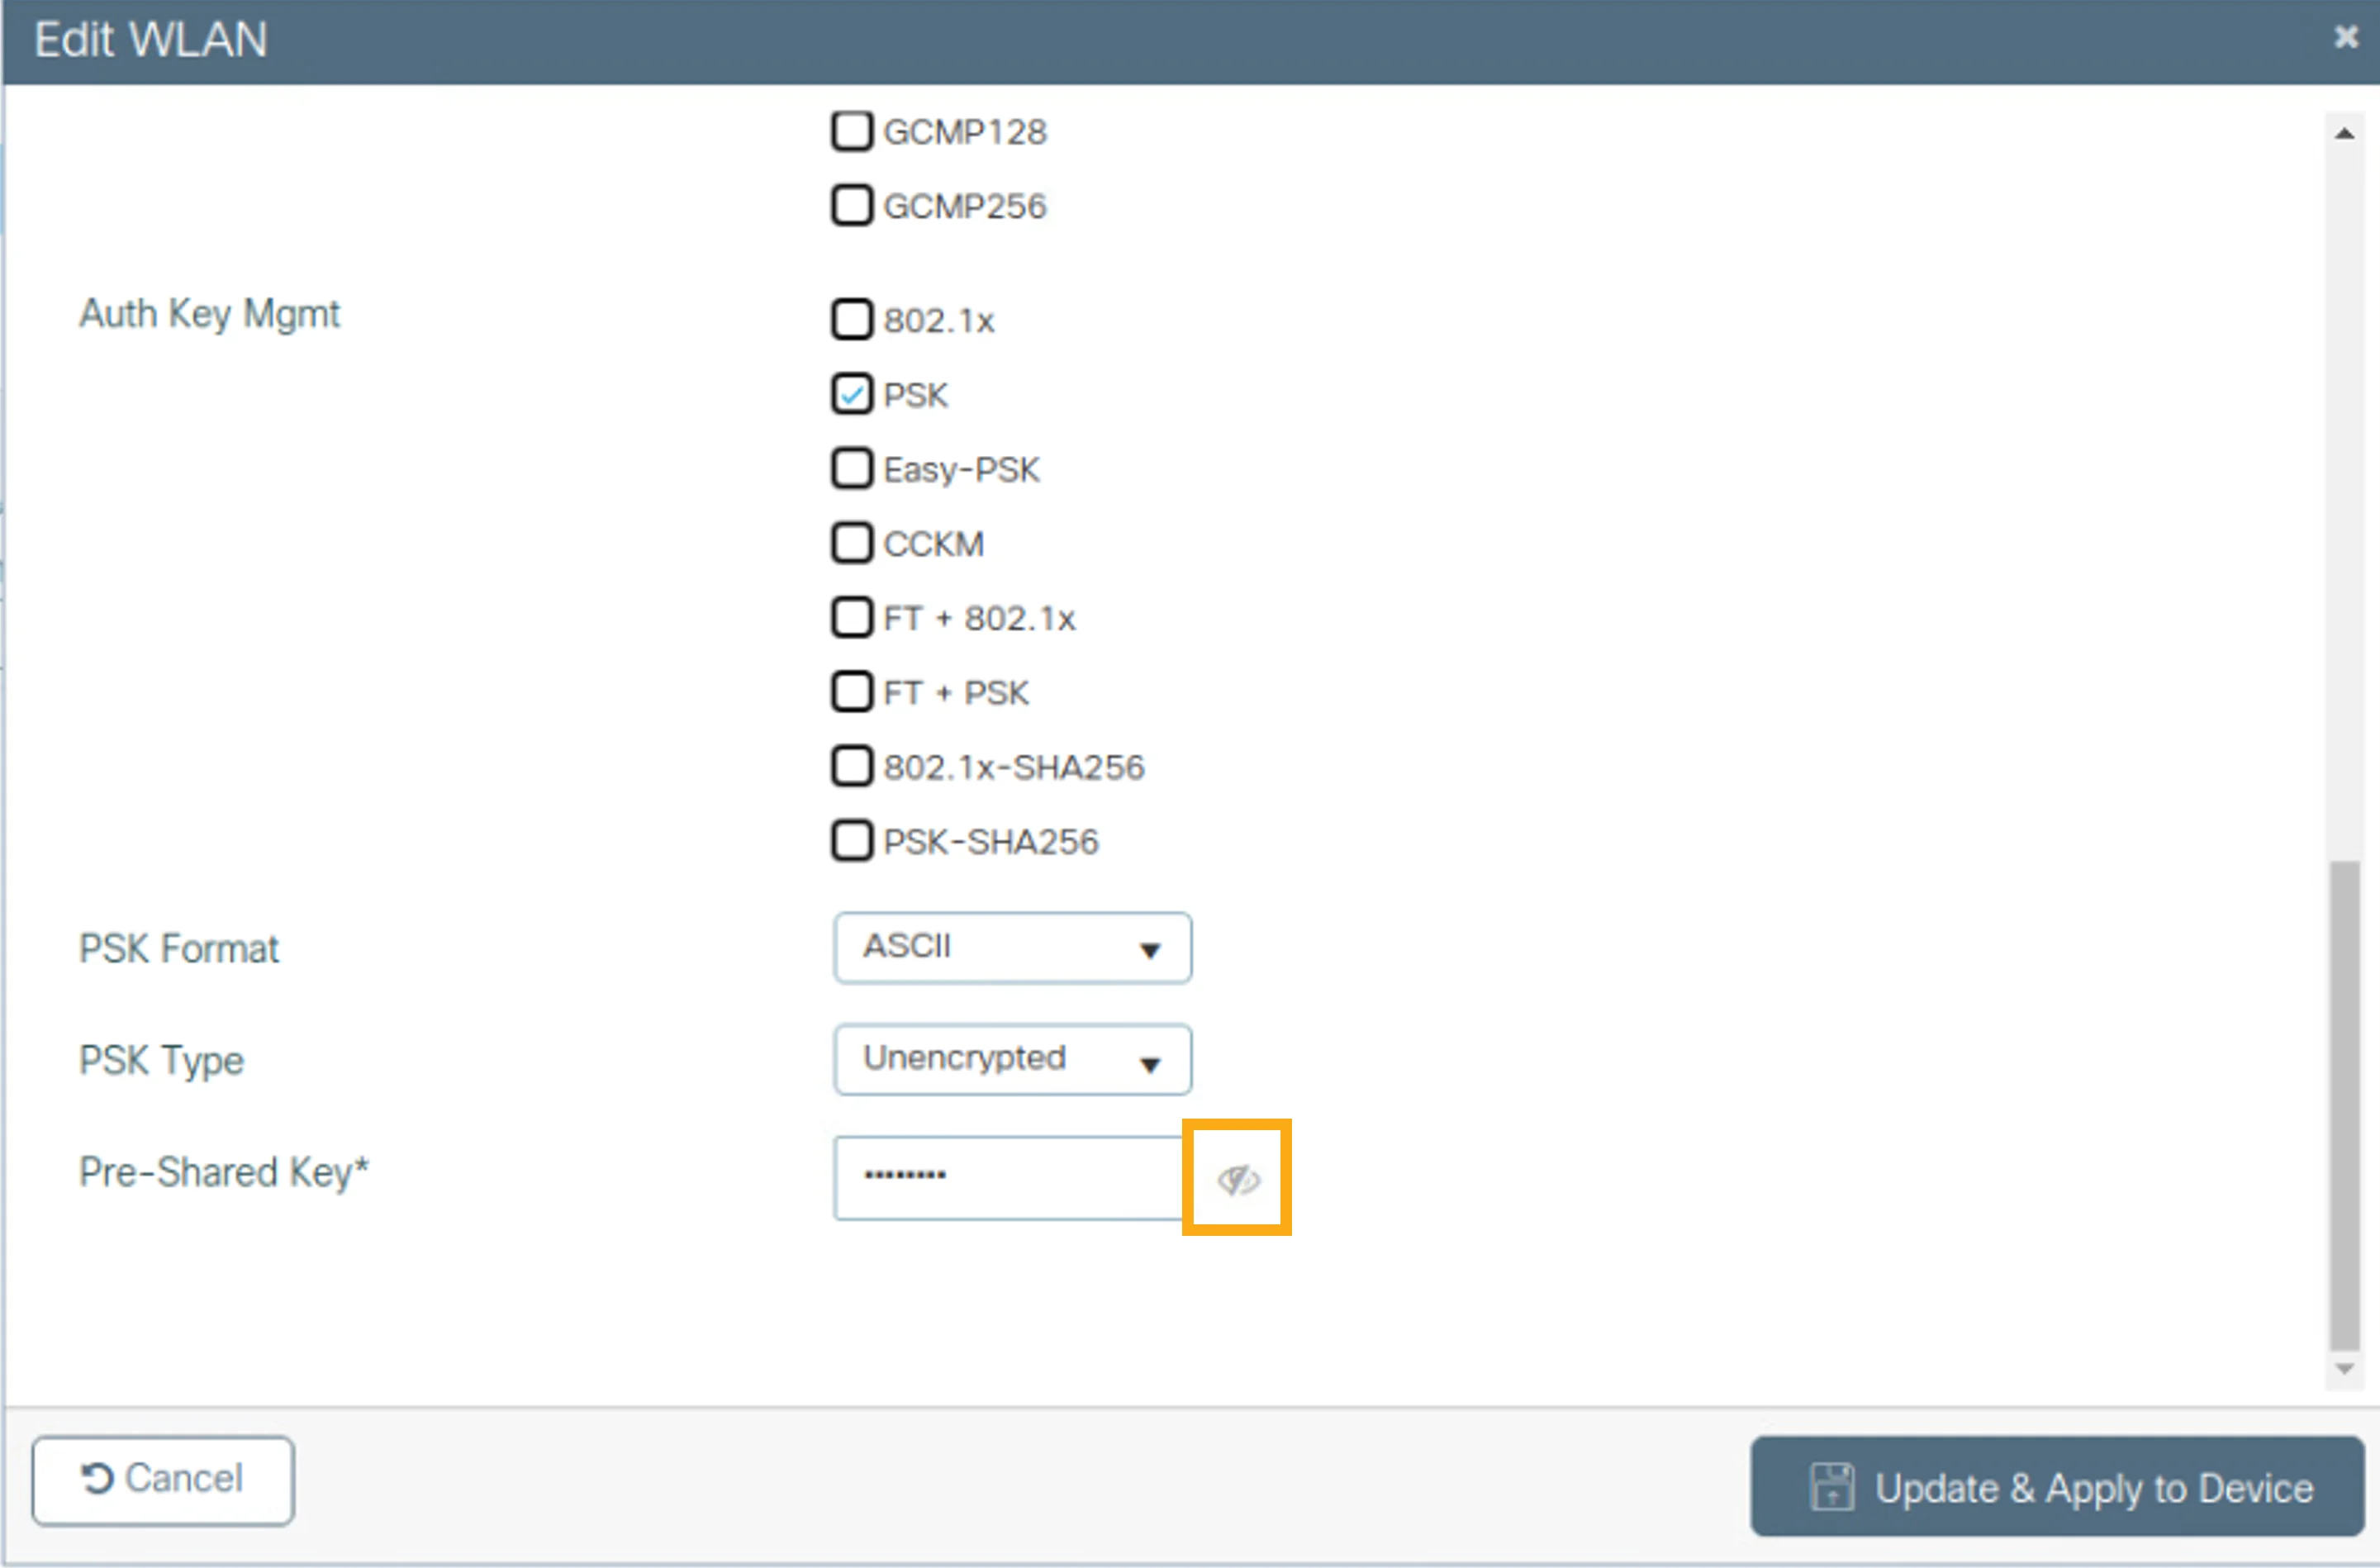
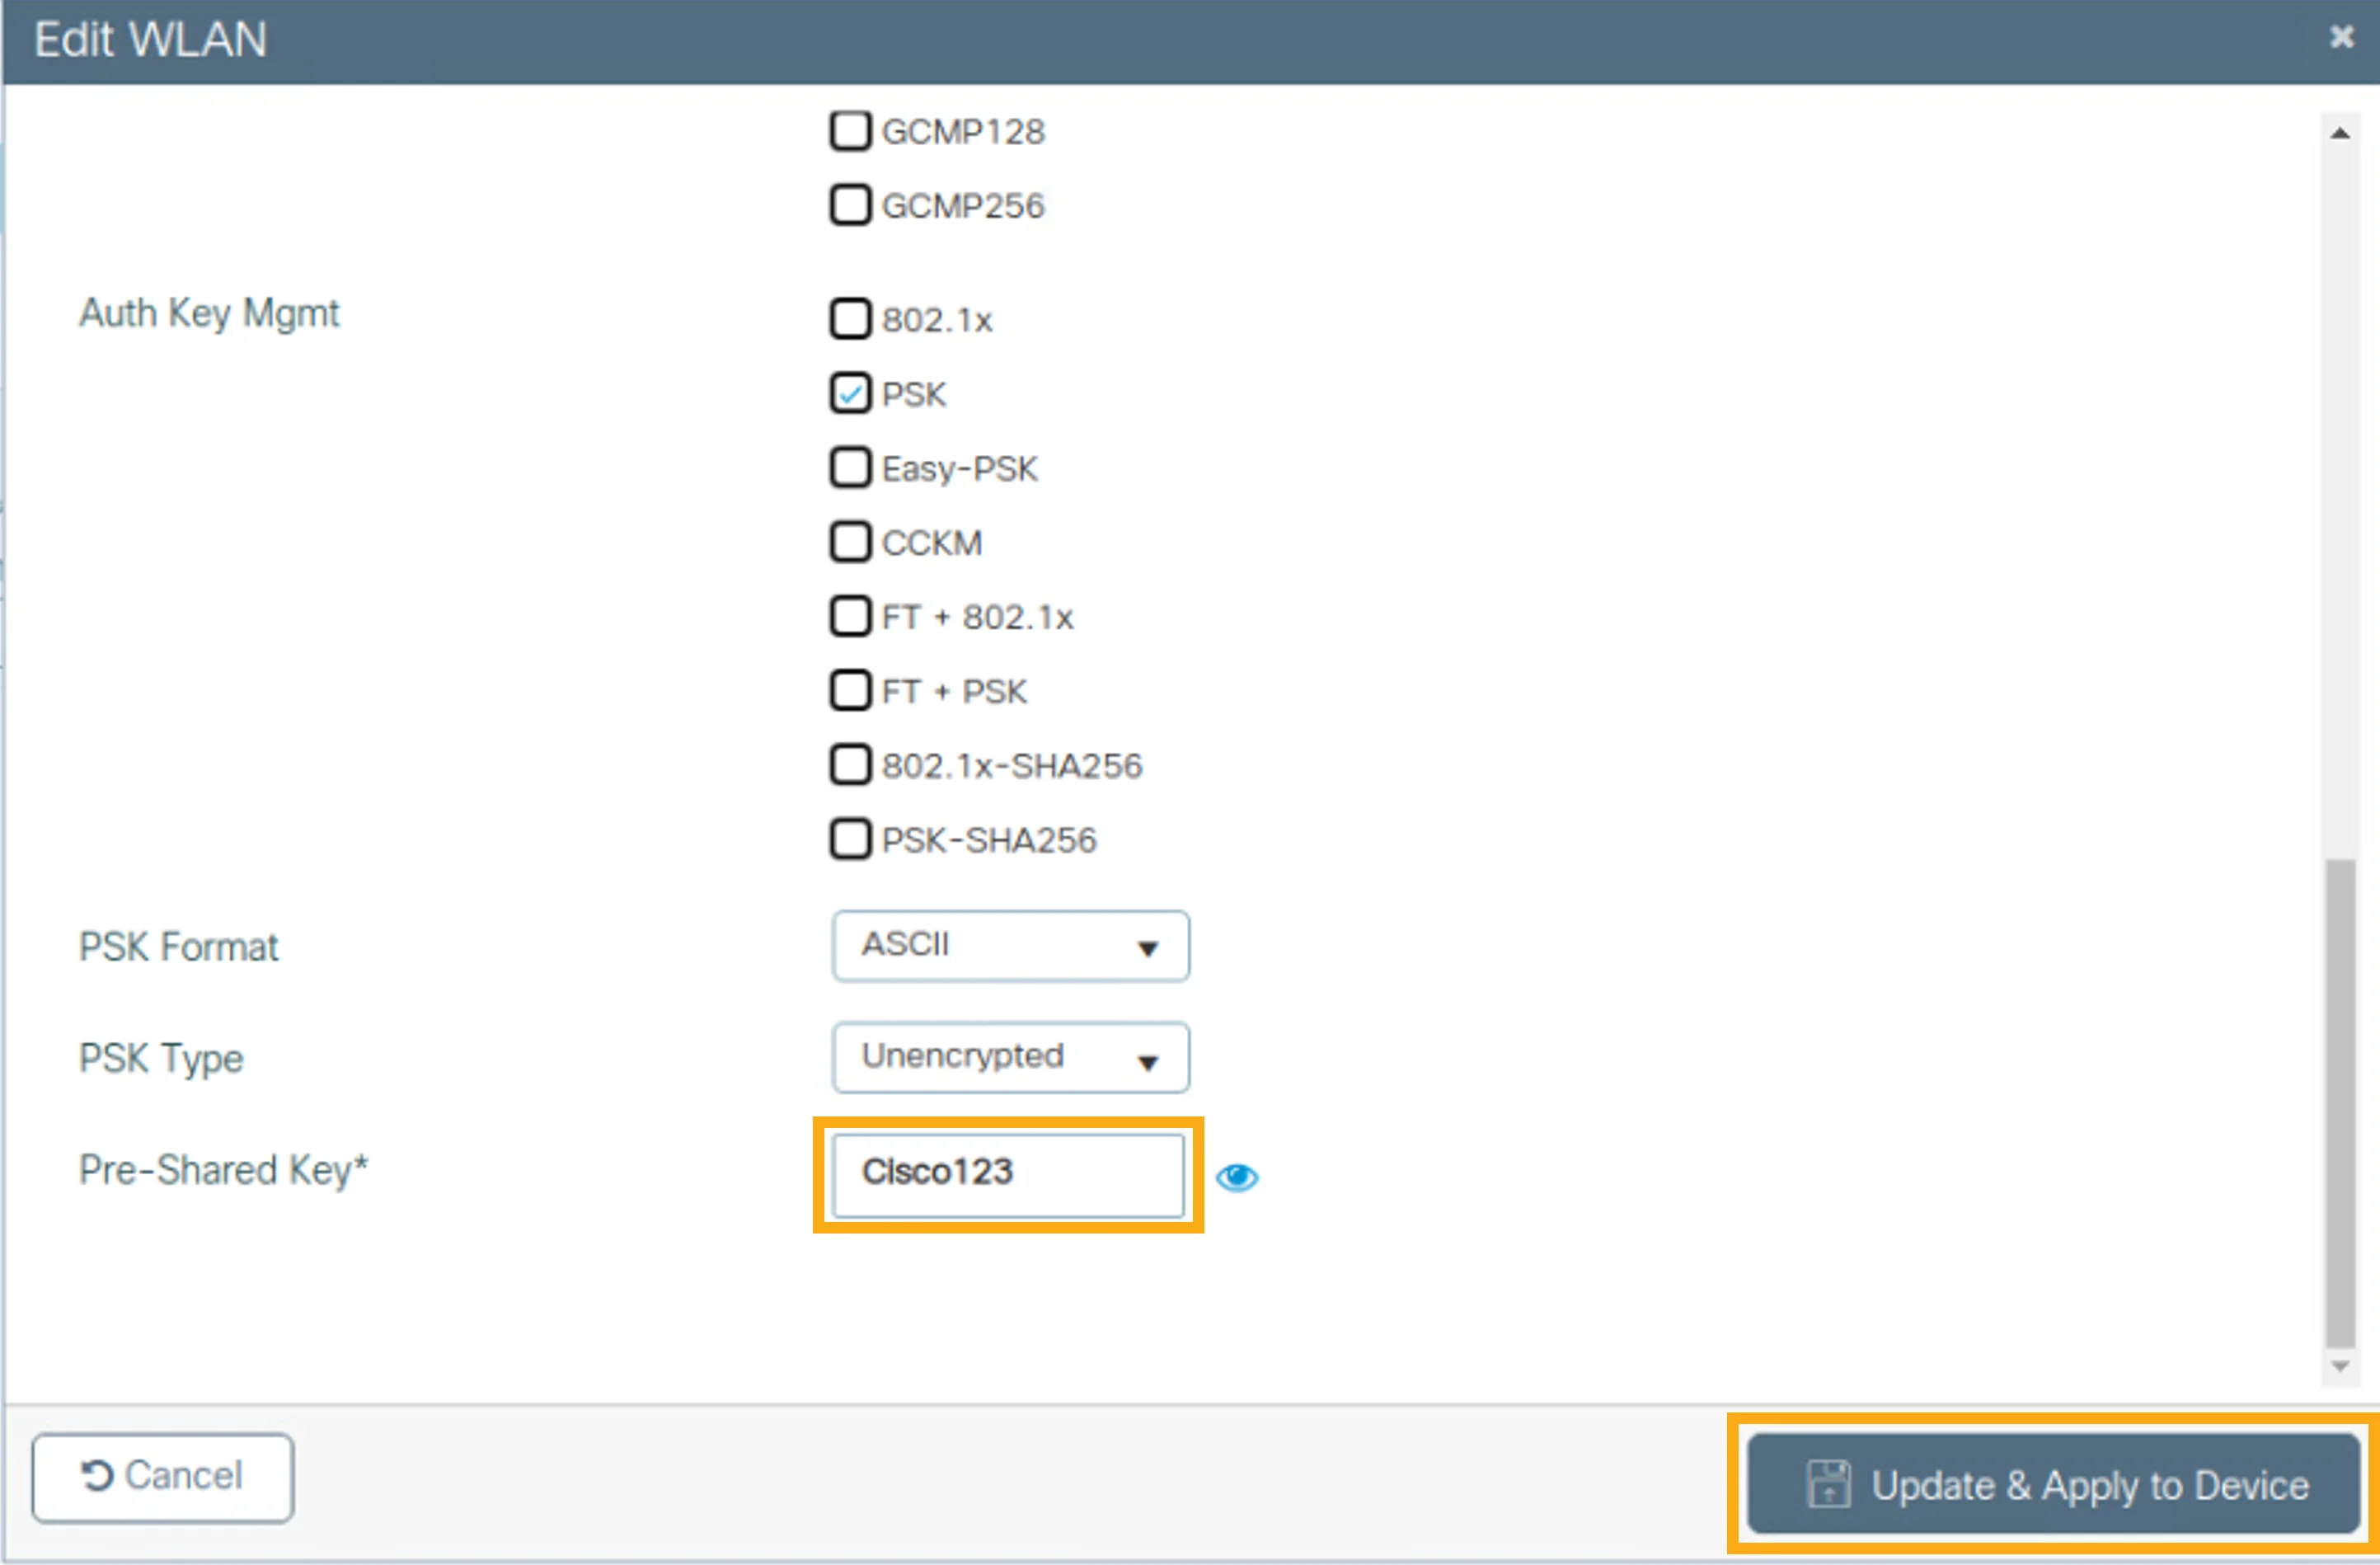
The key is now displayed in cleartext. Verify the key. If needed, edit the key.
金鑰現在以明文顯示。請驗證此金鑰,如有需要請進行編輯。
When the key is correct, click Update & Apply to Device.
確認金鑰正確後,按一下 Update & Apply to Device。
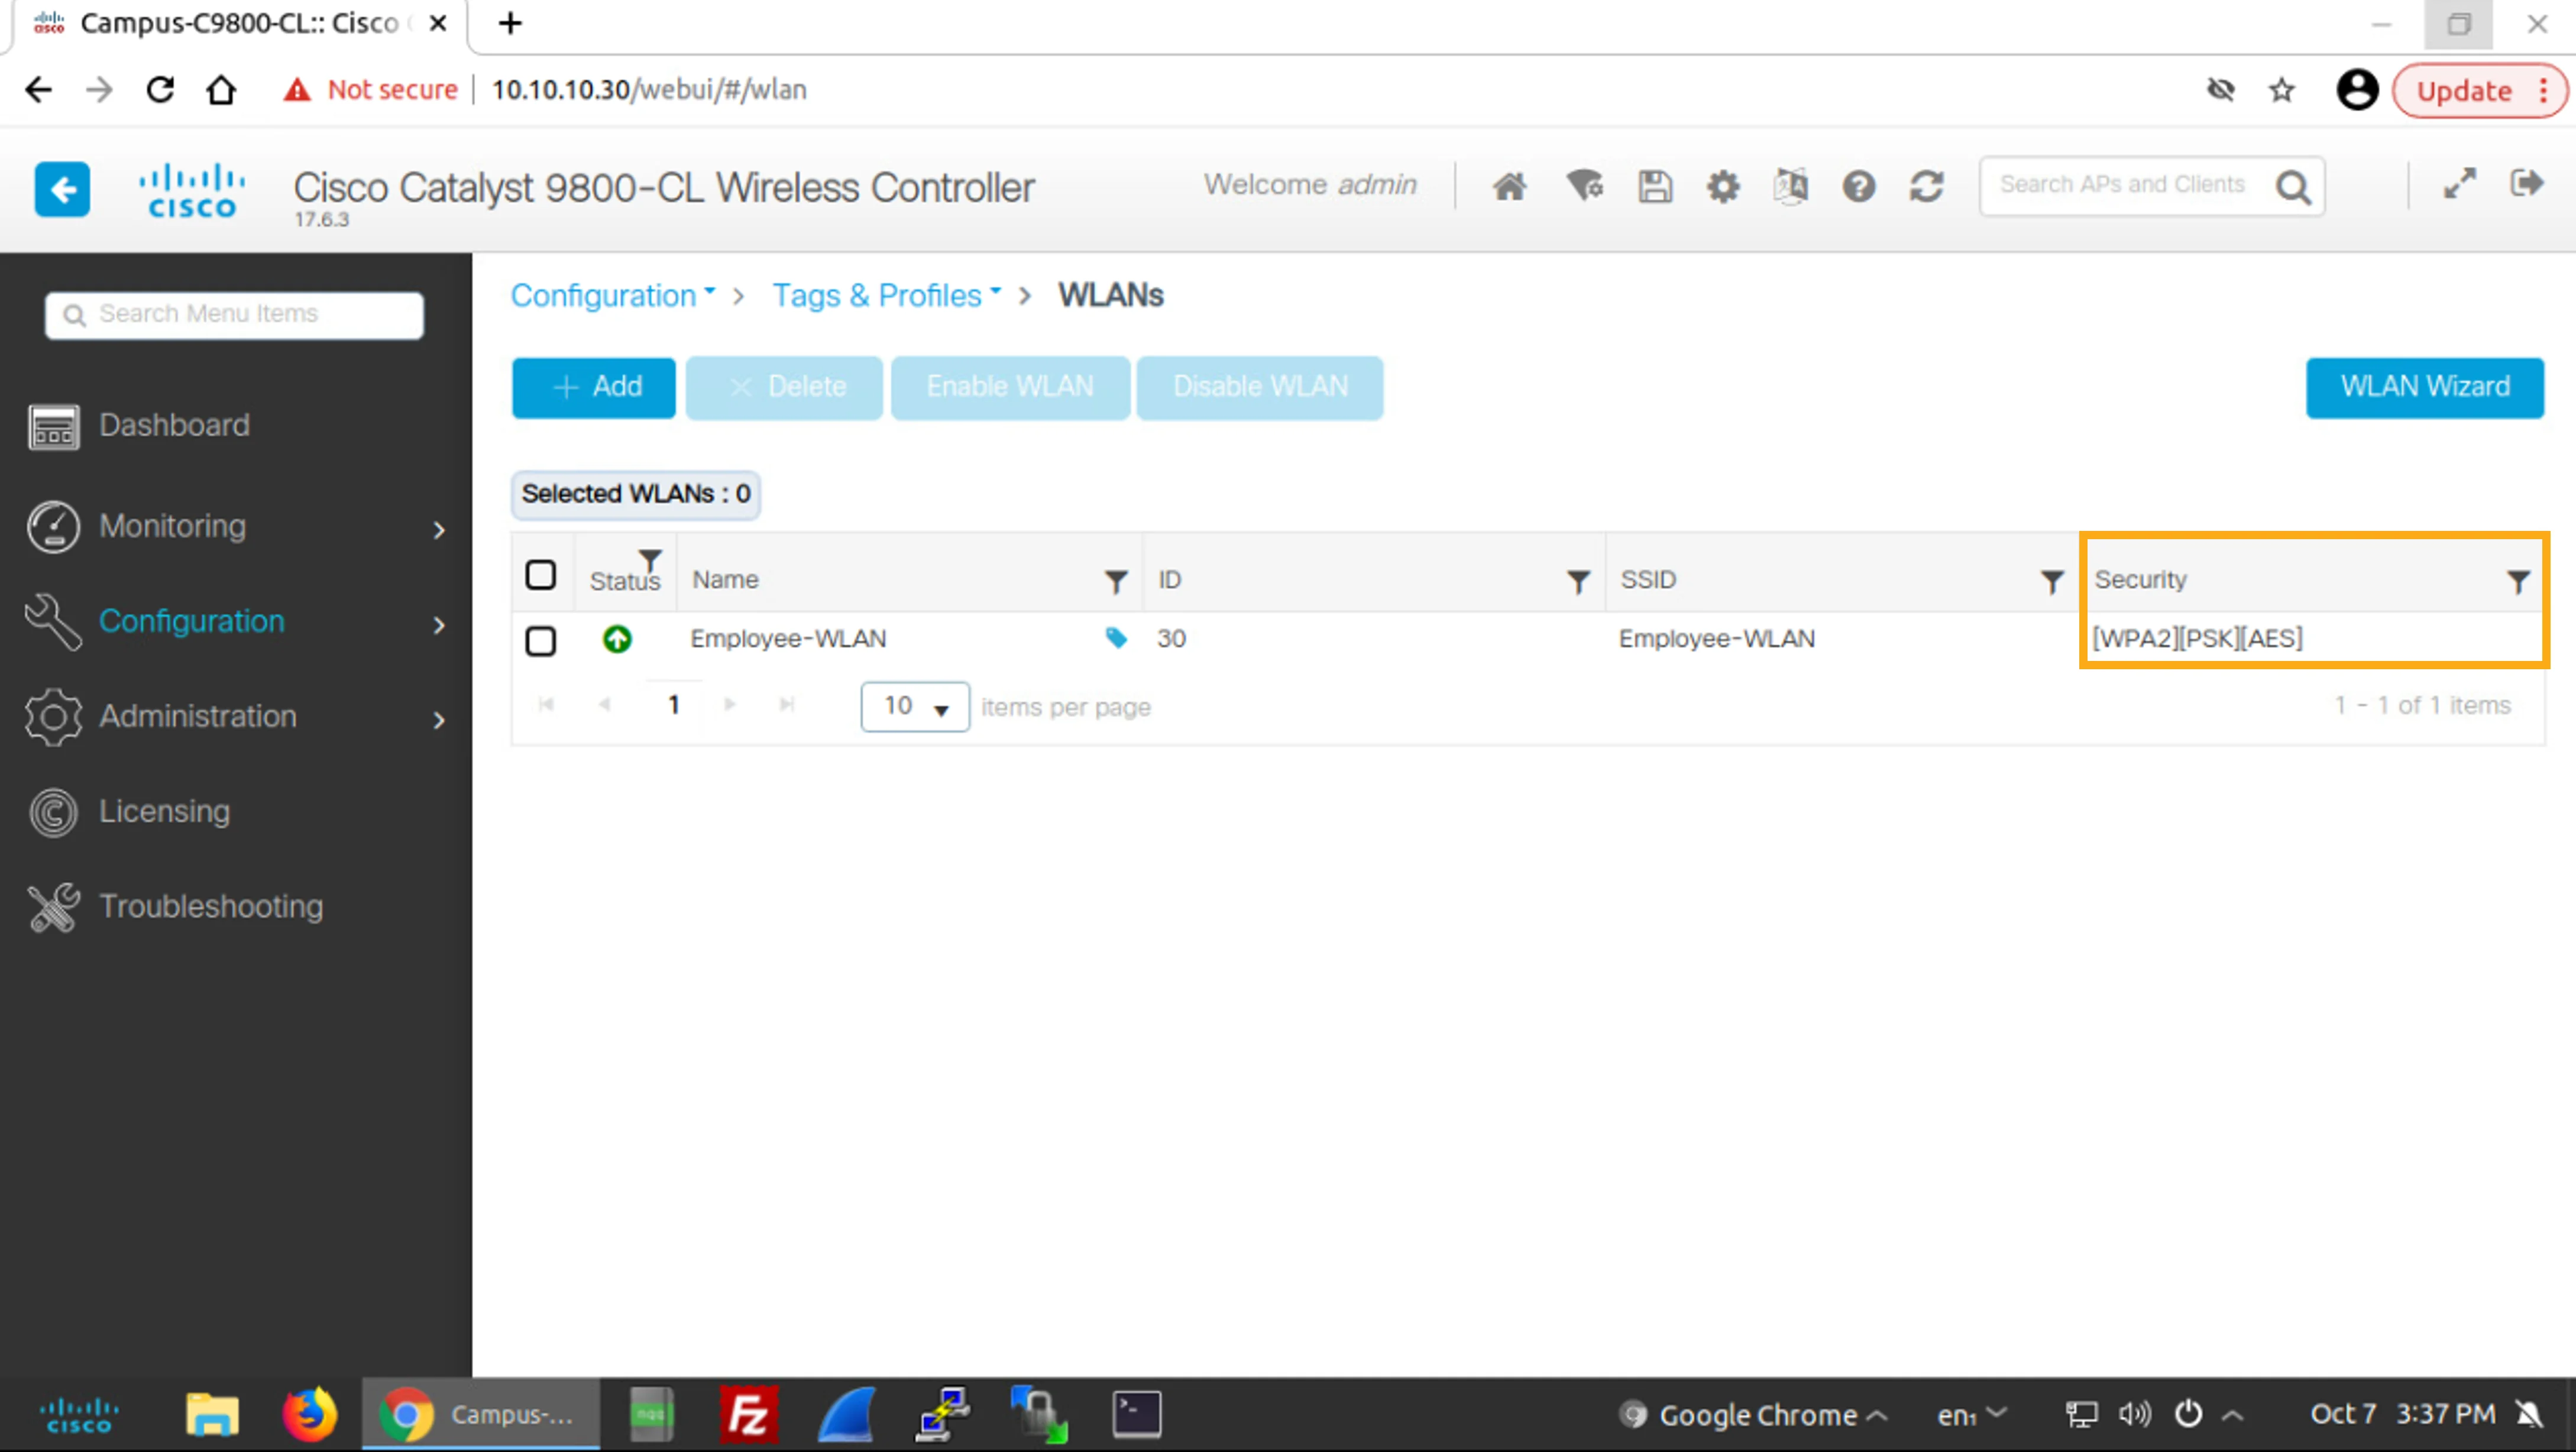
Back at the Configuration > Tags & Profiles > WLANs page that shows the configured WLANs, verify that the Employee-WLAN Security indicates the use of WPA2, PSK, and AES.
回到顯示已設定 WLAN 的 Configuration > Tags & Profiles > WLANs 頁面,驗證 Employee-WLAN 的 Security 是否顯示已使用 WPA2、PSK 及 AES。
Task 2: Verify Wireless Network Connectivity
任務 2:驗證無線網路連線
After changing the security settings of a wireless network, you should always make sure that you can access the network and test IP connectivity.
變更無線網路的安全性設定後,您應該務必確認能夠存取該網路,並測試 IP 連線。
You will now verify proper operation of the Employee-WLAN wireless network, for which you enabled WPA2 PSK in the previous task.
您現在將驗證 Employee-WLAN 無線網路的正常運作,該網路已在前一個任務中啟用 WPA2 PSK。
First, you will connect to the wireless network from two client PCs (Client PC 1 and Client PC 1). Then you will verify IP connectivity, and finally, you will monitor the client connections from the Campus WLC web GUI.
首先,您將從兩台用戶端 PC(Client PC 1 及 Client PC 1)連線至無線網路。接著您將驗證 IP 連線,最後從 Campus WLC 網頁 GUI 監控用戶端連線。
Activity
活動
Connect Client PC 1 to the WLAN
將 Client PC 1 連線至 WLAN
First, you will connect Client PC 1 to WLAN.
首先,您將把 Client PC 1 連線至 WLAN。
Click the Switch to Client PC 1 button, which is located at the bottom-right corner of the desktop to switch from the Admin PC to Client PC 1.
按一下位於桌面右下角的 Switch to Client PC 1 按鈕,從 Admin PC 切換至 Client PC 1。
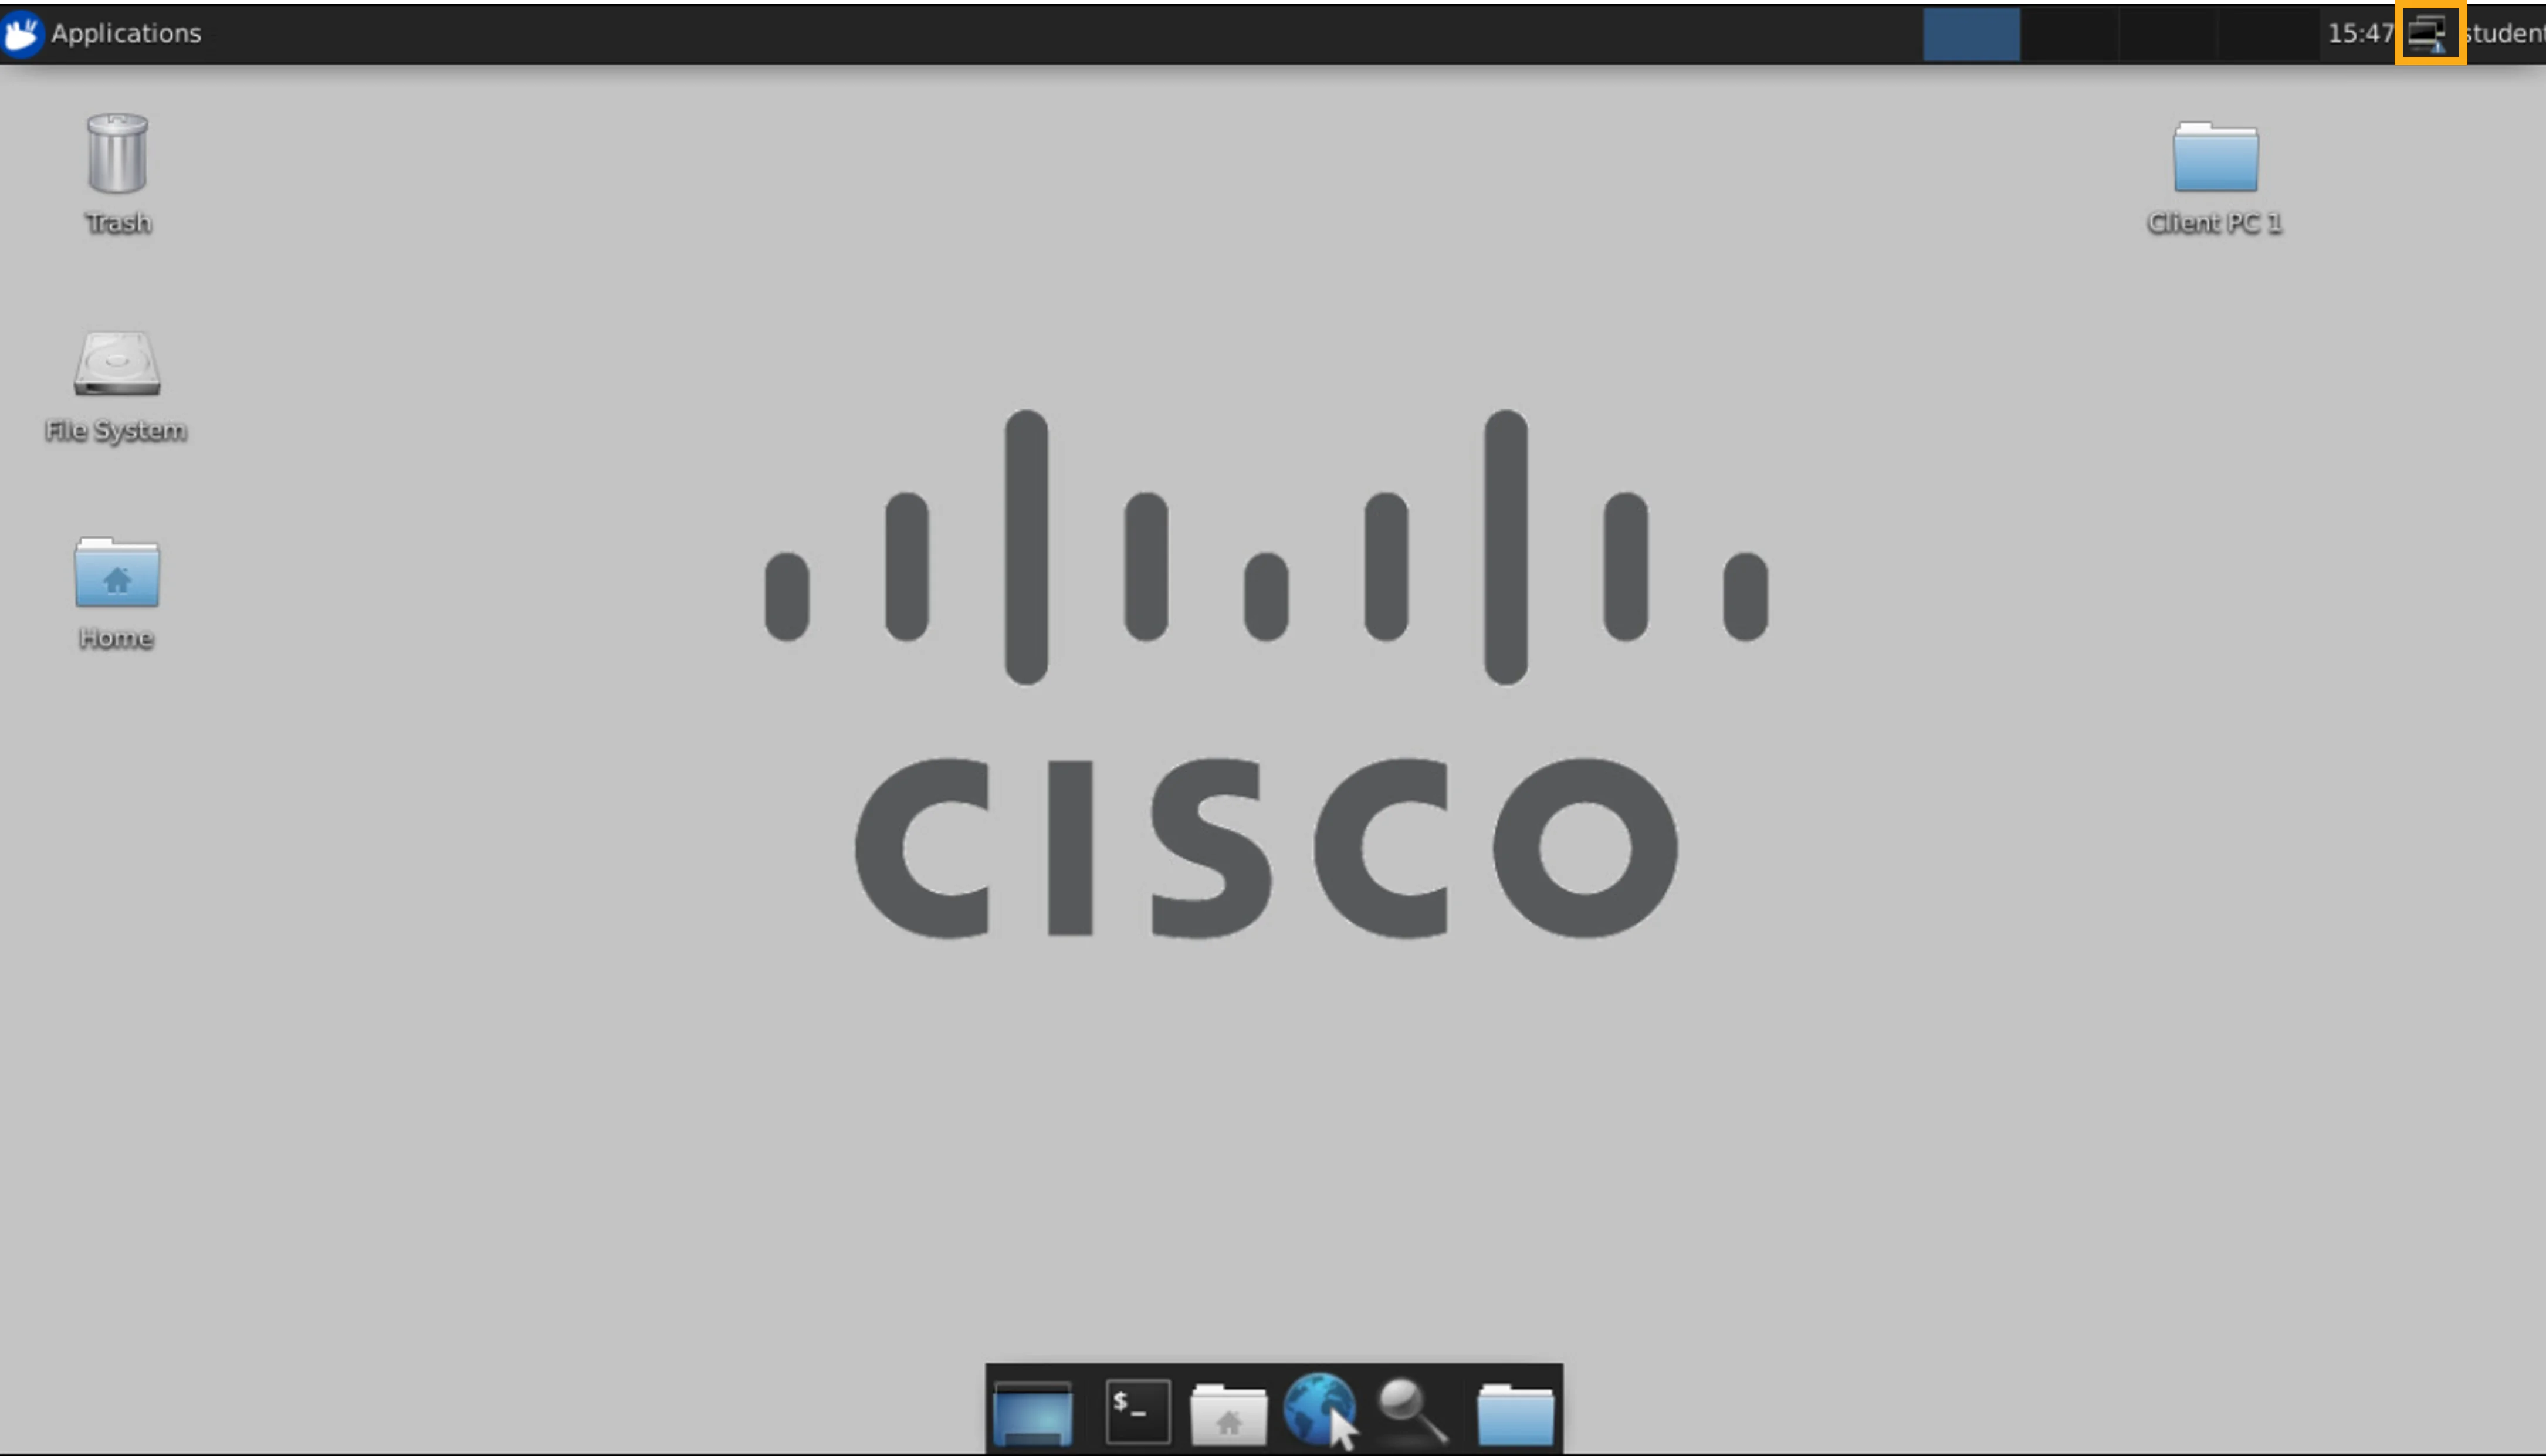
On Client PC 1, click the Network icon, which is in the top-right corner of the desktop.
在 Client PC 1 上,按一下位於桌面右上角的 Network 圖示。
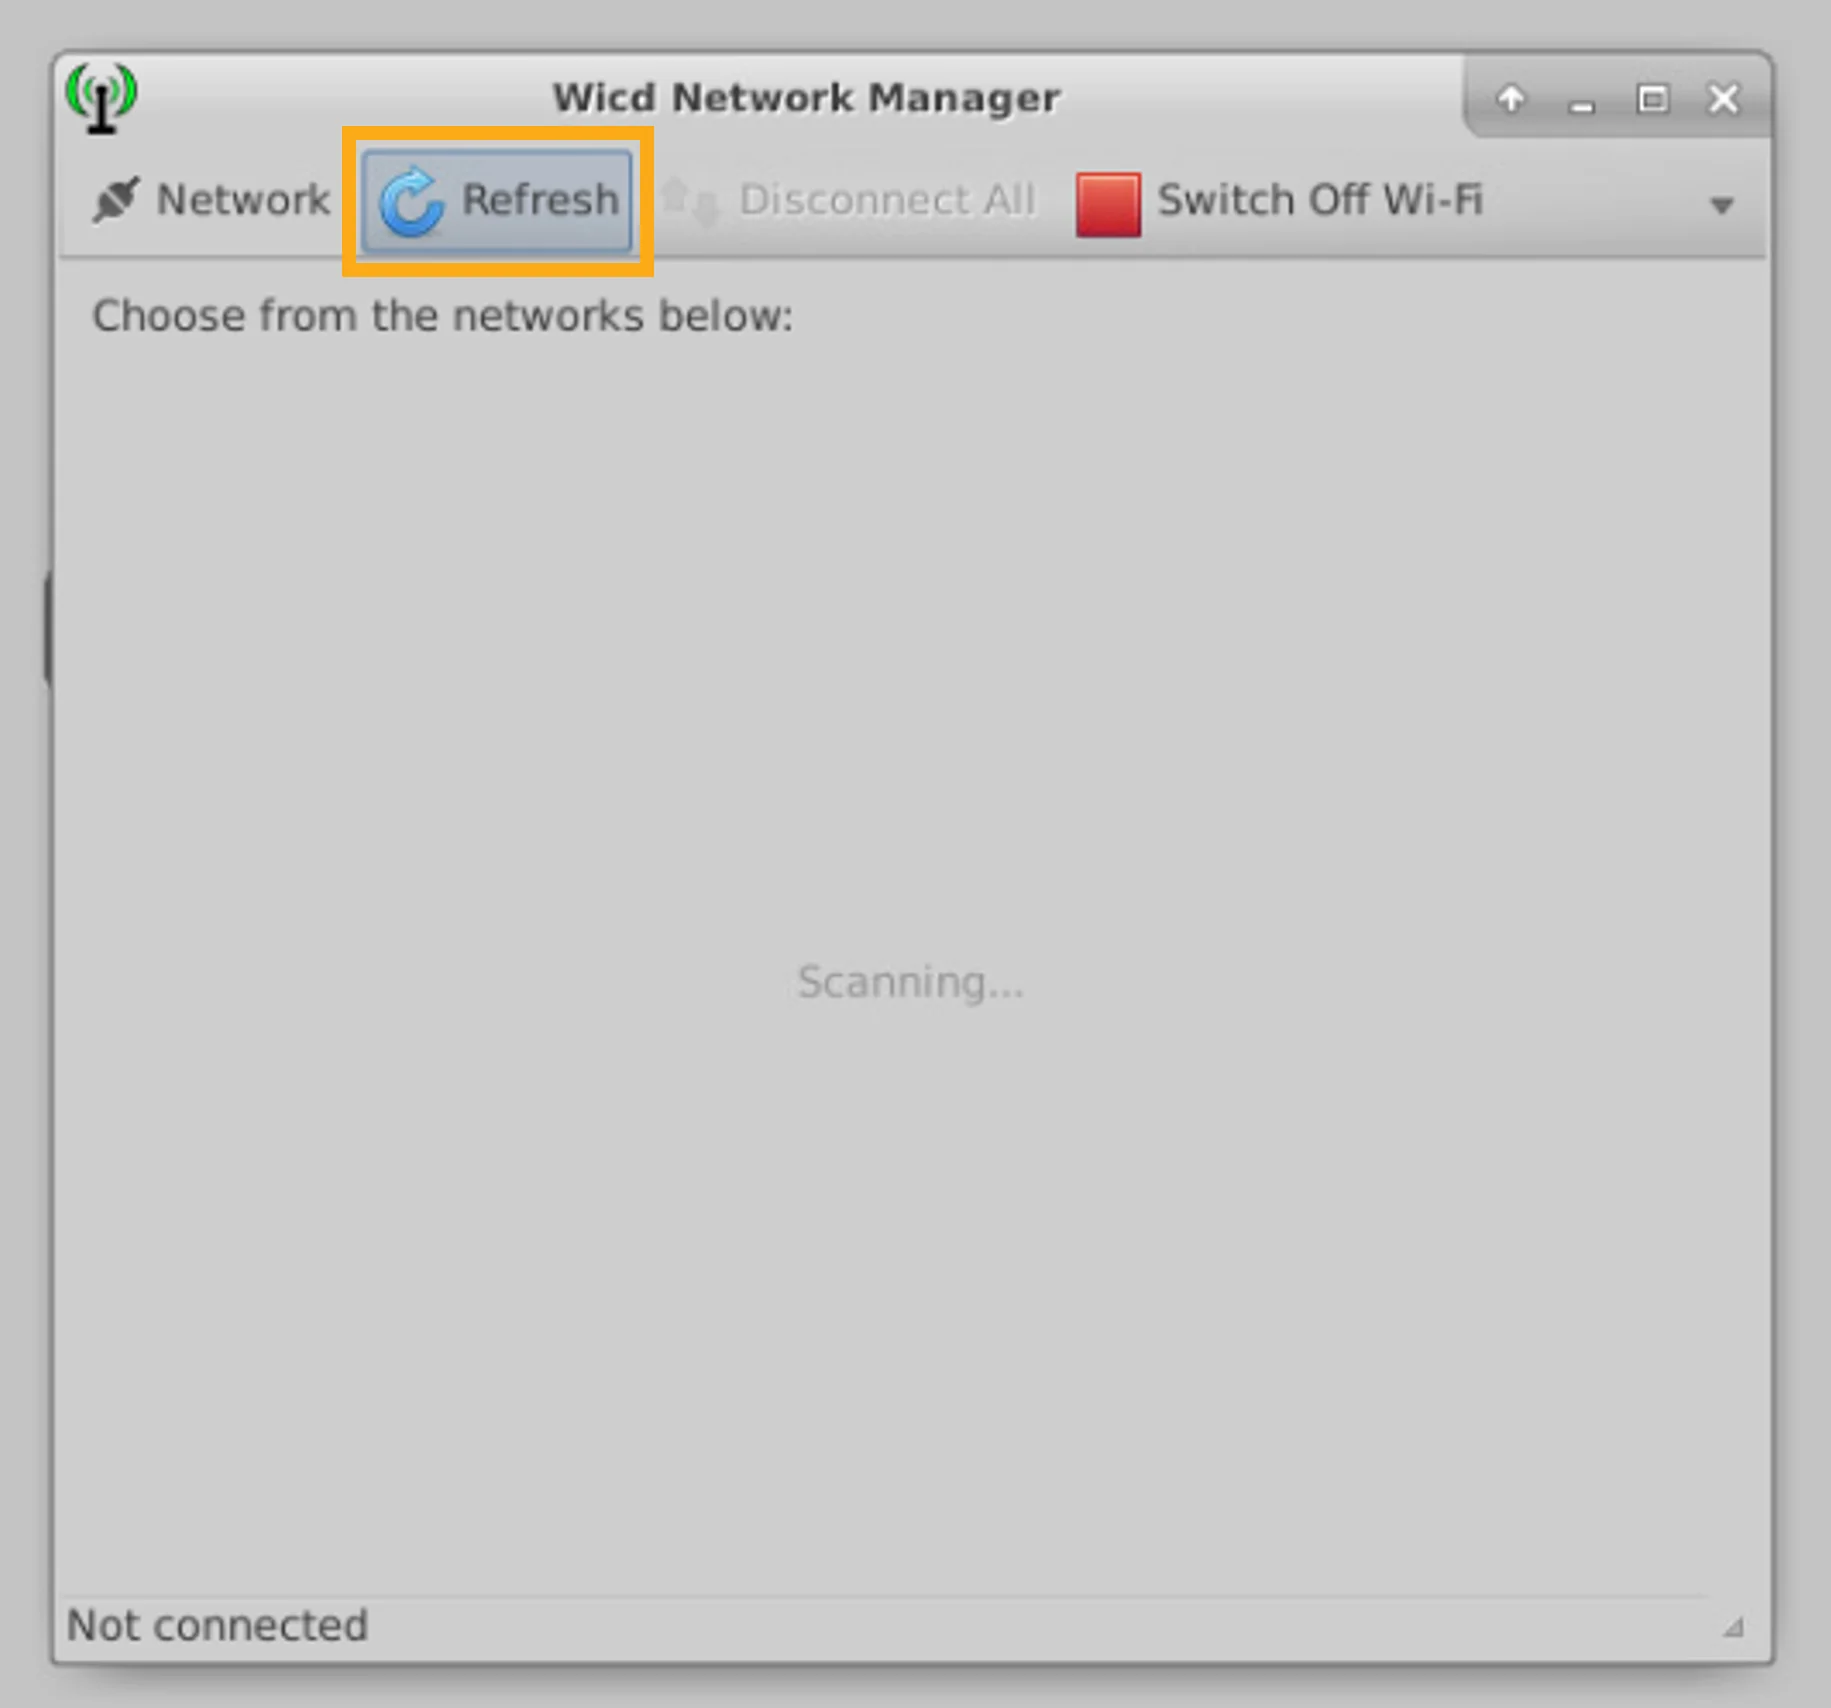
In the Wicd Network Manager window, click Refresh to scan for available networks.
在 Wicd Network Manager 視窗中,按一下 Refresh 掃描可用的網路。
The Employee-WLAN network is shown. Note that the wireless client indicates that the network is secured by WPA2.
畫面顯示 Employee-WLAN 網路。請注意,無線用戶端顯示該網路已由 WPA2 保護。
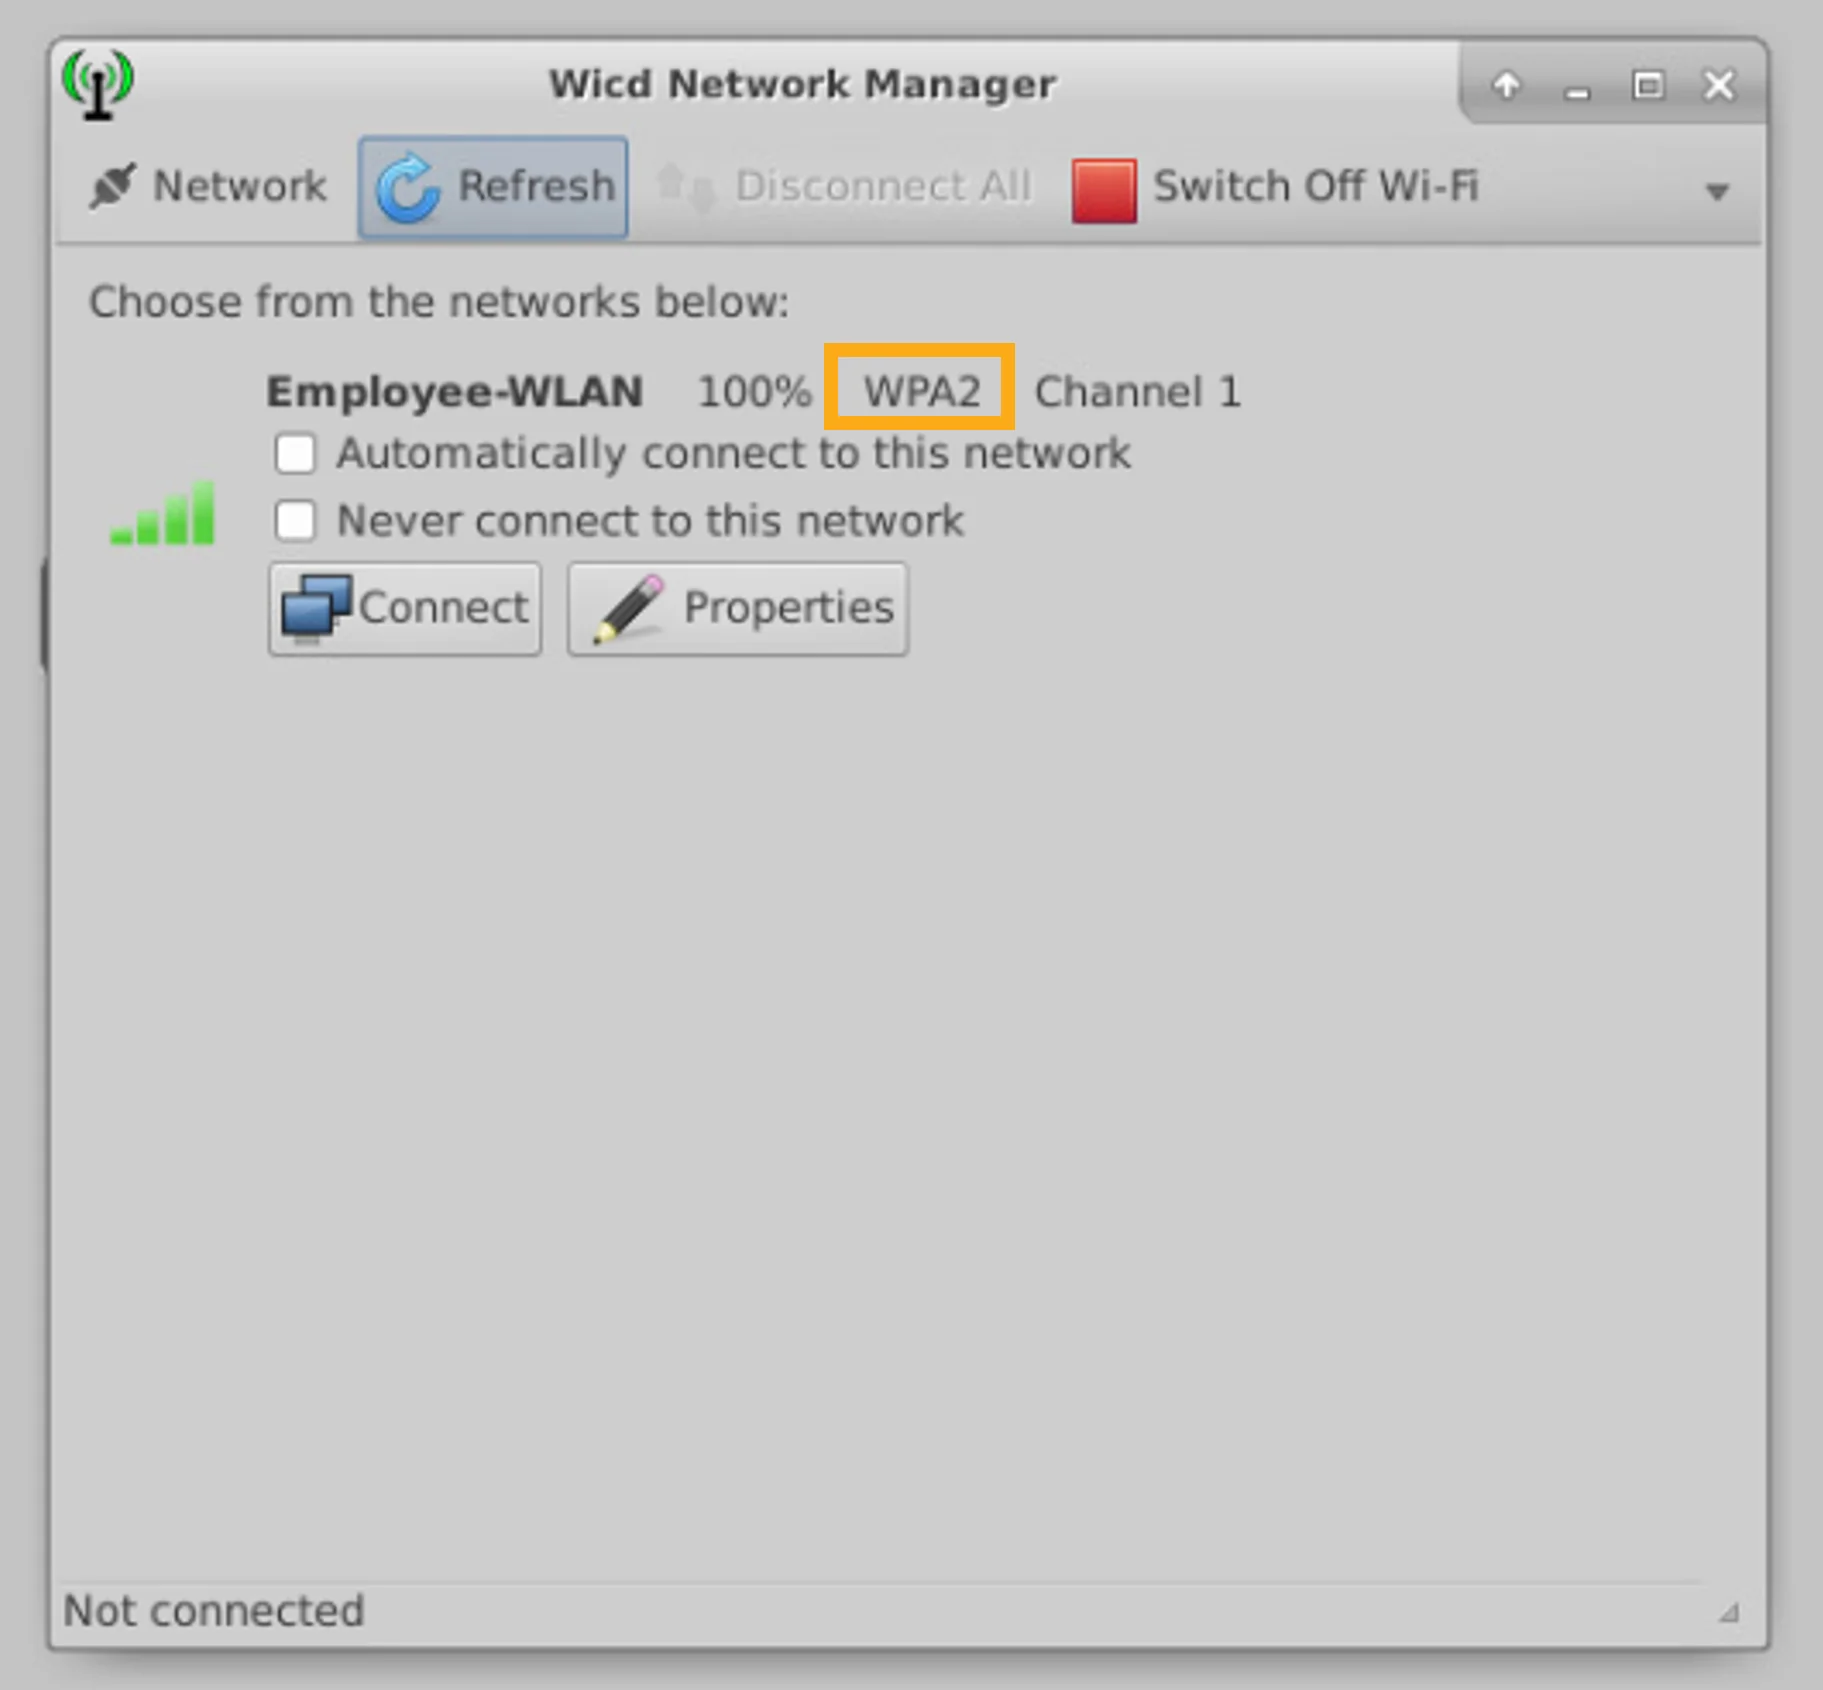
Click Connect to attempt to connect to the Employee-WLAN.
按一下 Connect,嘗試連線至 Employee-WLAN。
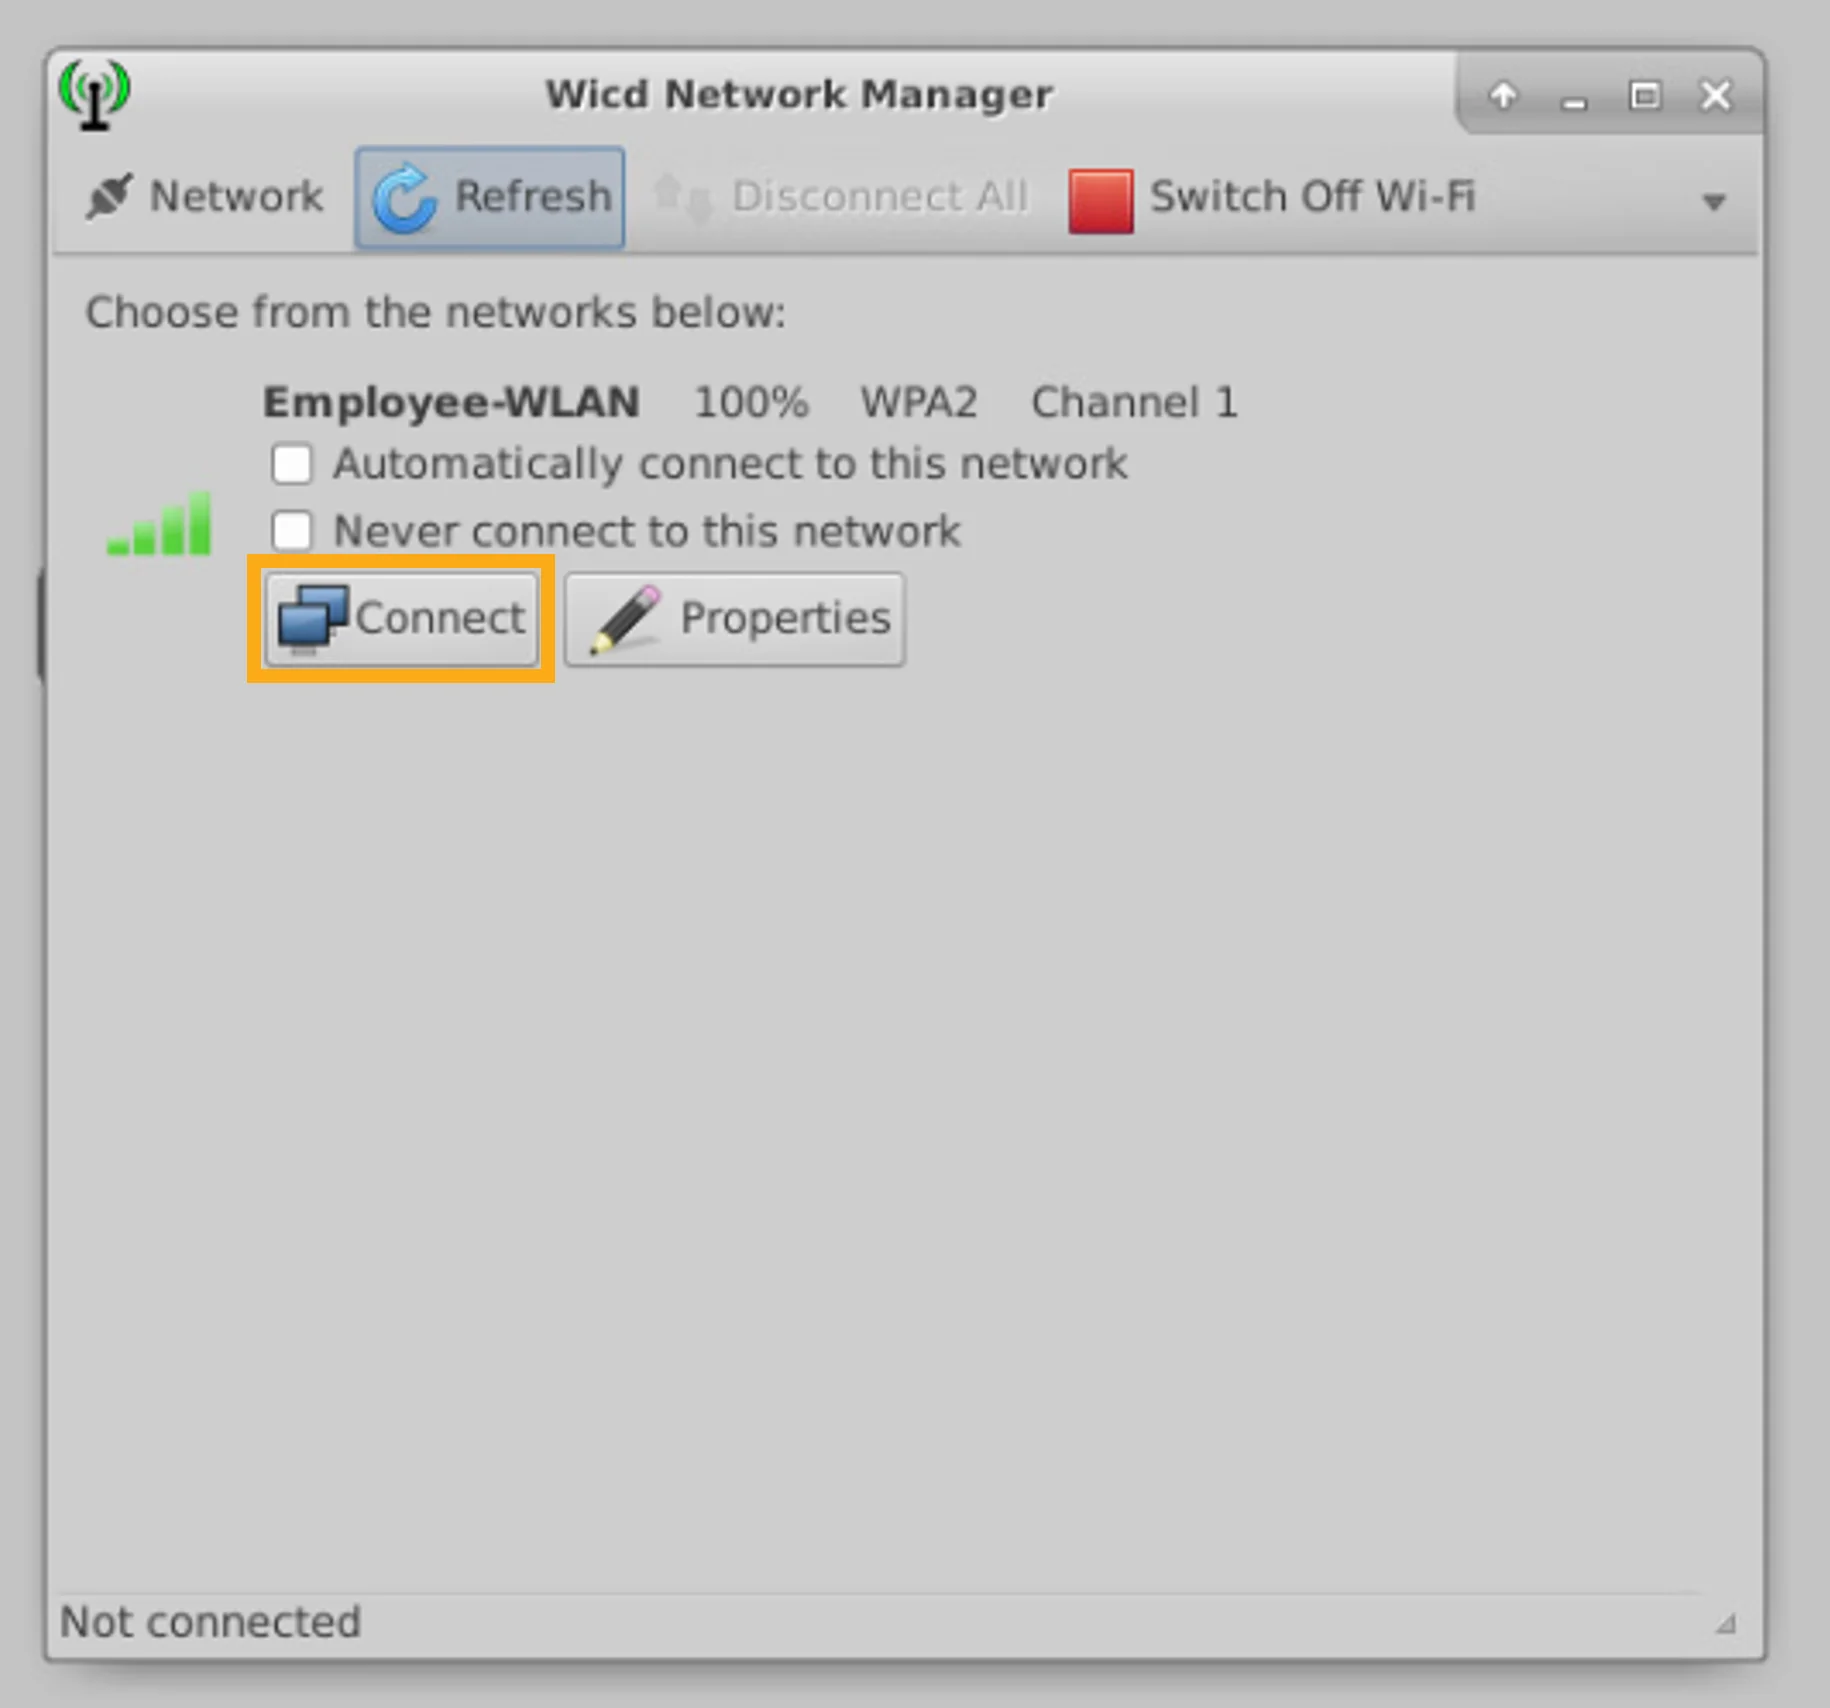
Note the message that encryption is required and click OK to confirm.
請注意顯示需要加密的訊息,按一下 OK 確認。
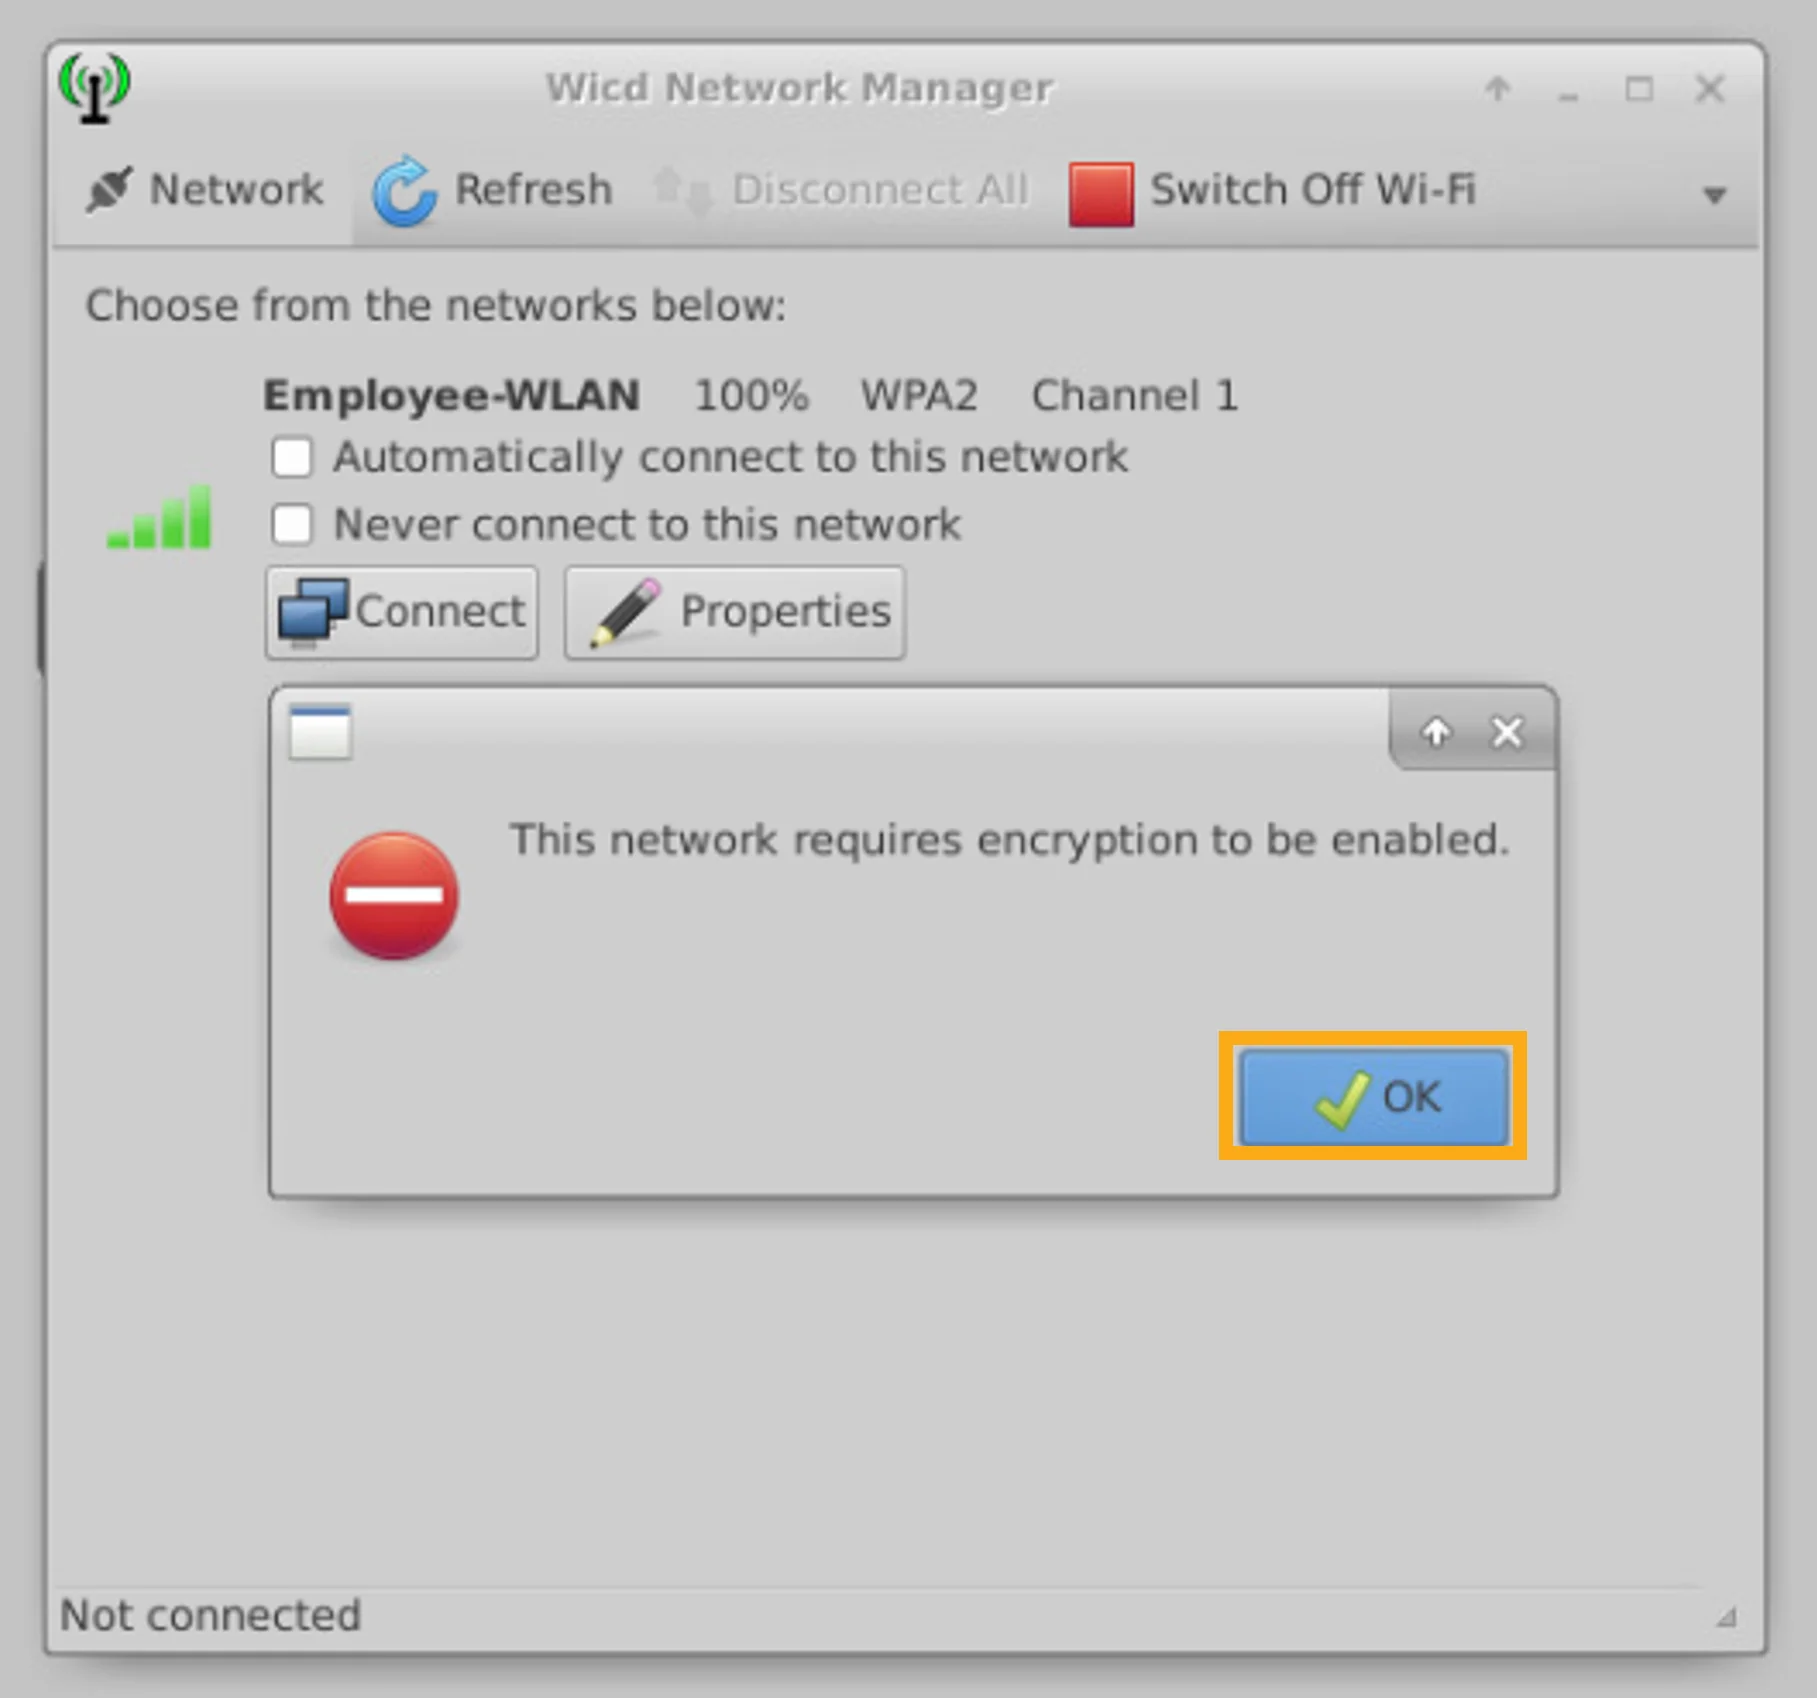
Set the Security Type and the Password
設定安全性類型與密碼
The Employee-WLAN - Properties window appears. The Use Encryption check box is automatically set, because this WLAN requires WPA2. Set the security type and the password as follows.
系統會顯示 Employee-WLAN - Properties 視窗。由於此 WLAN 需要 WPA2,Use Encryption 核取方塊會自動勾選。請依下列方式設定安全性類型與密碼。
Security type Security type | WPA 1/2 (Passphrase) WPA 1/2 (Passphrase) |
Preshared key Preshared key | Cisco123 Cisco123 |
Click the currently selected security type WPA 1/2 (Hex [0-9/A-F]) to display all security options in the drop-down list.
按一下目前選取的安全性類型 WPA 1/2 (Hex [0-9/A-F]),以在下拉式清單中顯示所有安全性選項。
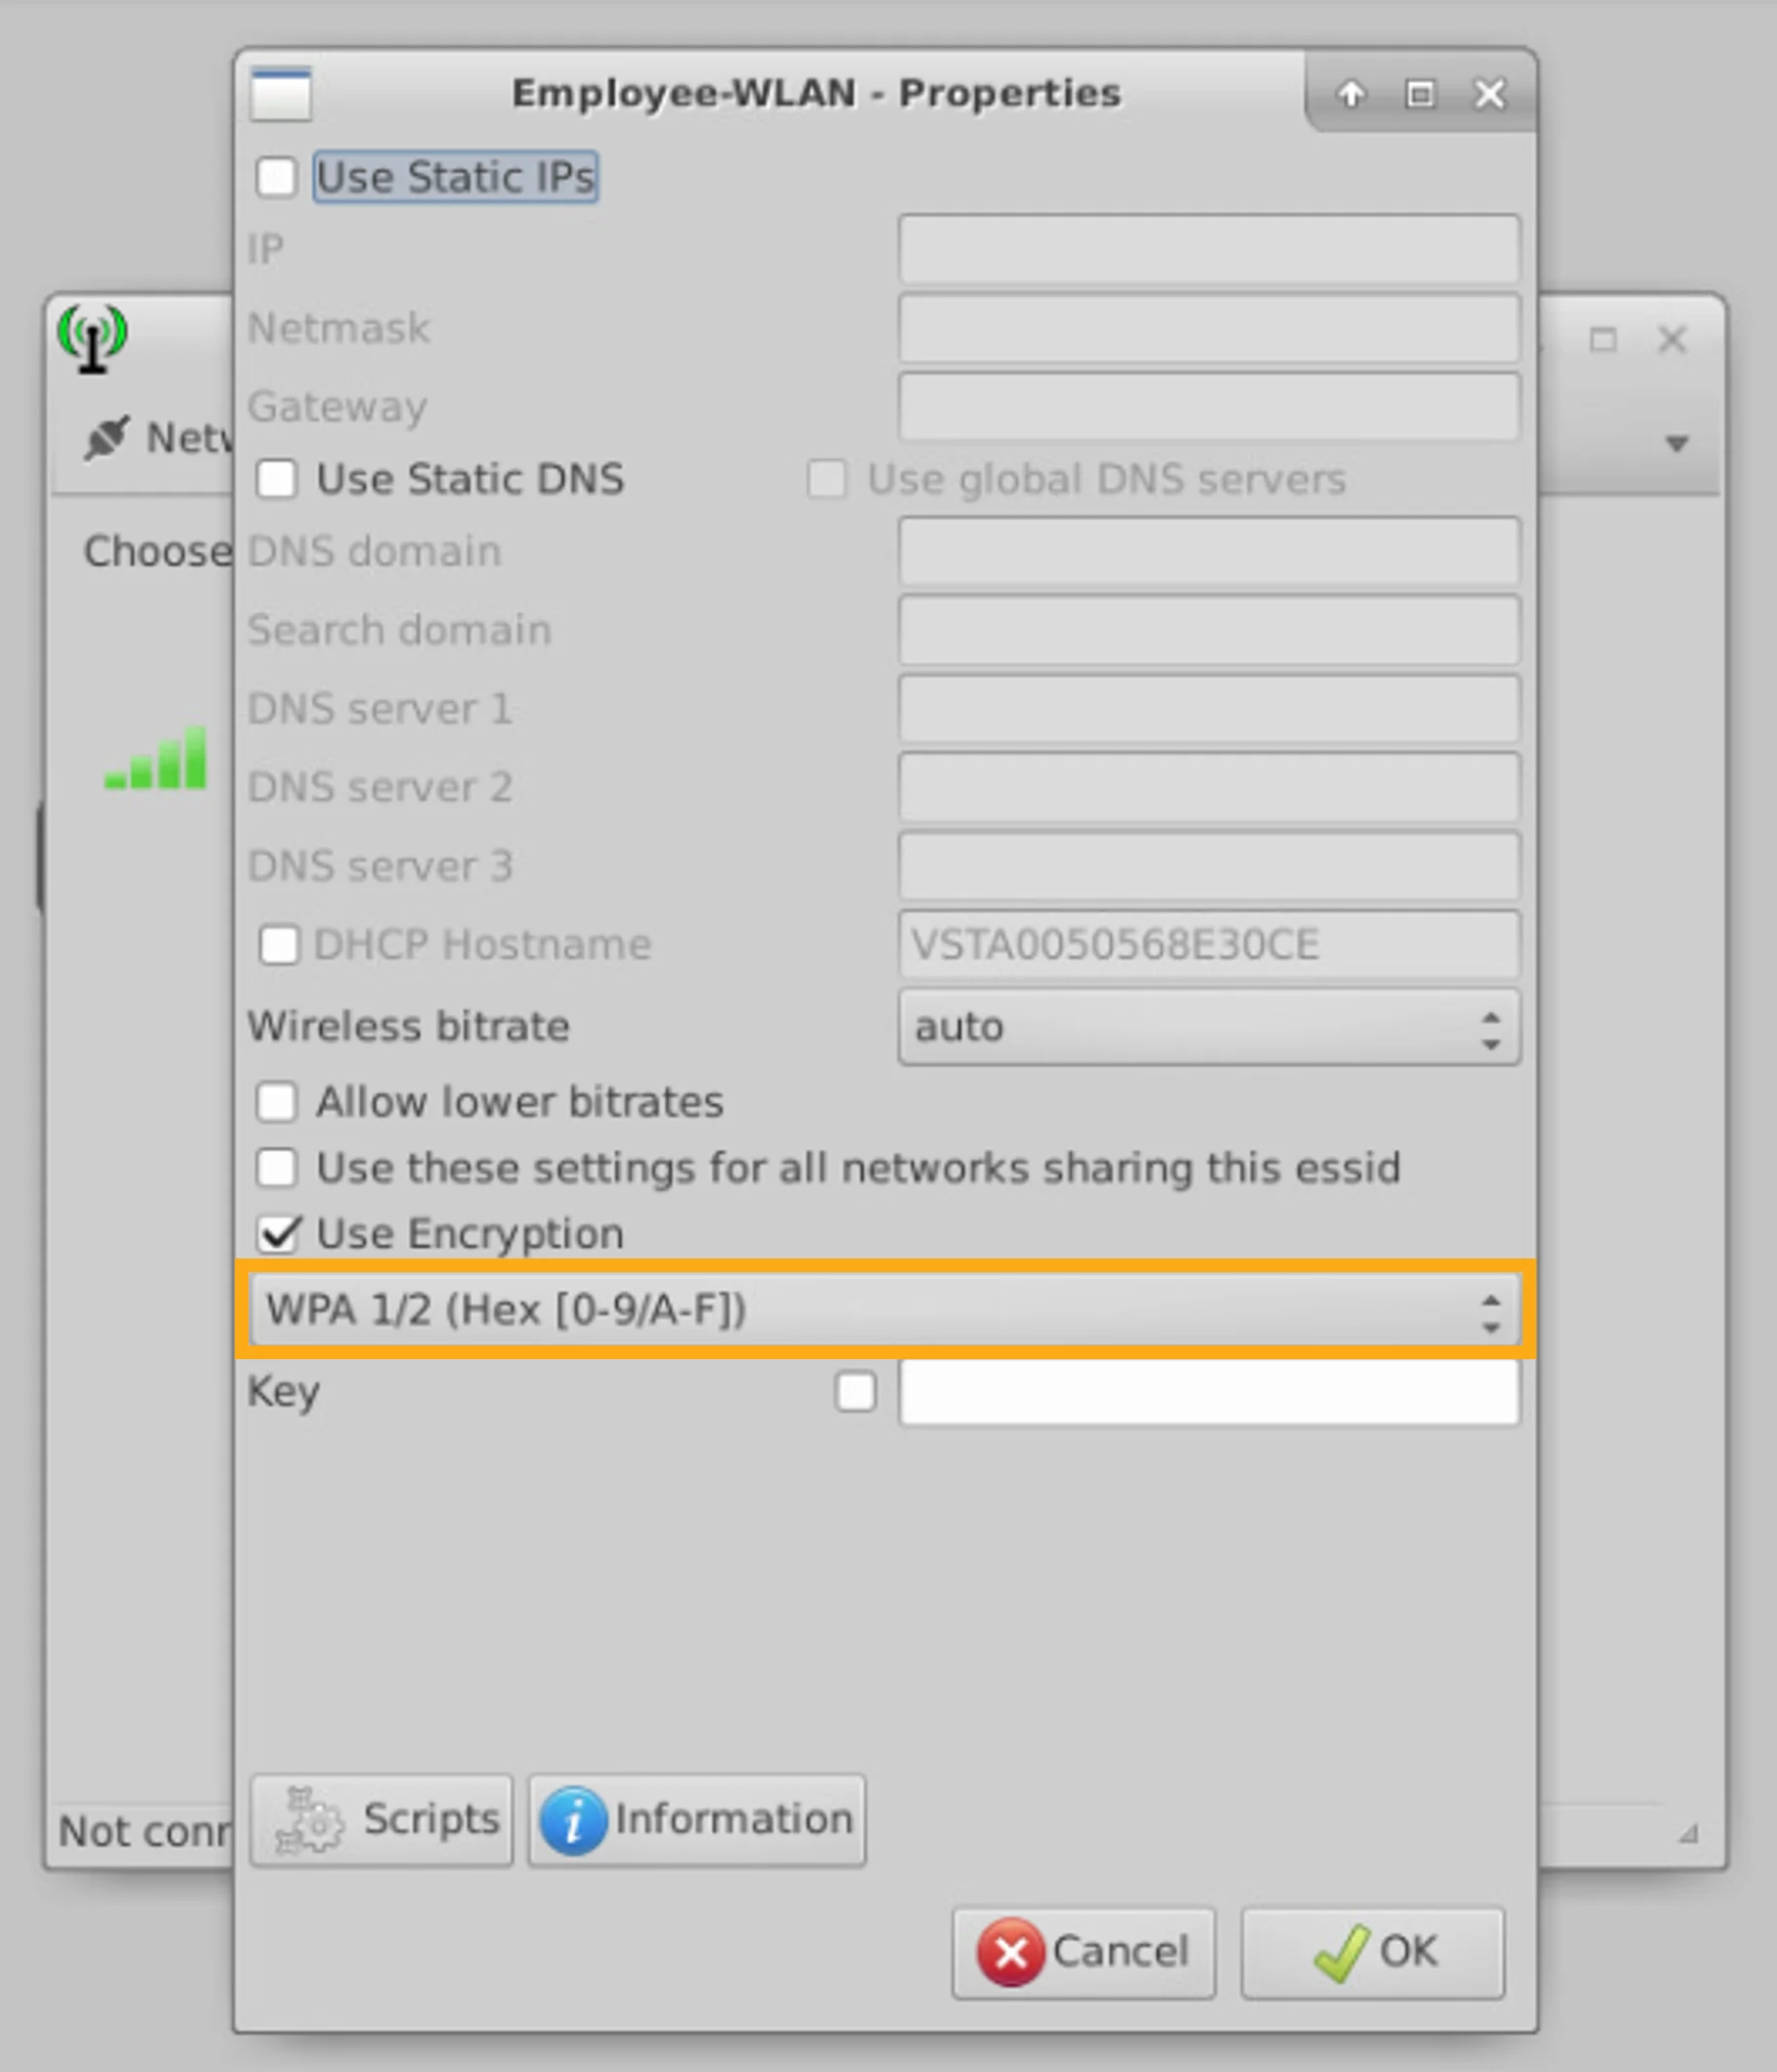
In the drop-down list, click the security type WPA 1/2 (Passphrase).
在下拉式清單中,按一下安全性類型 WPA 1/2 (Passphrase)。
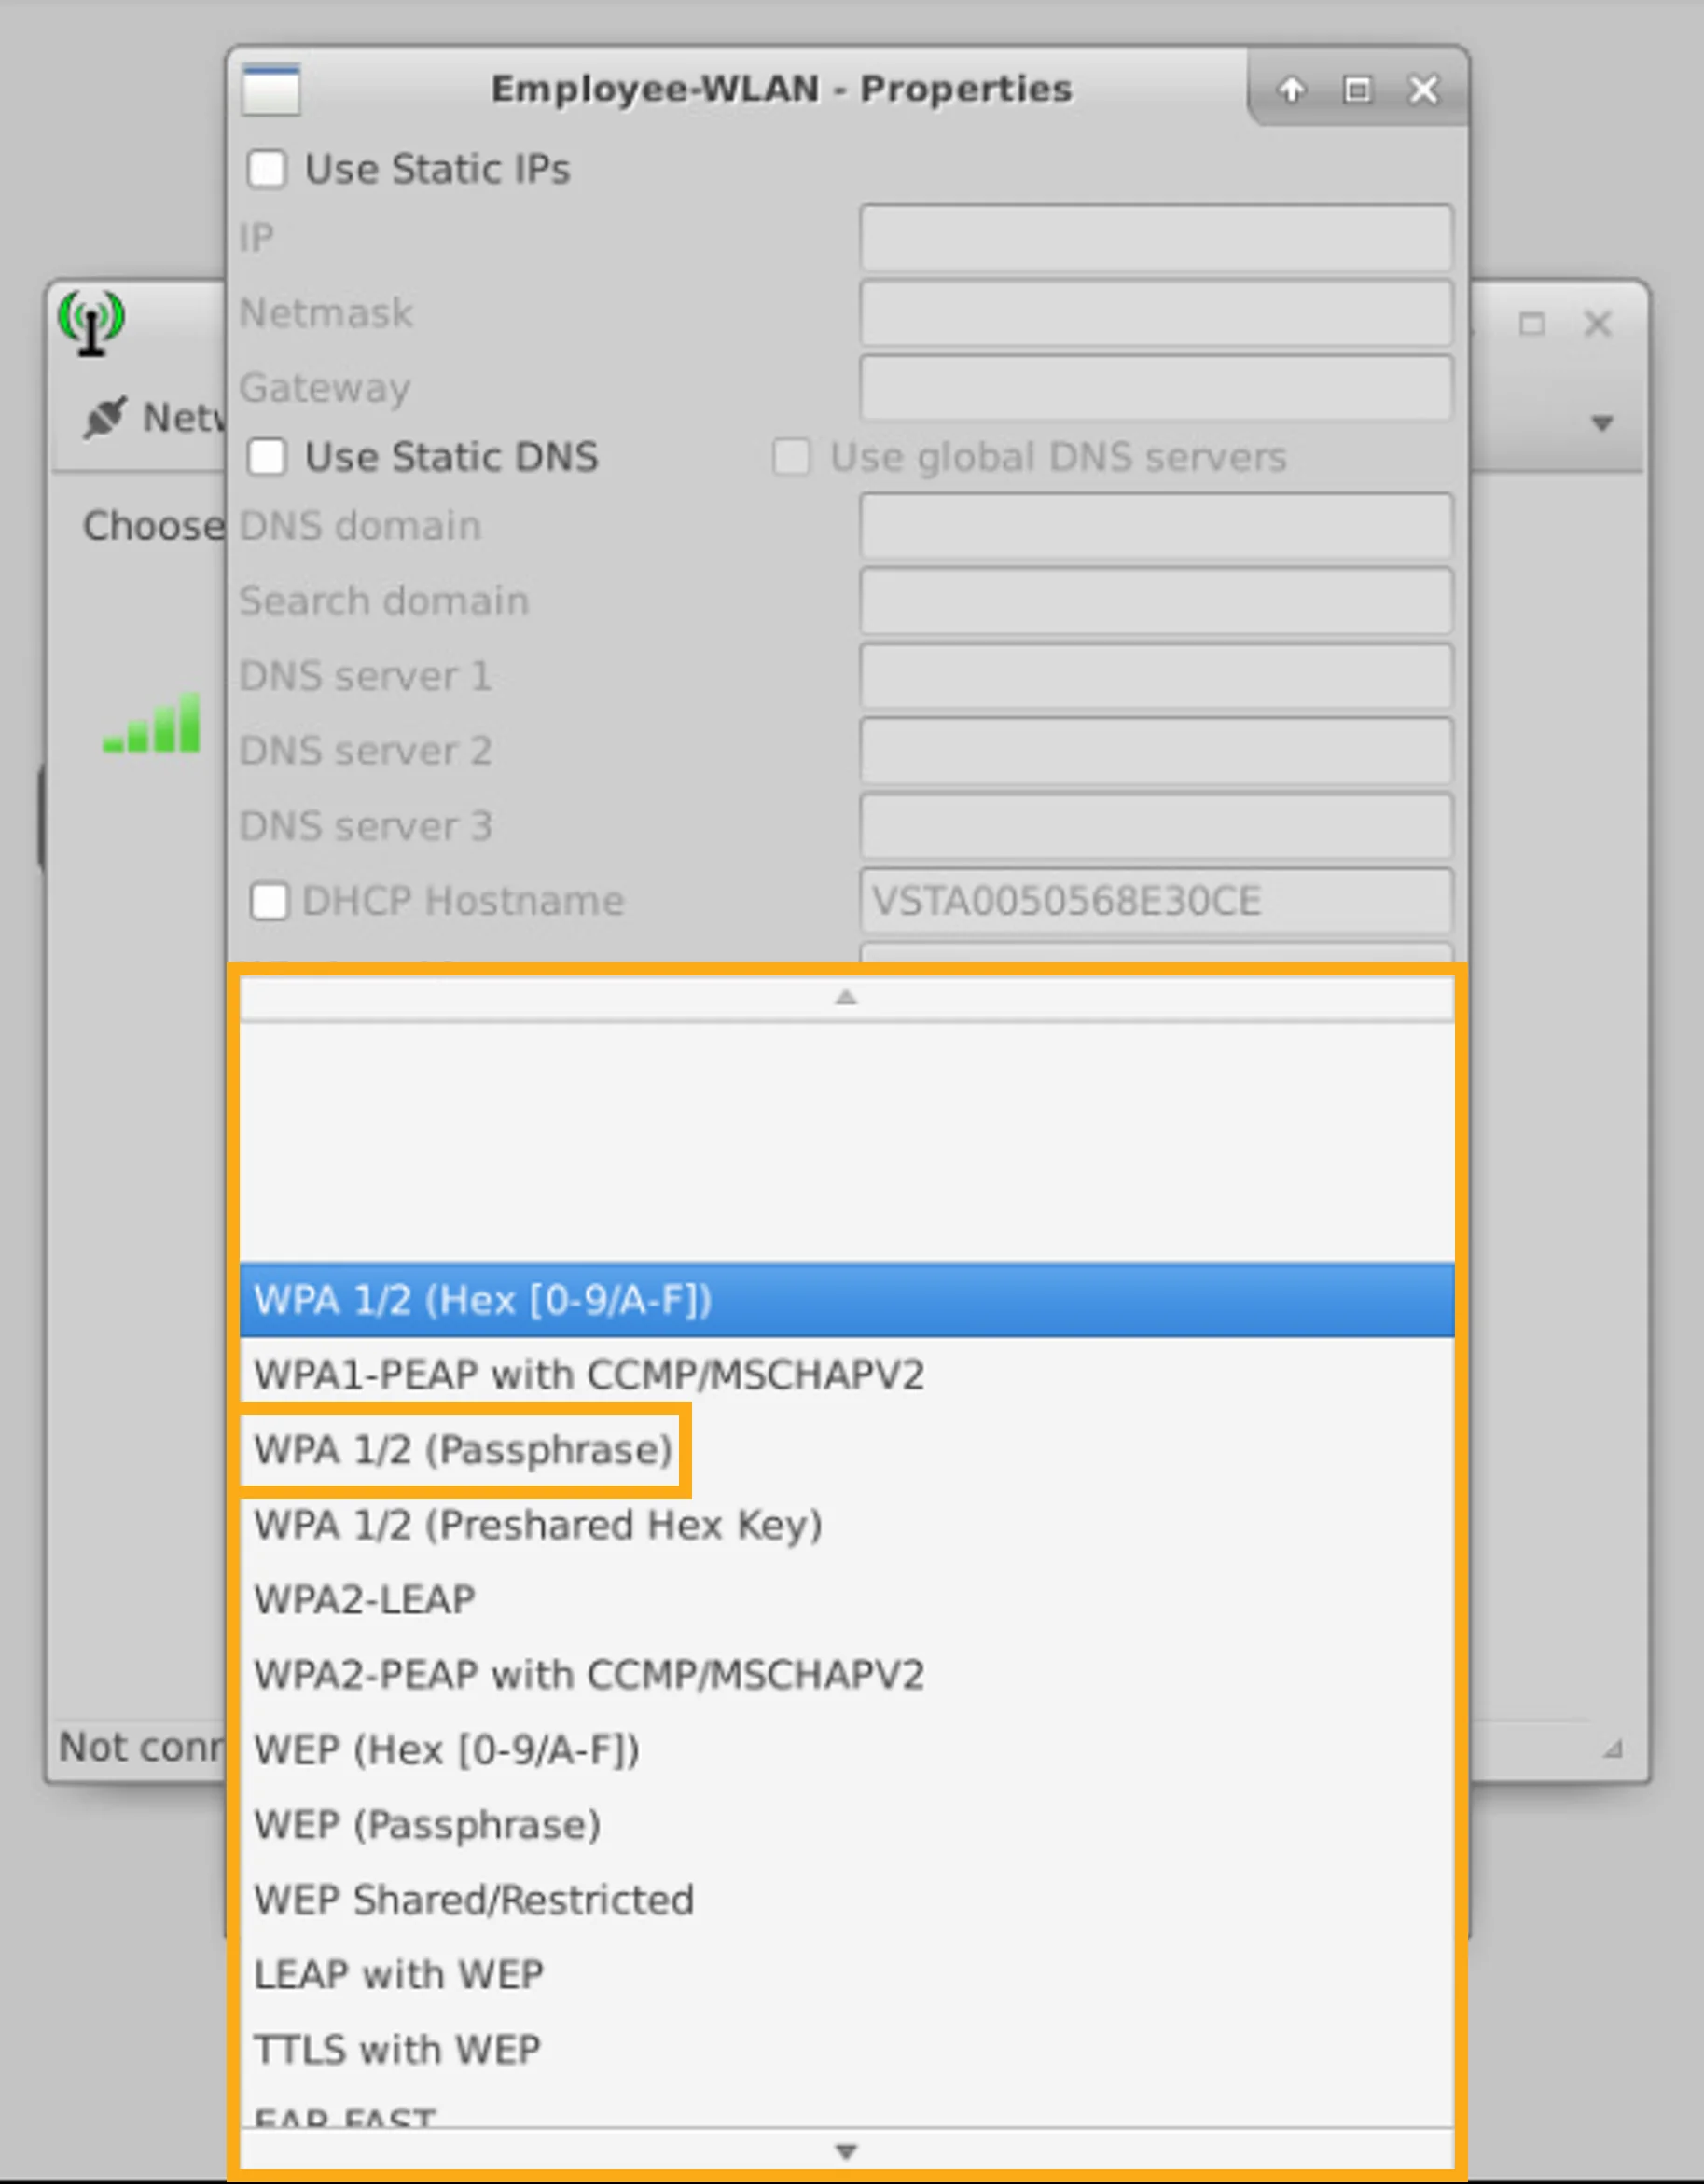
Click in the Preshared key input field and enter the key Cisco123.
按一下 Preshared key 輸入欄位,並輸入金鑰 Cisco123。
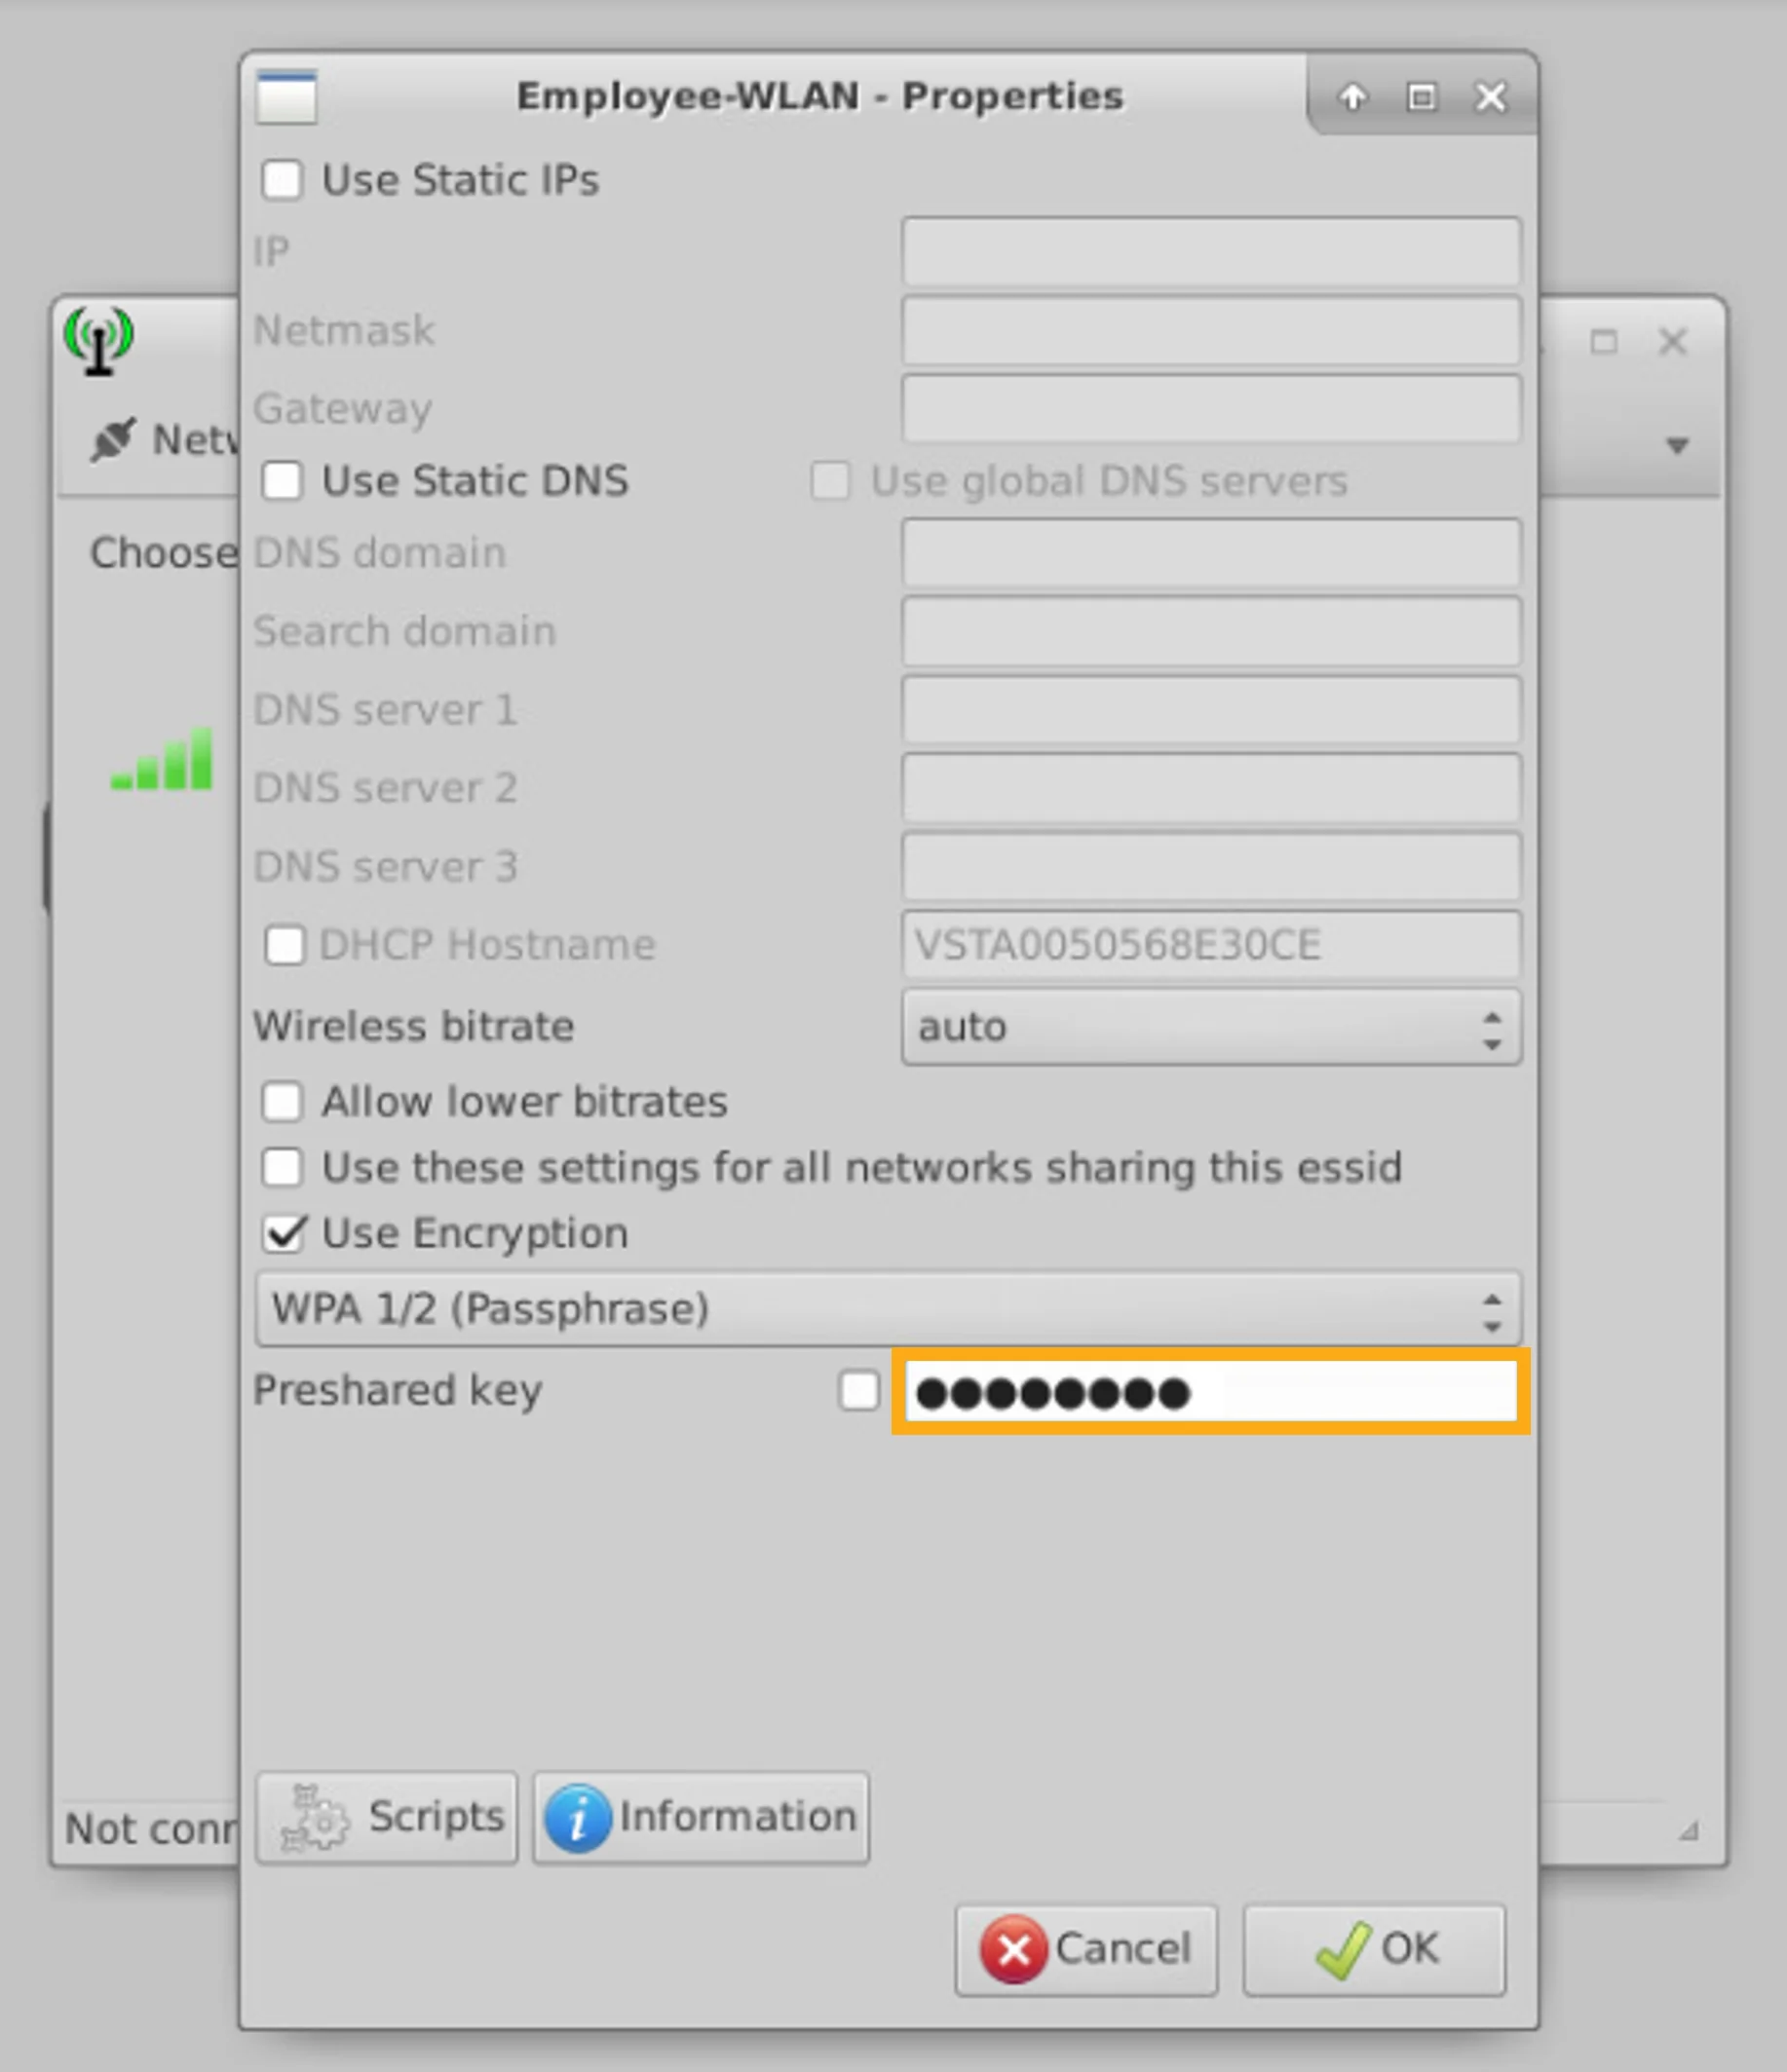
Check the check box that is to the left of the Preshared key input field
勾選 Preshared key 輸入欄位左側的核取方塊
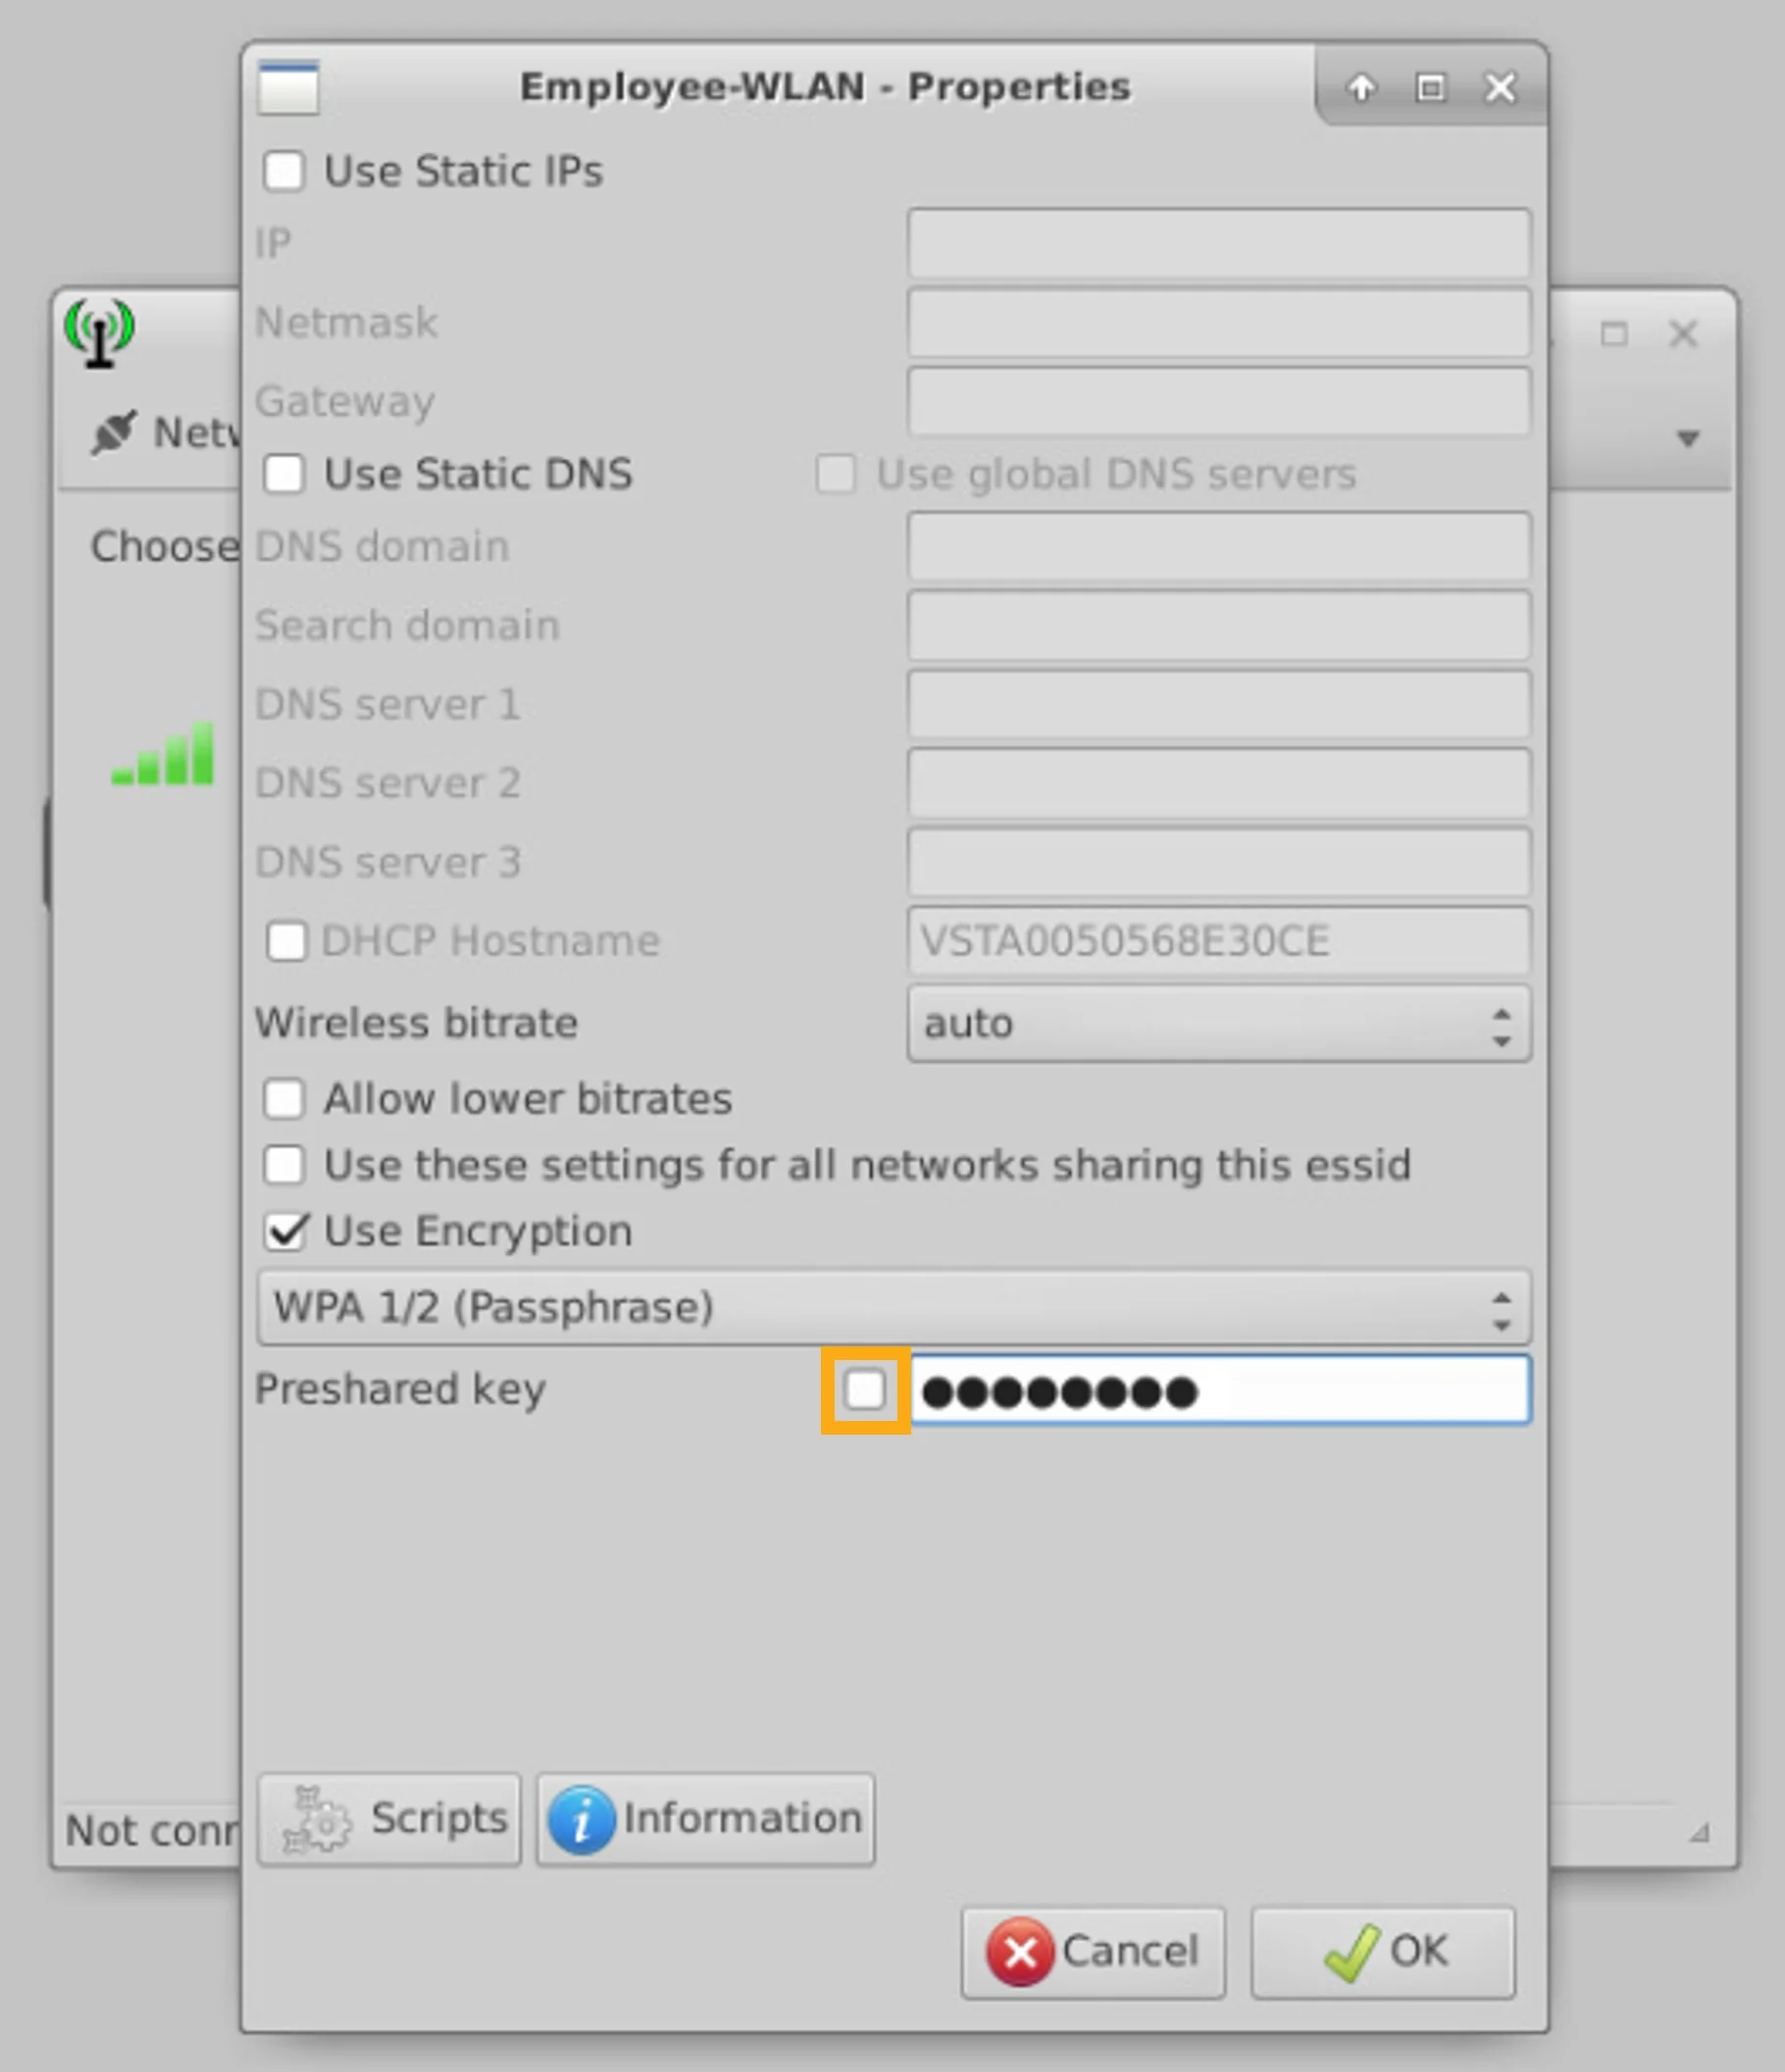
Note that the key is now displayed in cleartext. Verify the key. If needed, edit the key. When the key is correct, click OK.
請注意,金鑰現在以明文顯示。請驗證此金鑰,如有需要請進行編輯。確認金鑰正確後,按一下 OK。
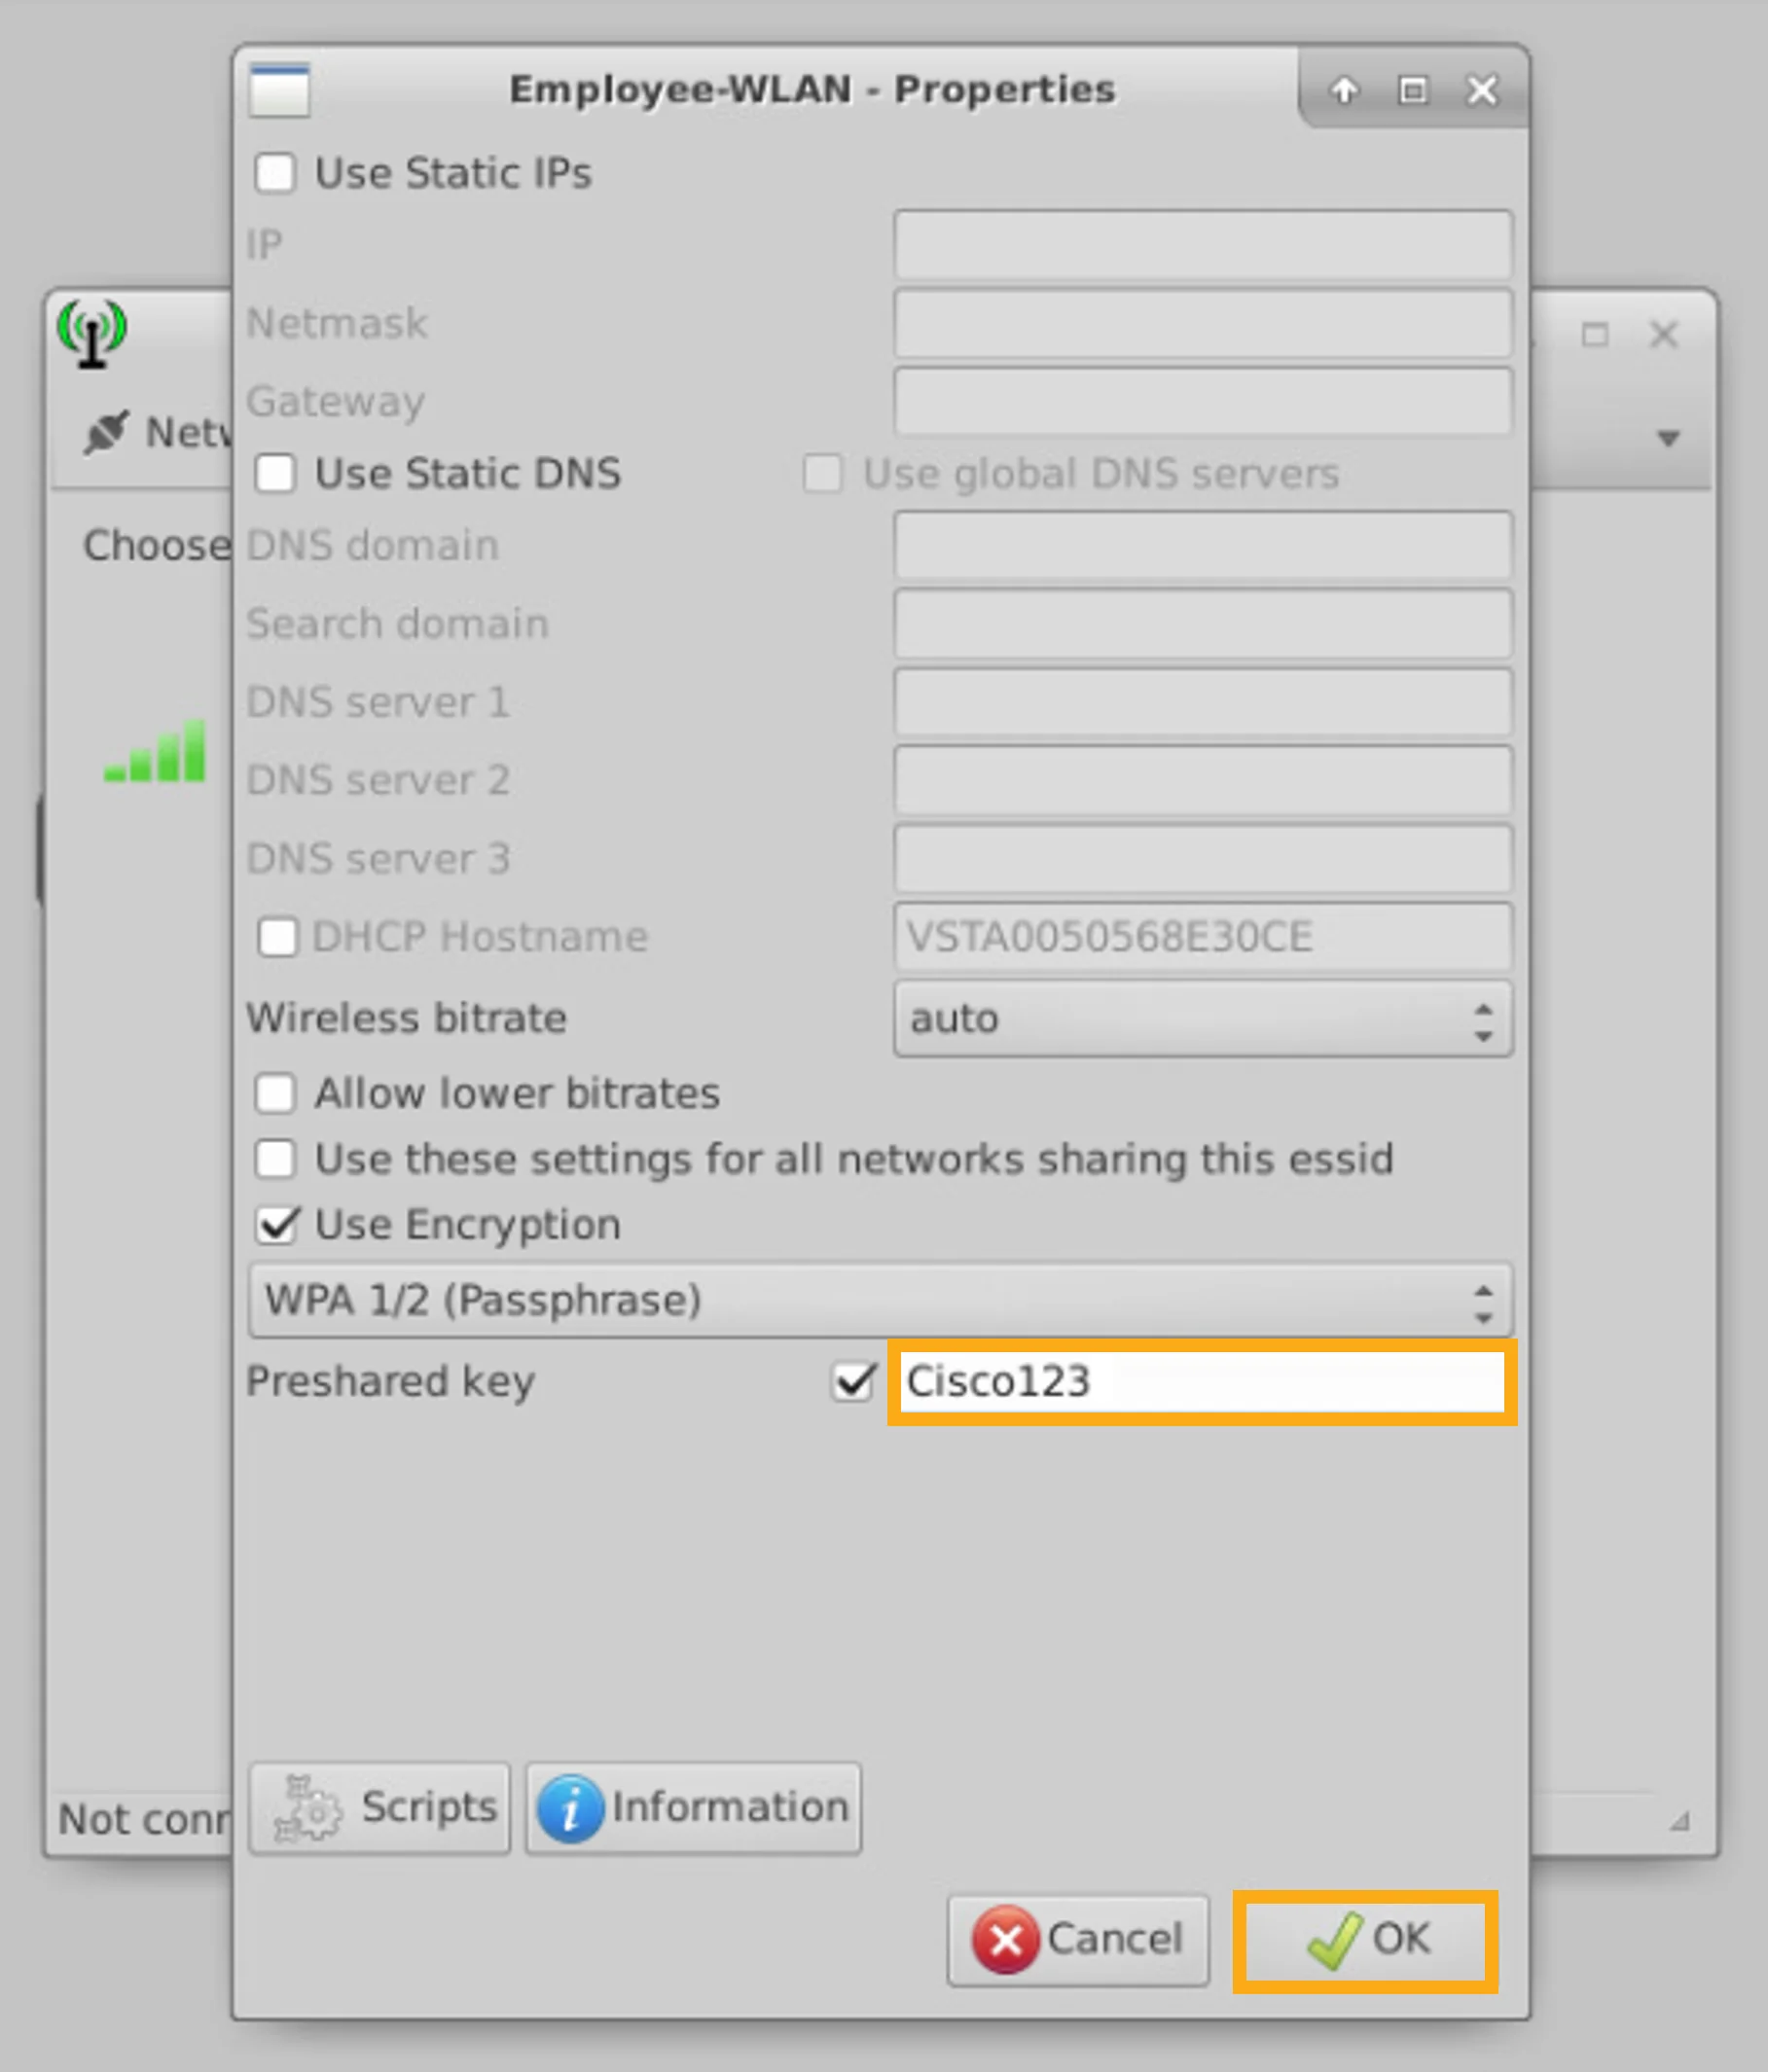
Connect to the WLAN
連線至 WLAN
Click Connect to connect to this WLAN.
按一下 Connect,連線至此 WLAN。
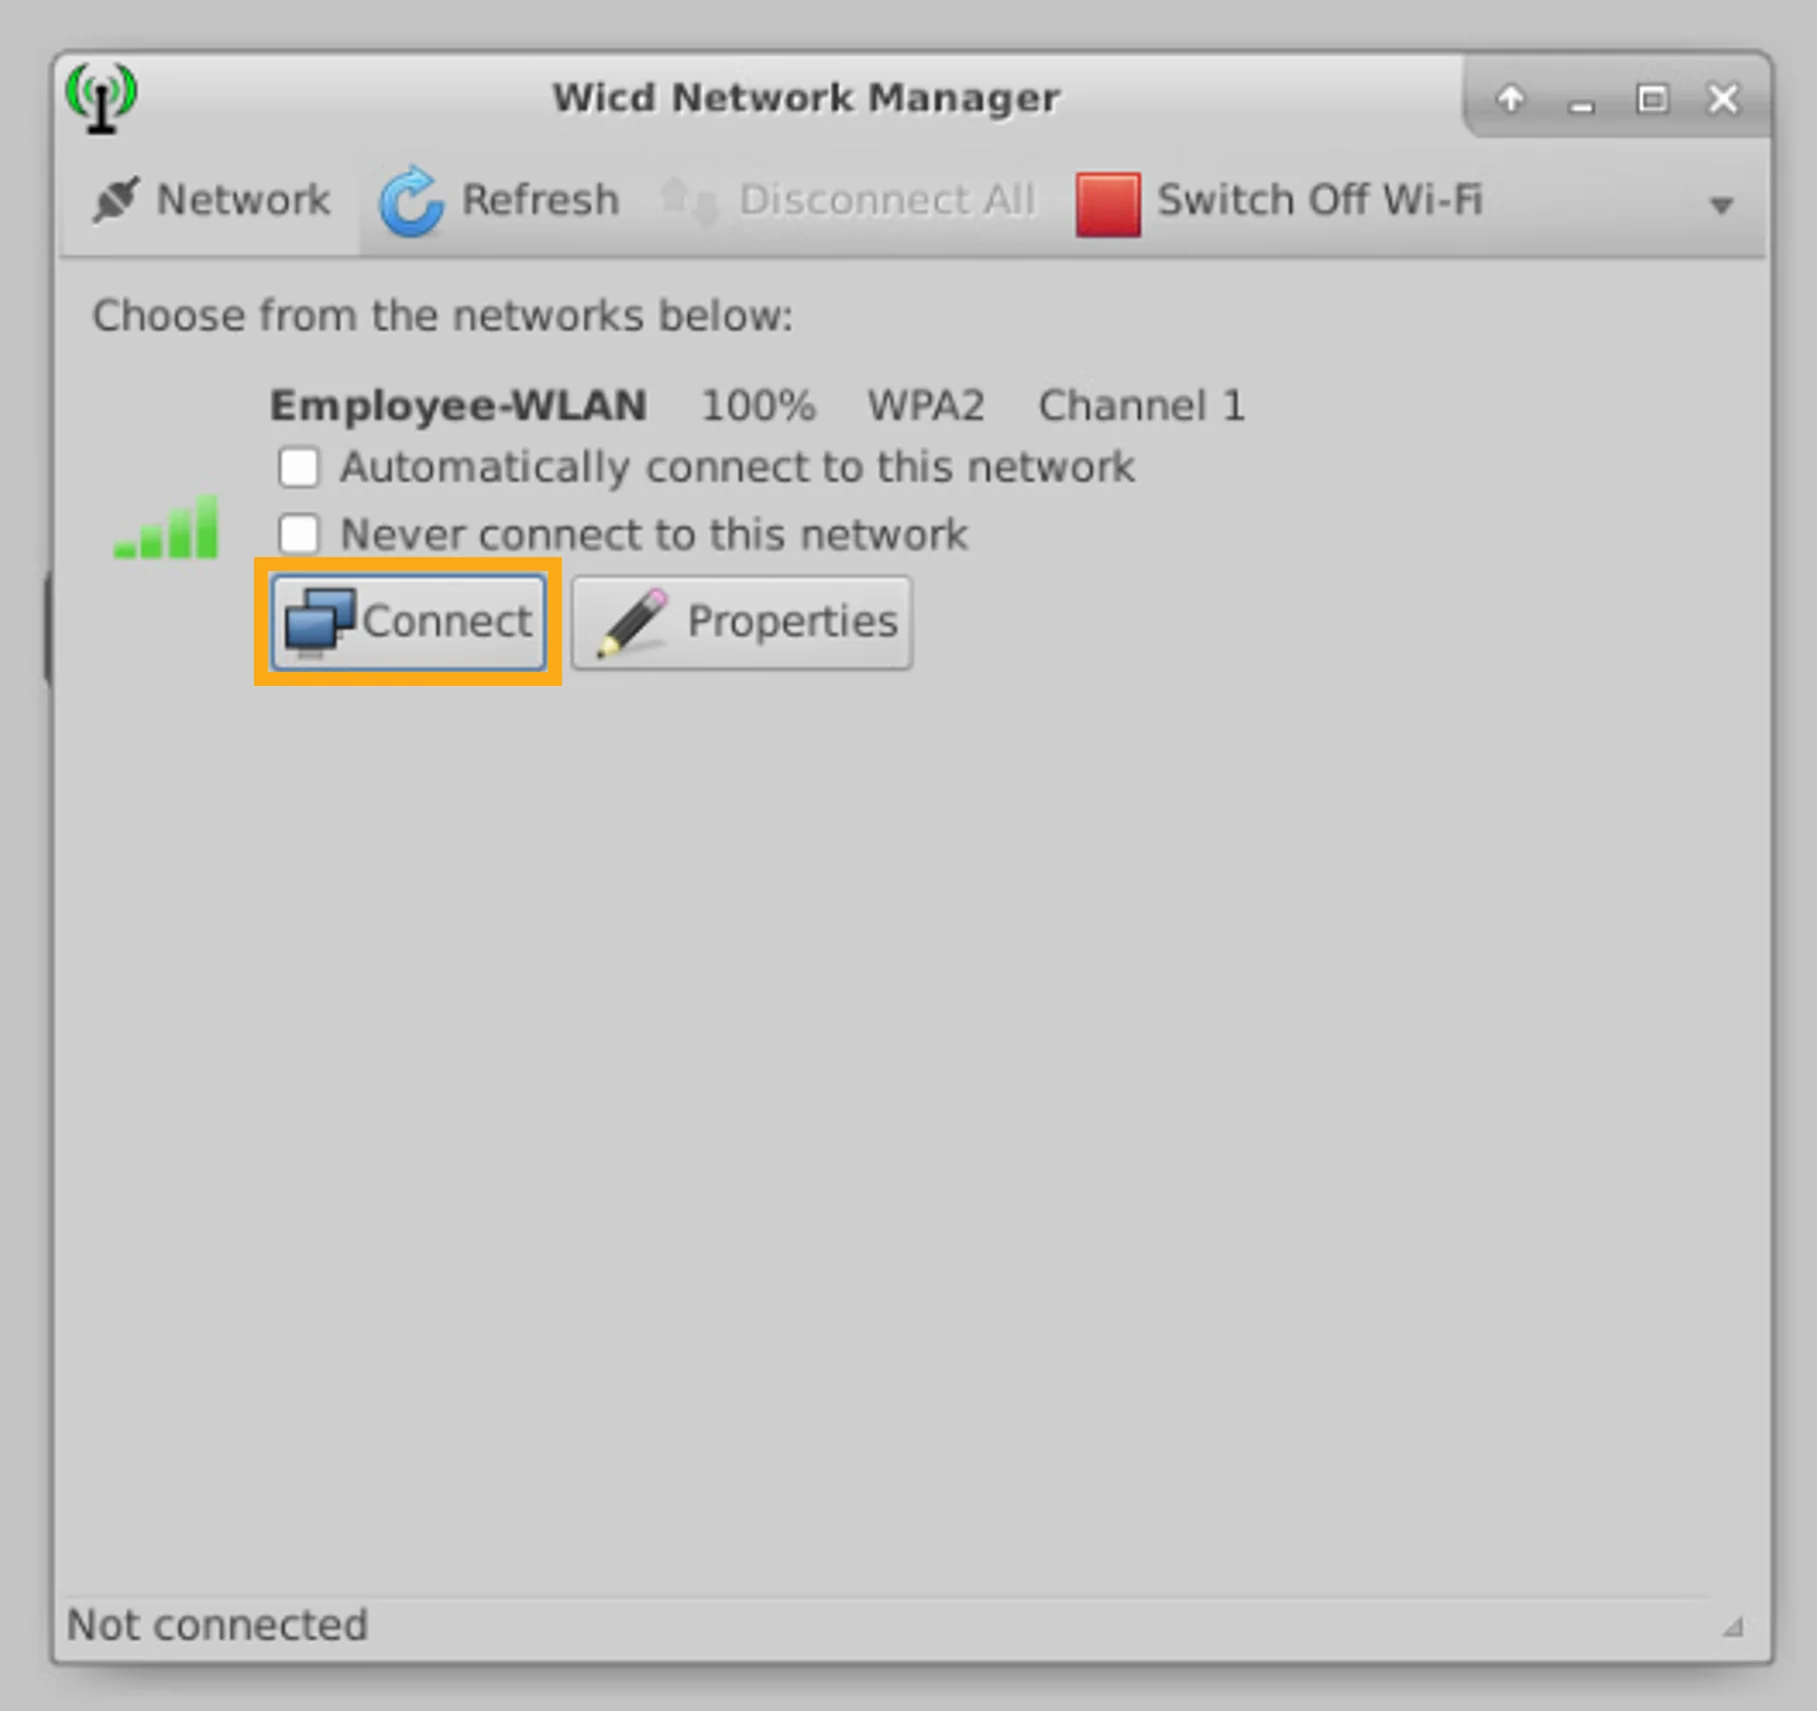
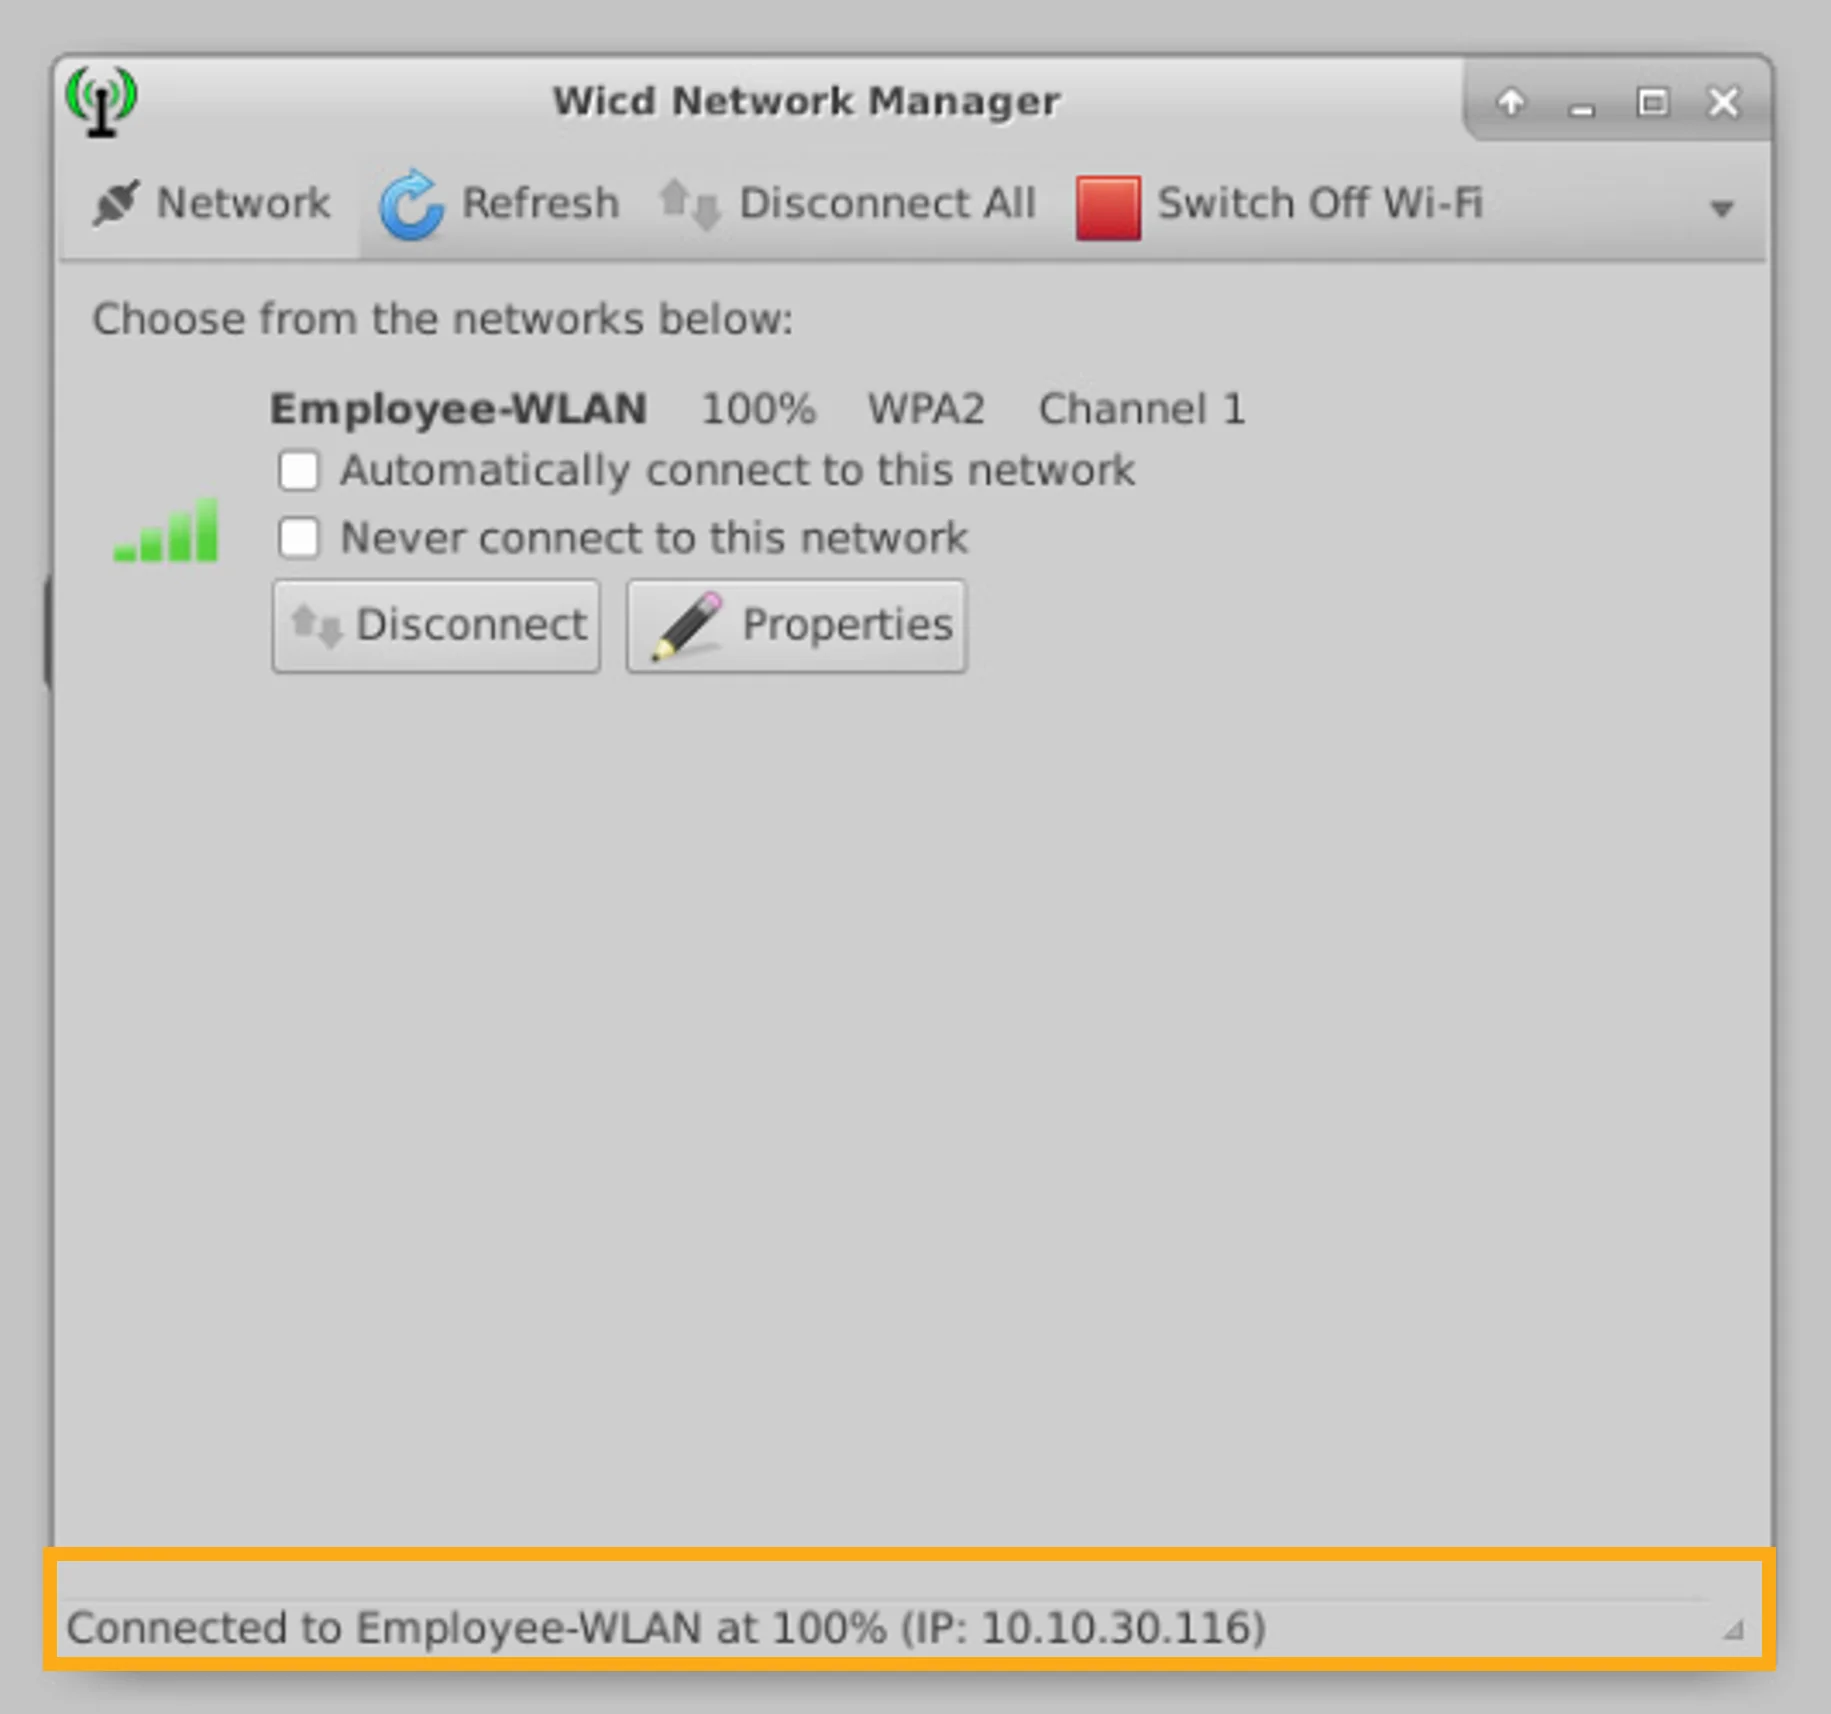
Verify that Client PC 1 is connected to the Employee-WLAN and that the client was assigned an IP address of network 10.10.30.0/24.
驗證 Client PC 1 是否已連線至 Employee-WLAN,且用戶端已取得 10.10.30.0/24 網路的 IP 位址。
Connect Client PC 2 to the WLAN
將 Client PC 2 連線至 WLAN
Now you will connect Client PC 2 to WLAN.
現在您將把 Client PC 2 連線至 WLAN。
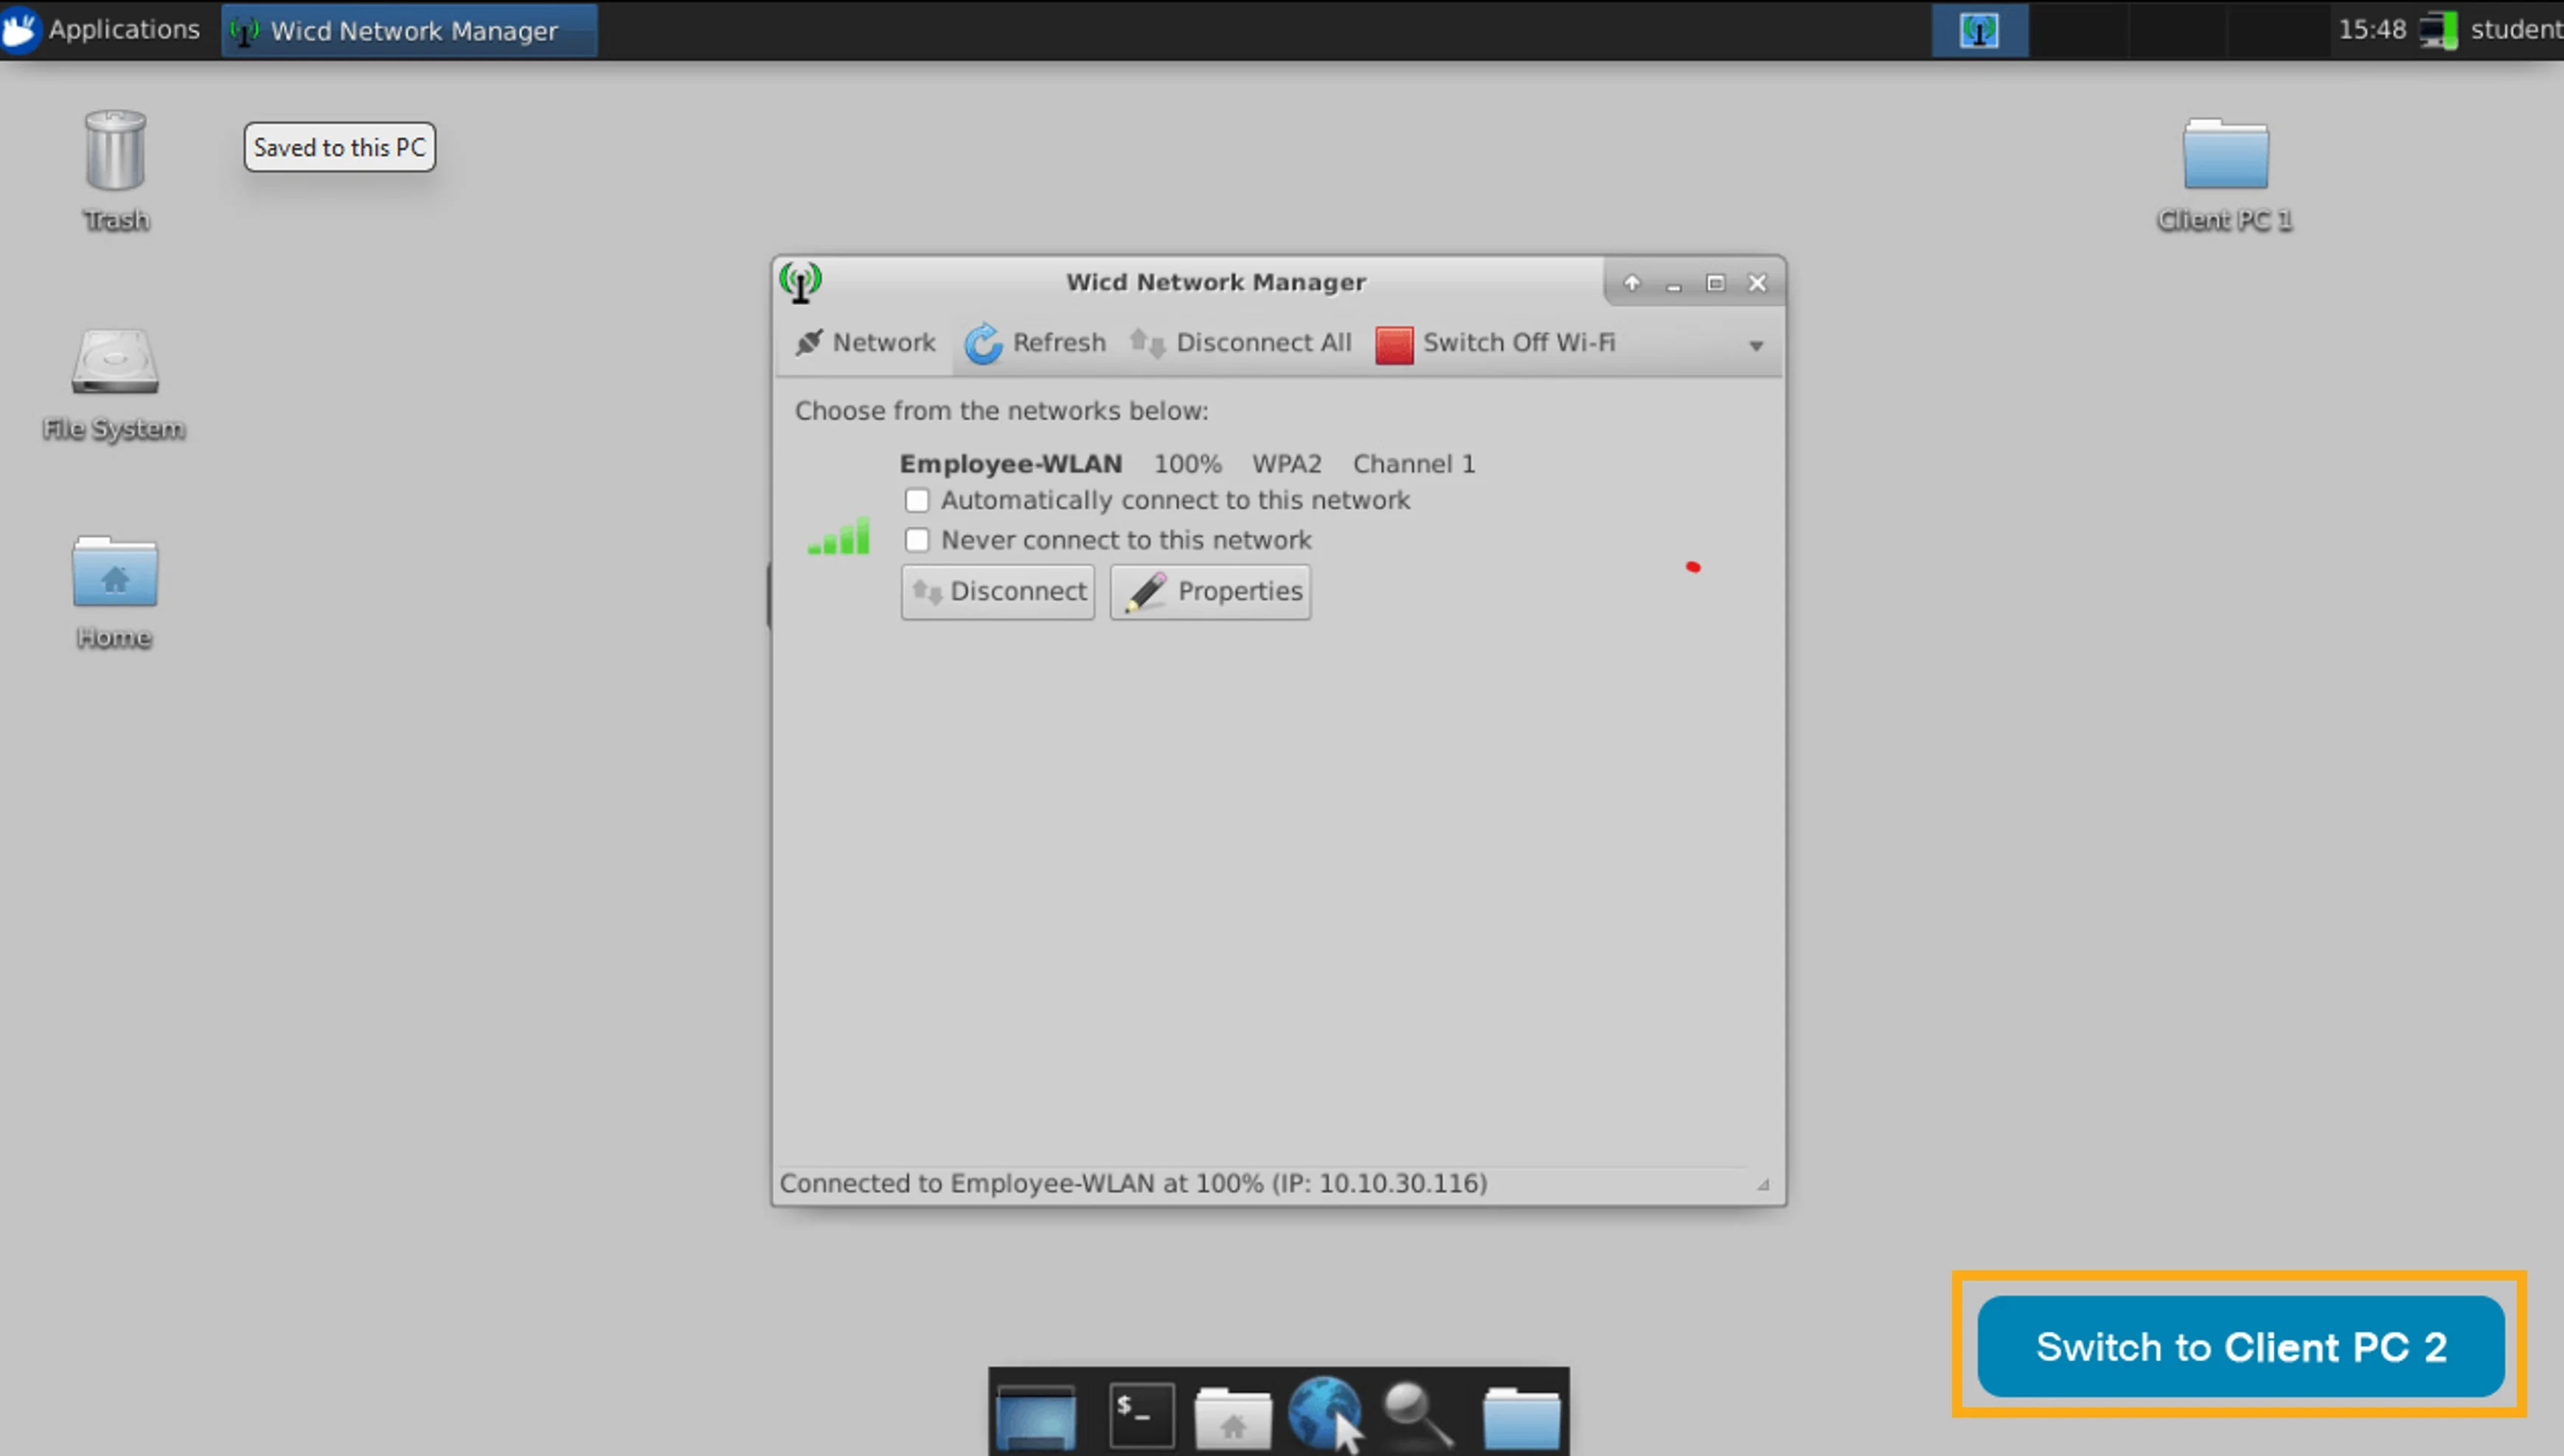
Click the Switch to Client PC 2 button, which is located at the bottom-right corner of the desktop to switch from Client PC 1 to Client PC 2.
按一下位於桌面右下角的 Switch to Client PC 2 按鈕,從 Client PC 1 切換至 Client PC 2。
On Client PC 2, configure the WLAN settings to connect to the WLAN called Employee-WLAN by repeating the same procedure that you performed on Client PC 1.
在 Client PC 2 上,重複您在 Client PC 1 上執行的相同程序,設定 WLAN 設定以連線至名為 Employee-WLAN 的 WLAN。
Click the Network icon that is in the top-right corner of the desktop.
按一下位於桌面右上角的 Network 圖示。
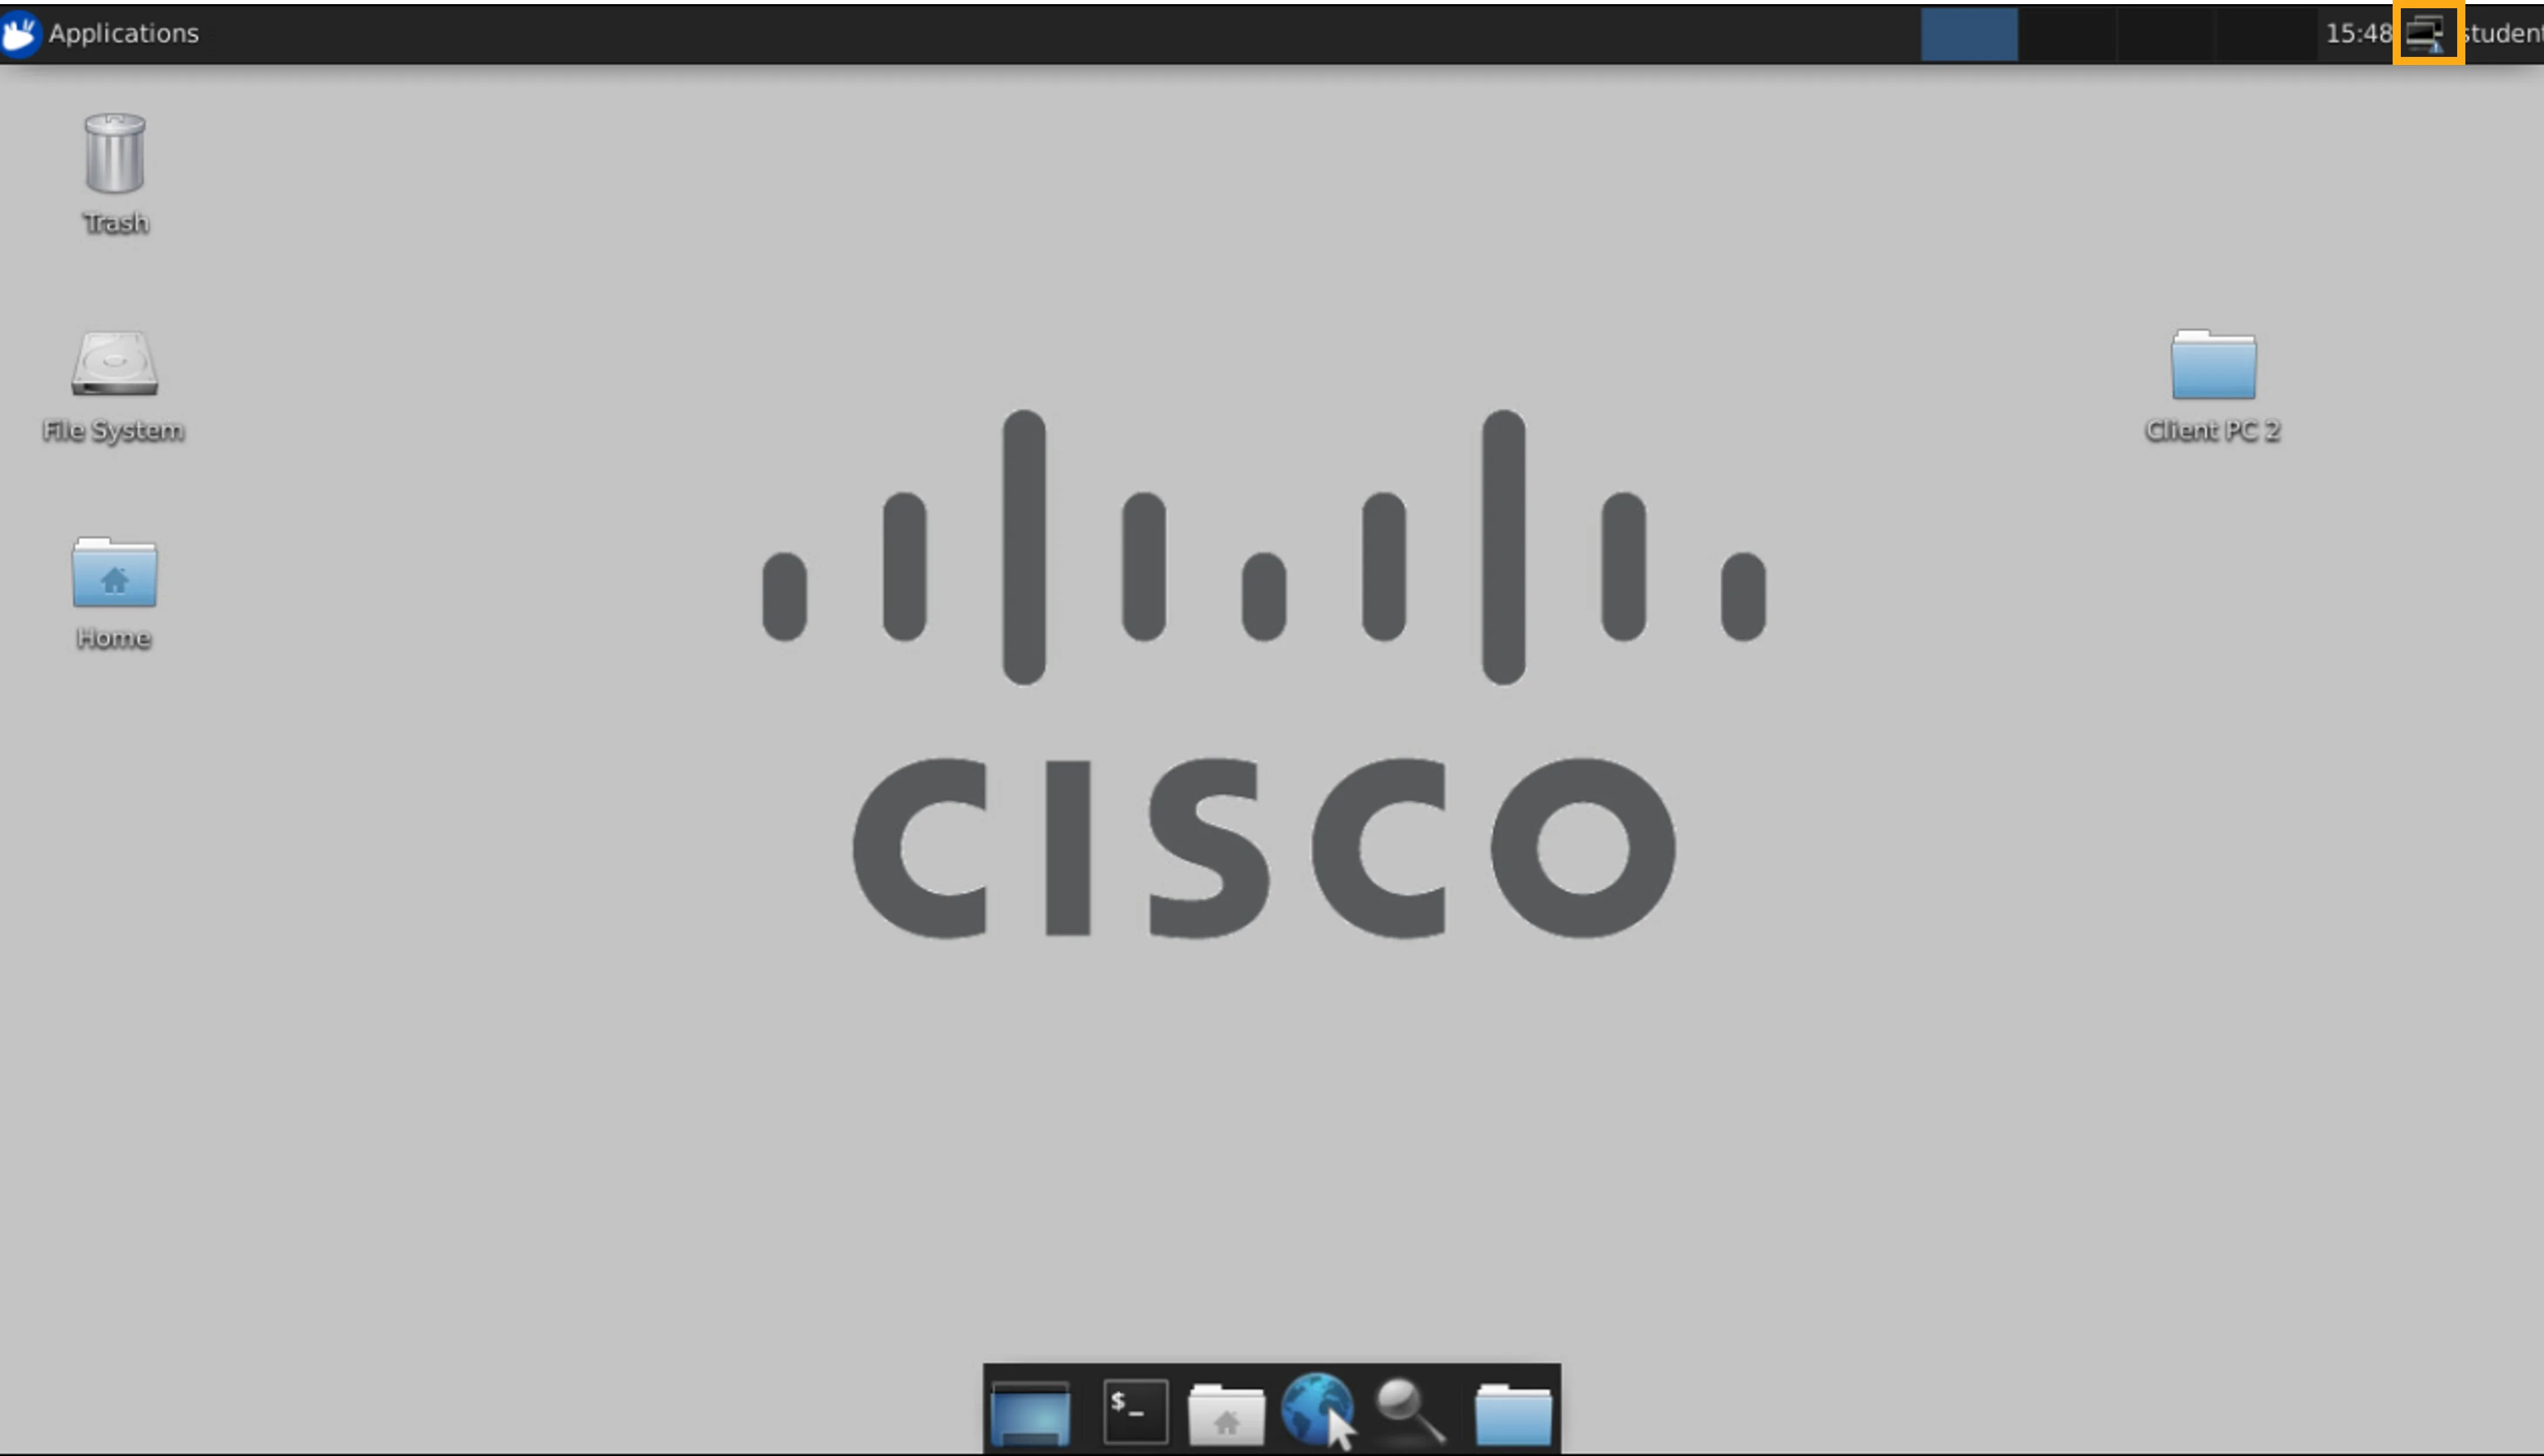
In the Wicd Network Manager window, click Refresh to scan for available networks.
在 Wicd Network Manager 視窗中,按一下 Refresh 掃描可用的網路。
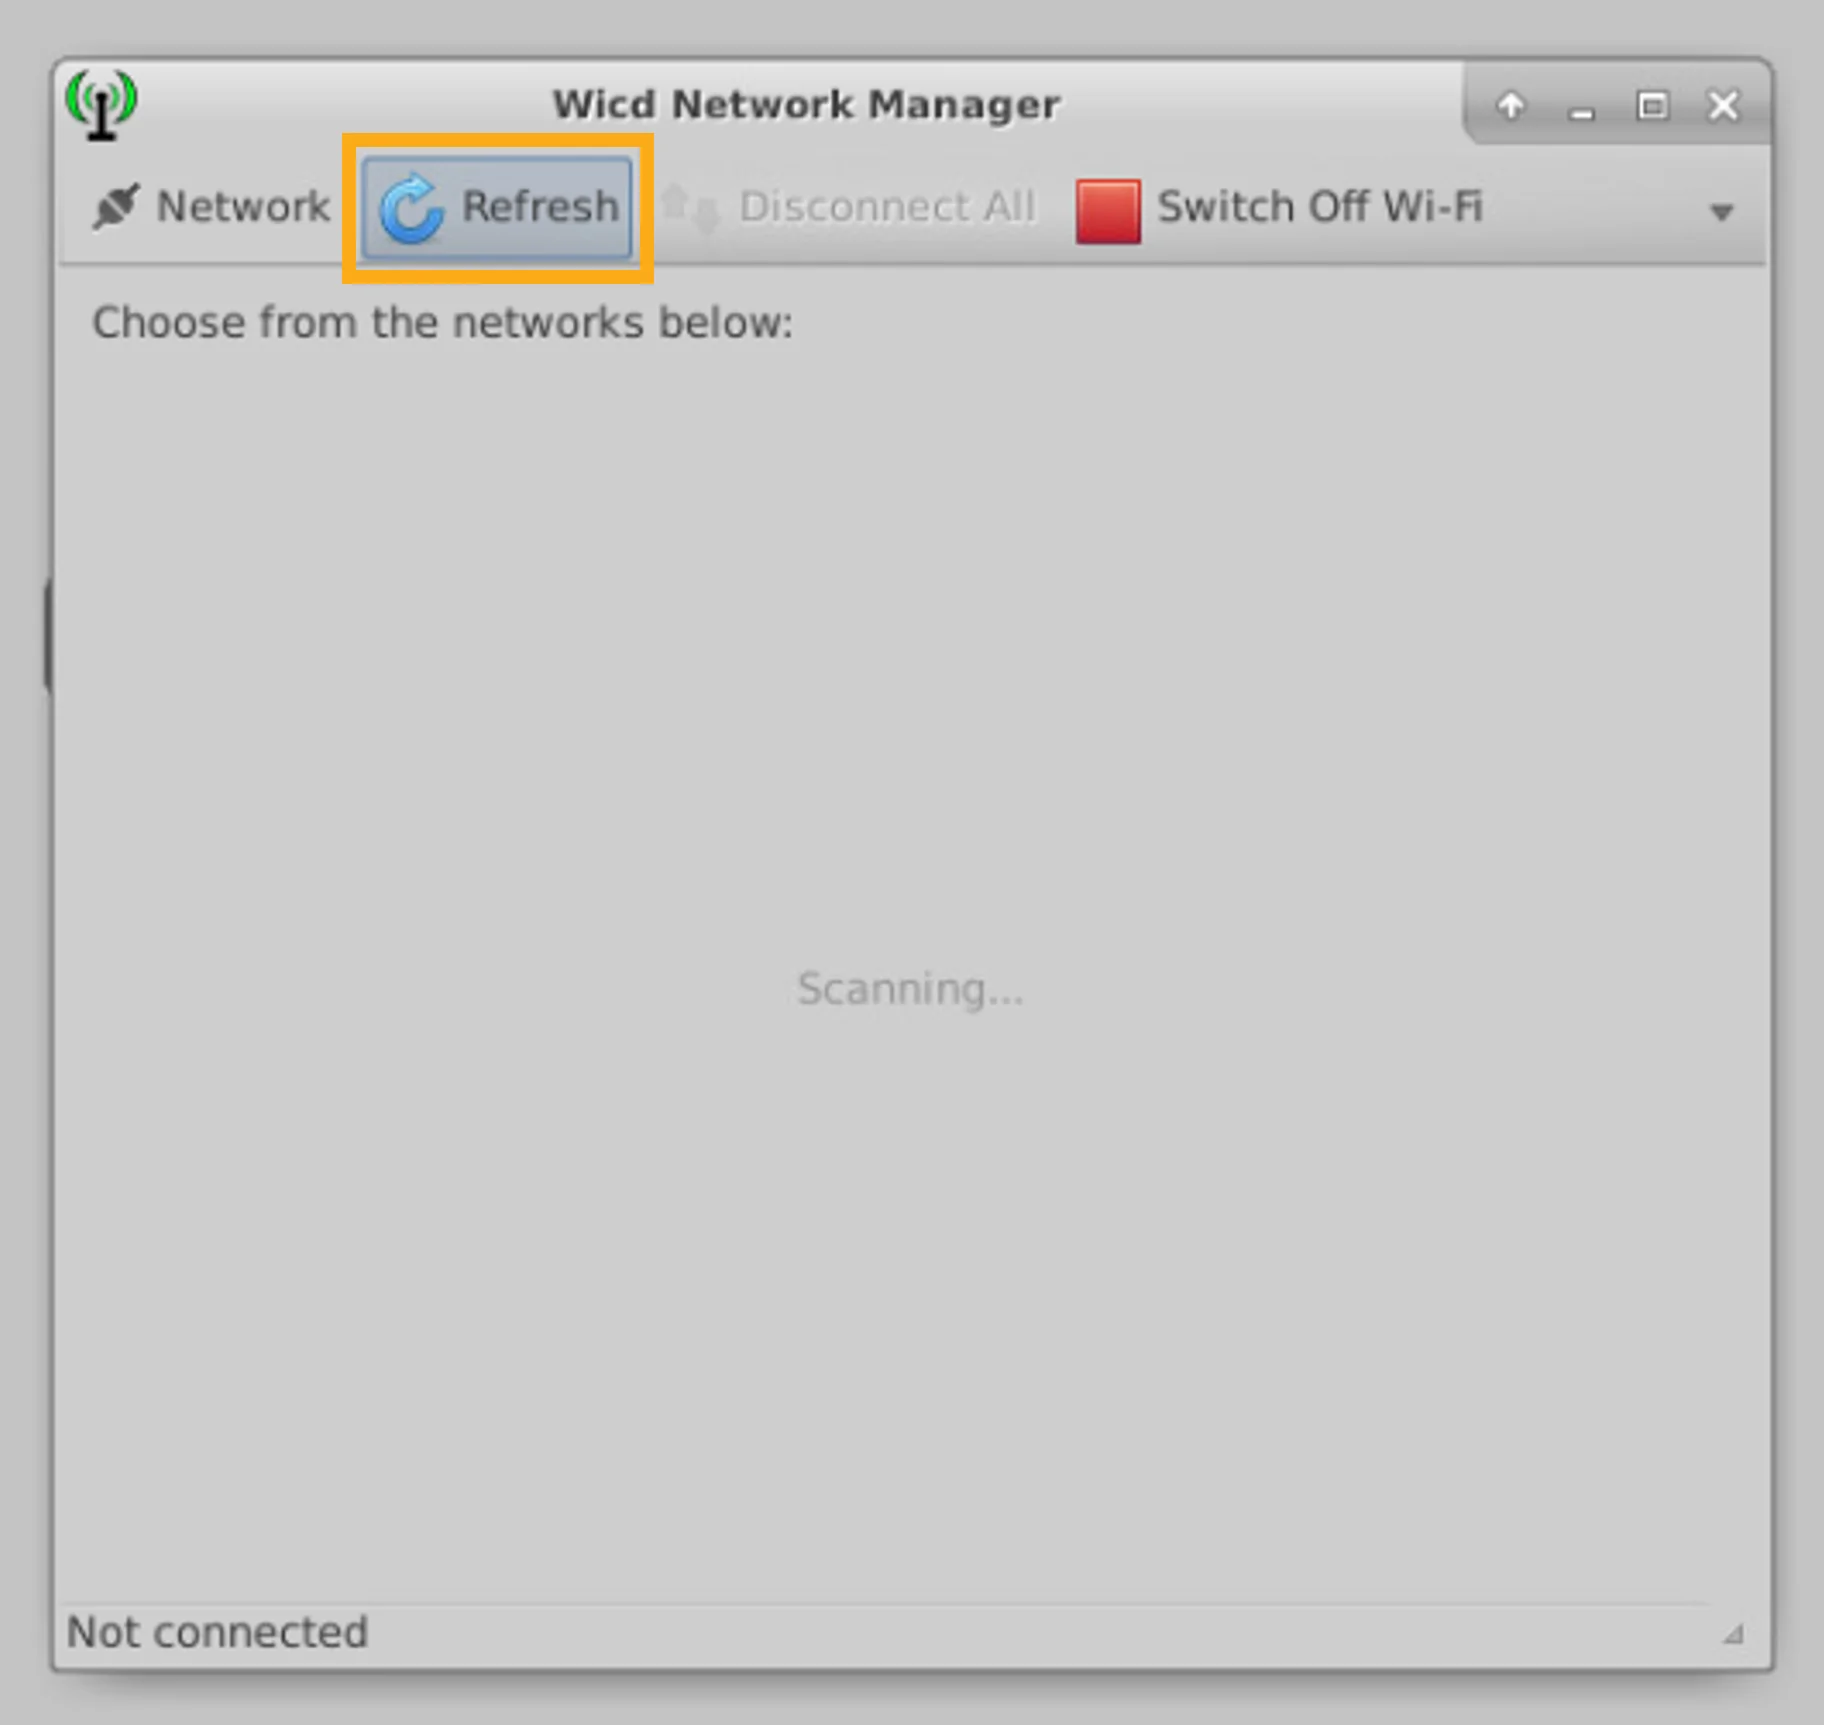
The Employee-WLAN network is shown. Note that the wireless client indicates that the network is secured by WPA2.
畫面顯示 Employee-WLAN 網路。請注意,無線用戶端顯示該網路已由 WPA2 保護。
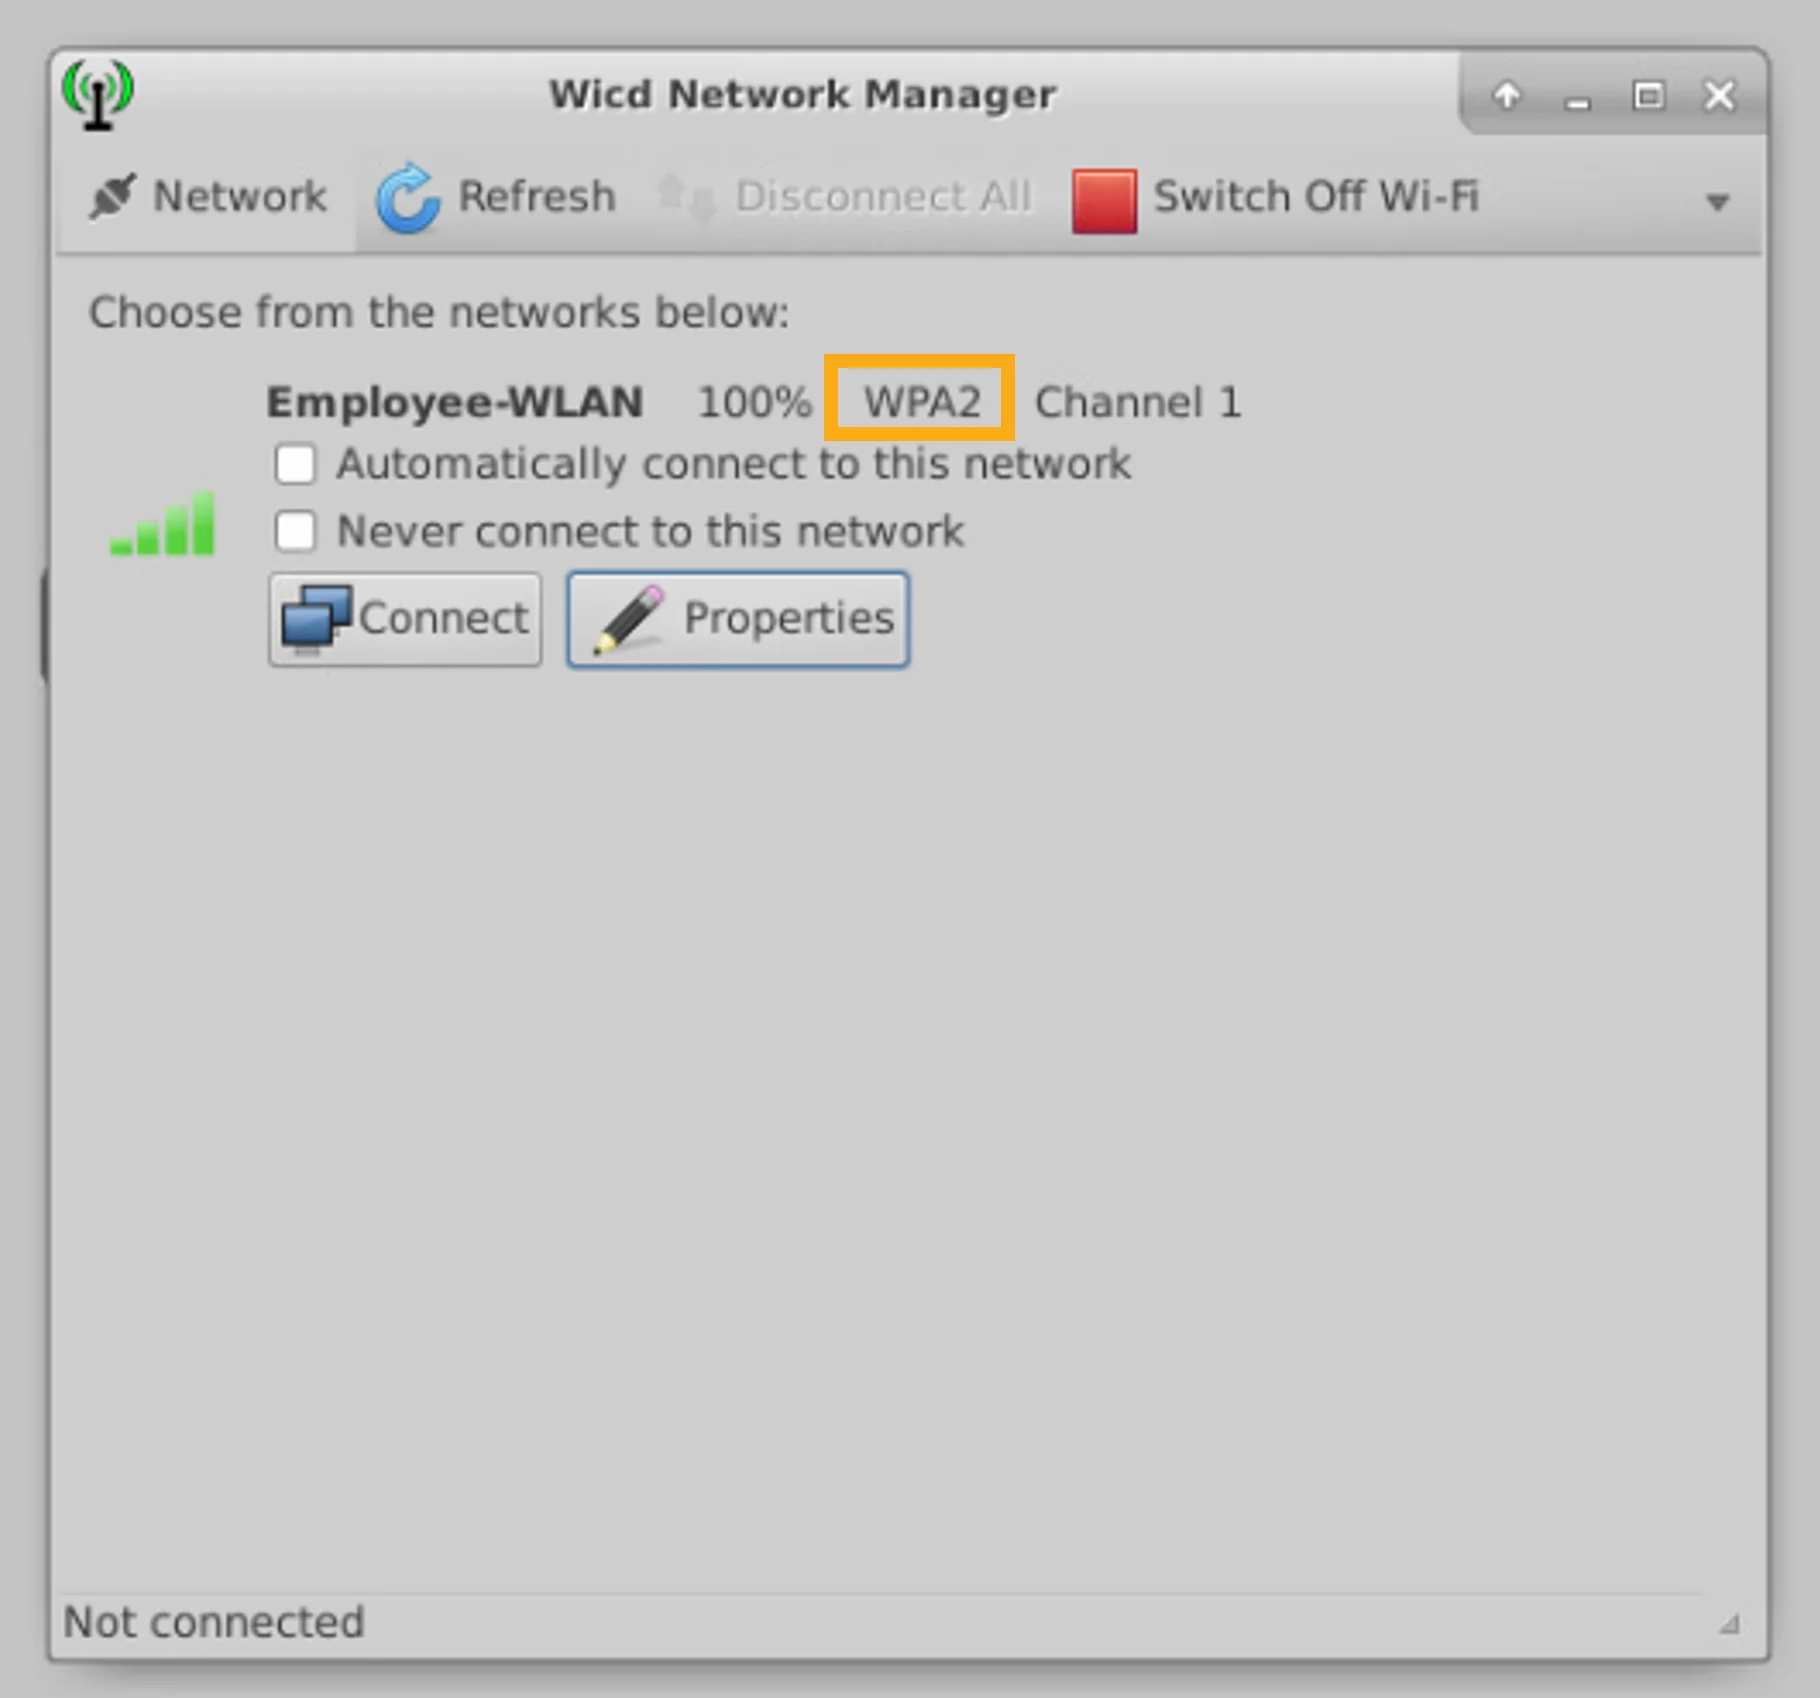
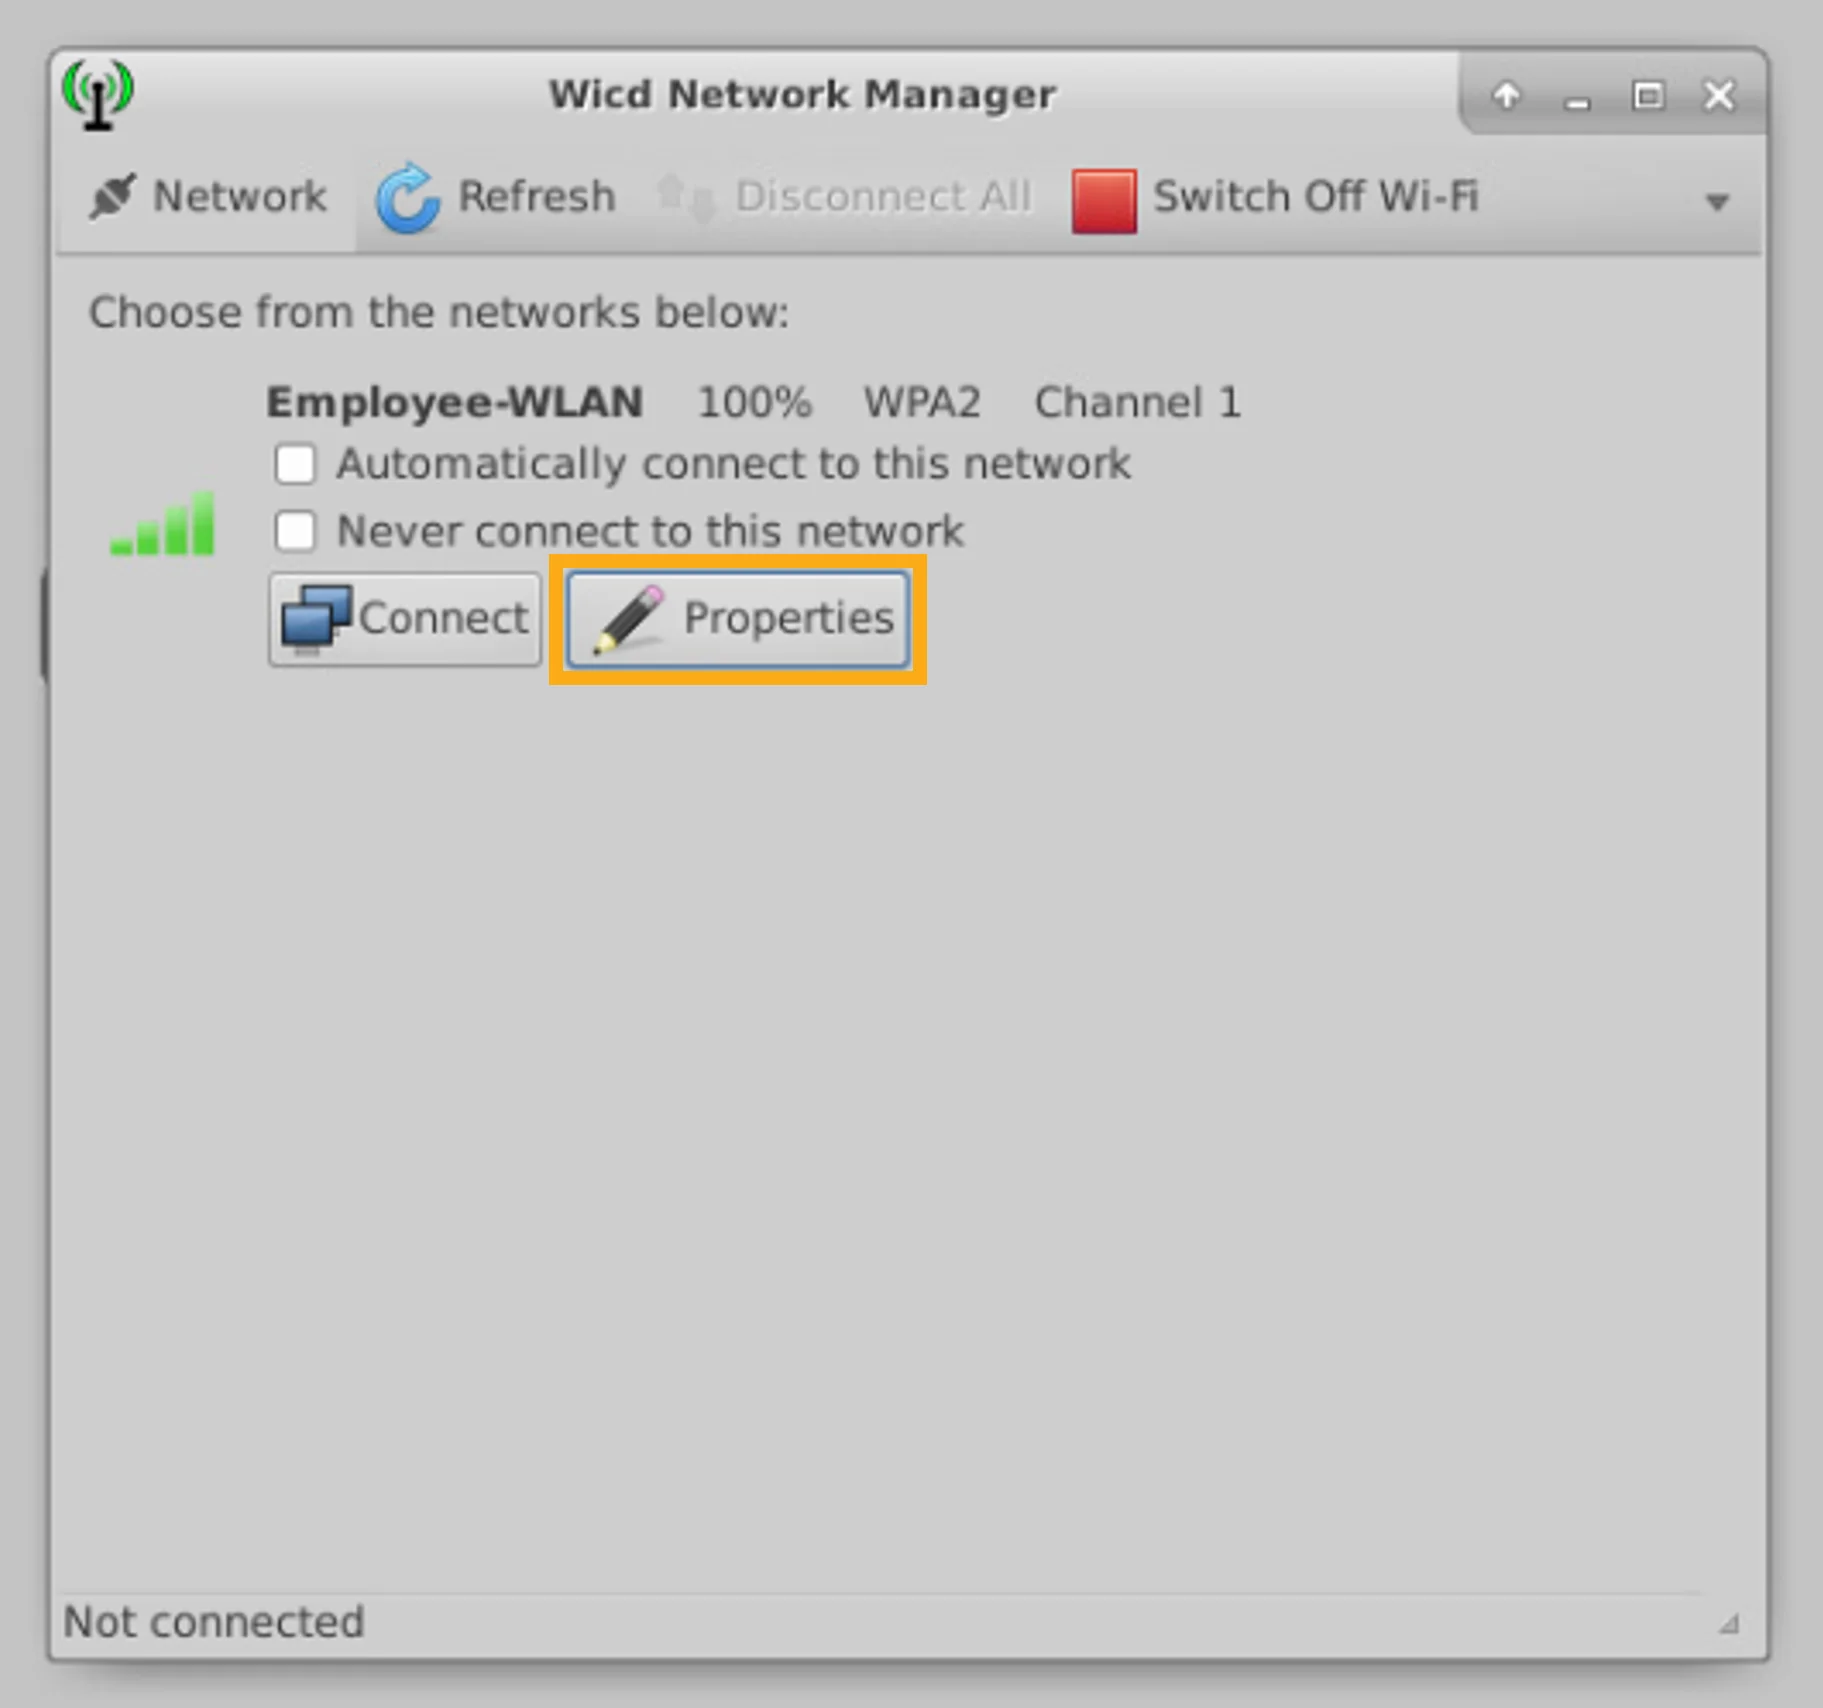
In theWicd Network Manager, click Properties.
在Wicd Network Manager中,按一下 Properties。
The Employee-WLAN - Properties window appears. The Use Encryption check box is automatically set, because this WLAN requires WPA2. Set the security type and the password as follows.
系統會顯示 Employee-WLAN - Properties 視窗。由於此 WLAN 需要 WPA2,Use Encryption 核取方塊會自動勾選。請依下列方式設定安全性類型與密碼。
- Security type: WPA 1/2 (Passphrase)Security type: WPA 1/2 (Passphrase)
- Preshared key: Cisco123Preshared key: Cisco123
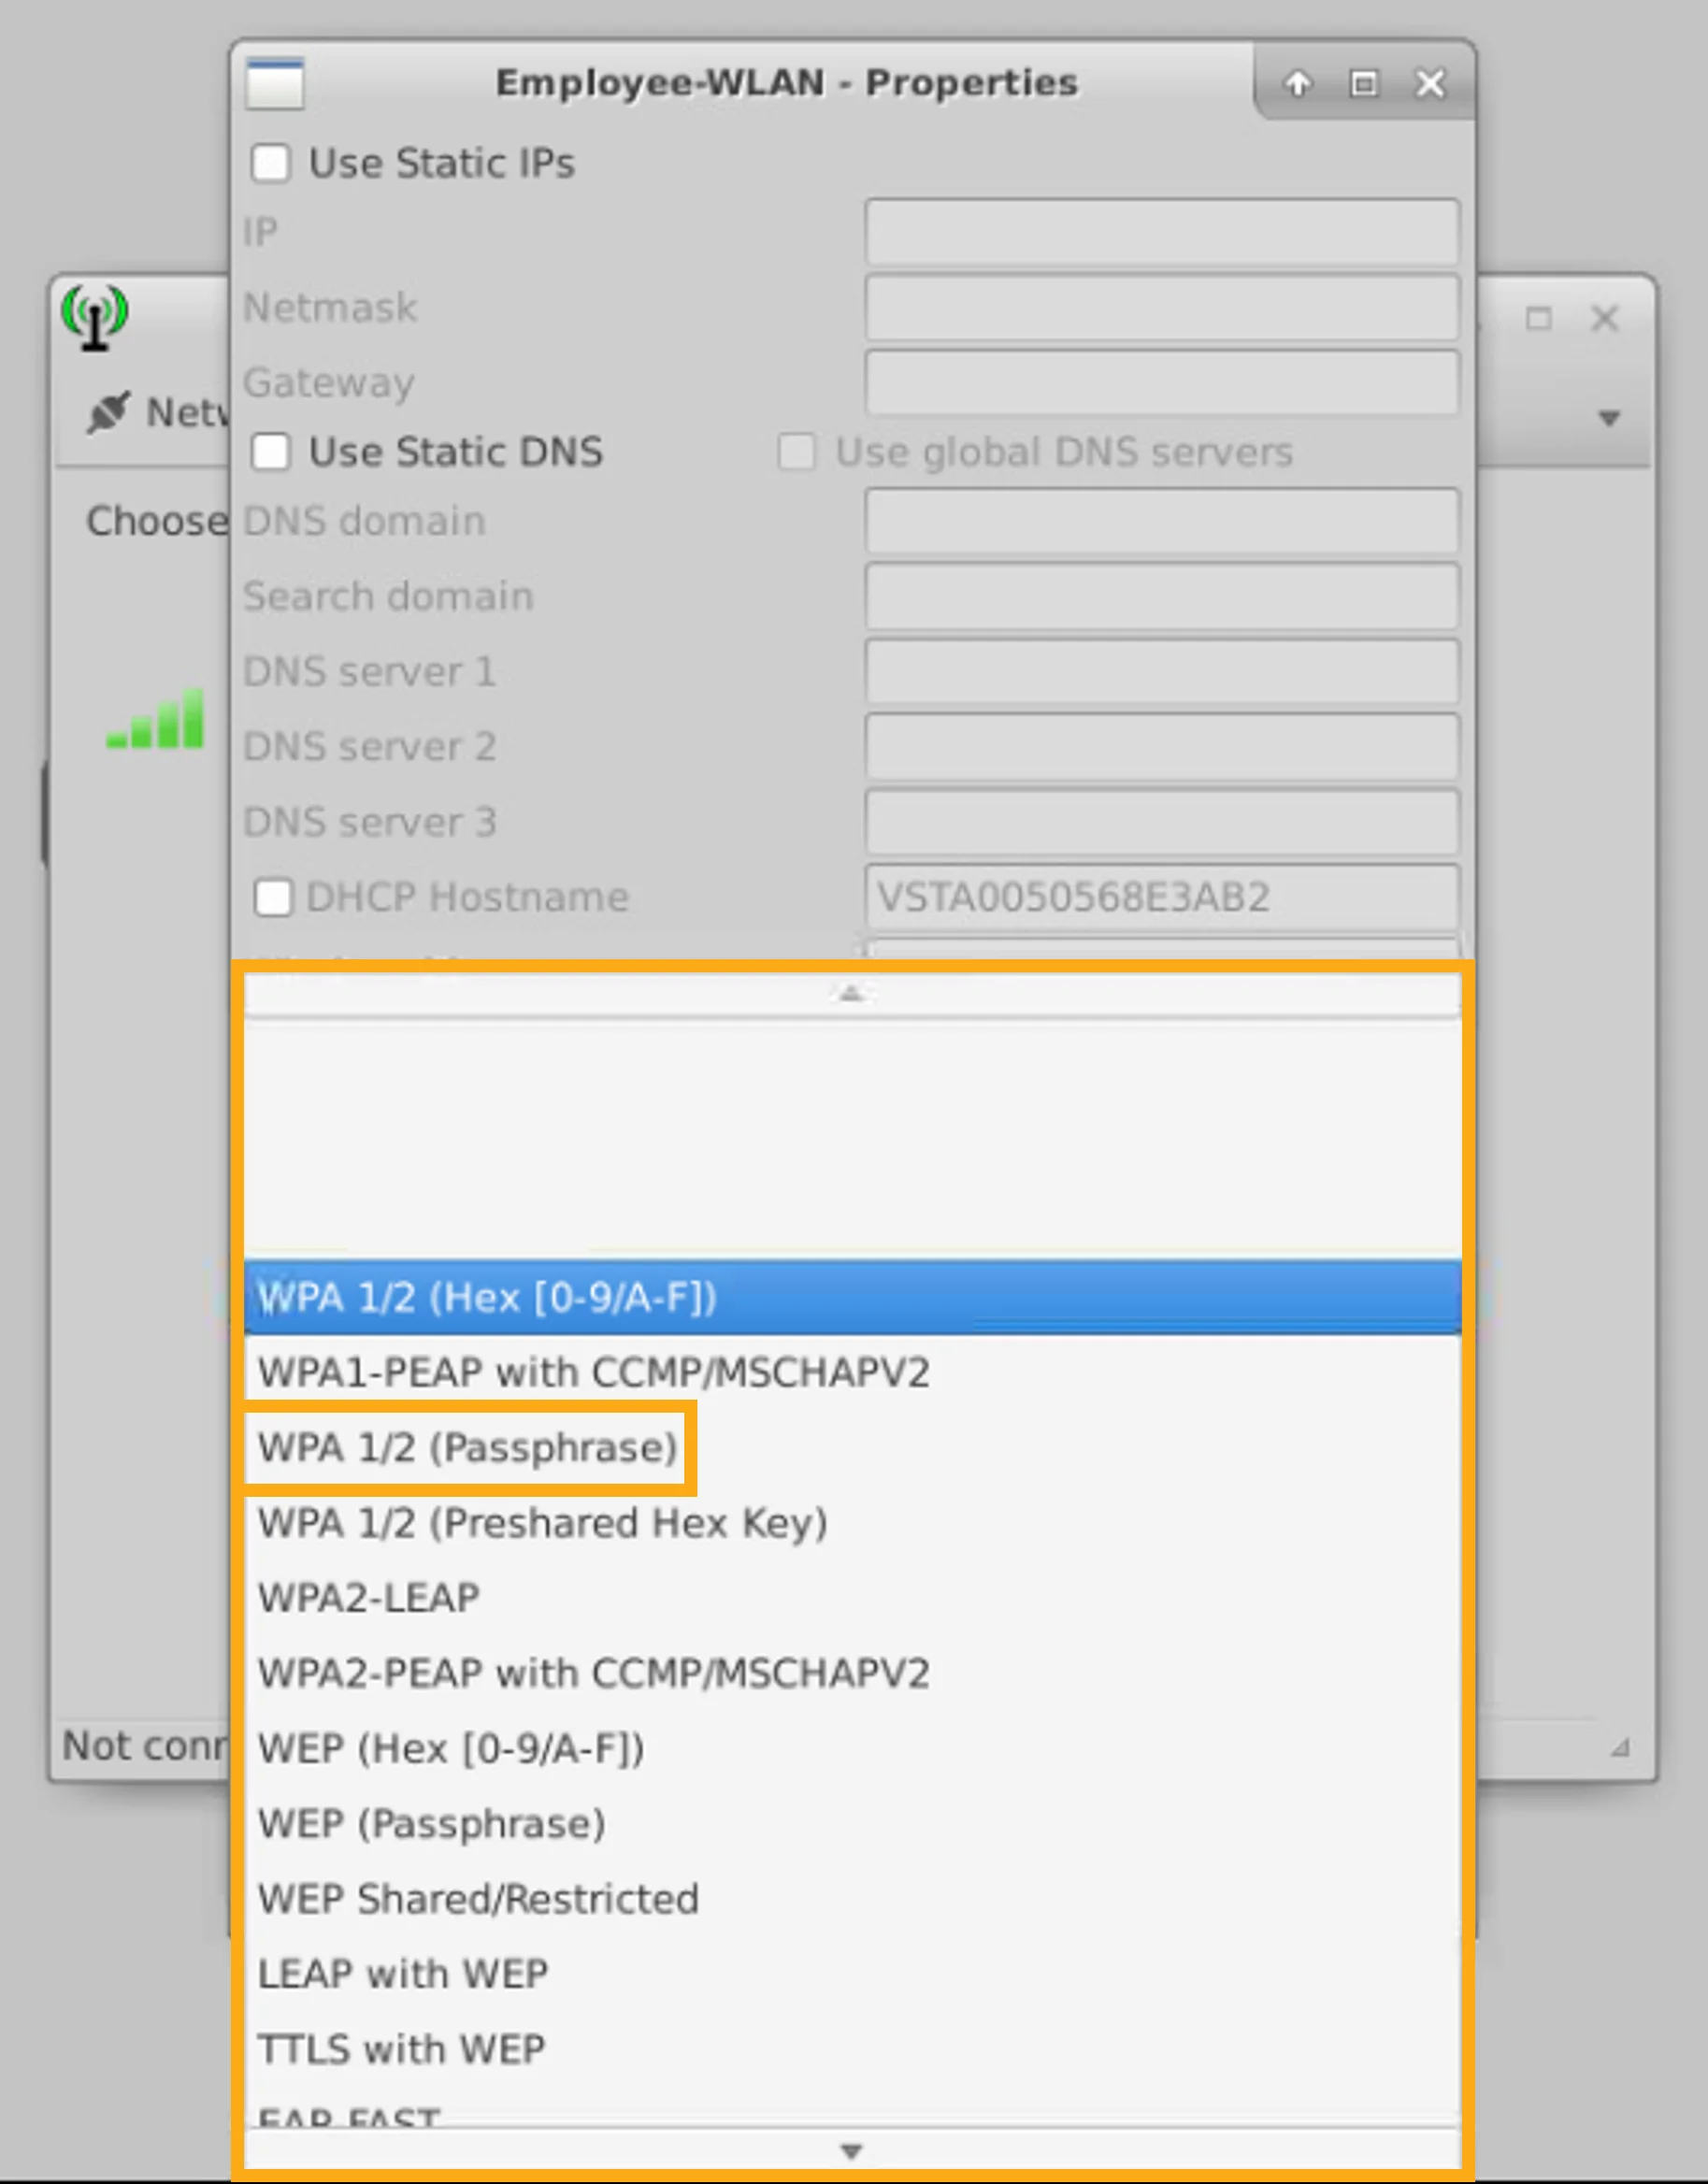
Click the currently selected security type WPA 1/2 (Hex [0-9/A-F]) to display all security options in the drop-down list.
按一下目前選取的安全性類型 WPA 1/2 (Hex [0-9/A-F]),以在下拉式清單中顯示所有安全性選項。
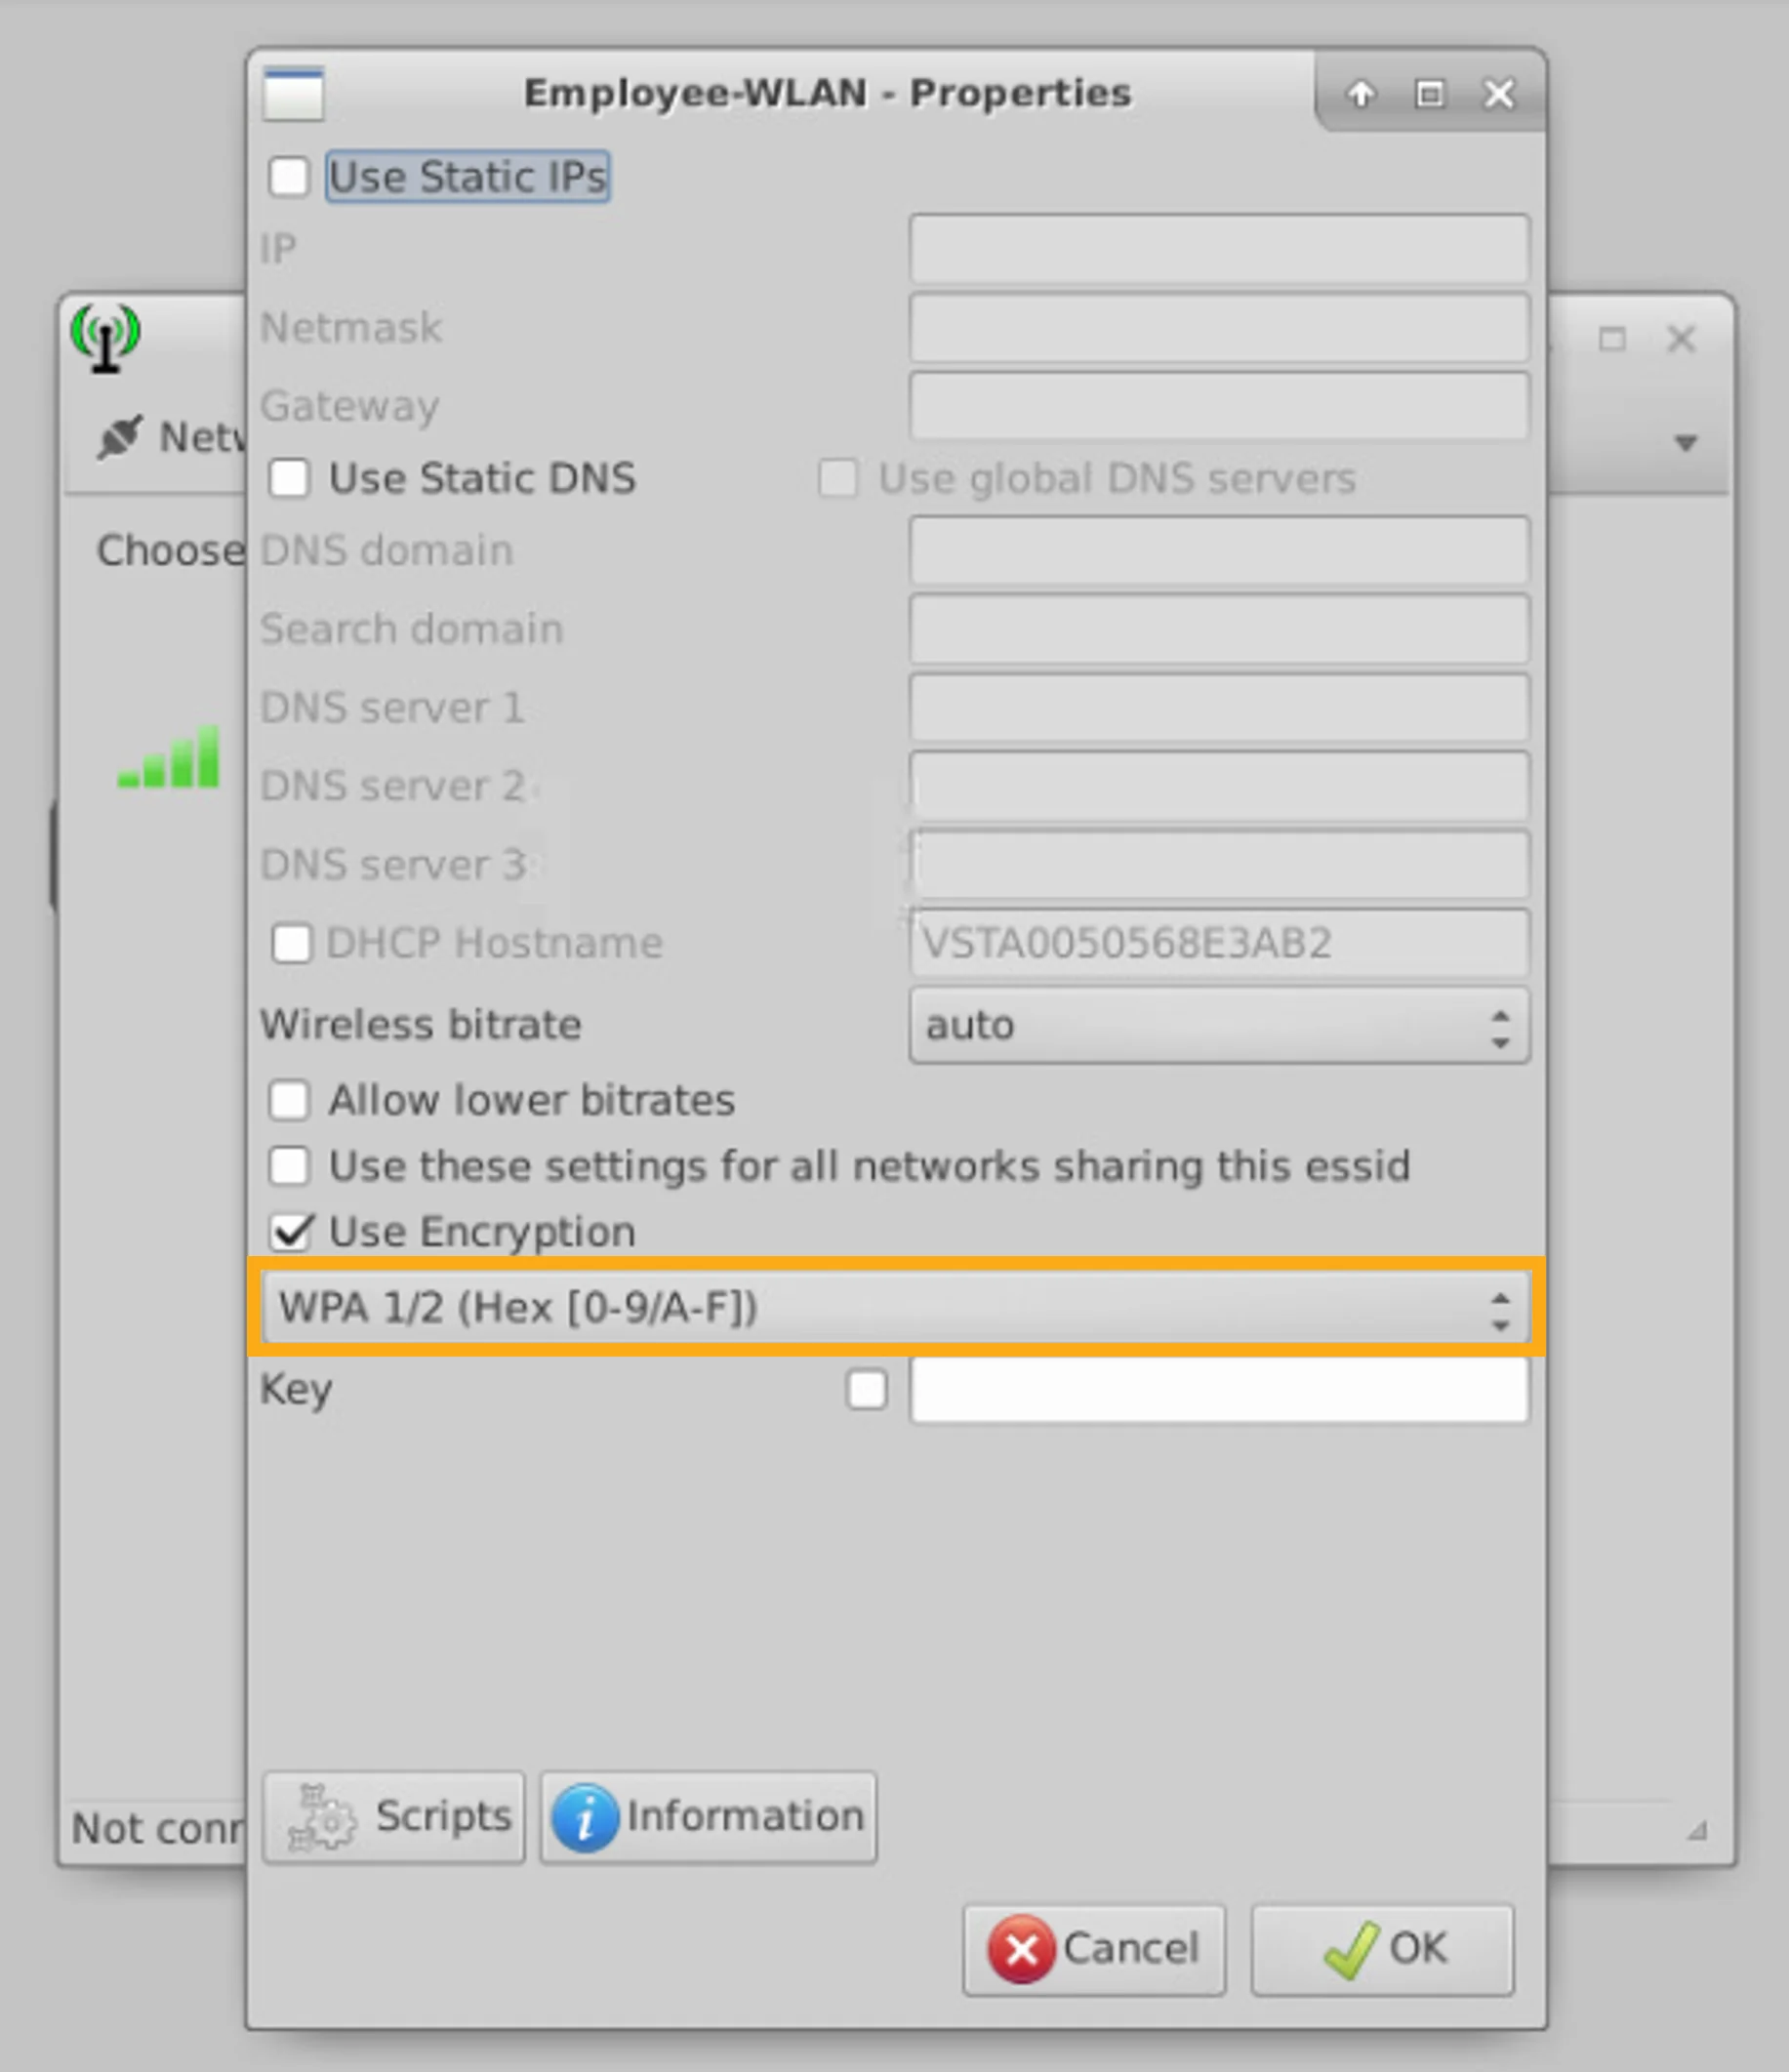
In the drop-down list, click the security type WPA 1/2 (Passphrase).
在下拉式清單中,按一下安全性類型 WPA 1/2 (Passphrase)。
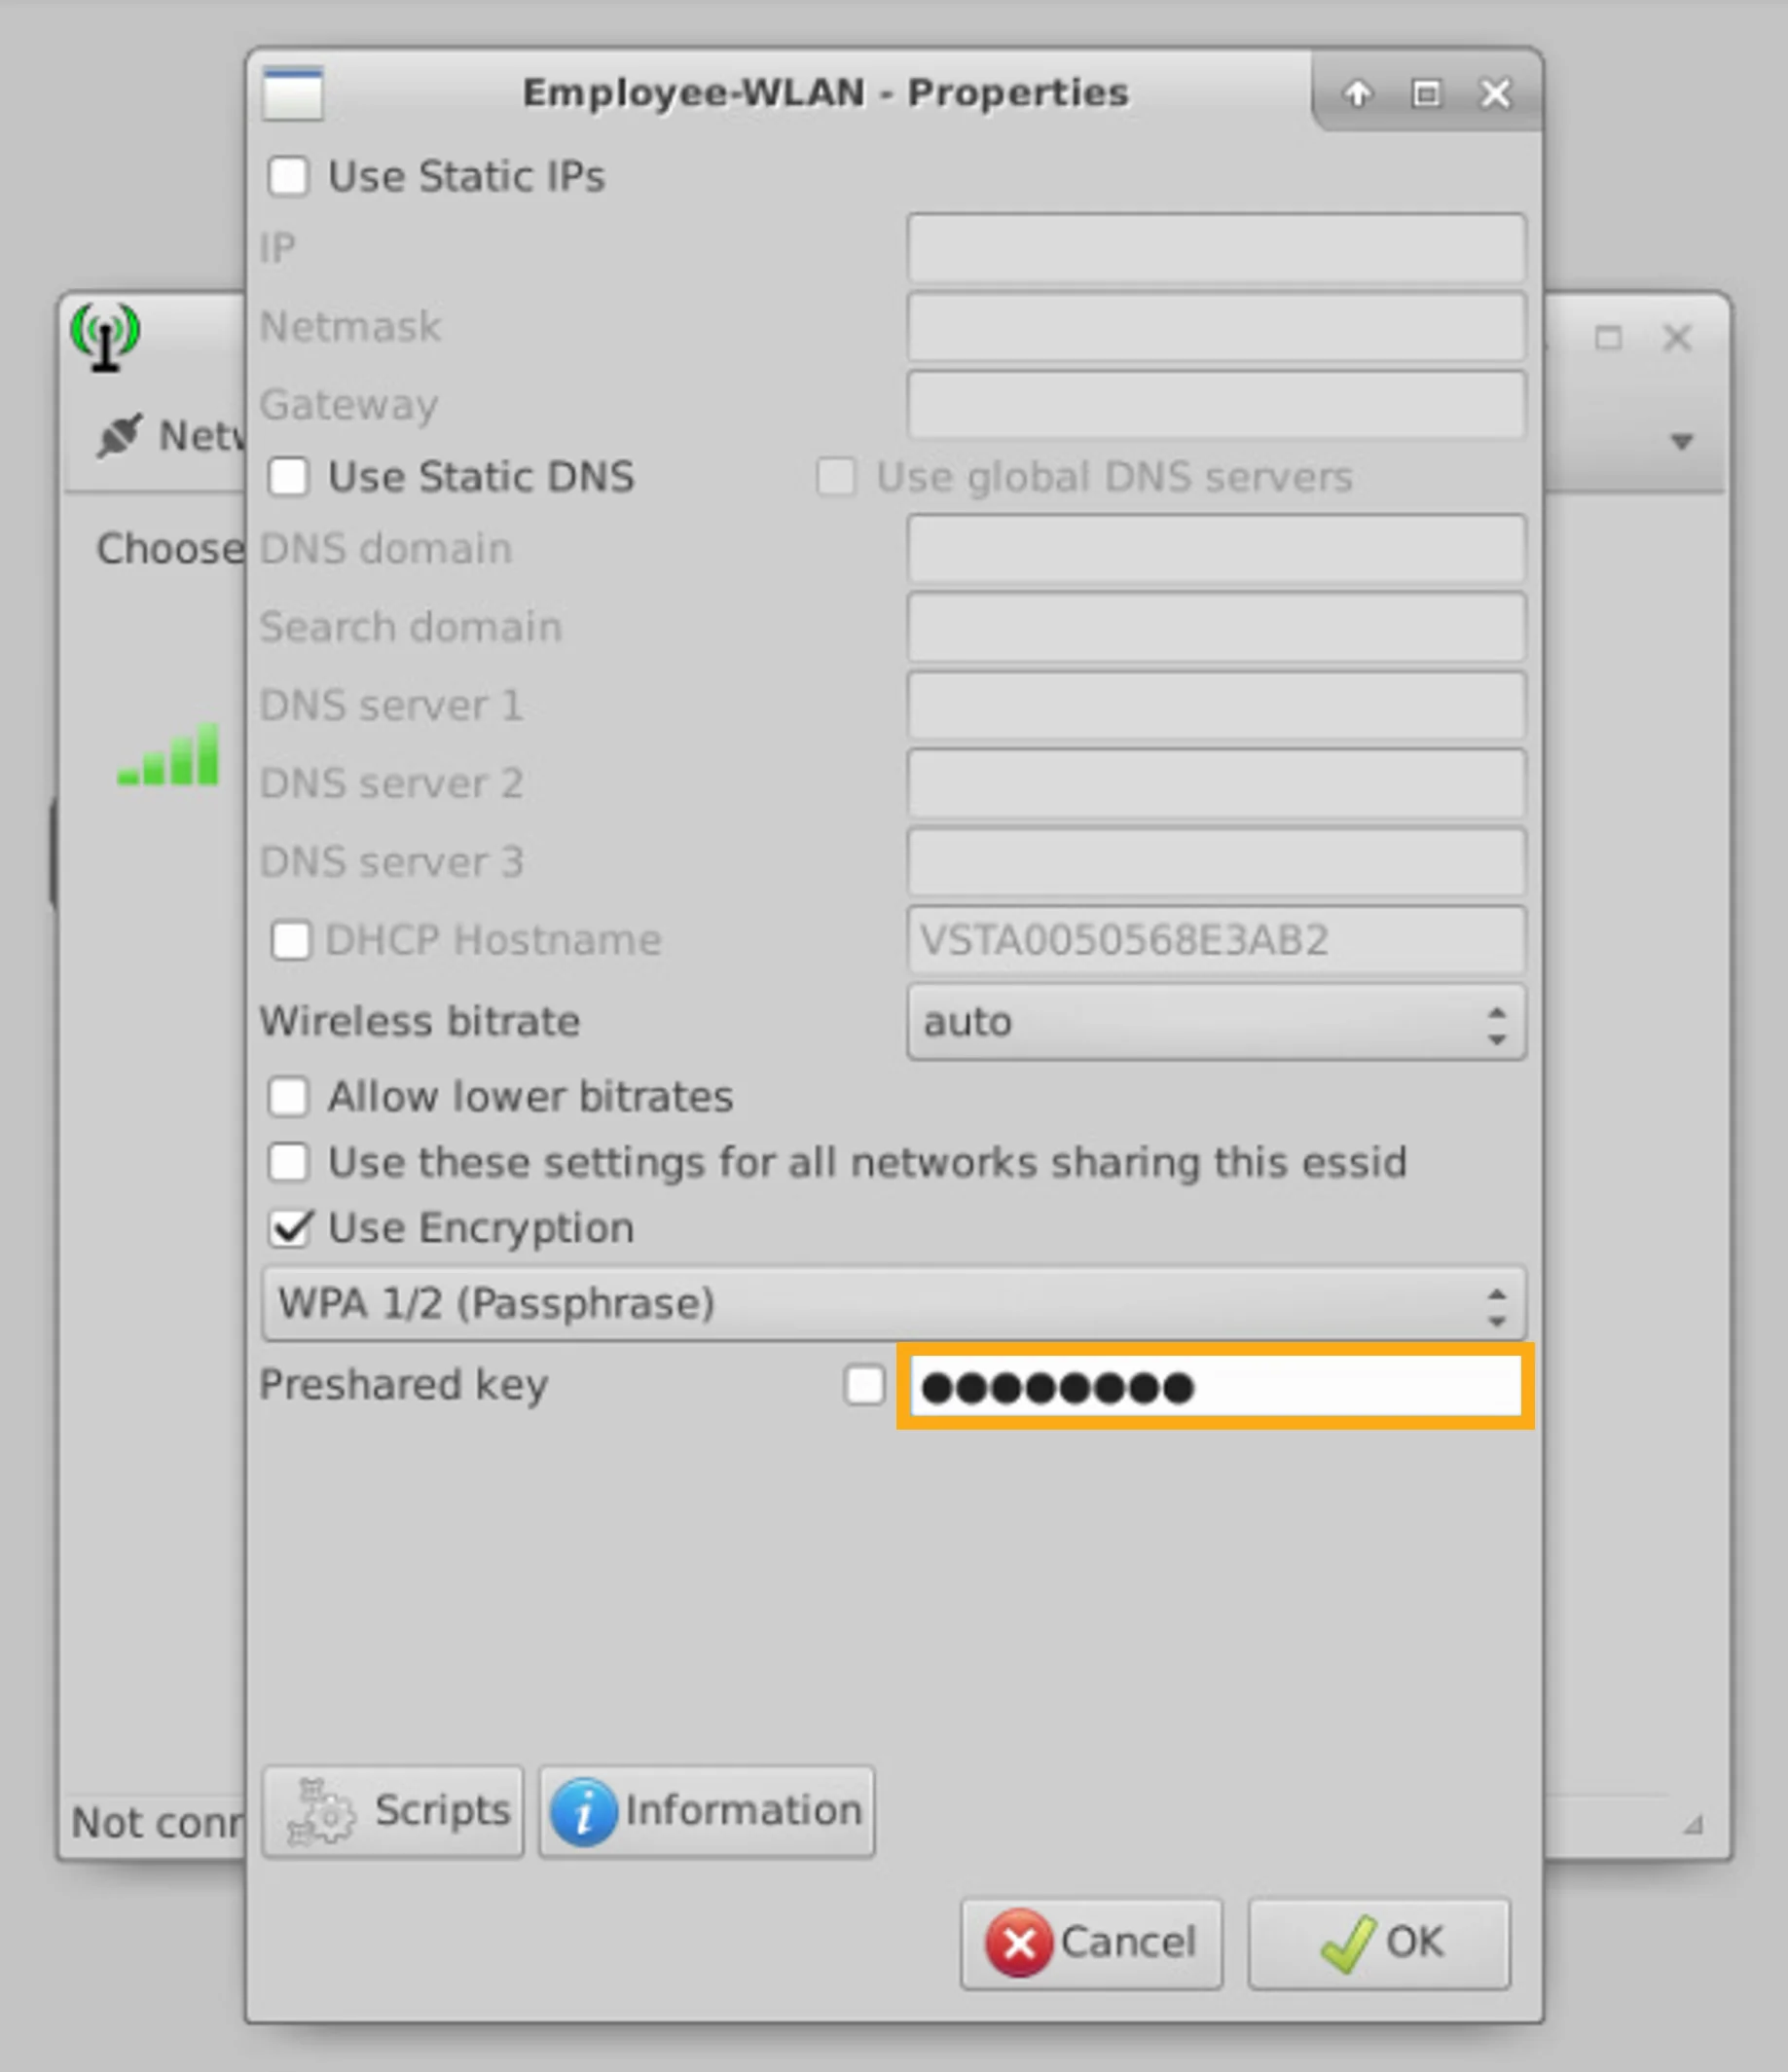
Click in the Preshared key input field and enter the key Cisco123.
按一下 Preshared key 輸入欄位,並輸入金鑰 Cisco123。
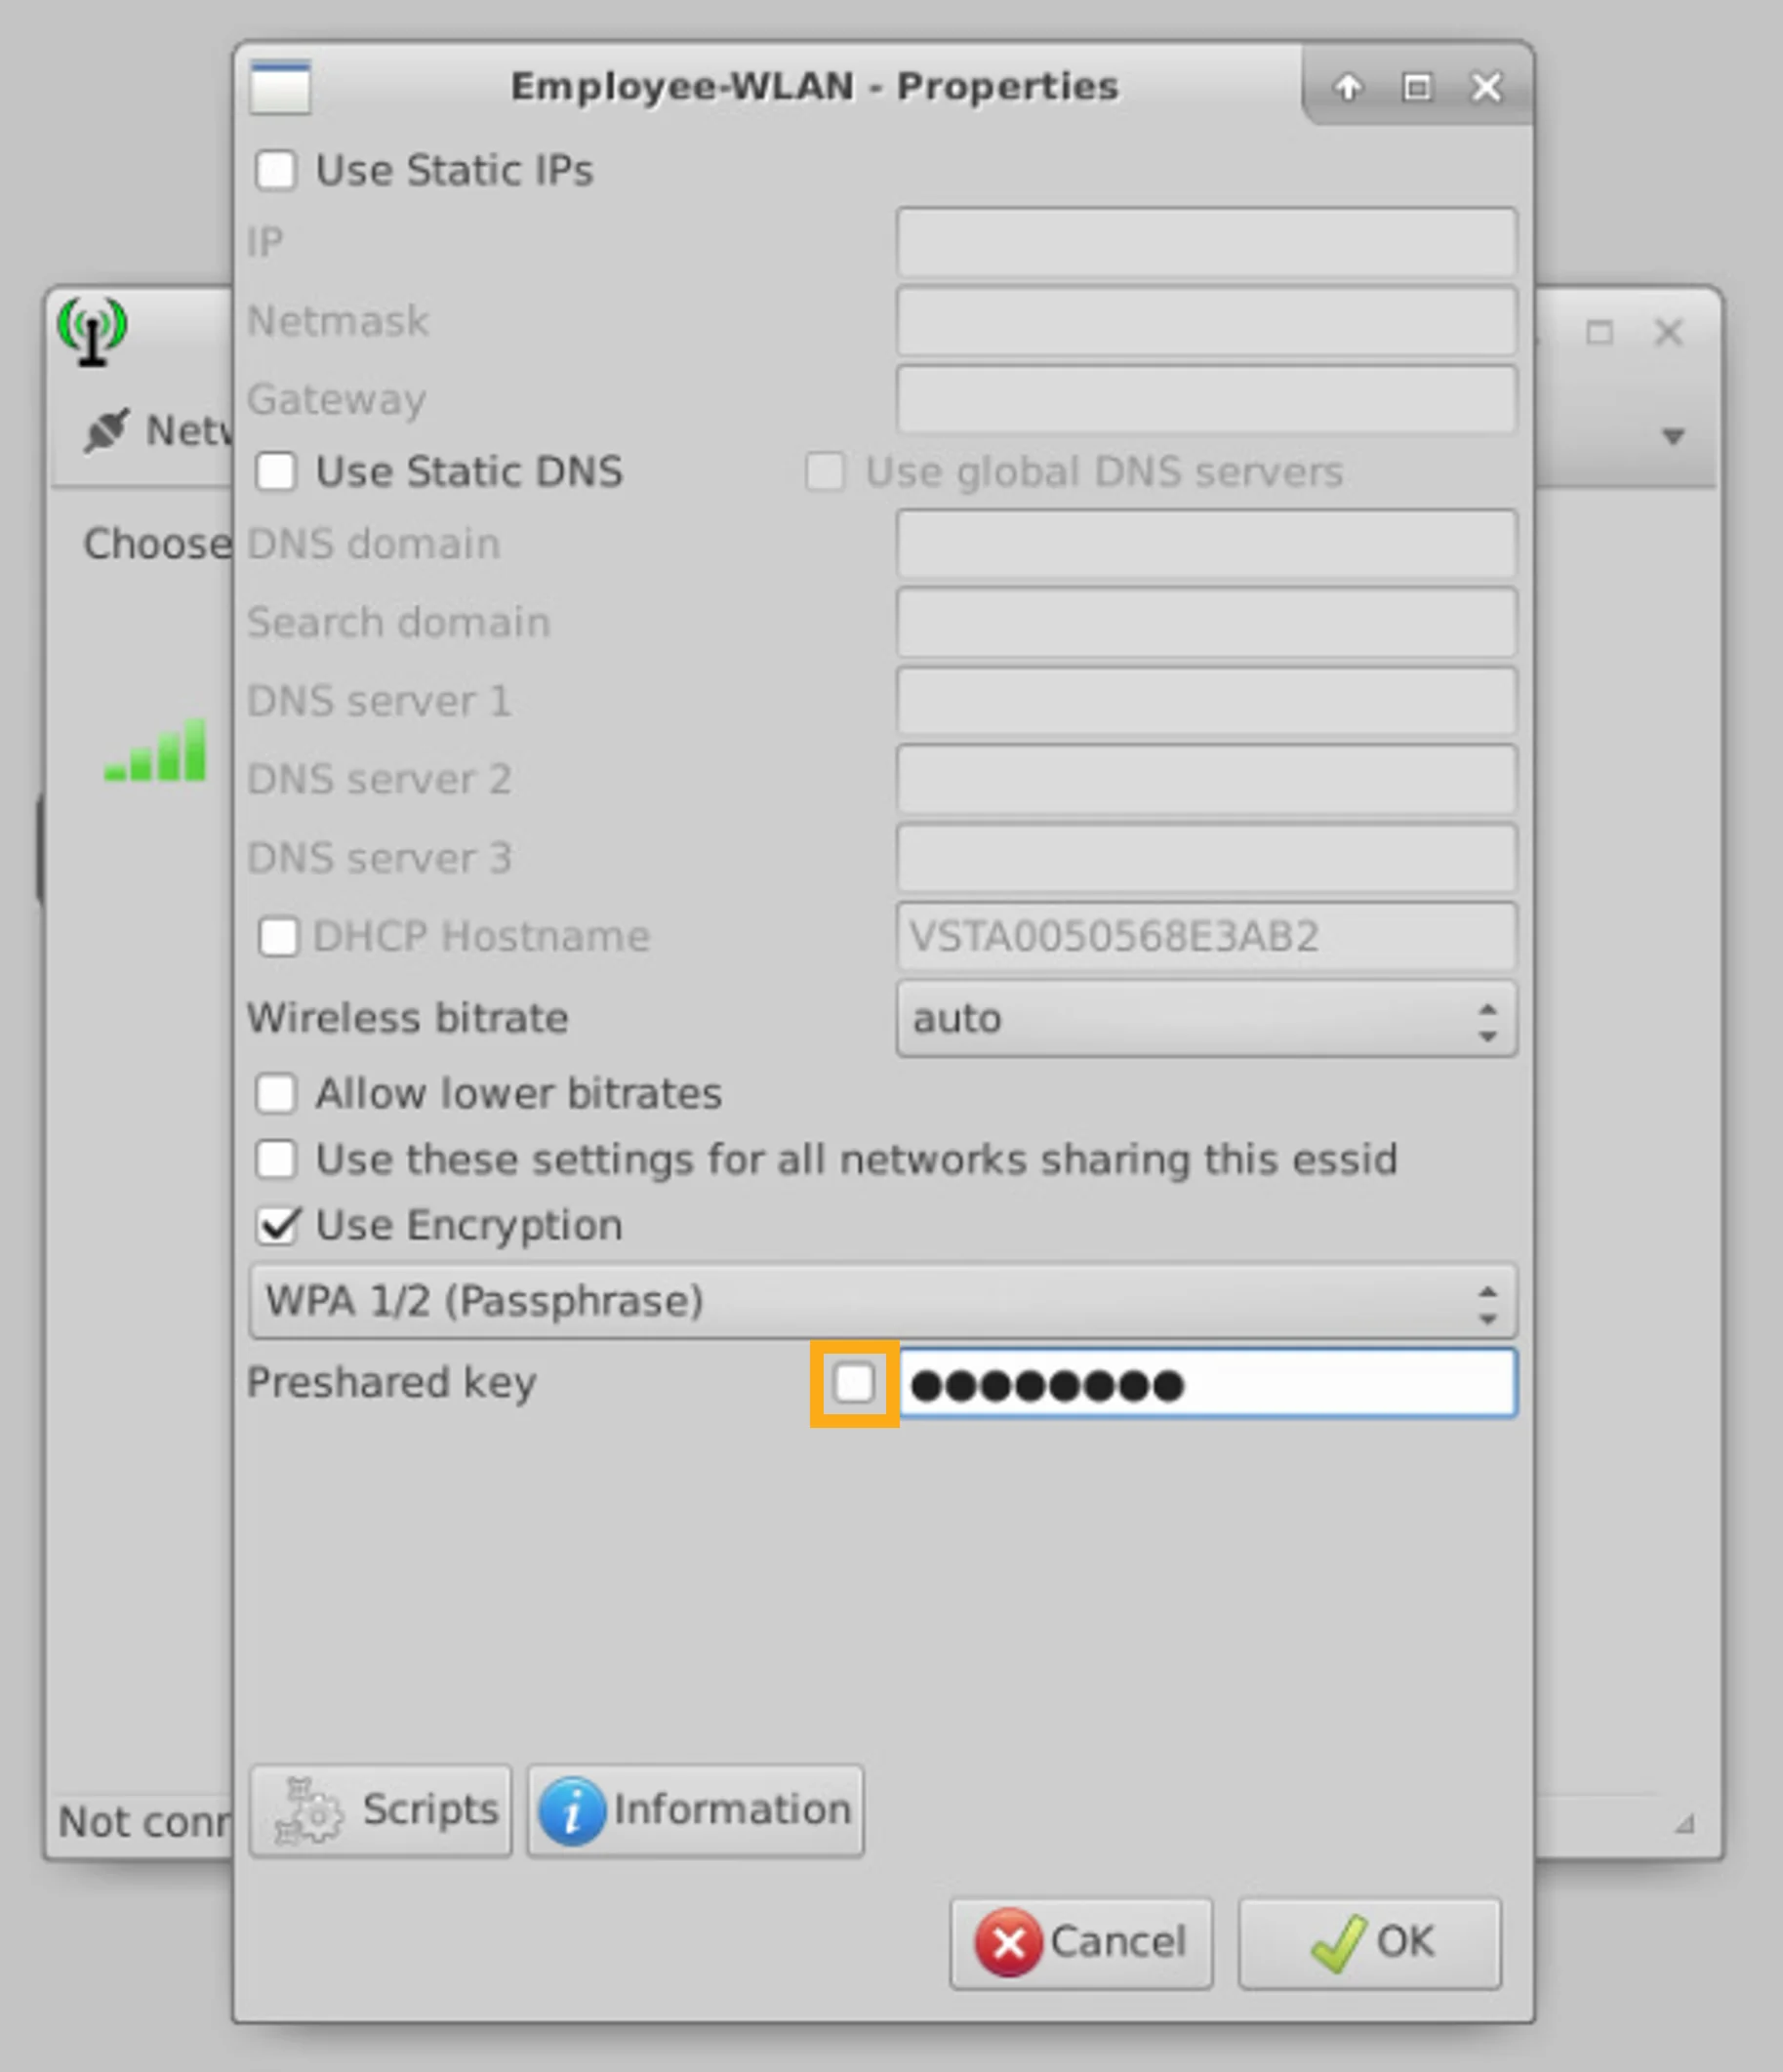
Check the check box that is to the left of the Preshared key input field
勾選 Preshared key 輸入欄位左側的核取方塊
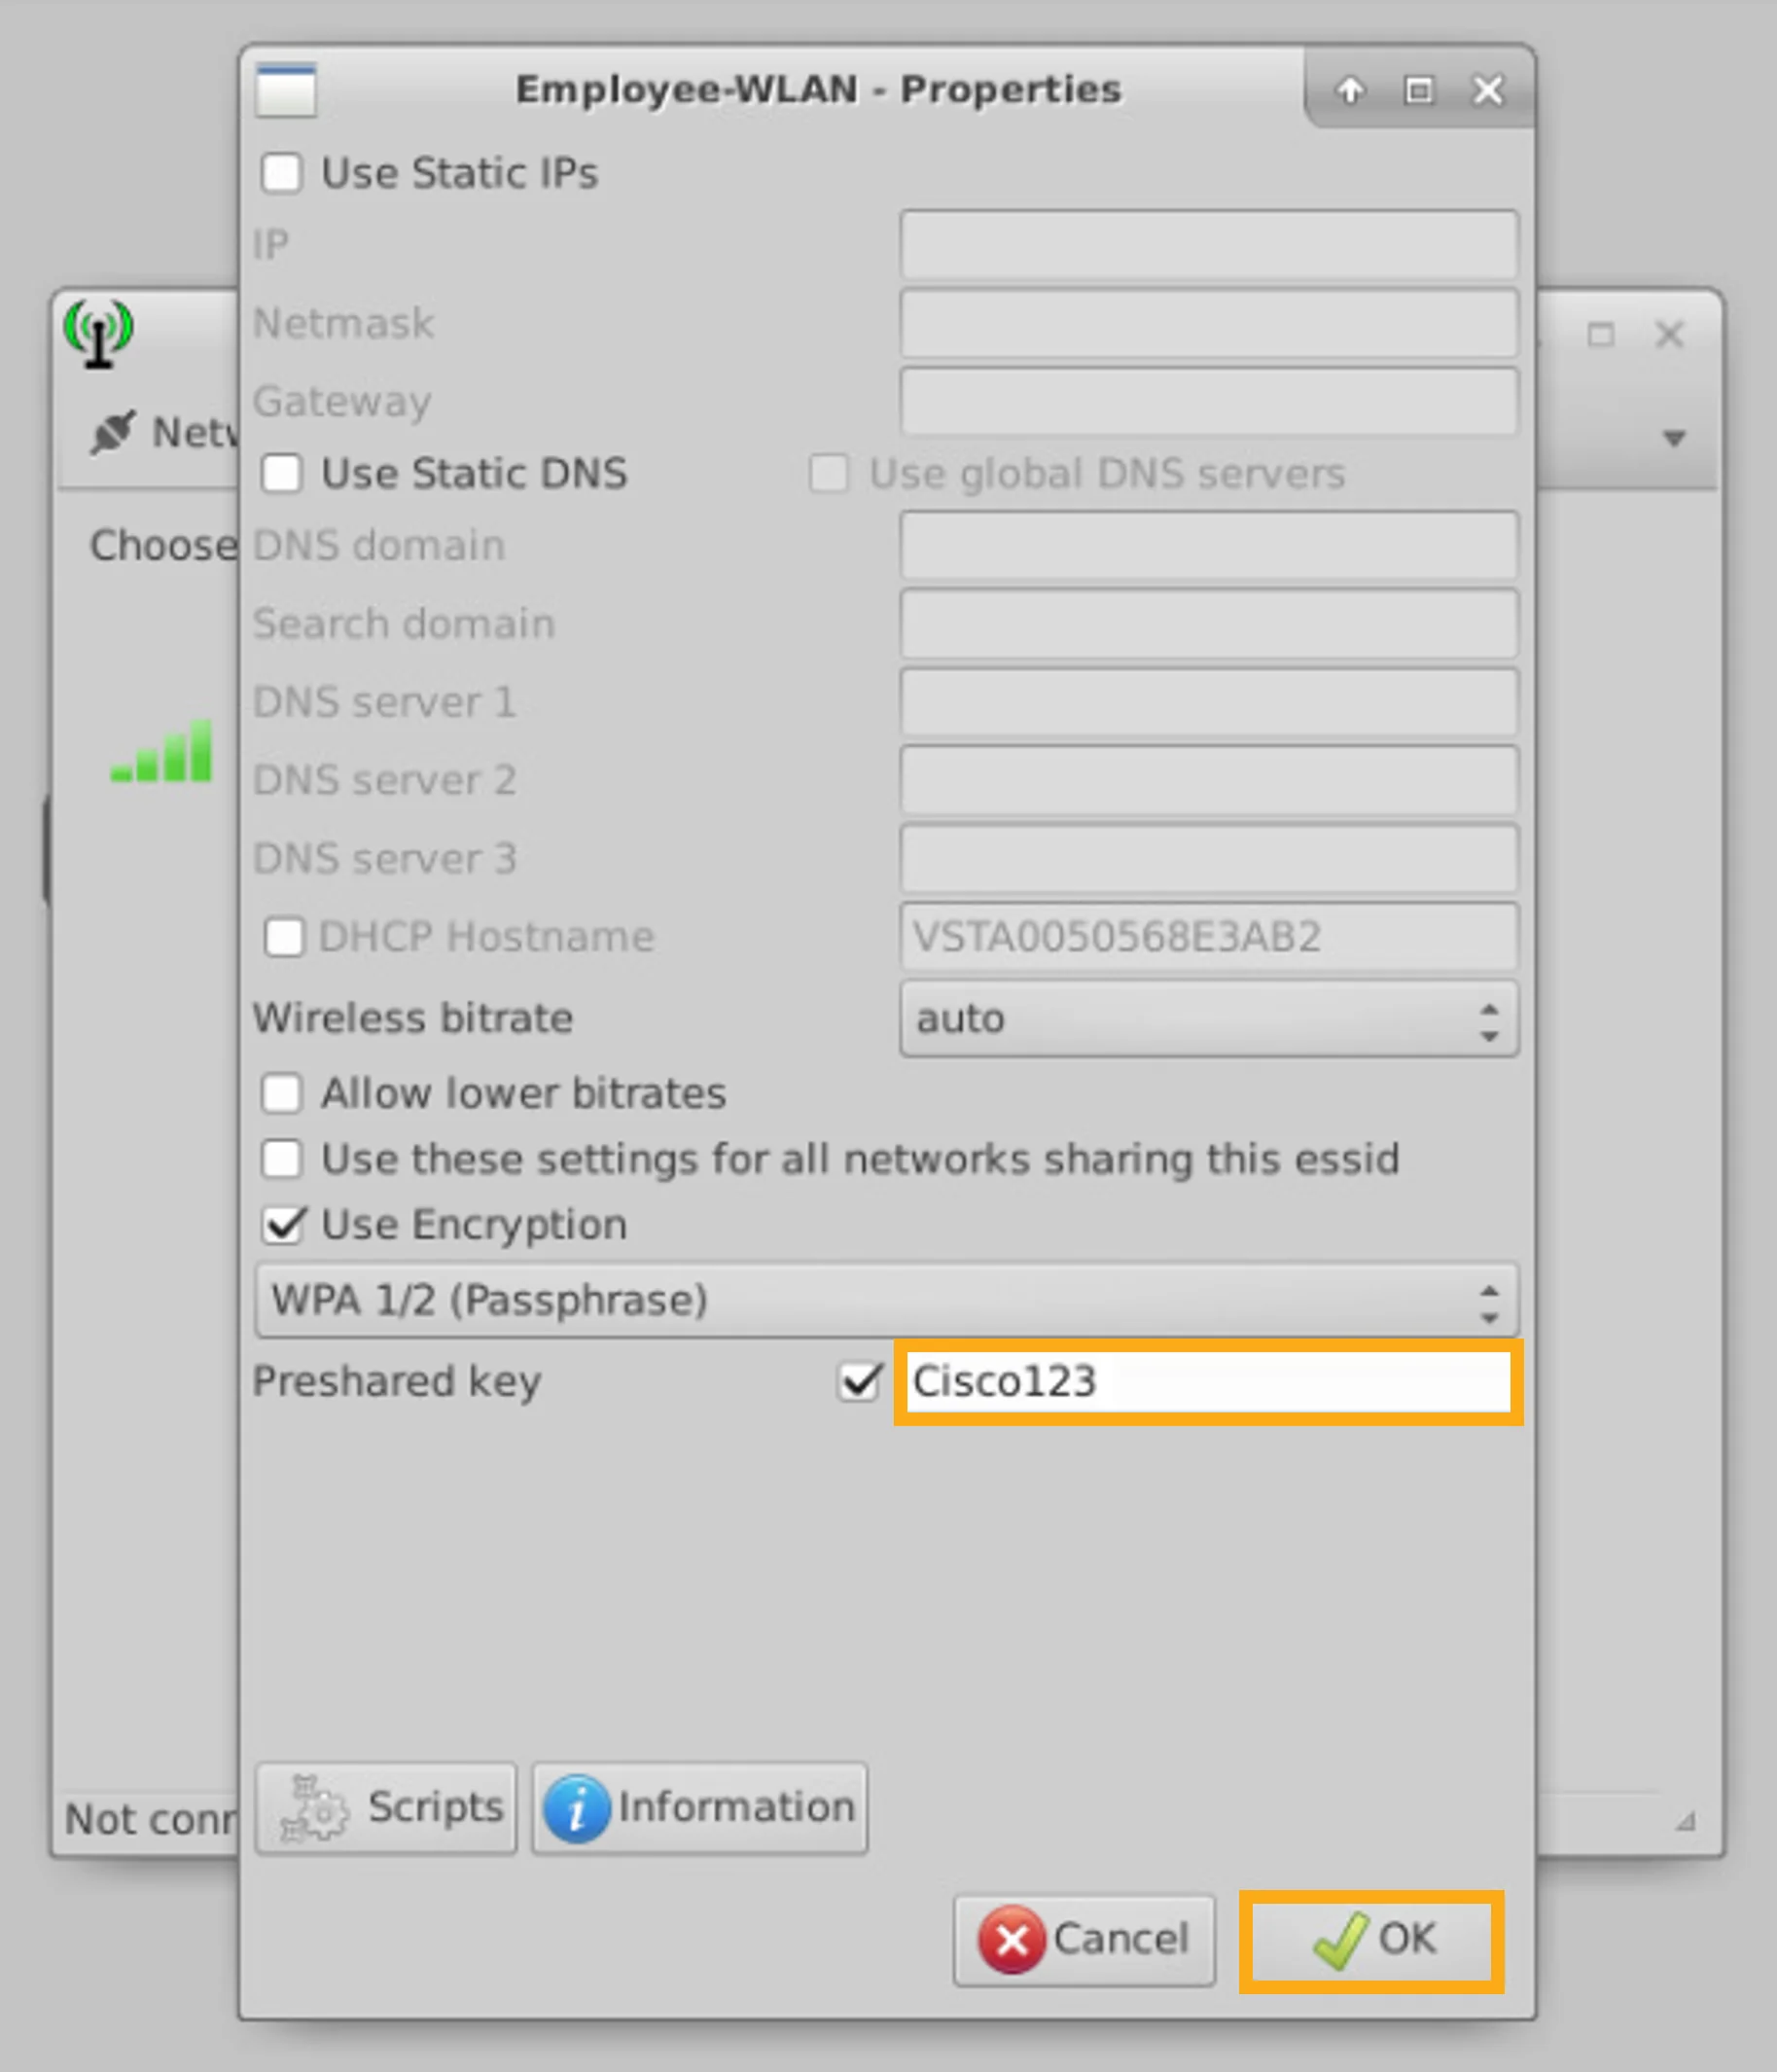
Note that the key is now displayed in cleartext. Verify the key. If needed, edit the key. When the key is correct, click OK.
請注意,金鑰現在以明文顯示。請驗證此金鑰,如有需要請進行編輯。確認金鑰正確後,按一下 OK。
Click Connect to connect to this WLAN.
按一下 Connect,連線至此 WLAN。
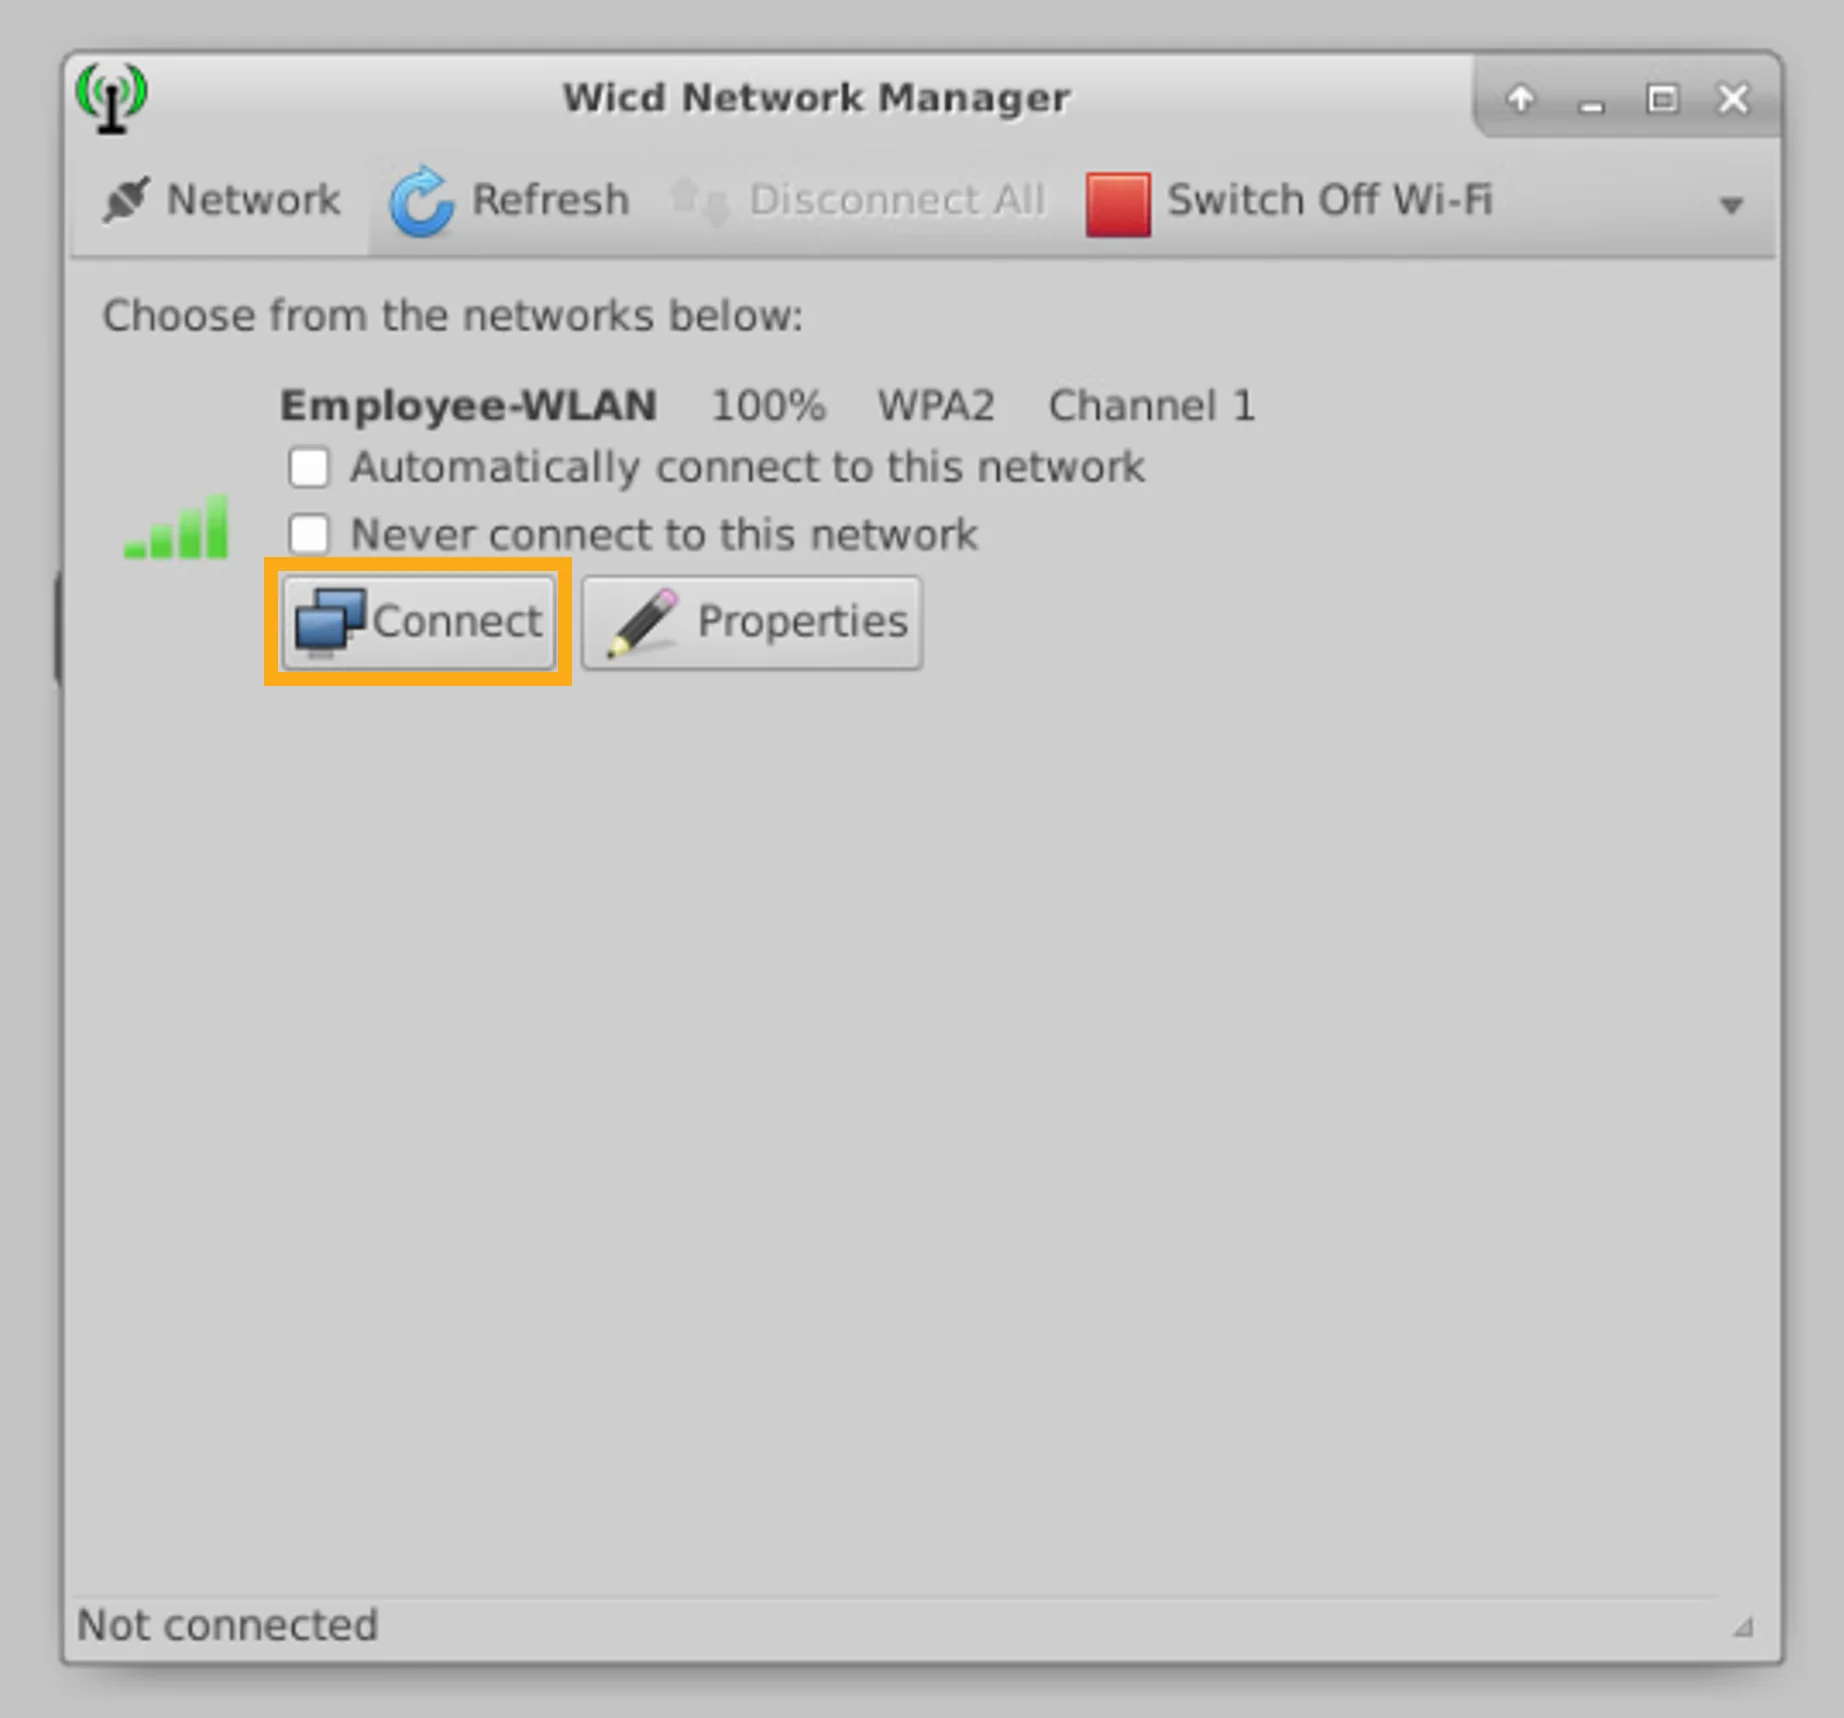
Verify that Client PC 2 is connected to the Employee-WLAN and that the client was assigned an IP address of network 10.10.30.0/24.
驗證 Client PC 2 是否已連線至 Employee-WLAN,且用戶端已取得 10.10.30.0/24 網路的 IP 位址。
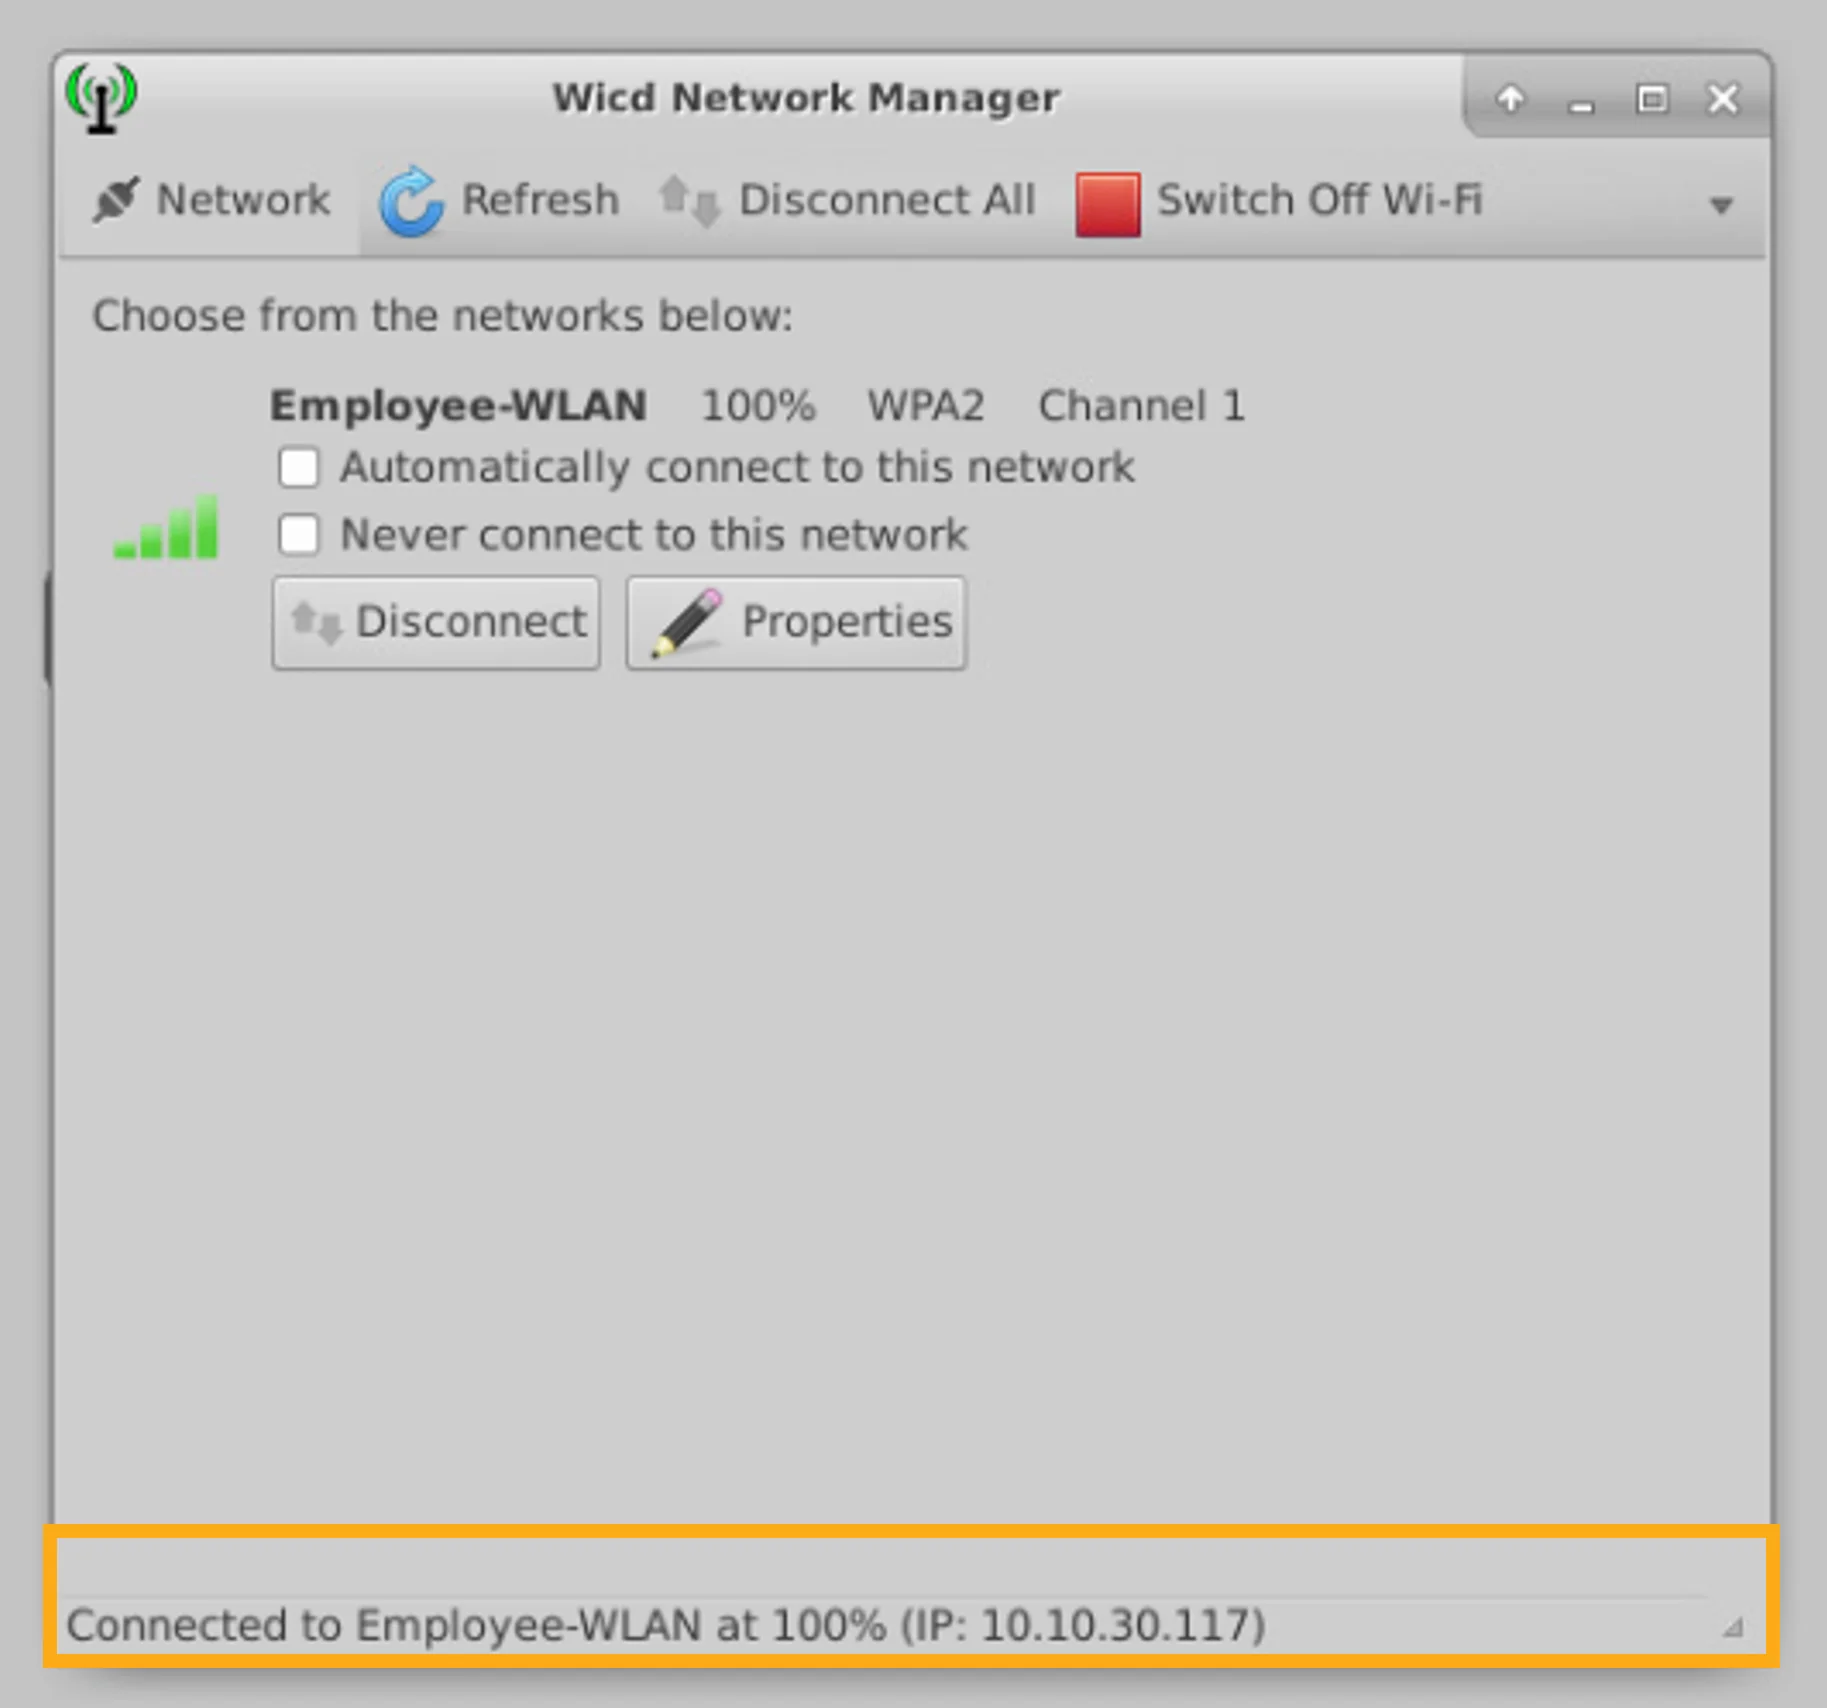
Verify the Client PC 2 Network Connectivity
驗證 Client PC 2 的網路連線
In the next steps, you will verify network connectivity by pinging the default gateway and Client PC 1.
在接下來的步驟中,您將 ping 預設閘道與 Client PC 1,以驗證網路連線。
On Client PC 2, open a Terminalwindow, and verify network connectivity by pinging the default gateway at 10.10.30.1. Validate the results.
在 Client PC 2 上開啟 Terminal視窗,藉由 ping 預設閘道 10.10.30.1 來驗證網路連線。驗證結果。
You will see that the first ping timed out, but the following four pings were successful.
您將看到第一次 ping 逾時,但接下來四次 ping 都成功。
Perform the following procedure:
請執行下列程序:
- Click the Terminal icon.按一下 Terminal 圖示。
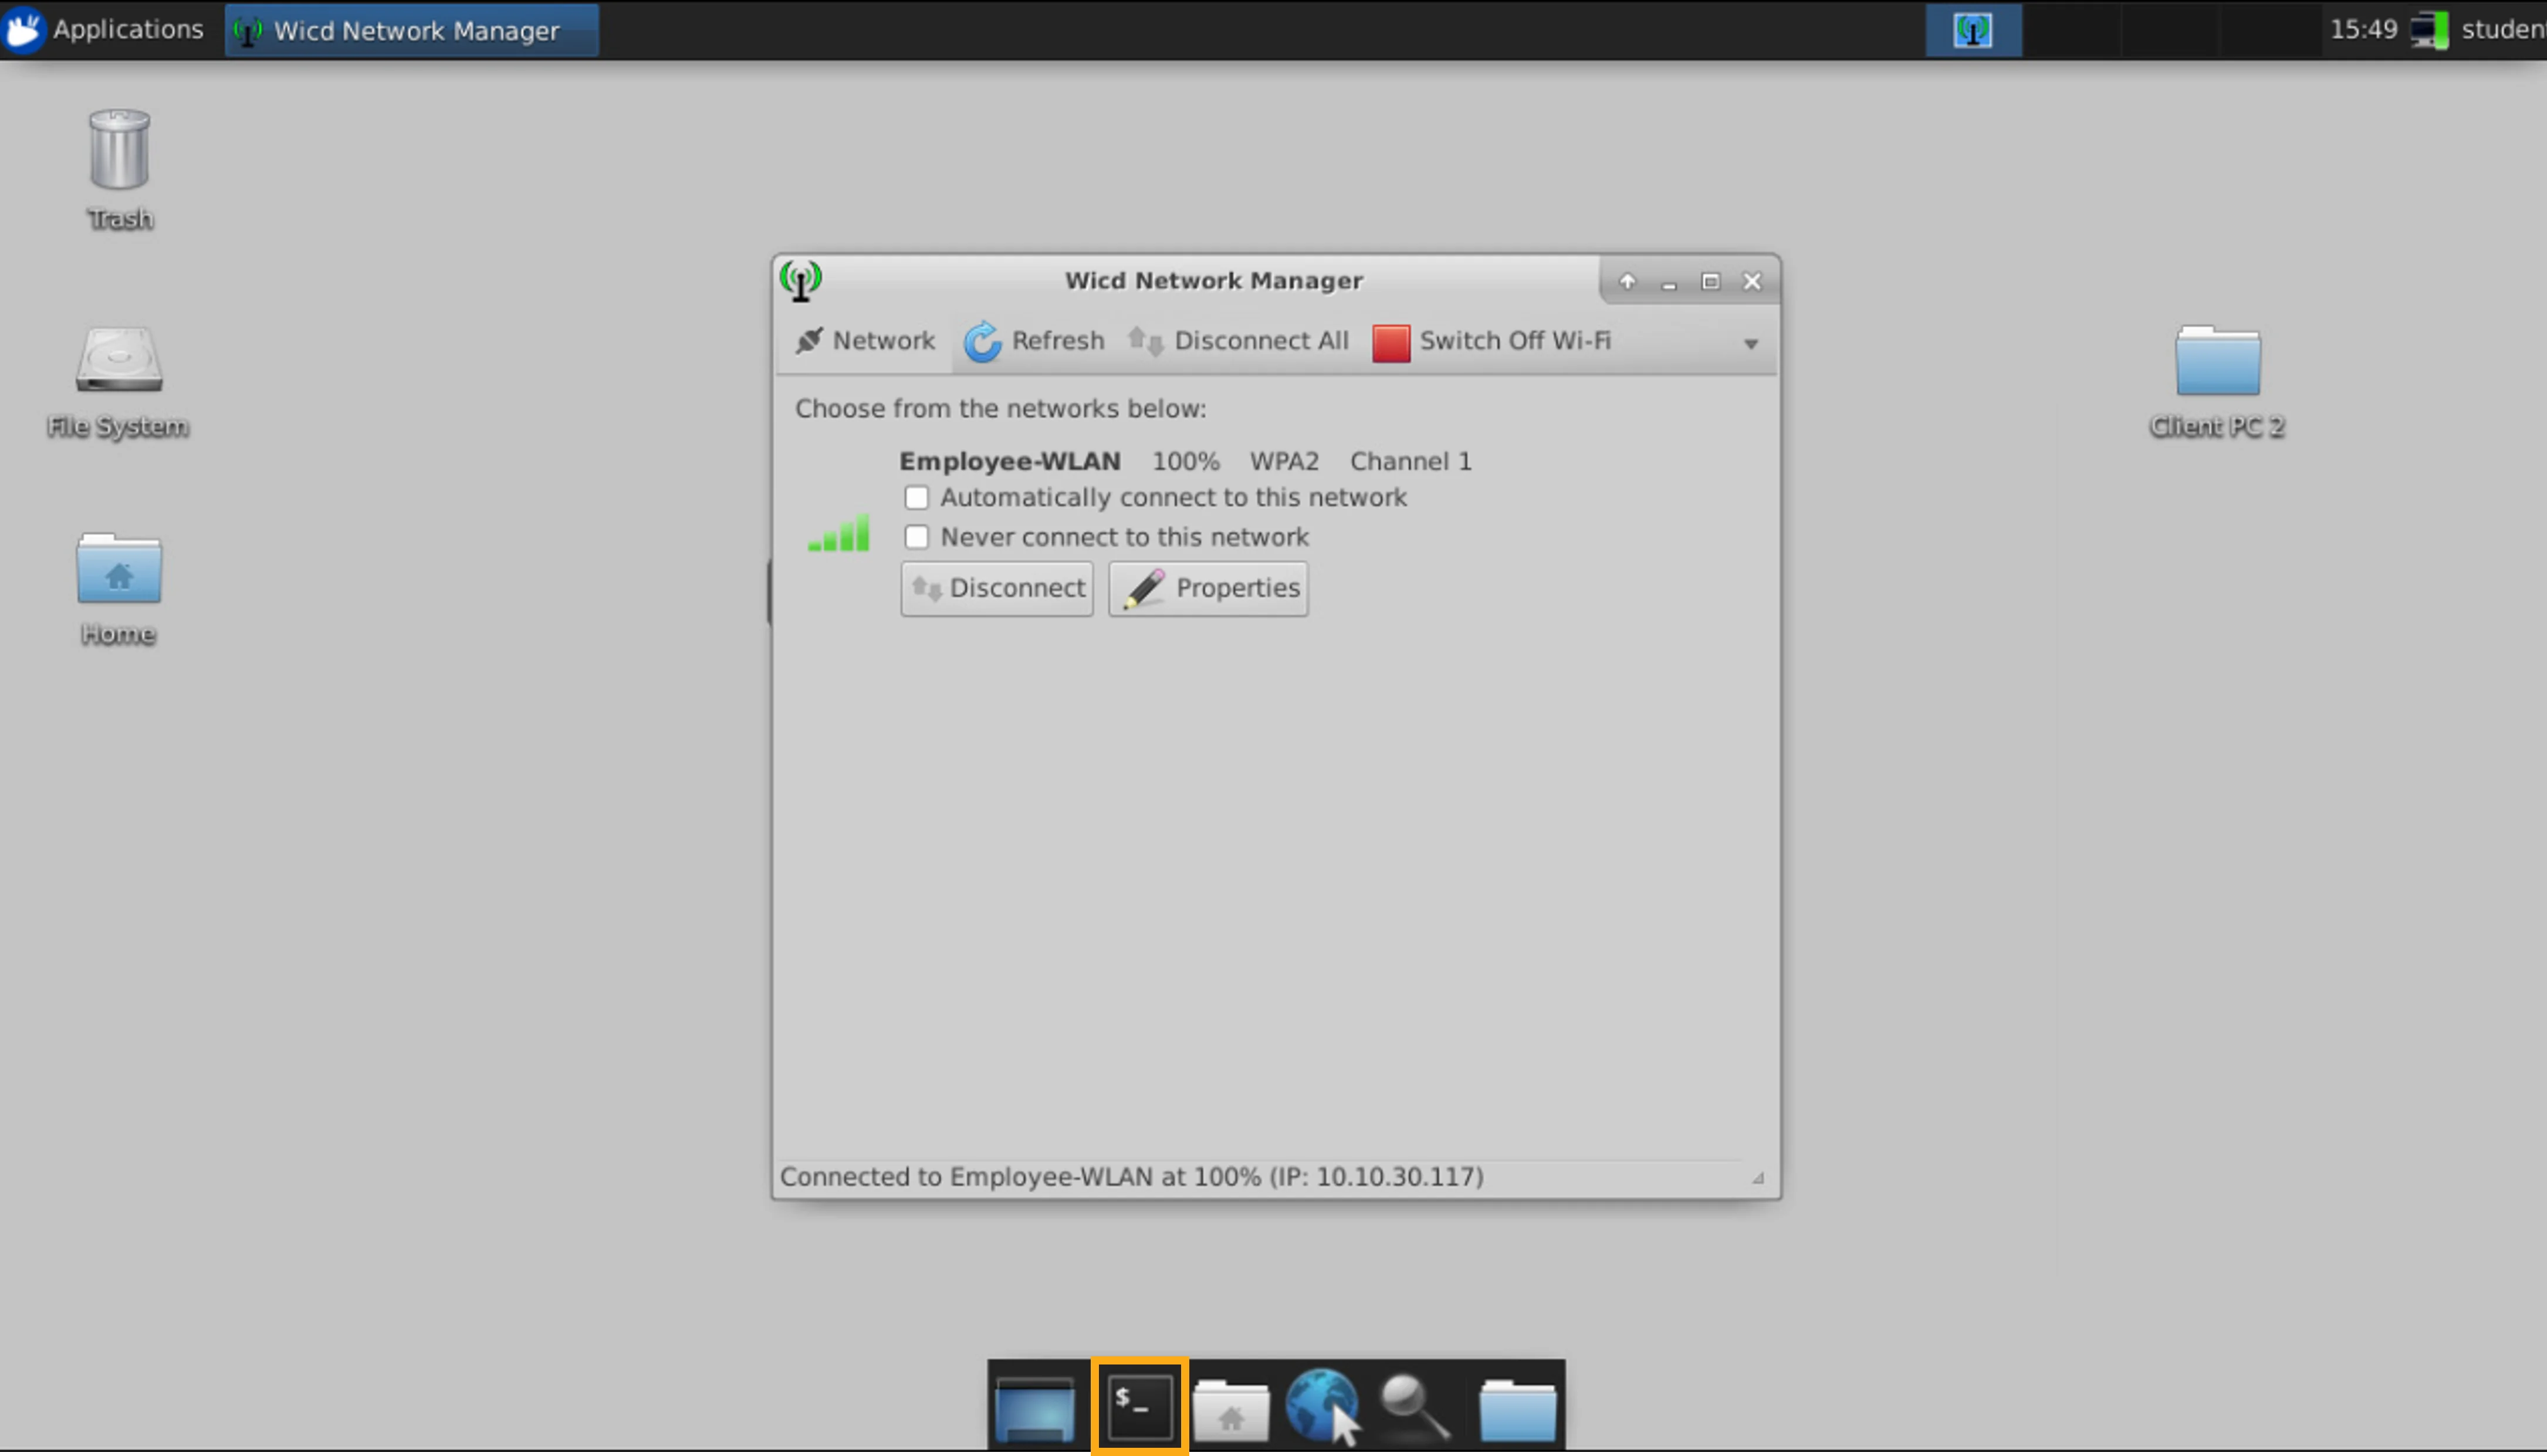
- In the terminal window, enter the
ping 10.10.30.1command. Then, press Enter.在終端機視窗中,輸入ping 10.10.30.1命令,然後按 Enter。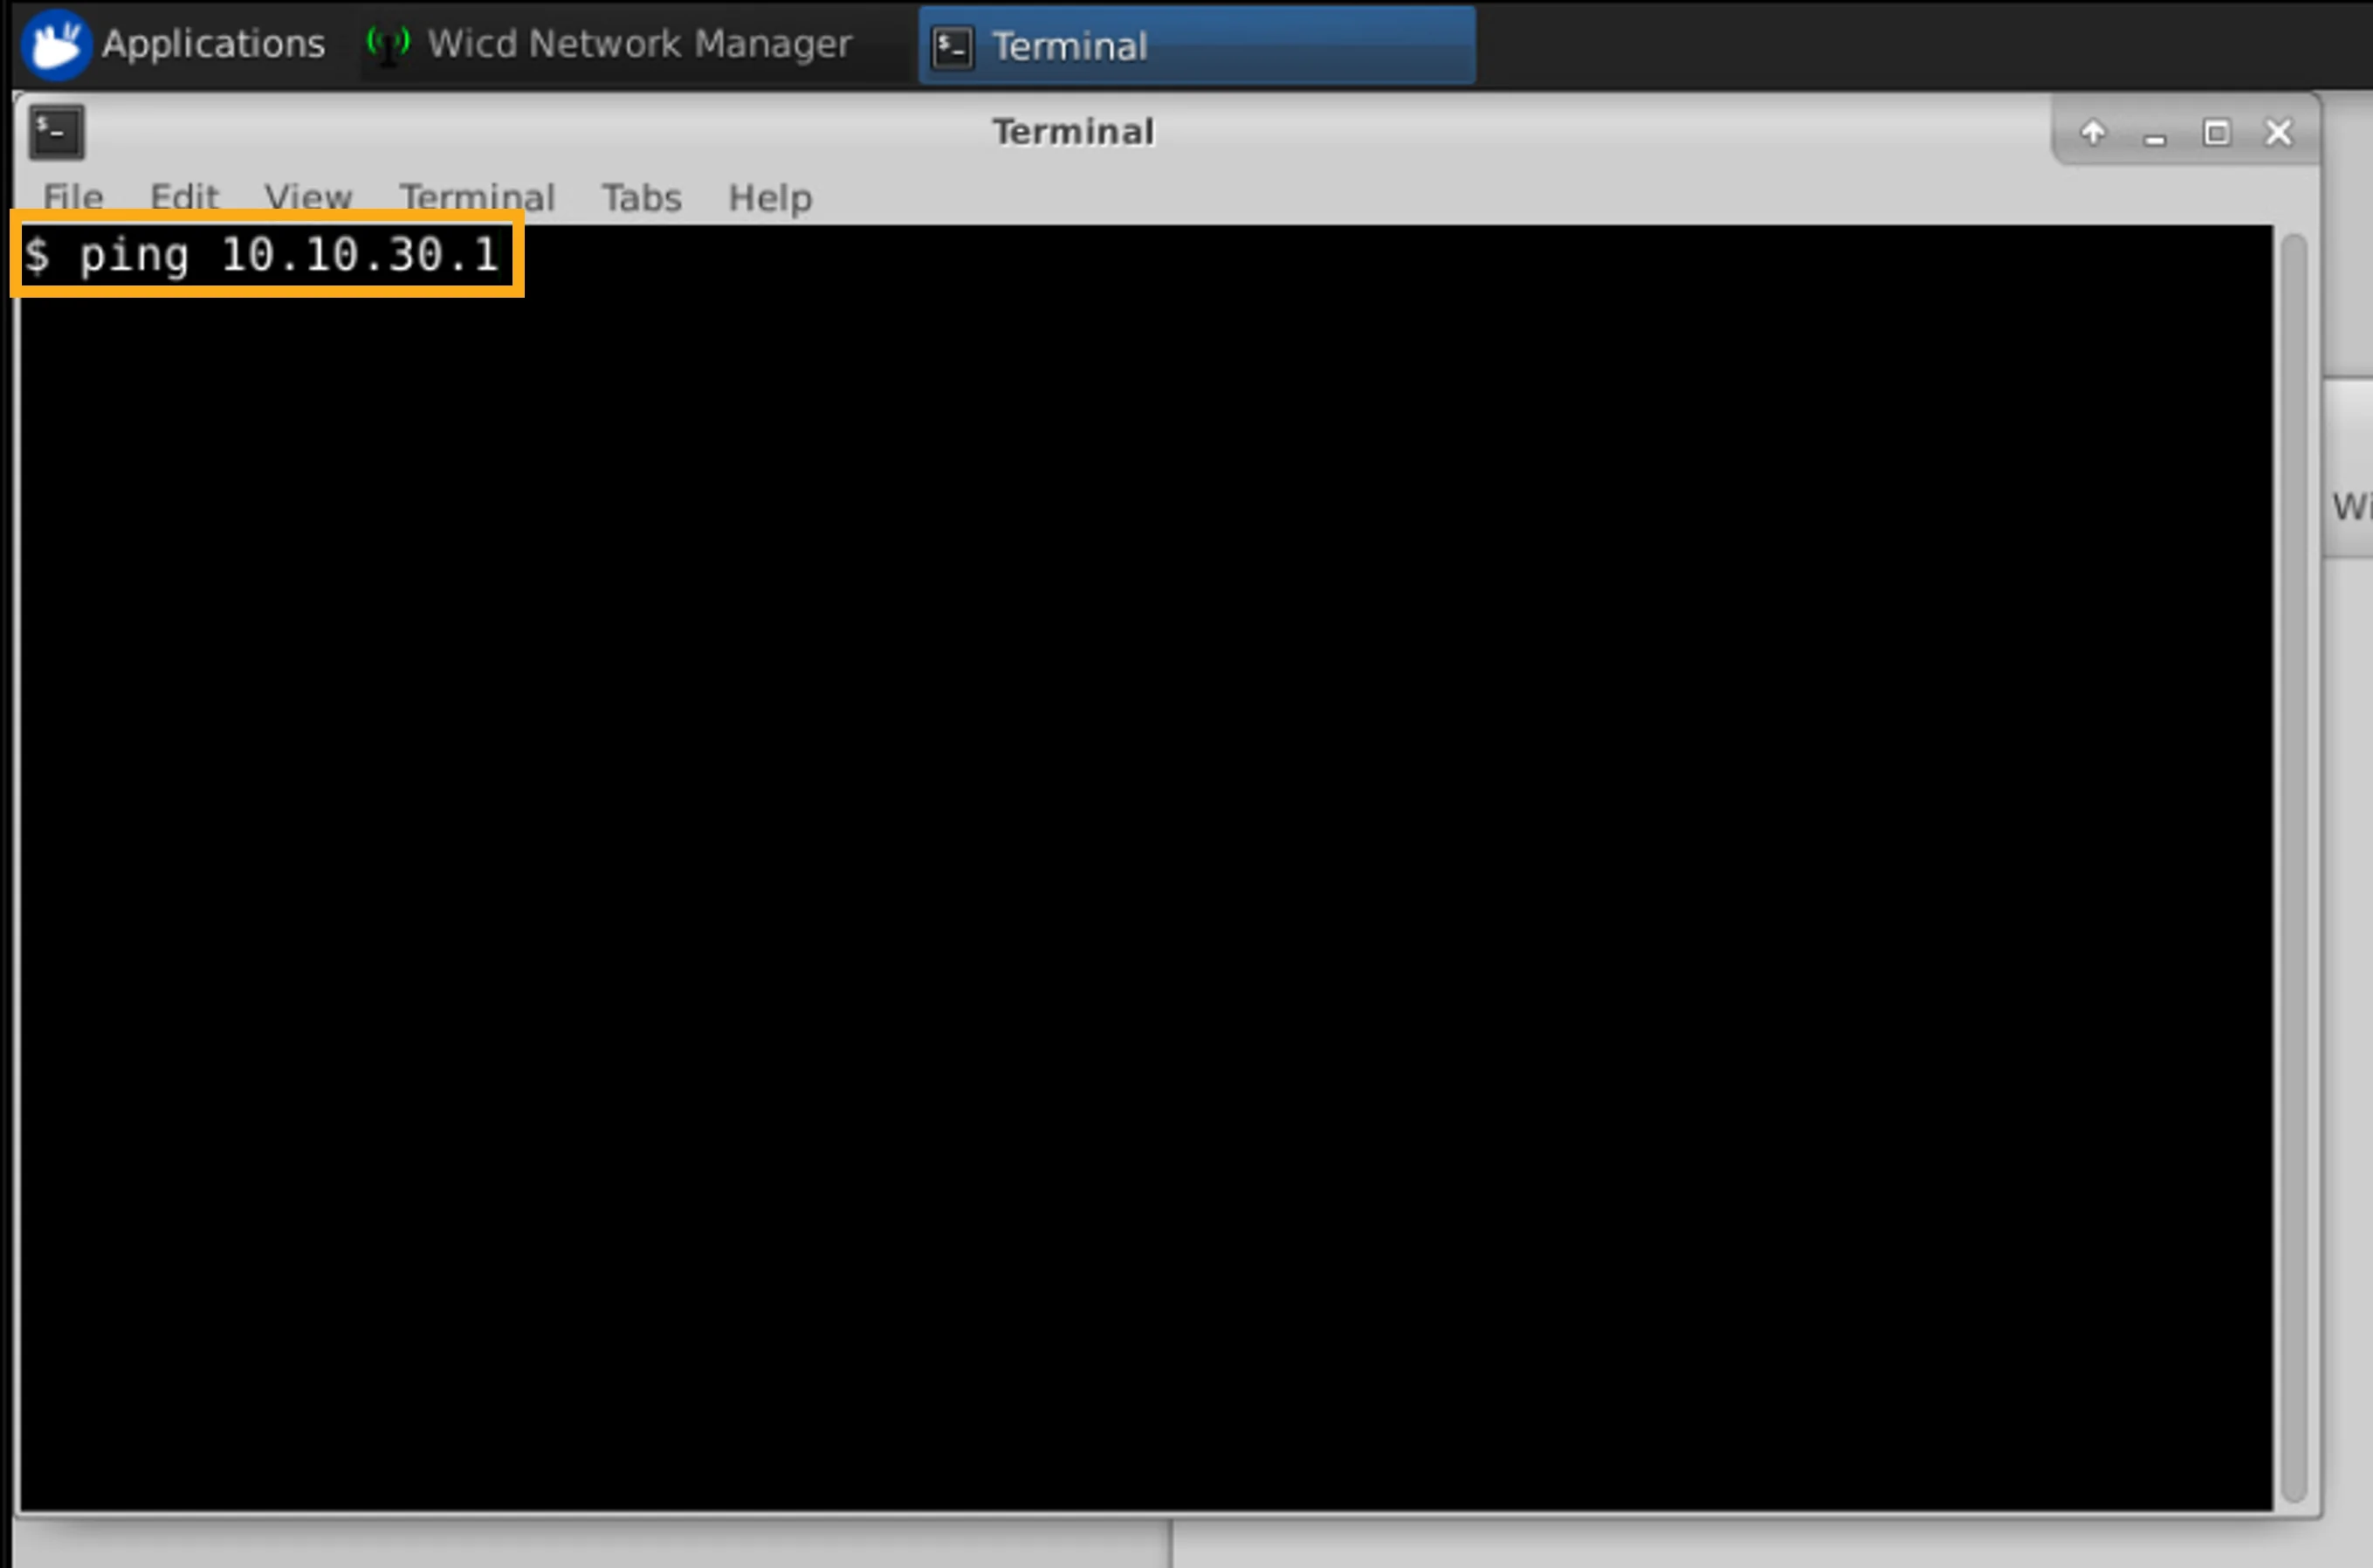
- Verify the result. The first ping timed out, but the following four pings were successful.驗證結果。第一次 ping 逾時,但接下來四次 ping 都成功。
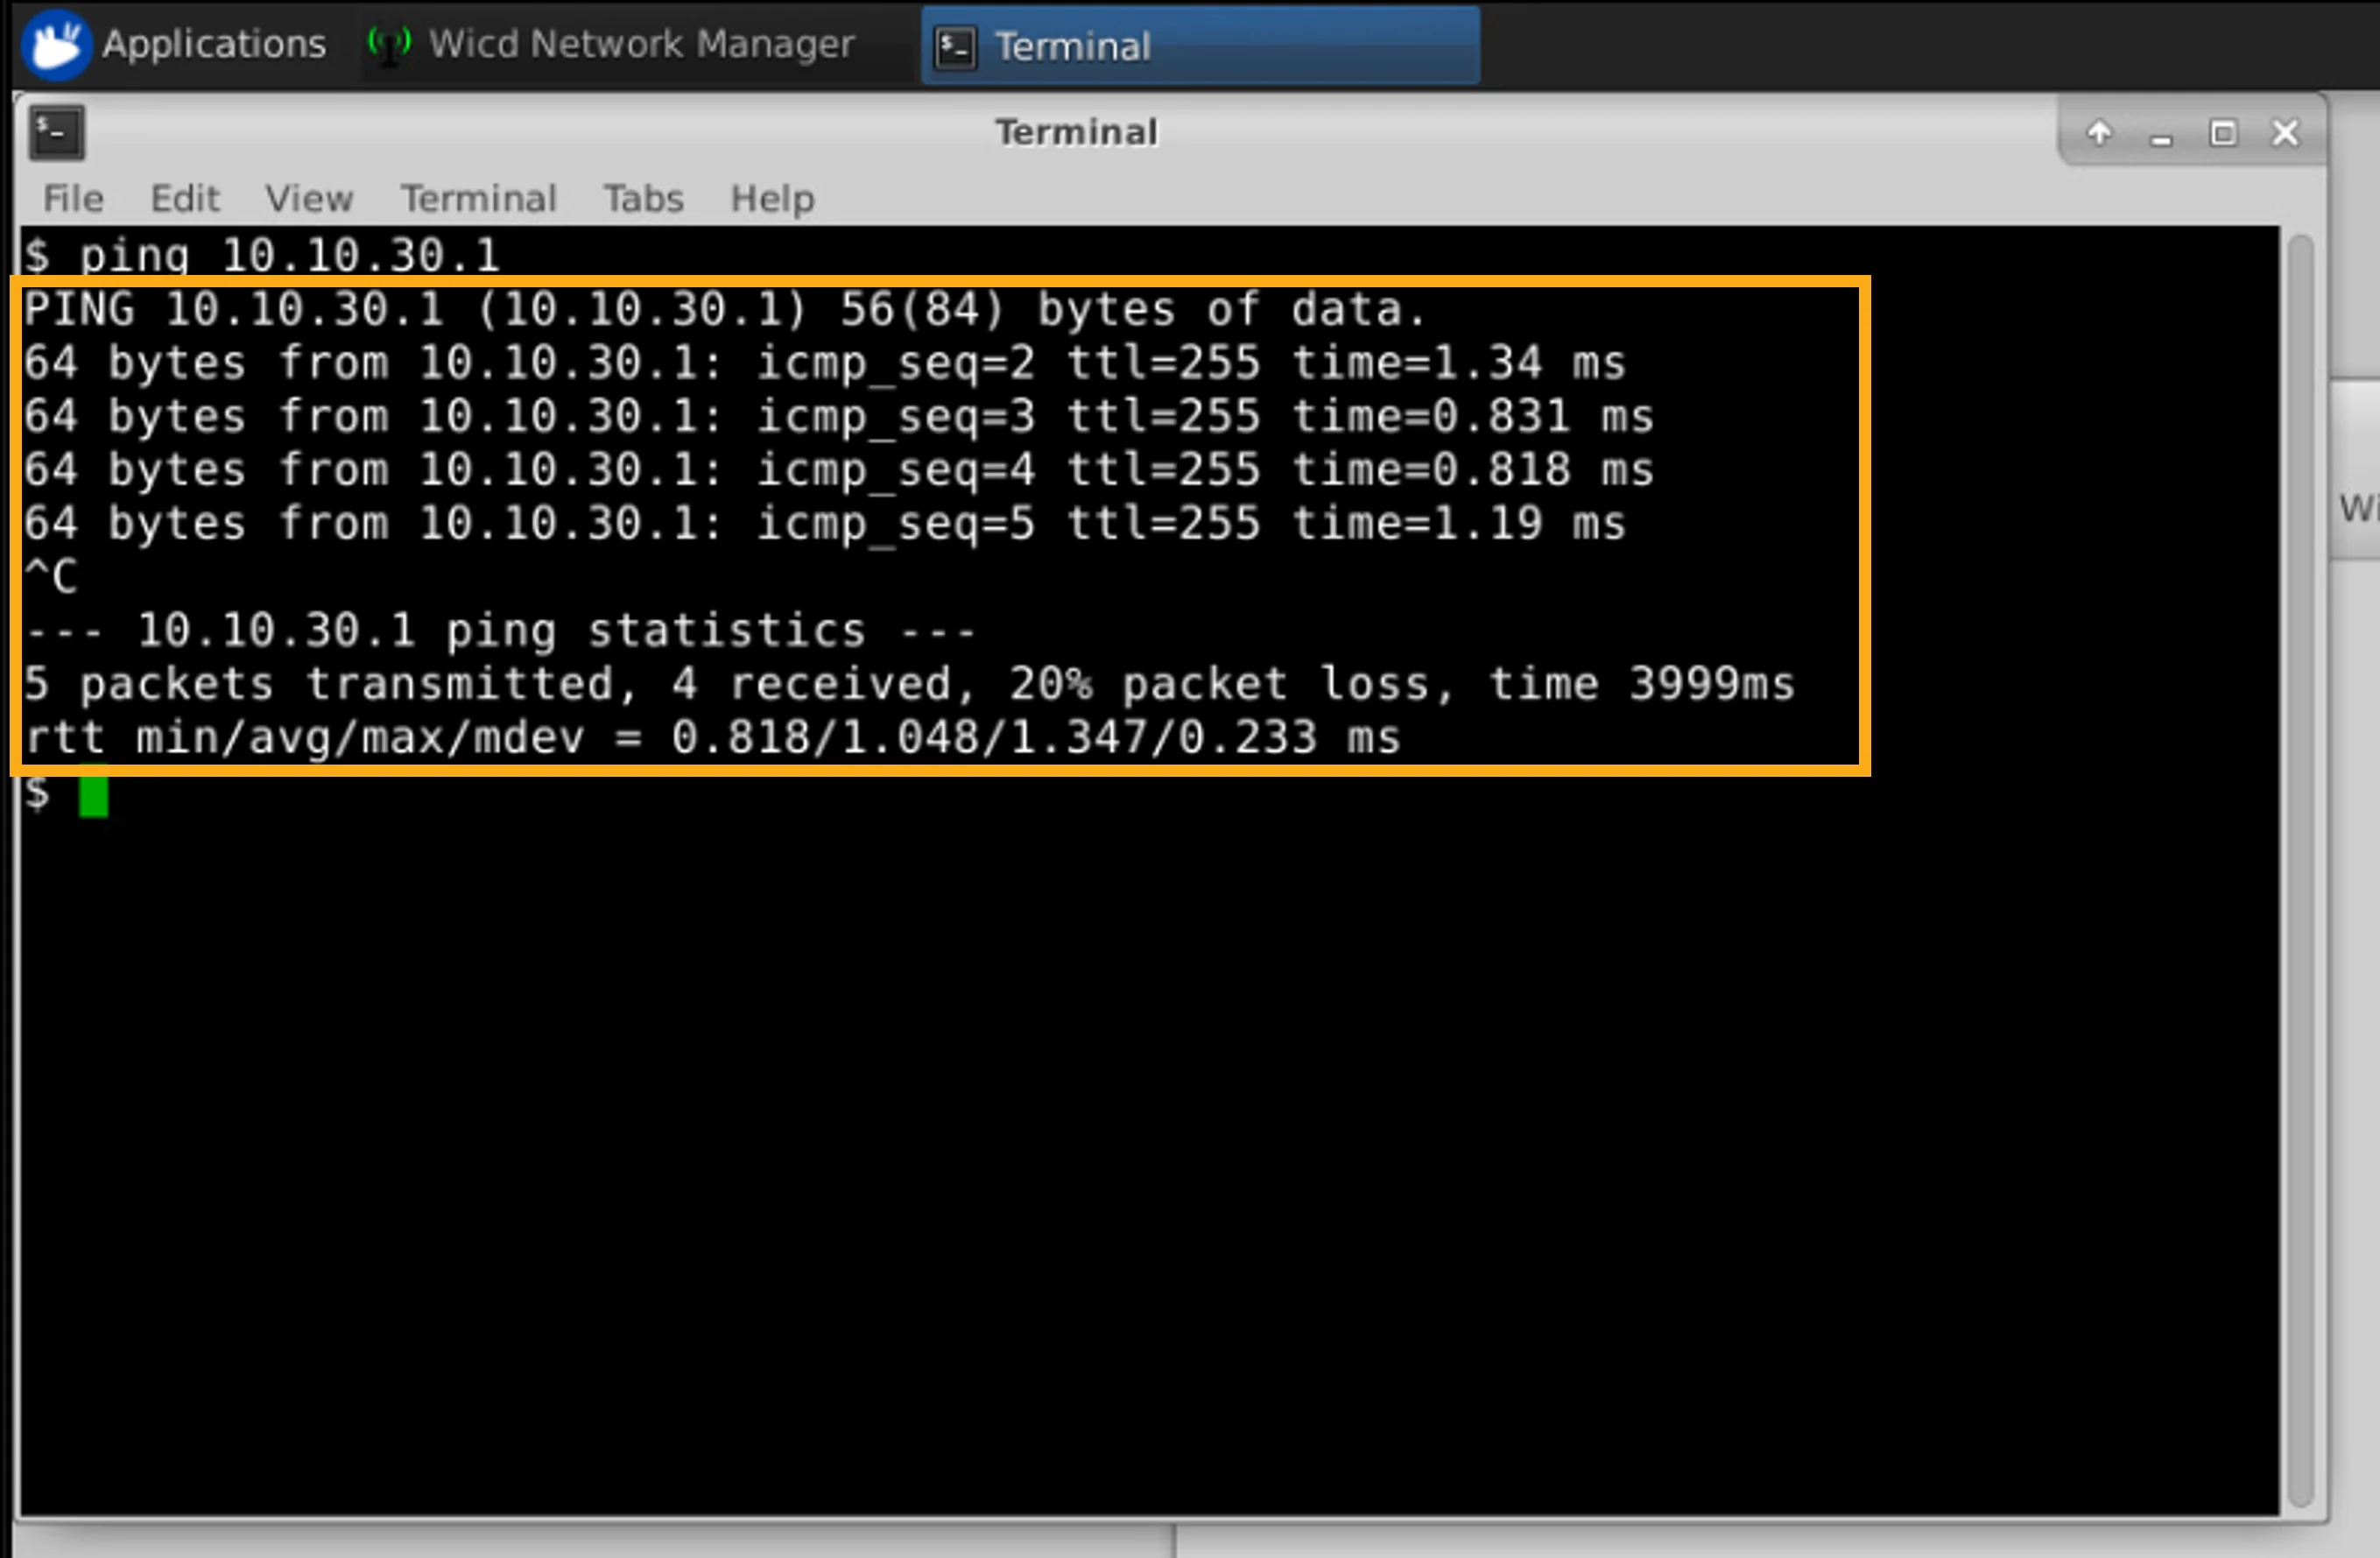
Now, let's verify the connectivity to Client PC 1 at 10.10.30.116.
現在,讓我們驗證與 Client PC 1(10.10.30.116)的連線。
You will see that all five pings were successful.
您將看到全部五次 ping 都成功。
Perform the following procedure:
請執行下列程序:
- In the terminal window, enter the
ping 10.10.30.116command and press Enter.在終端機視窗中,輸入ping 10.10.30.116命令並按 Enter。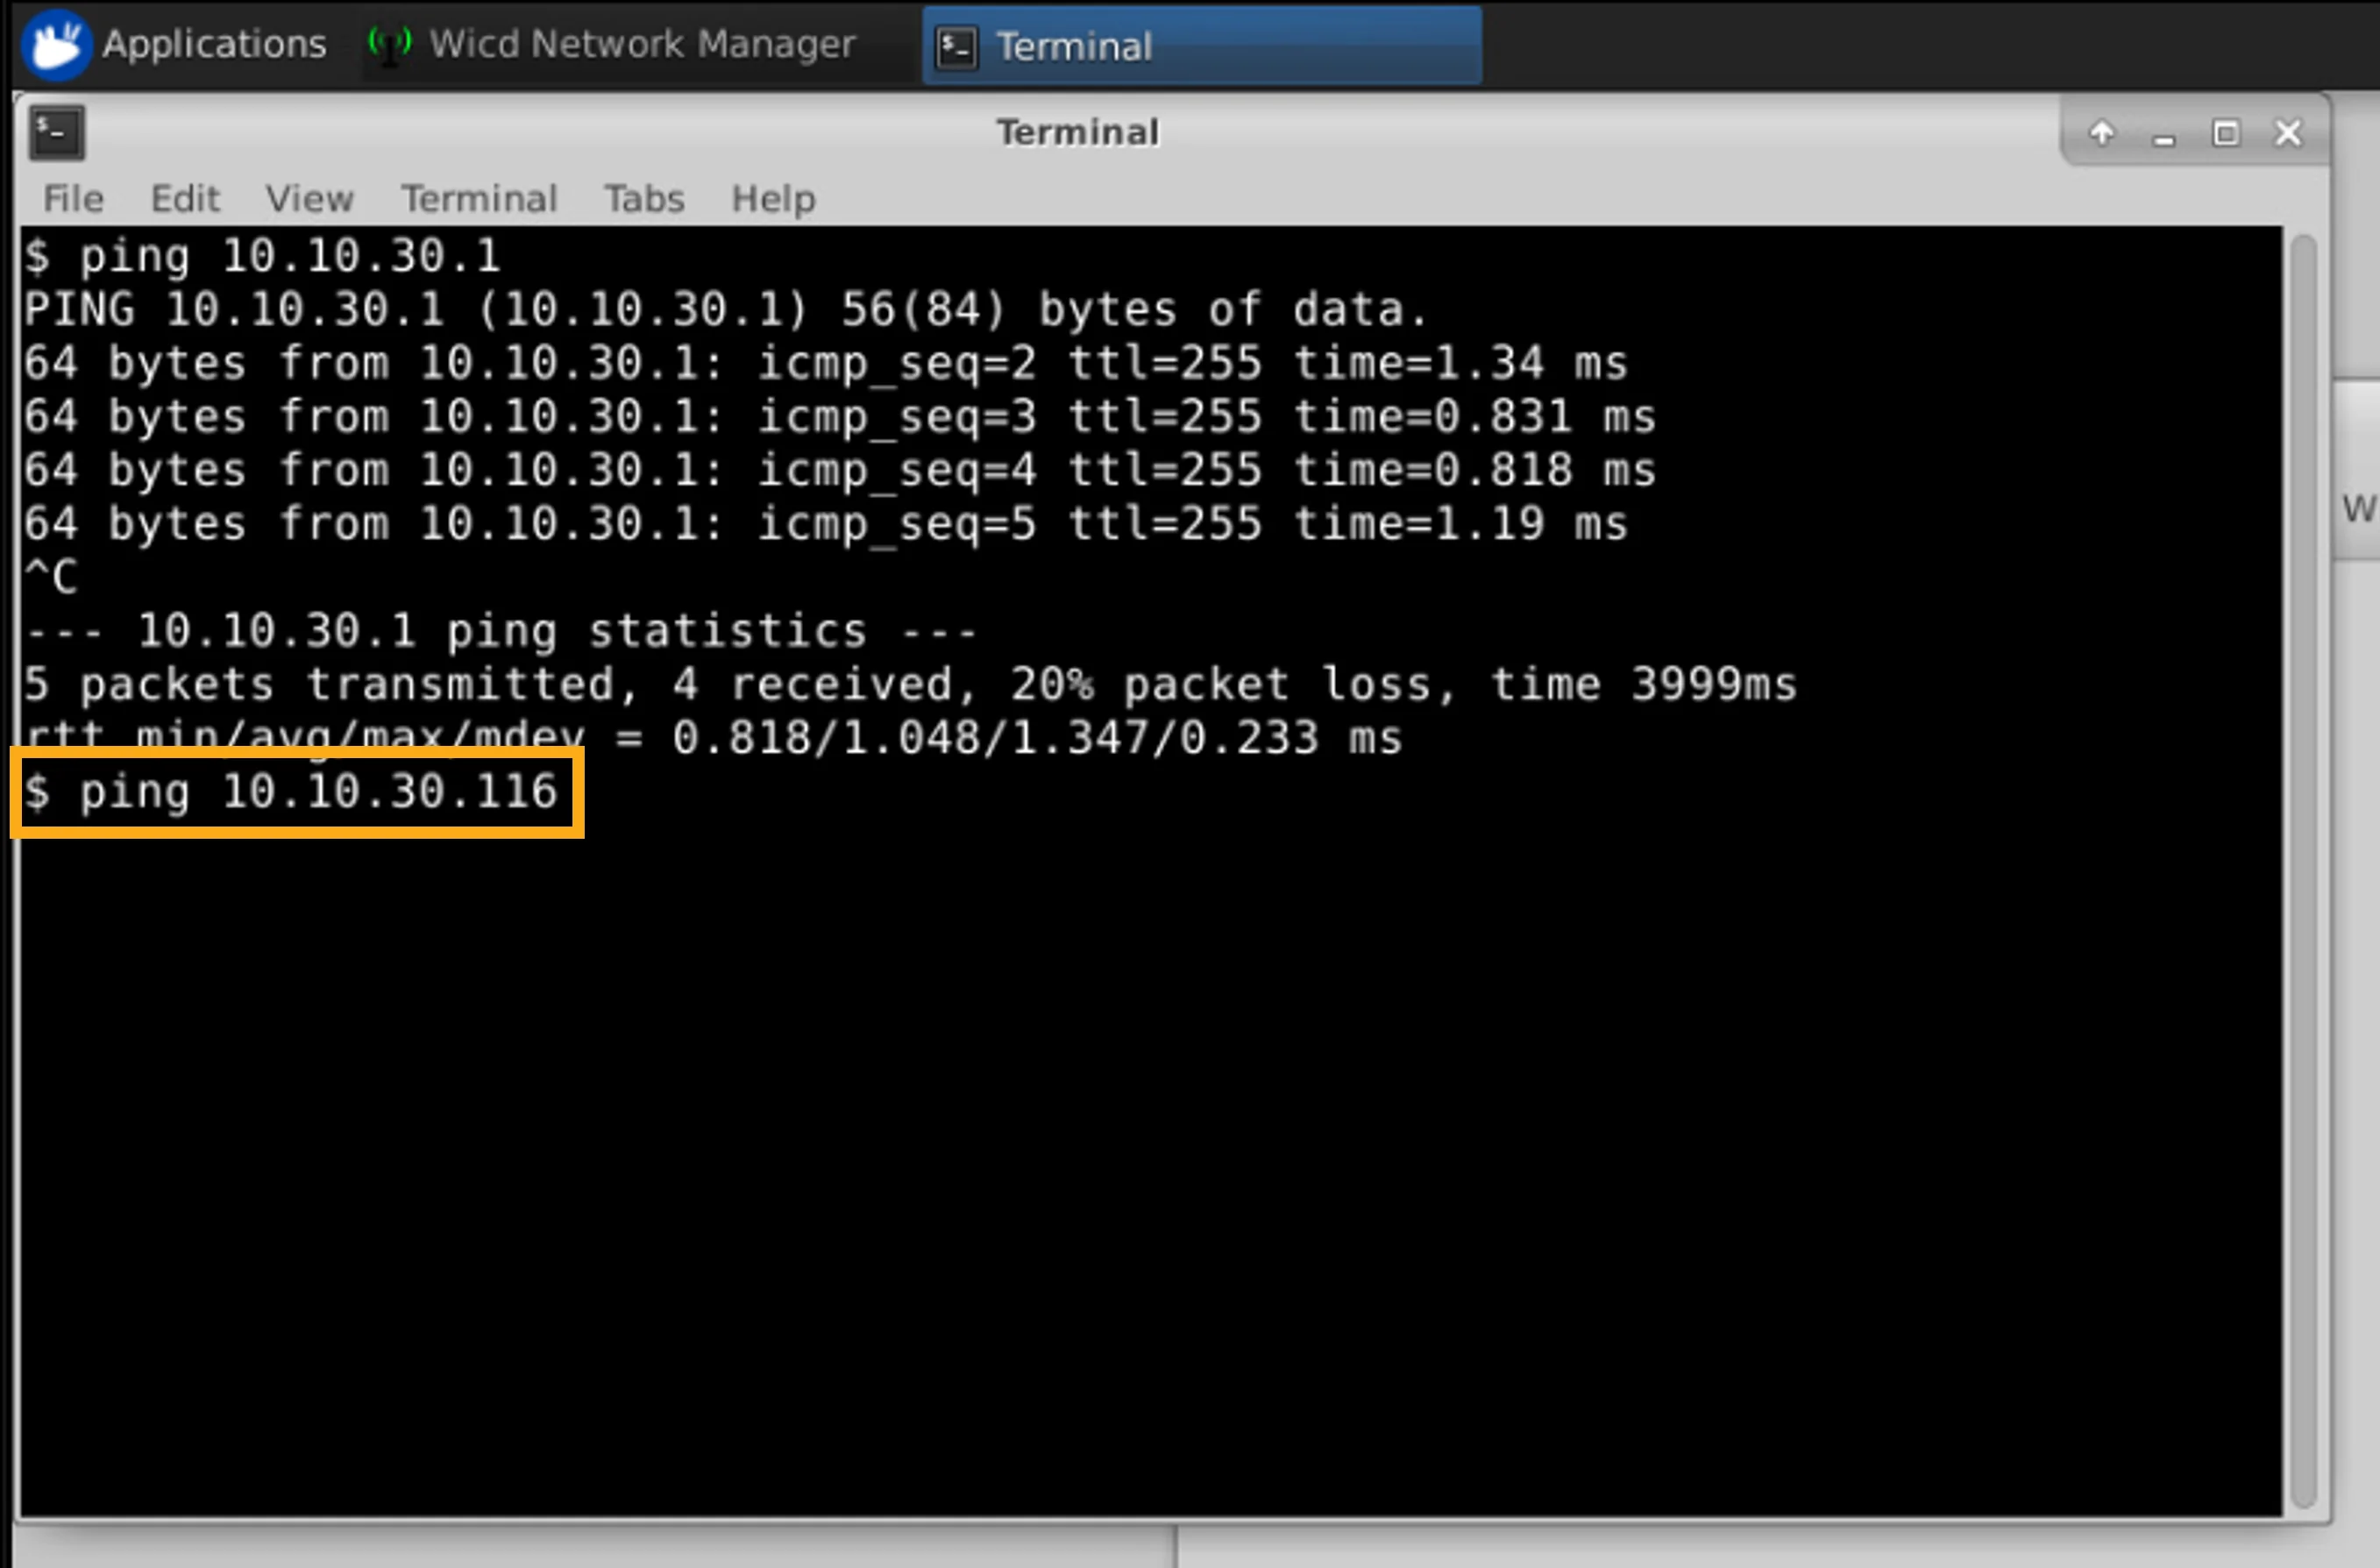
- Verify the result. All five pings were successful.驗證結果。全部五次 ping 都成功。
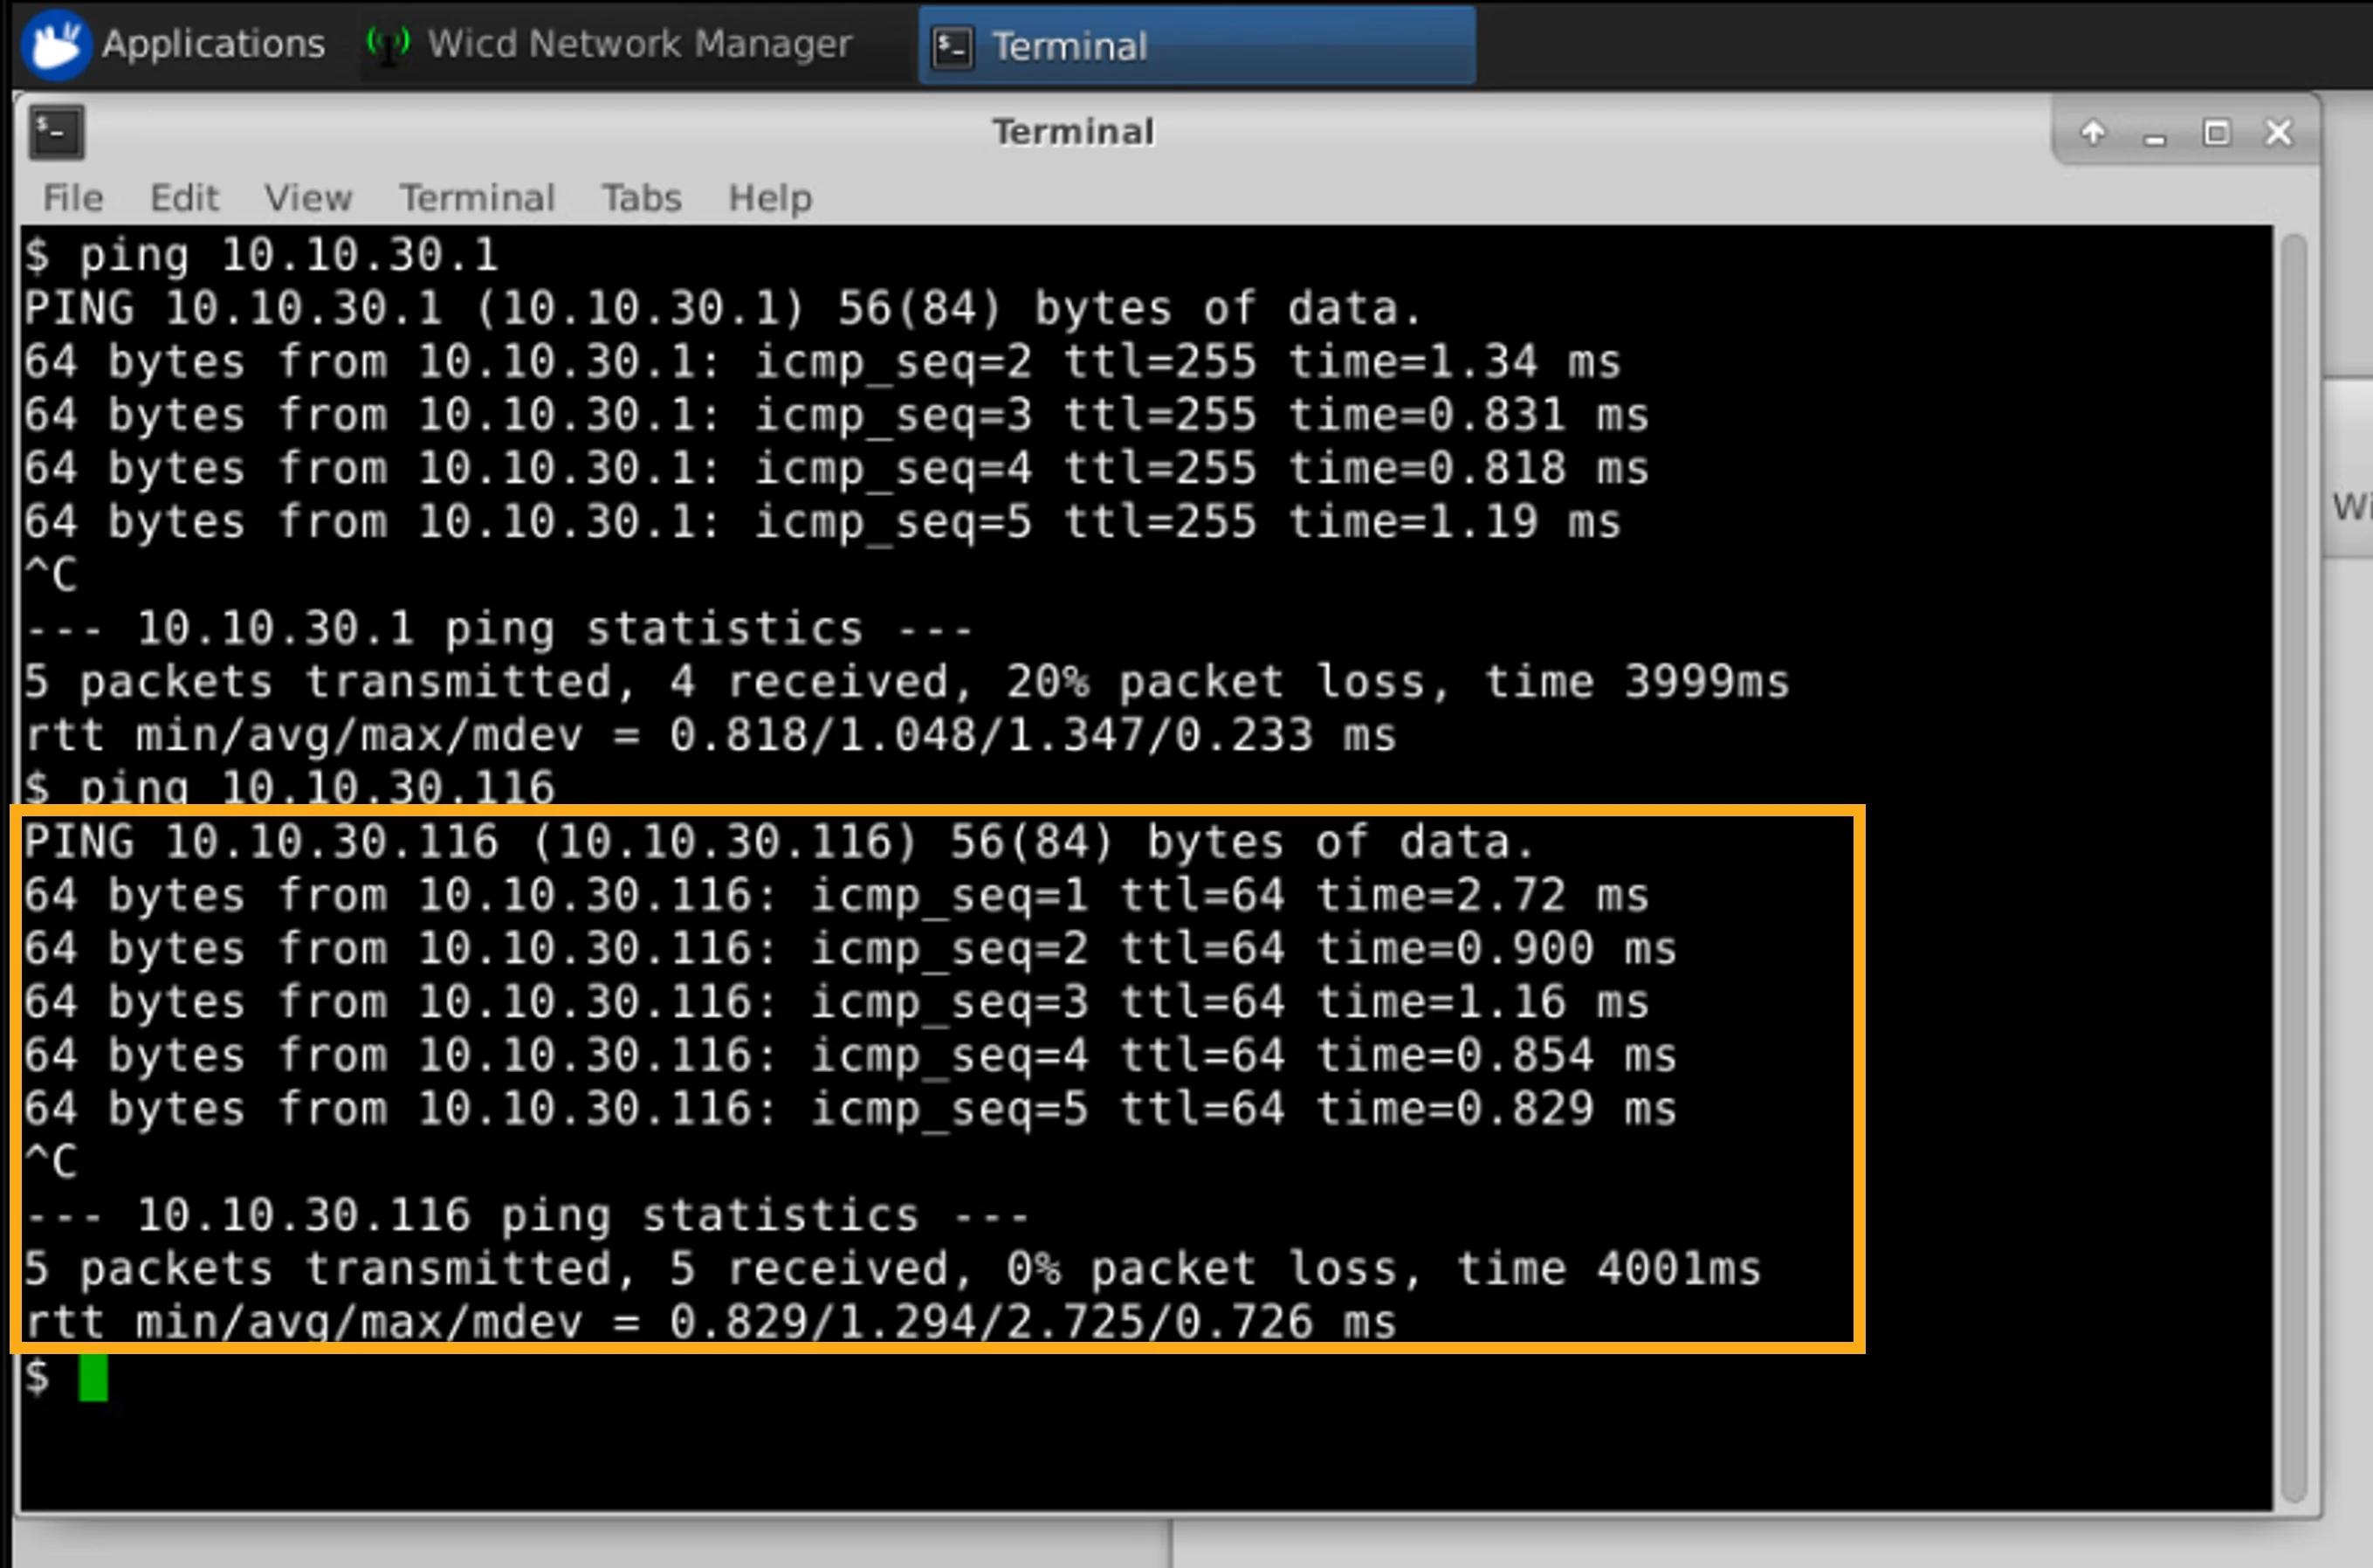
View Client Details on the Campus WLC
在 Campus WLC 上檢視用戶端詳細資料
You will now examine more details about the wireless clients that are connected to the WLAN.
您現在將檢視連線至此 WLAN 的無線用戶端更多詳細資料。
Click the Switch to Admin PC button, which is located at the bottom-right corner of the desktop to switch from Client PC 2 to the Admin PC.
按一下位於桌面右下角的 Switch to Admin PC 按鈕,從 Client PC 2 切換至 Admin PC。
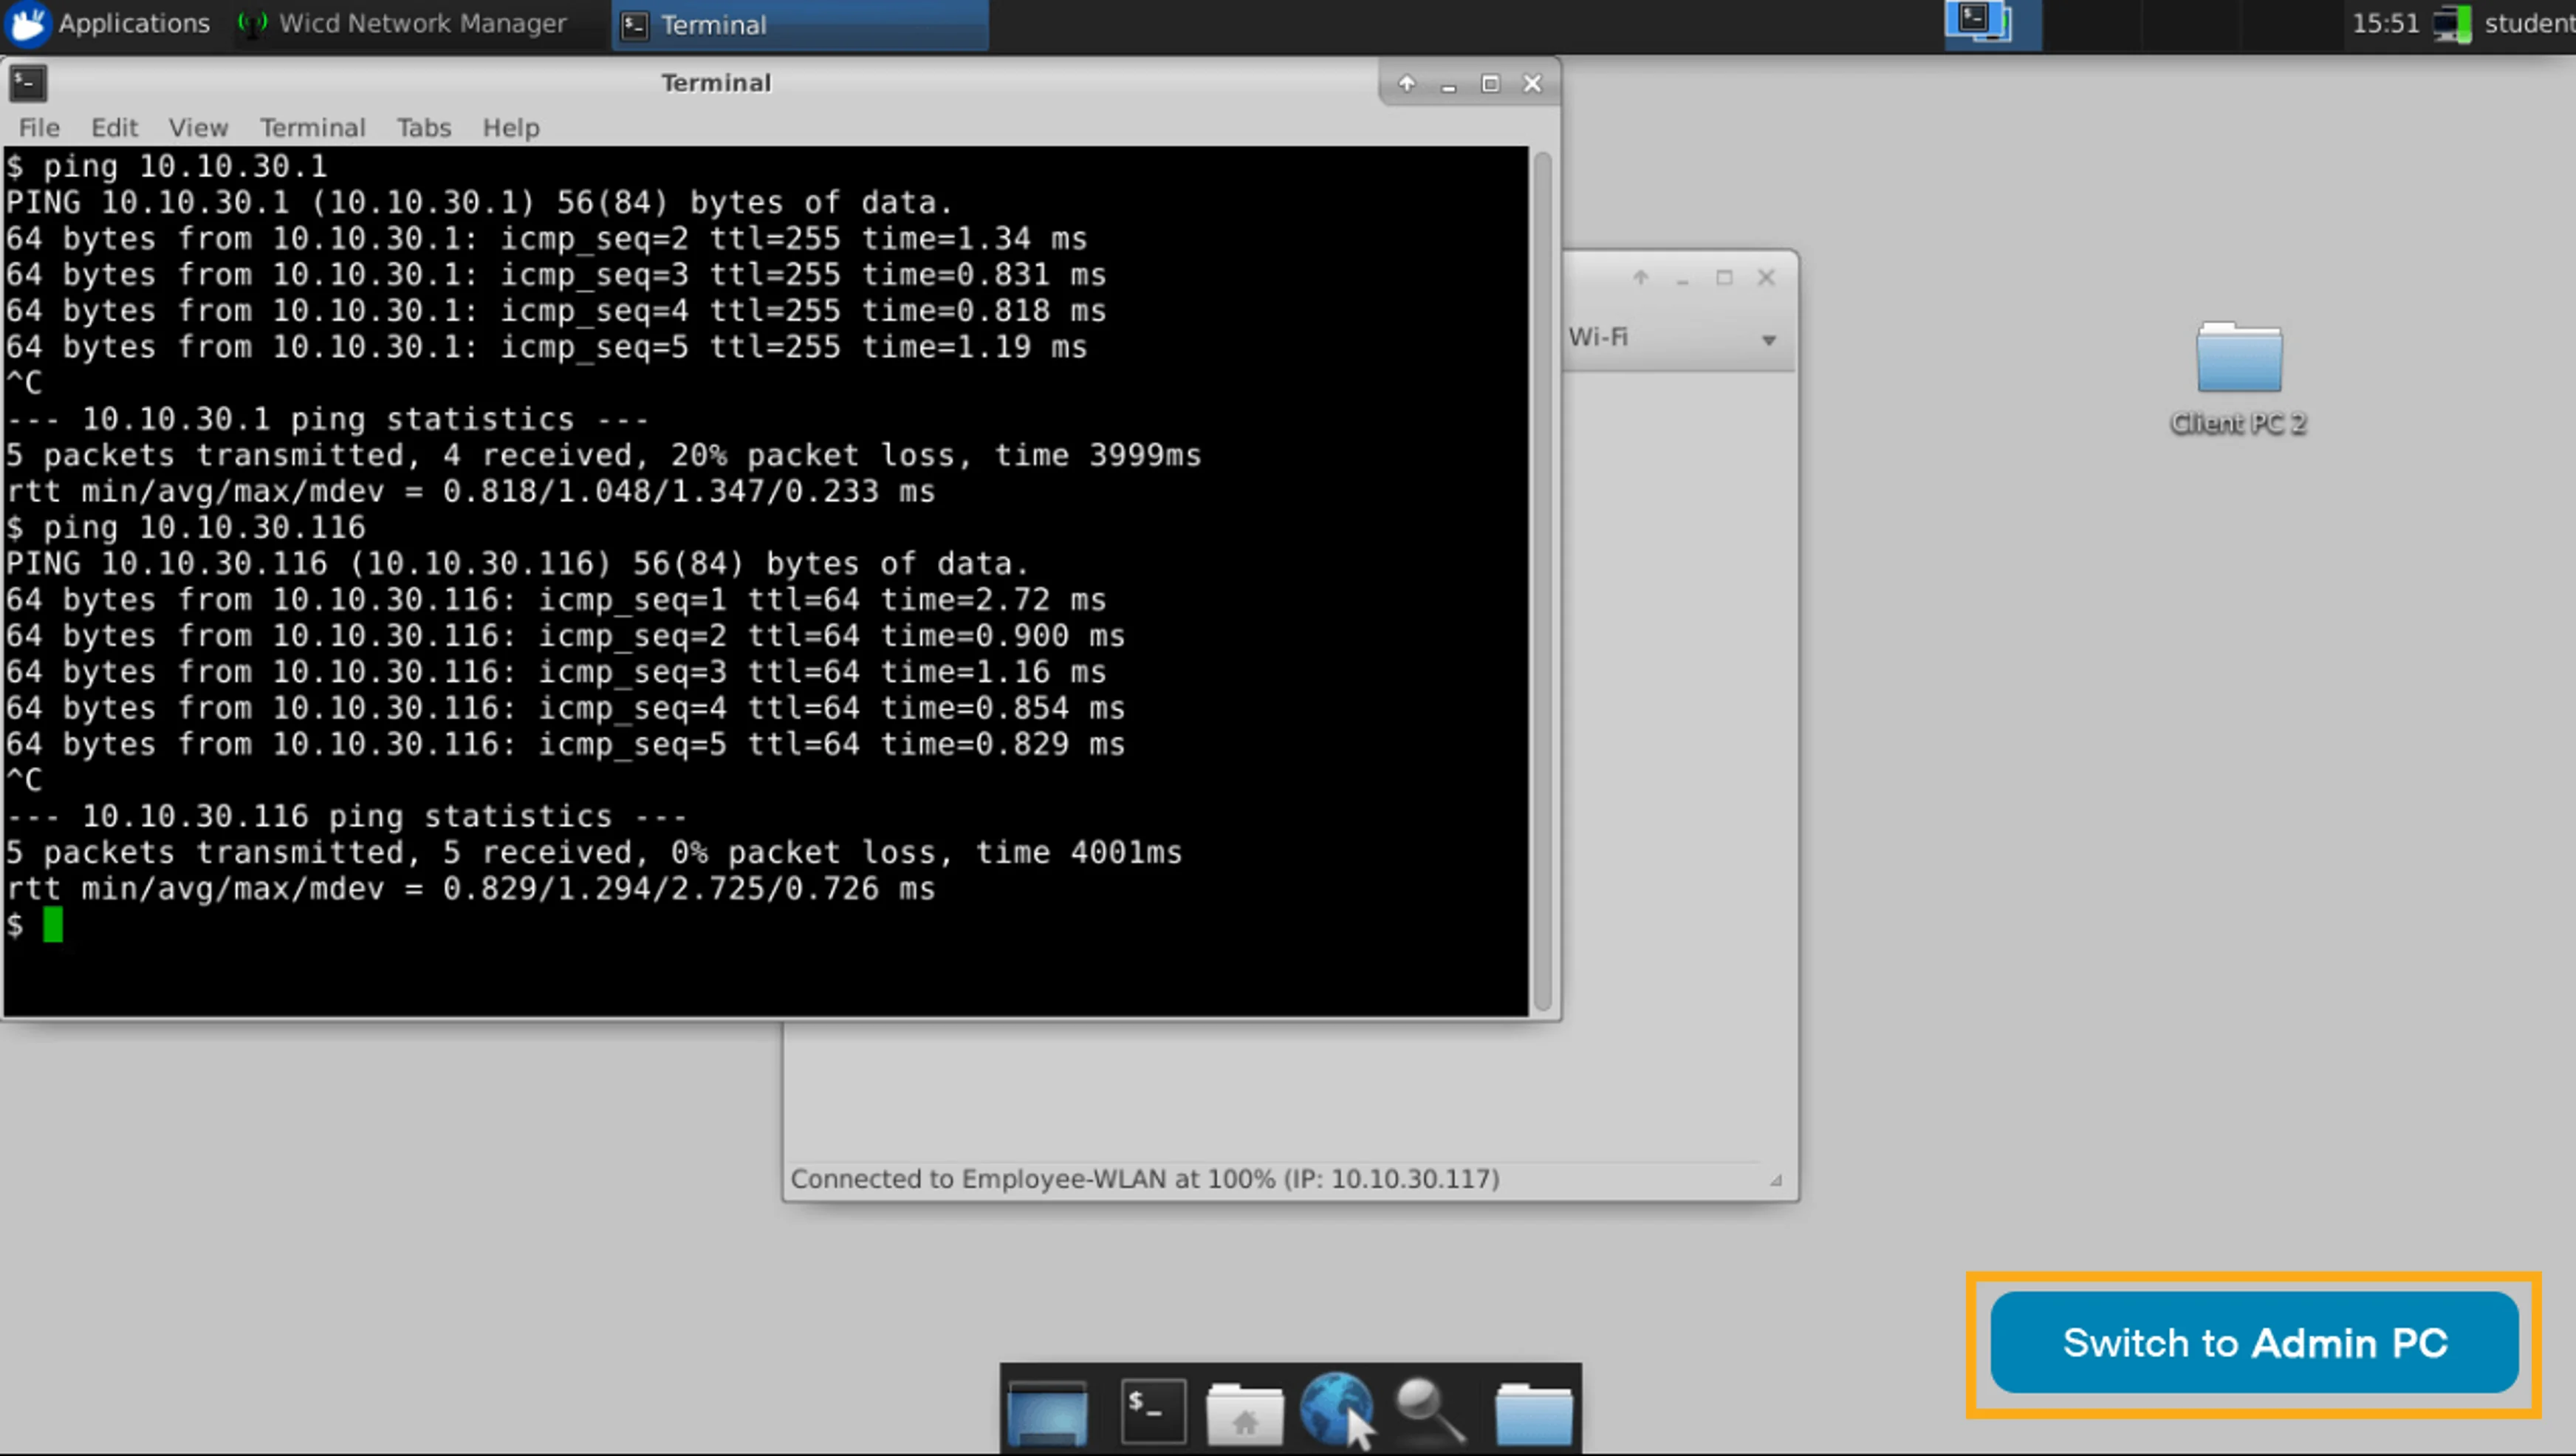
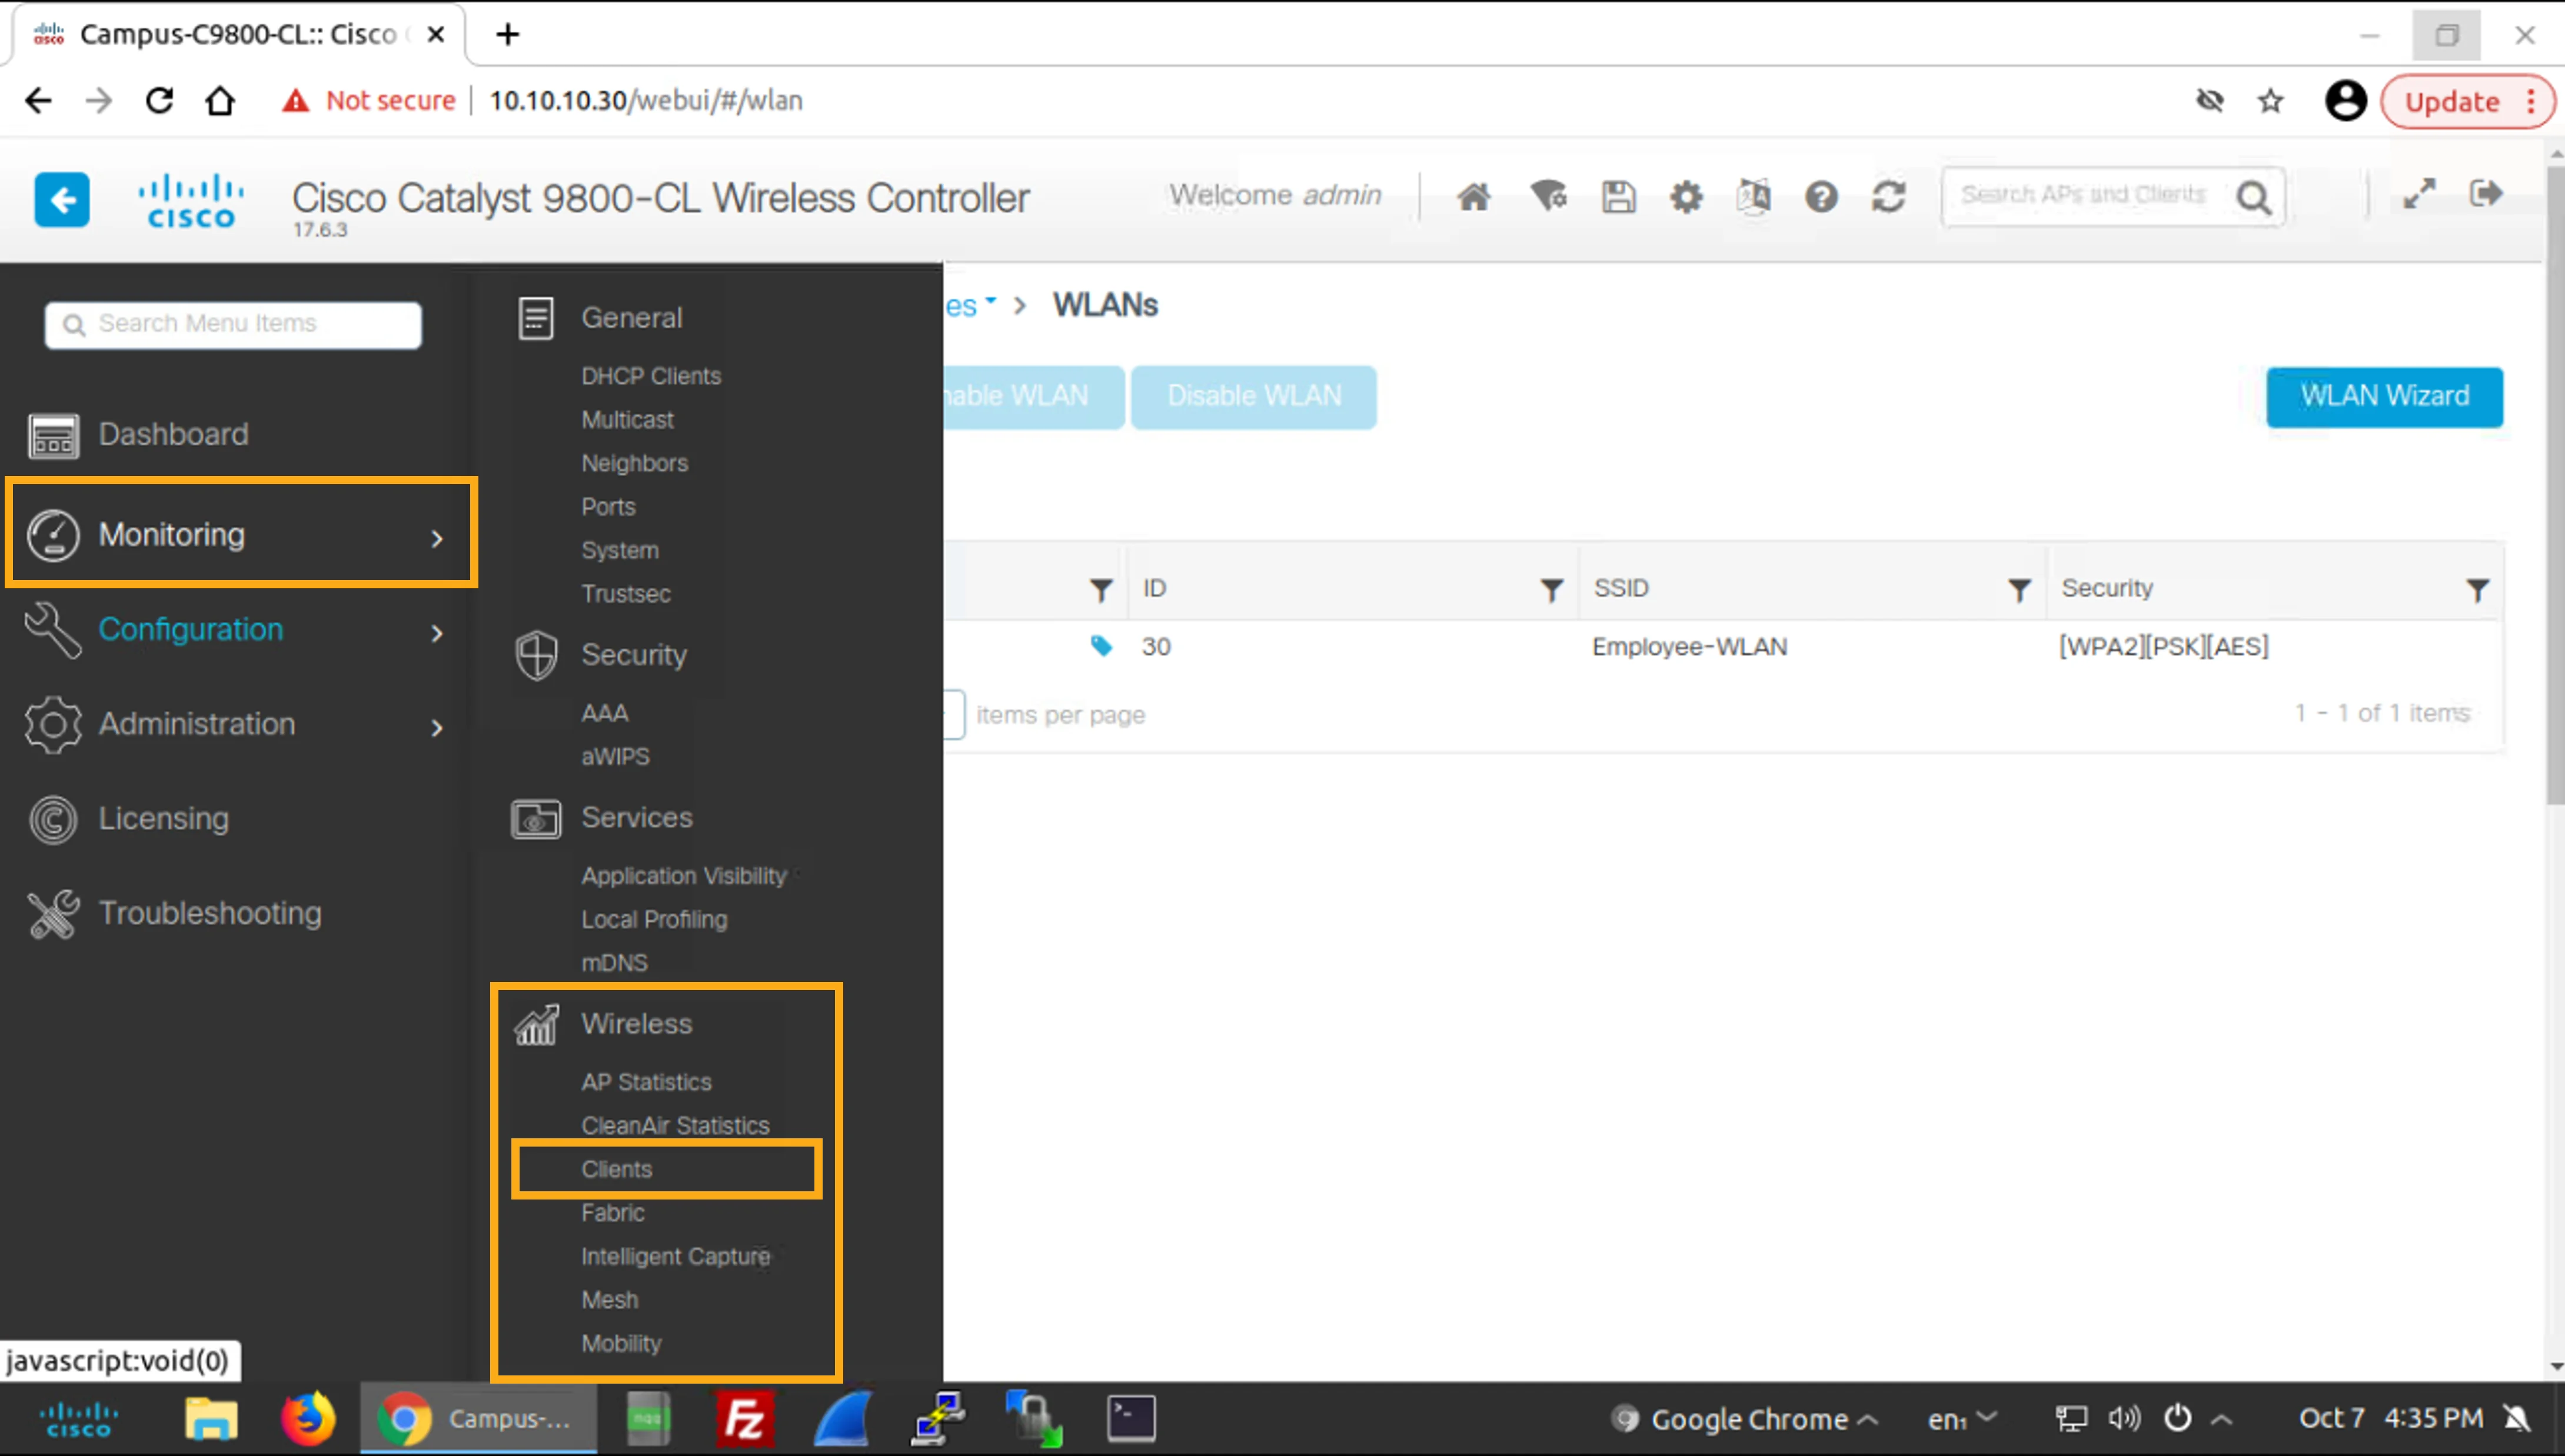
Choose Monitoring > Wireless > Clients.
選擇 Monitoring > Wireless > Clients。
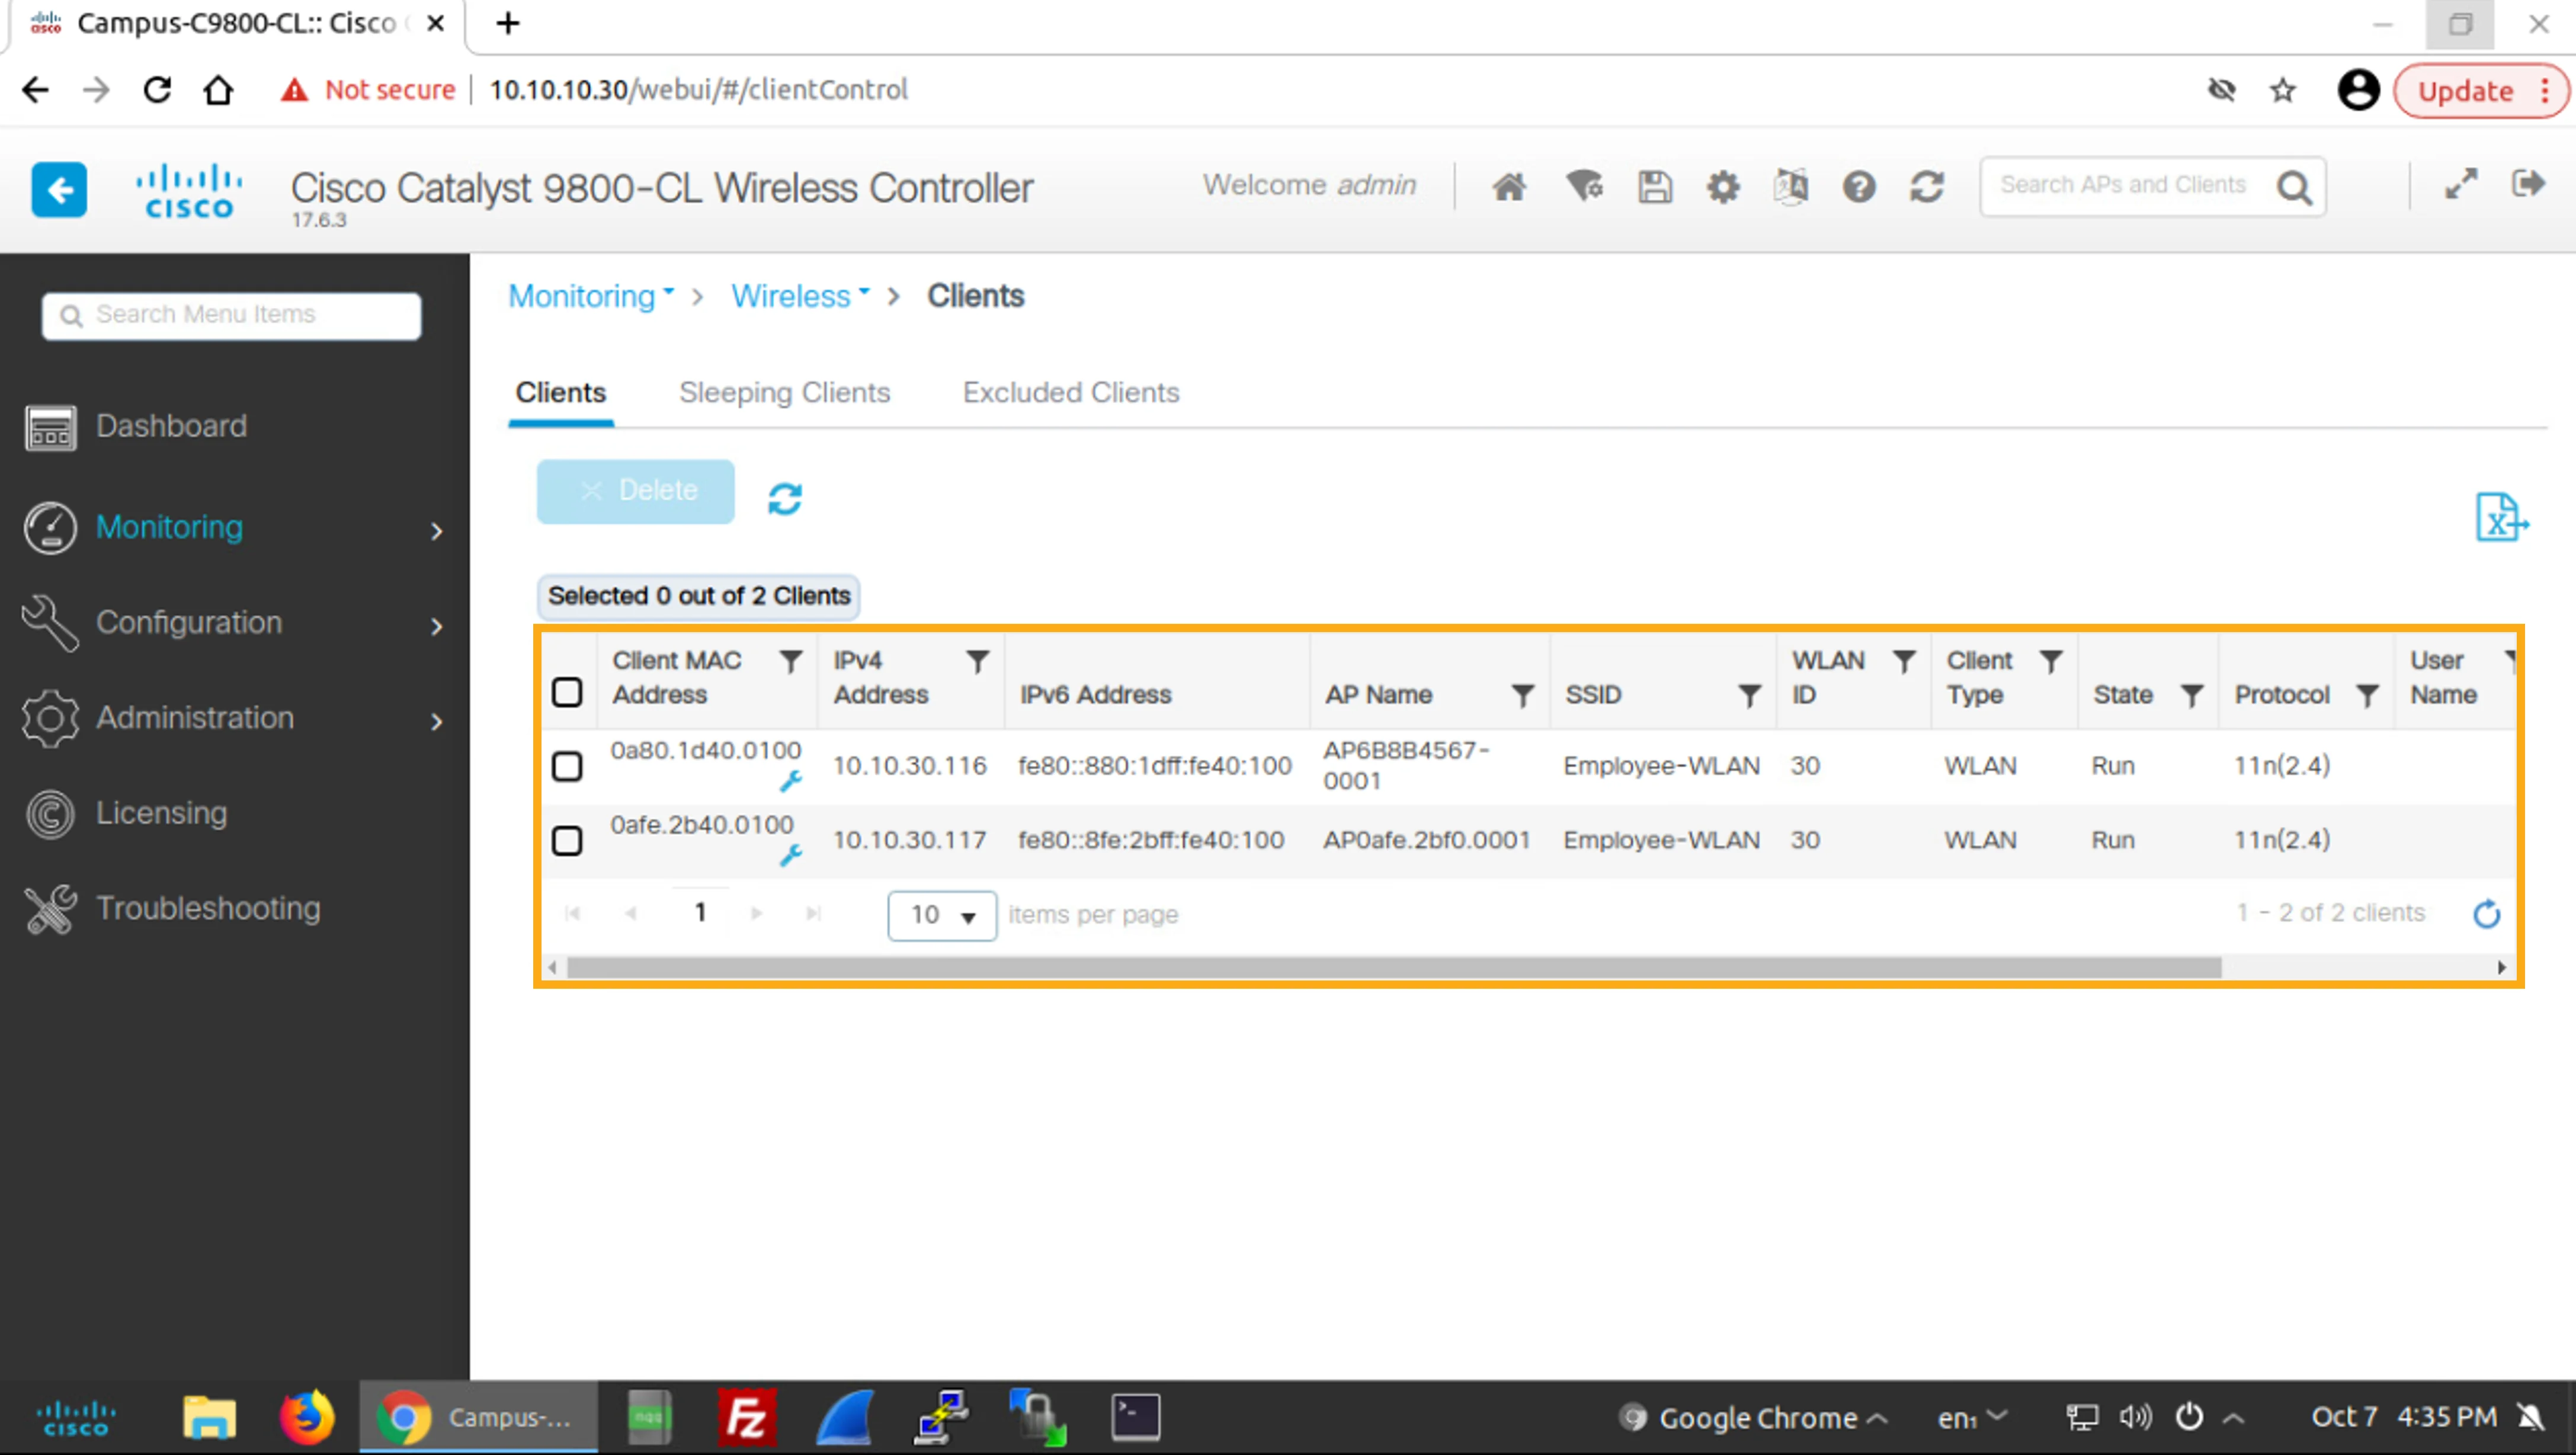
Verify that you can see the two connected WLAN clients, including their MAC address and client IP address.
驗證您可以看到兩個已連線的 WLAN 用戶端,包括其 MAC 位址及用戶端 IP 位址。
You can also see the name of the AP to which the clients are connected, their SSID, and the WLAN ID.
您也可以看到用戶端所連線的 AP 名稱、其 SSID,以及 WLAN ID。
Client Security Information
用戶端安全性資訊
Let's see what security information about the connected clients the Campus WLC provides.
讓我們看看 Campus WLC 提供了哪些已連線用戶端的安全性資訊。
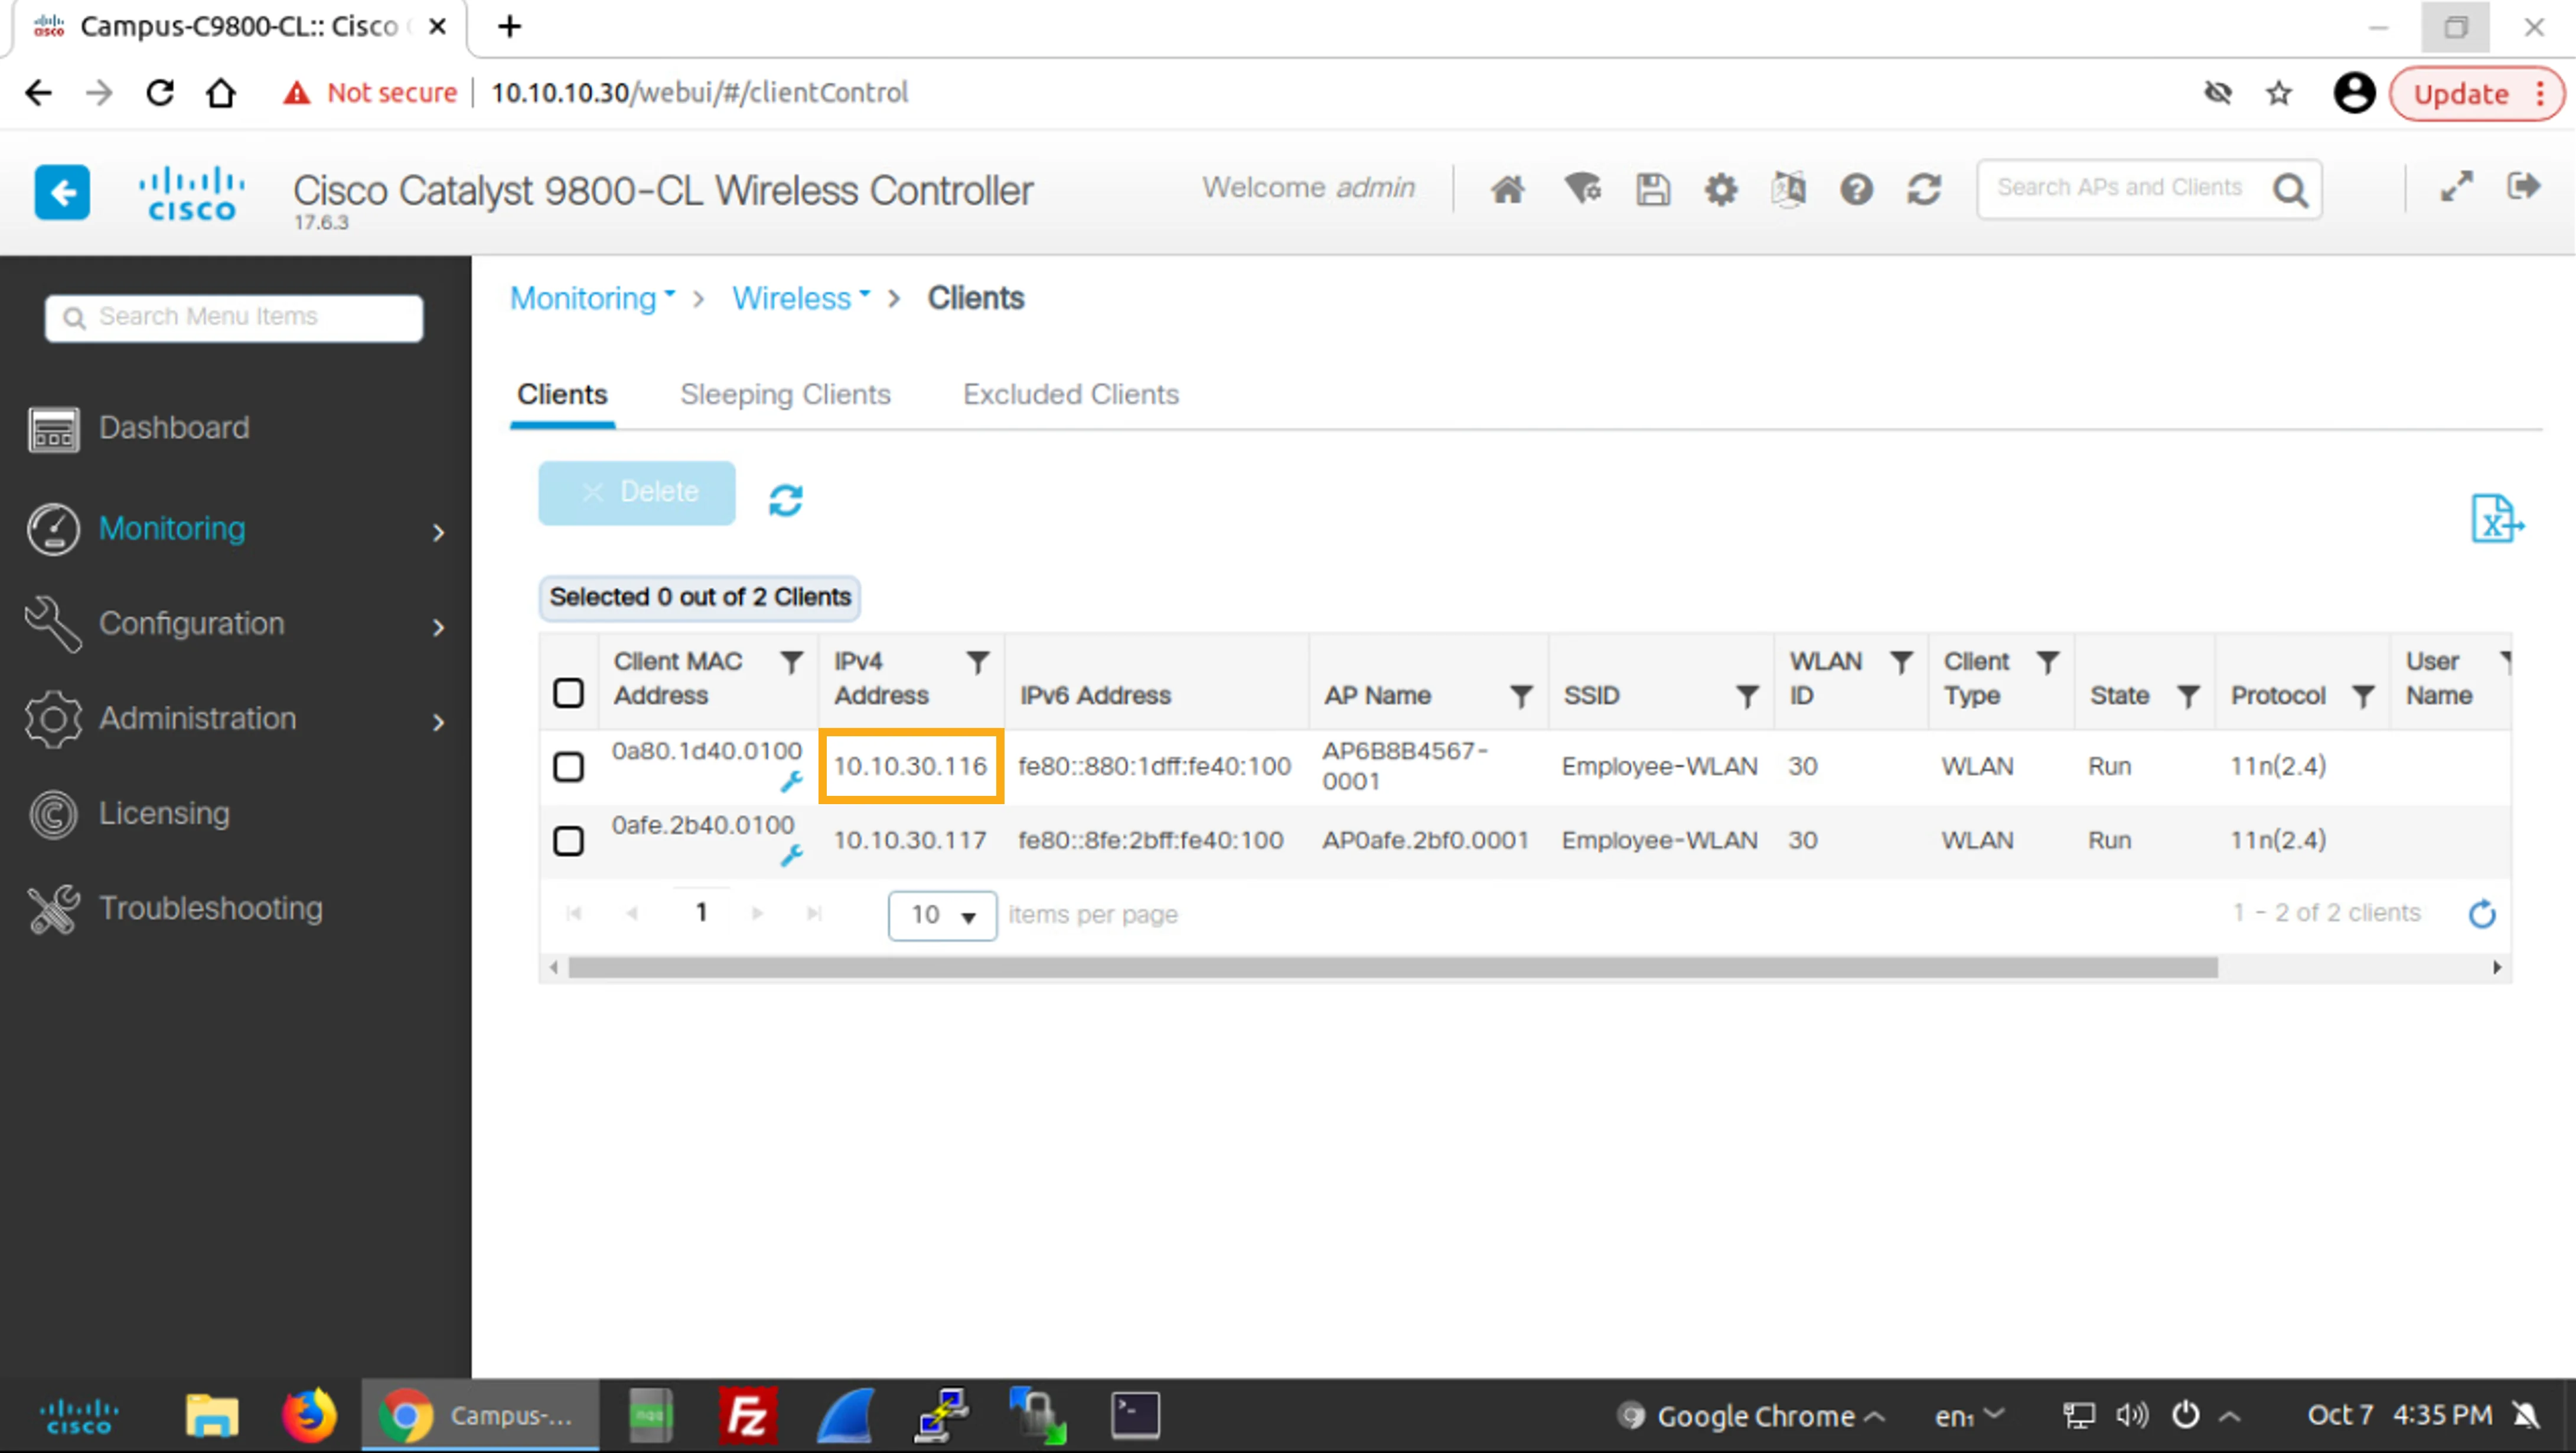
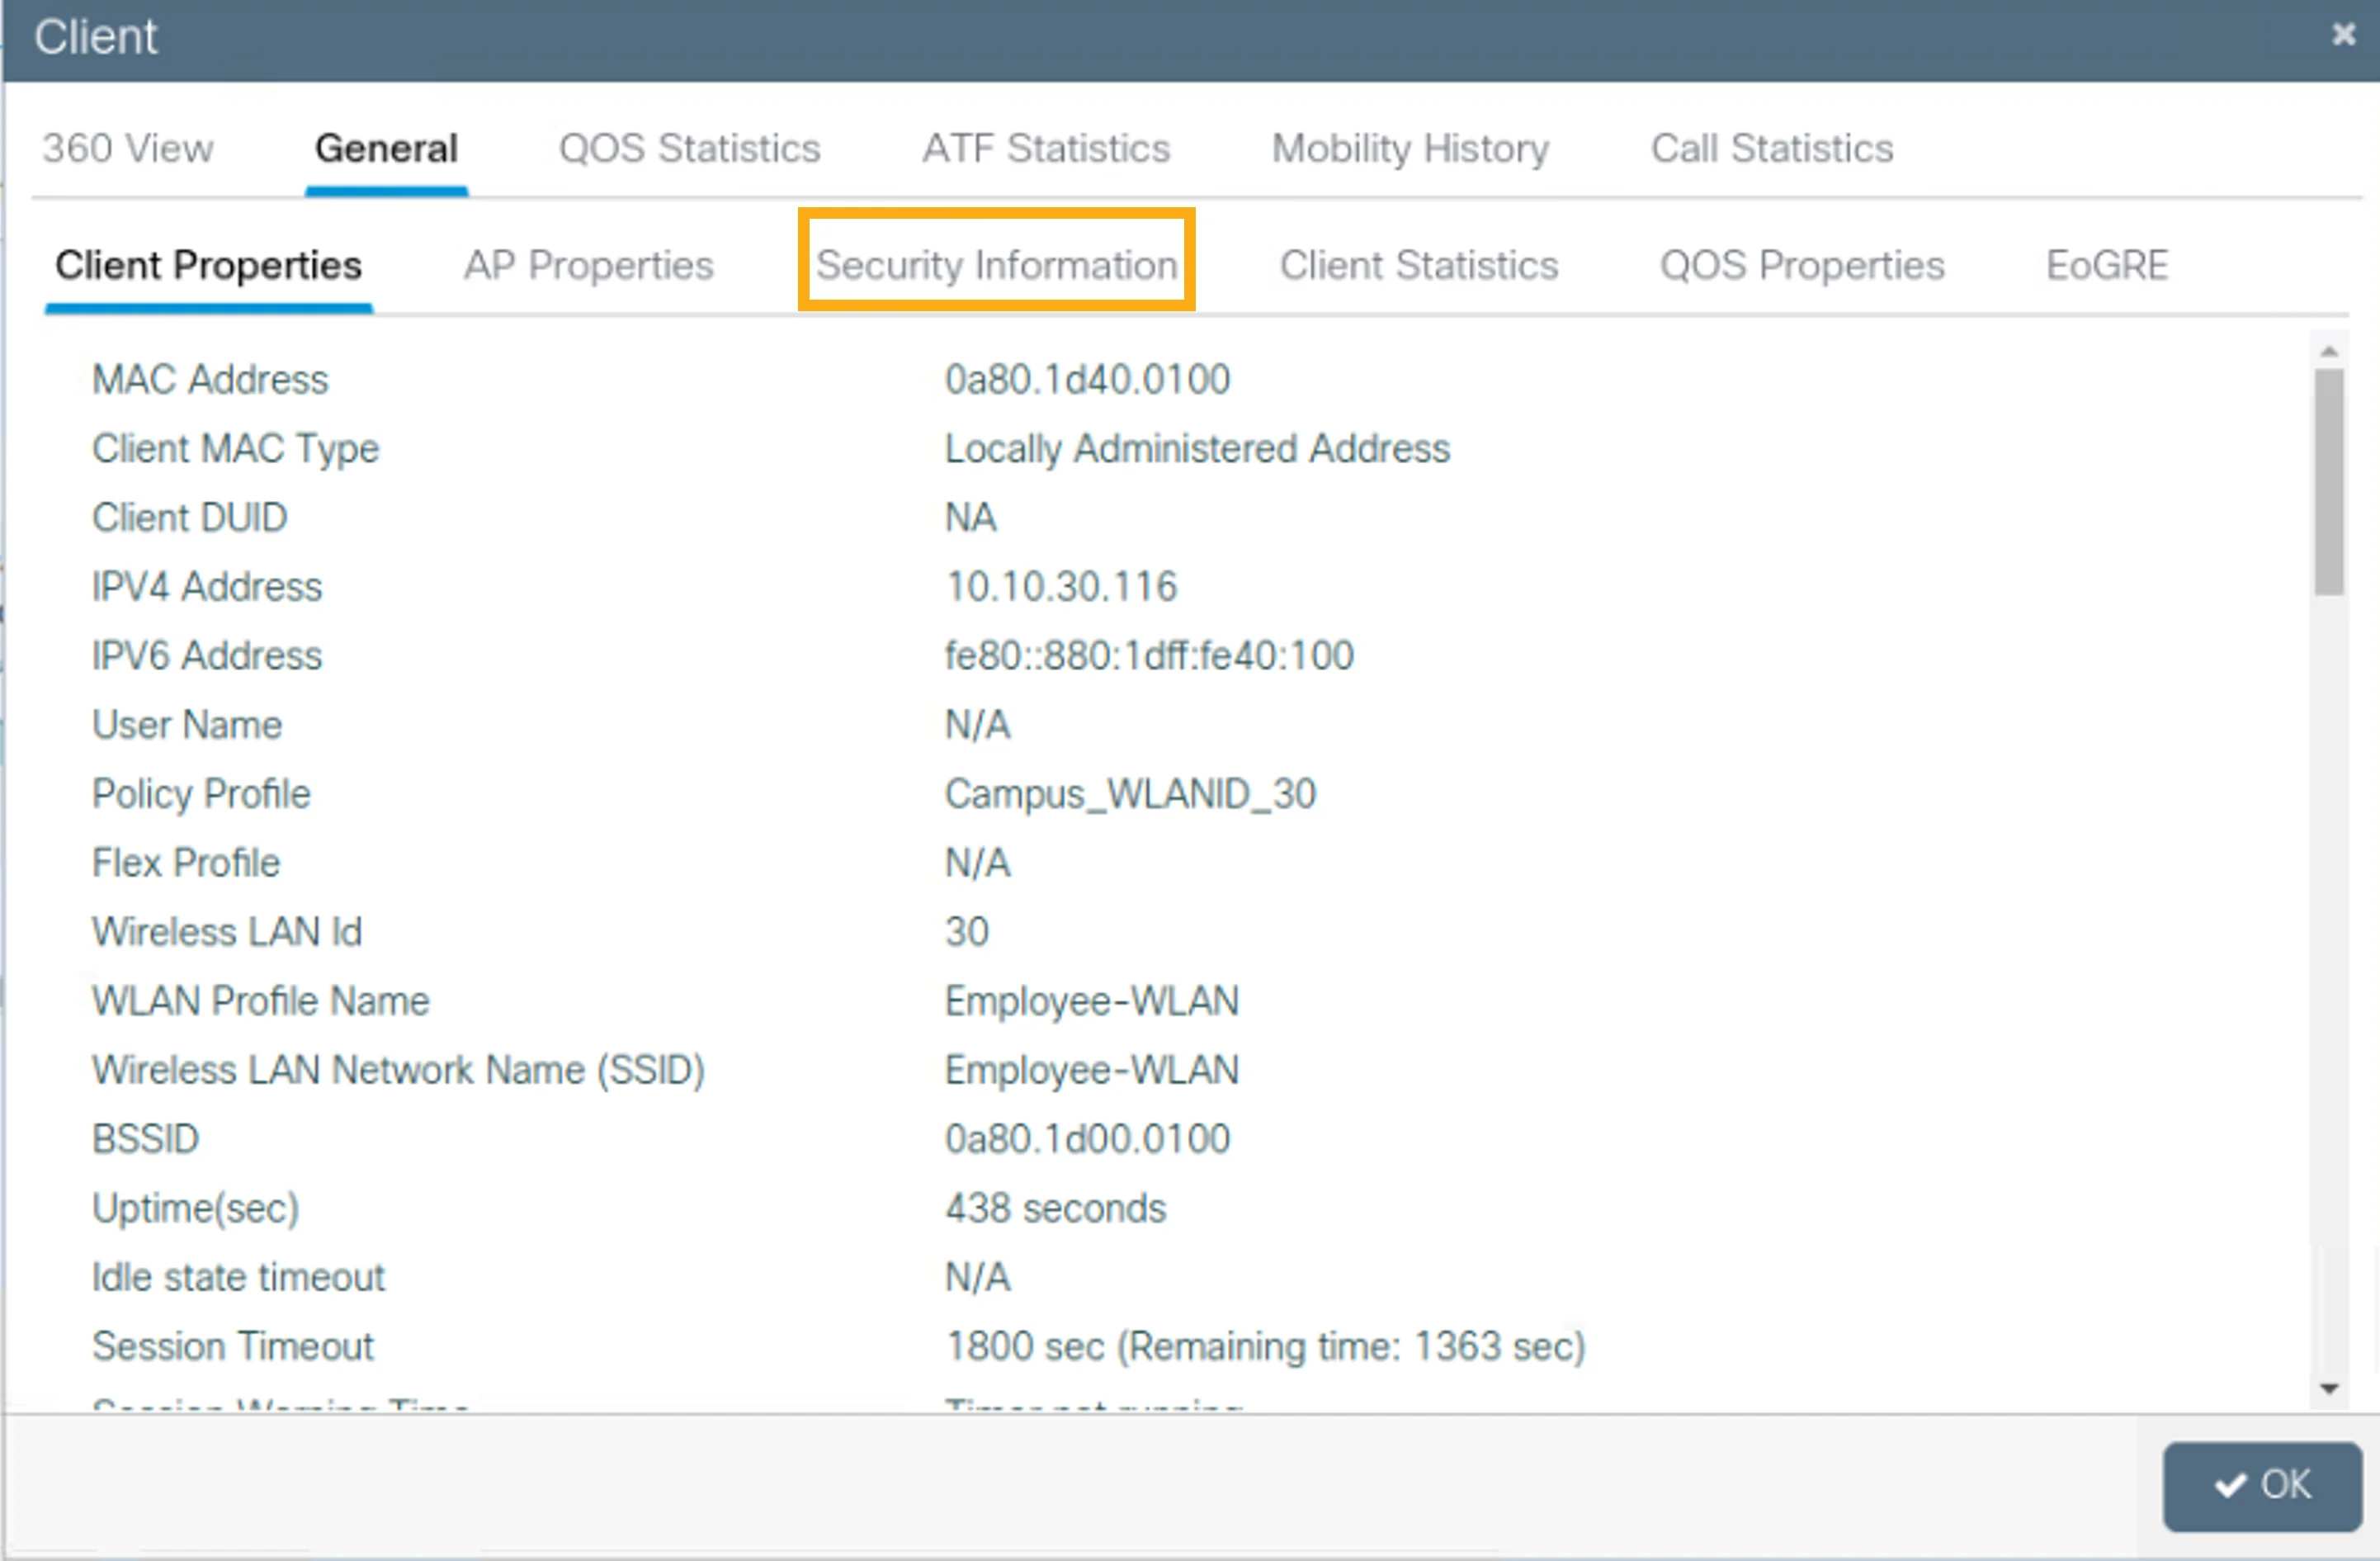
Click the IP address of the first client (10.10.30.116, the IP address of Client PC 1) to get to the 360 View of the client.
按一下第一個用戶端的 IP 位址(10.10.30.116,即 Client PC 1 的 IP 位址),前往該用戶端的 360 View。
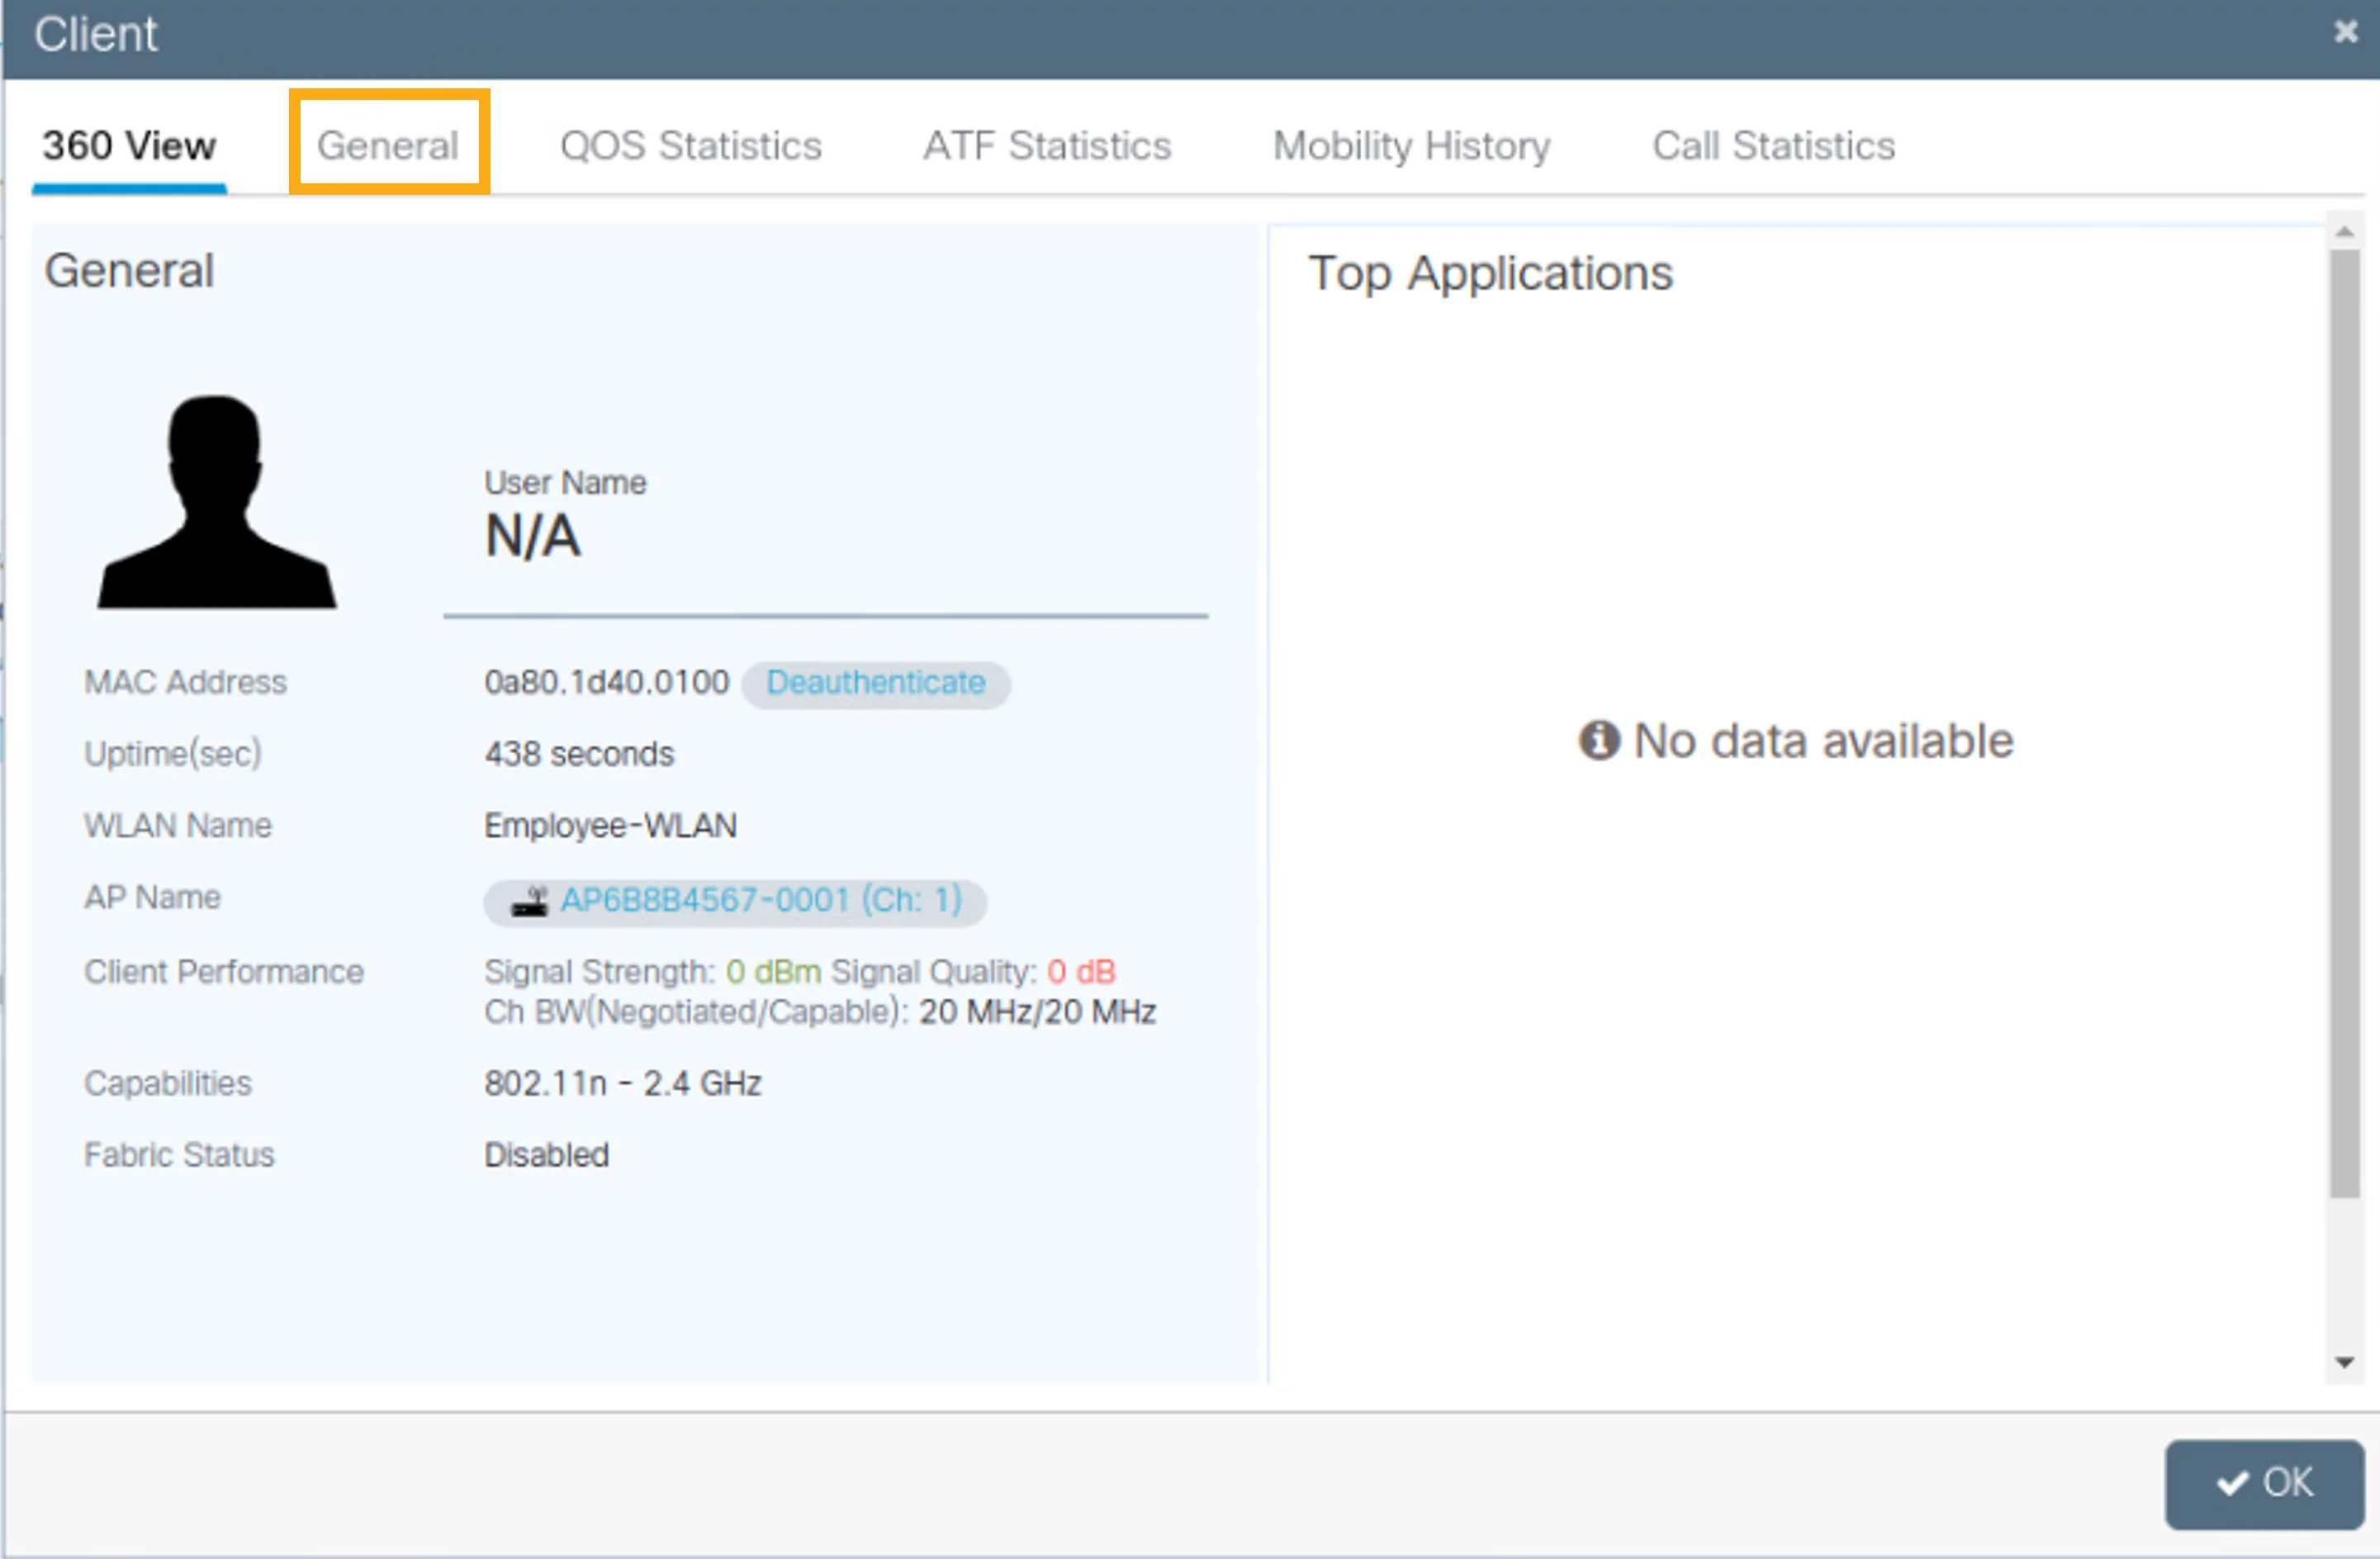
Click the General tab.
按一下 General 標籤。
Under General, click the Security Information tab.
在 General 下,按一下 Security Information 標籤。
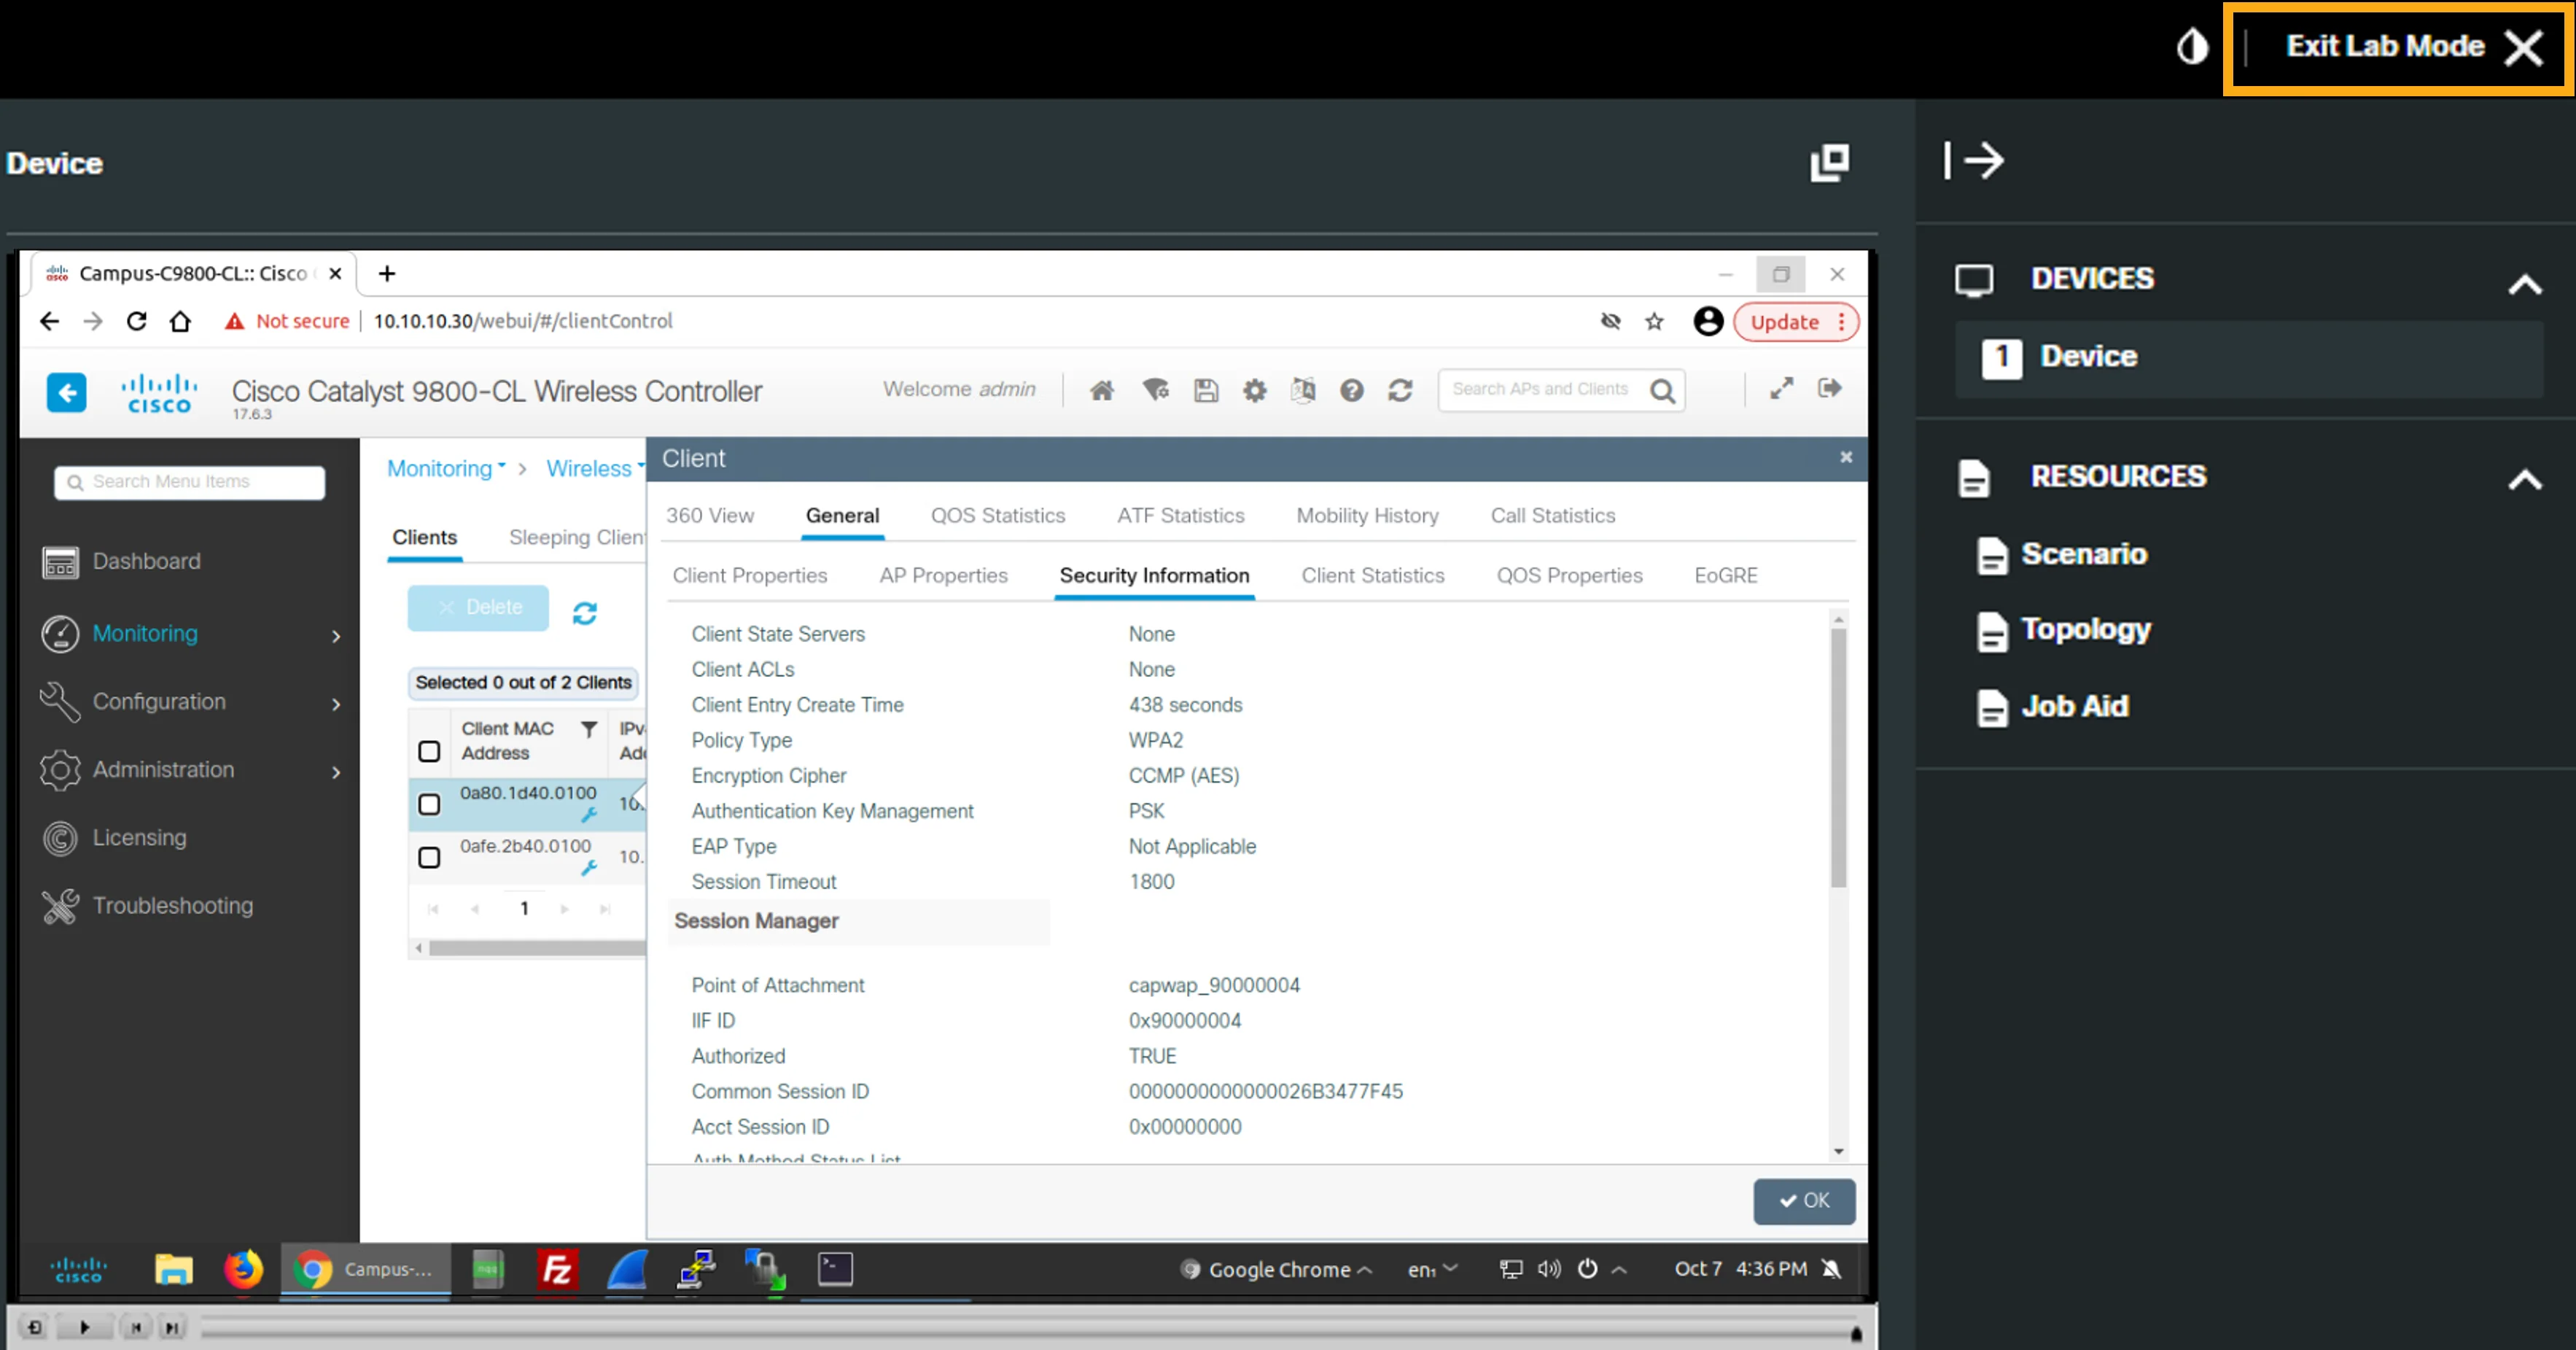
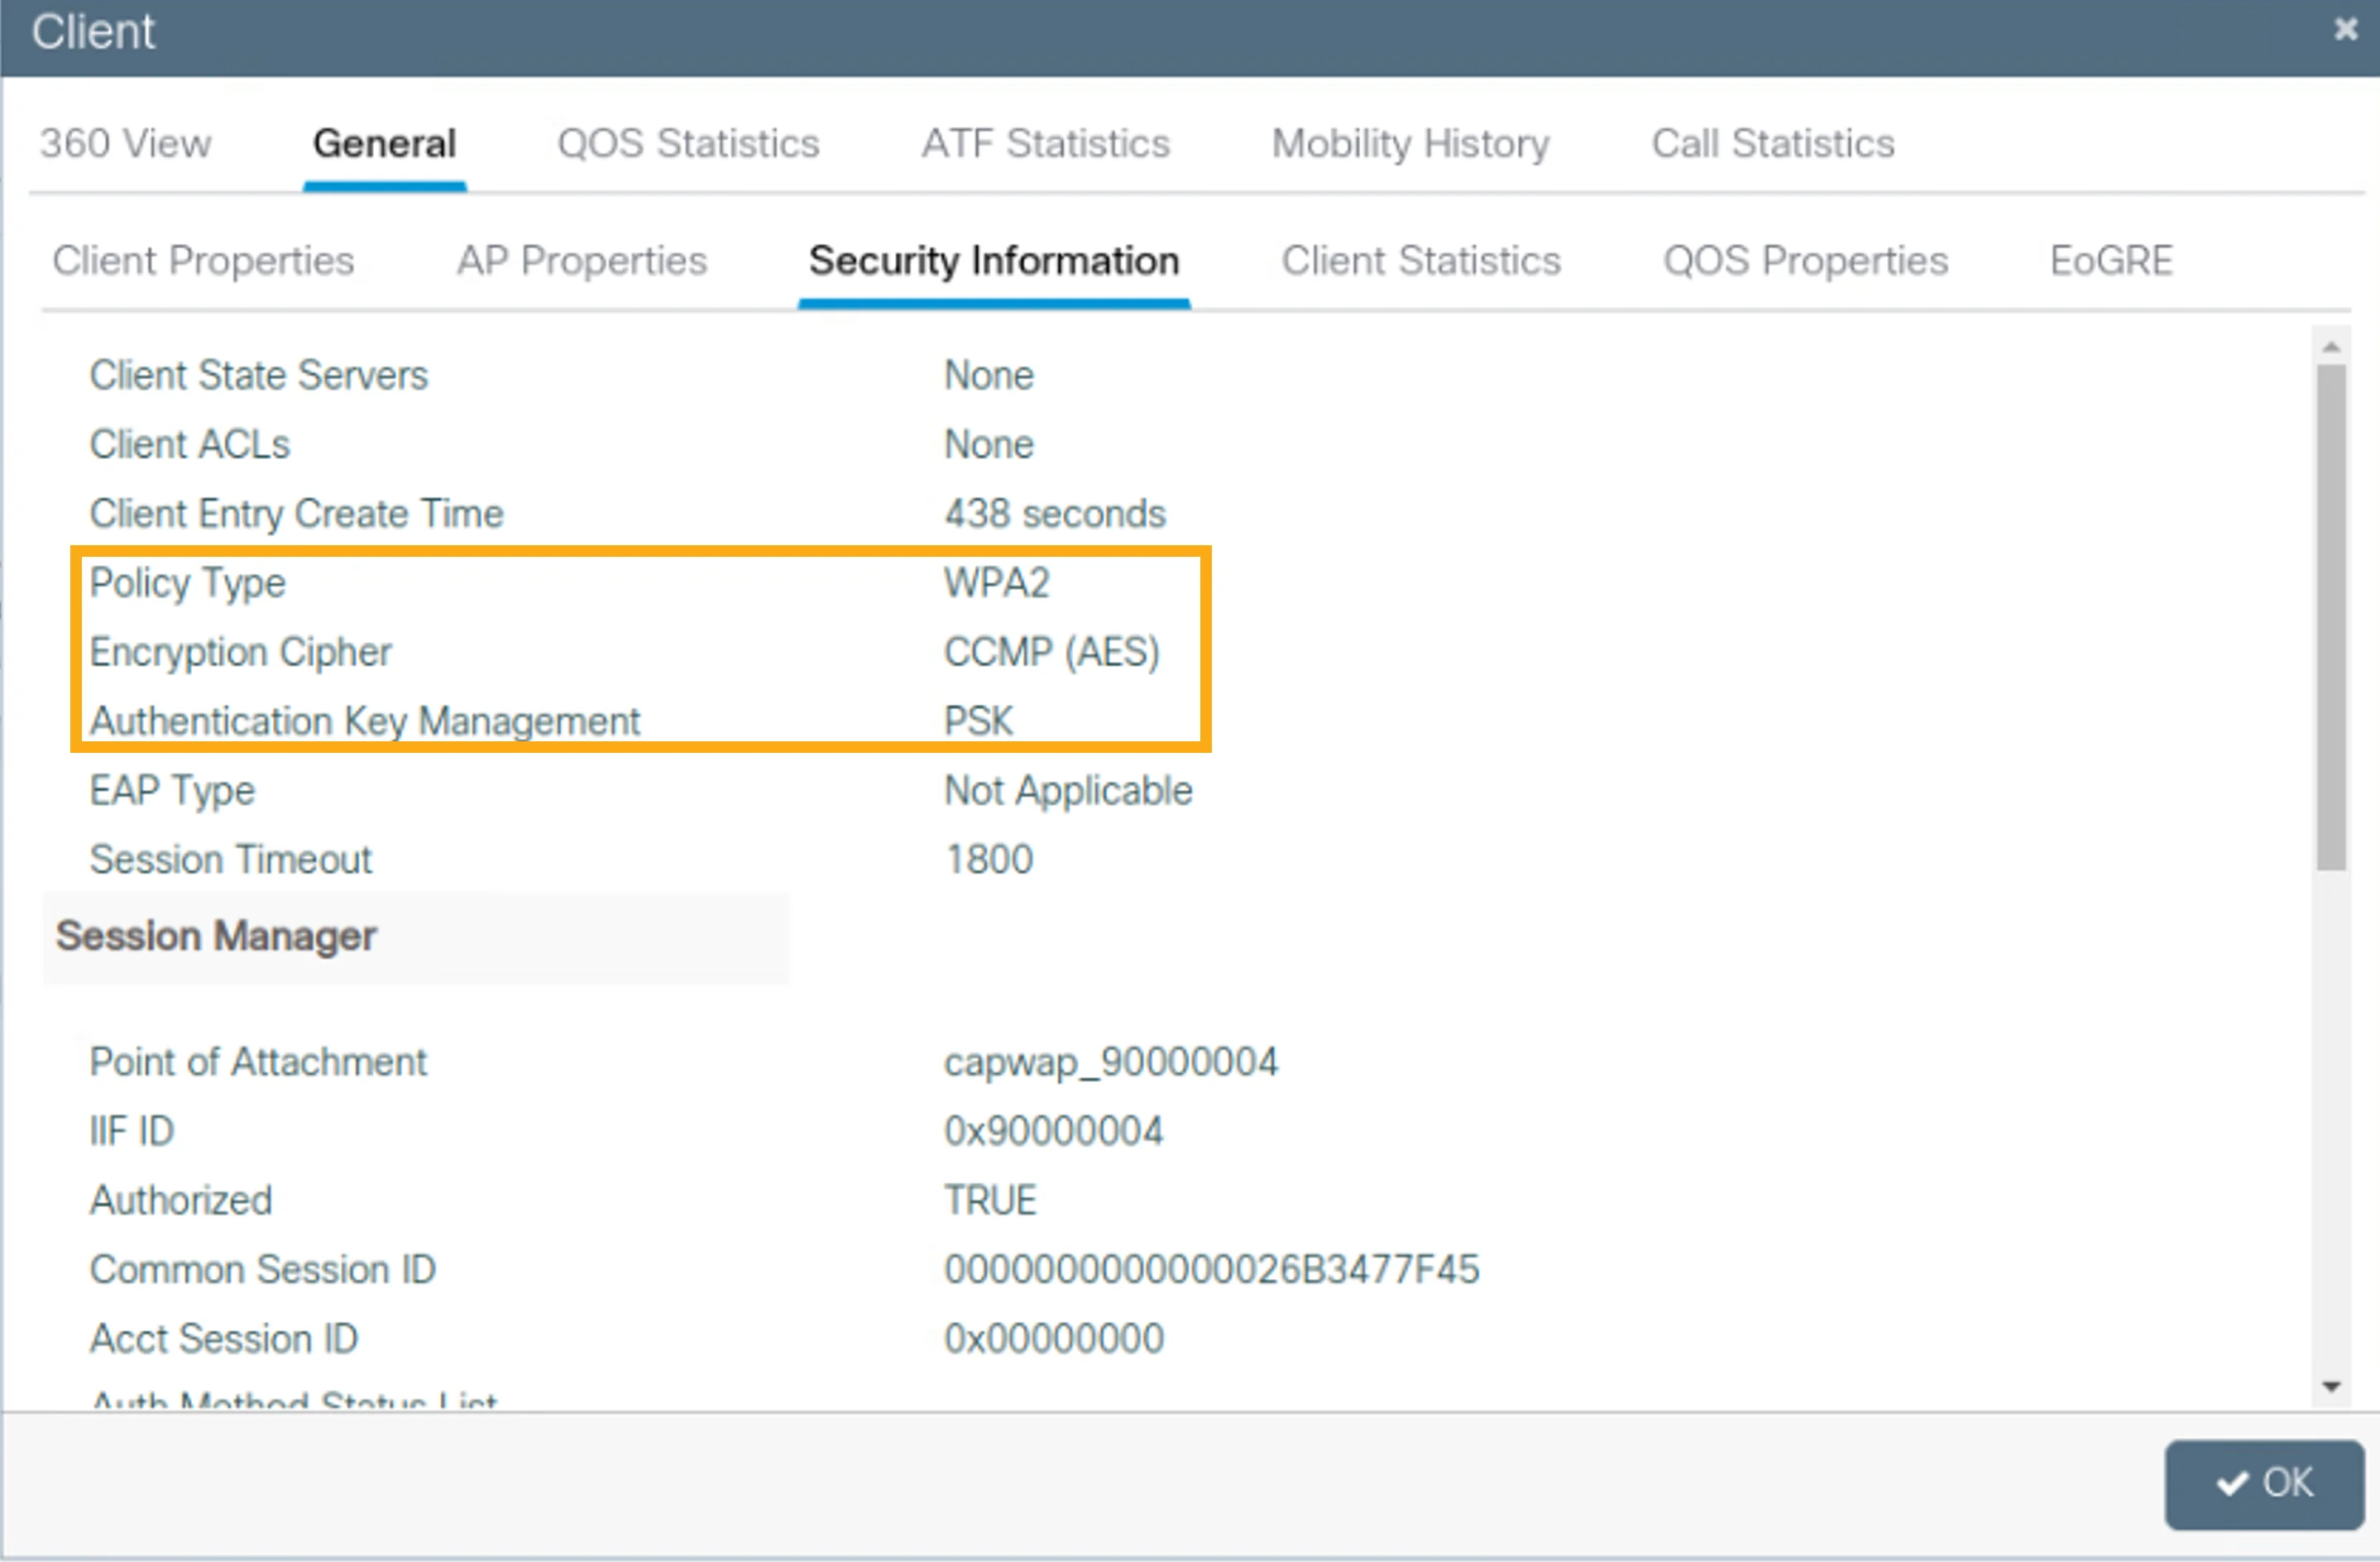
Verify that the client uses WPA2 PSK with CCMP (AES) encryption.
驗證用戶端使用 WPA2 PSK 搭配 CCMP (AES) 加密。
You have reached the last step of this simulation. Click Exit Lab Mode to end the simulation.
您已完成此模擬的最後一個步驟。按一下 Exit Lab Mode 結束模擬。