To understand VLANs, you need a solid understanding of LANs. A LAN is a group of devices that share a common broadcast domain. When a device on the LAN sends broadcast messages, the switch floods the broadcast messages (as well as unknown unicast) to all ports except the incoming port. Therefore, all other devices on the LAN receive them. You can think of a LAN and a broadcast domain as being basically the same thing. Without VLANs, a switch considers all its interfaces to be in the same broadcast domain. In other words, all connected devices are in the same LAN. With VLANs, a switch can put some interfaces into one broadcast domain and some into another. The individual broadcast domains that are created by the switch are called VLANs. A VLAN is a group of devices on one or more LANs that are configured to communicate as if they were attached to the same wire, when in fact they are located on a number of different LAN segments.
要了解 VLAN,你需要對 LAN 有紮實的理解。LAN 是一群共享同一個廣播網域的裝置。當 LAN 上的某裝置傳送廣播訊息時,交換器會將該廣播訊息(以及未知的單播)氾濫轉發到除了進入埠以外的所有連接埠。因此,LAN 上的其他所有裝置都會收到這些訊息。你可以將 LAN 與廣播網域視為基本上是同一件事。若沒有 VLAN,交換器會將其所有介面視為位於同一個廣播網域。換句話說,所有連接的裝置都在同一個 LAN 中。有了 VLAN,交換器可以將部分介面放入一個廣播網域,其他介面放入另一個廣播網域。交換器所建立的個別廣播網域稱為 VLAN。VLAN 是一群位於一個或多個 LAN 上的裝置,經過設定後可以像連接在同一條線路上一樣通訊,儘管它們實際上位於數個不同的 LAN 區段中。
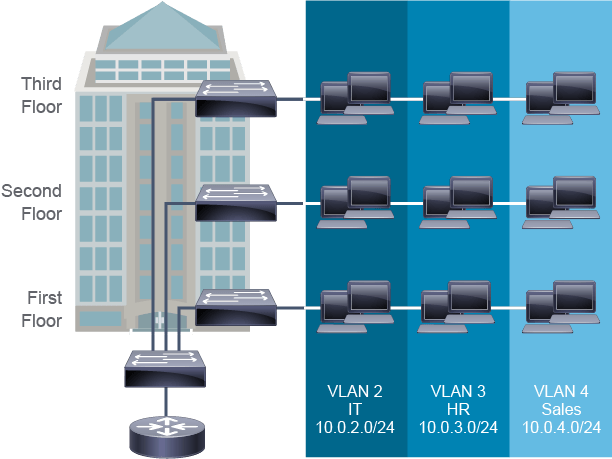
A VLAN allows a network administrator to create logical groups of network devices. These devices act like they are in their own independent network, even if they share a common infrastructure with other VLANs. Each VLAN is a separate Layer 2 broadcast domain that is usually mapped to a unique IP subnet (Layer 3 broadcast domain). A VLAN can exist on a single switch or span multiple switches. VLANs can include devices in a single building as illustrated in the figure or multiple-building infrastructures.
VLAN 讓網路管理員能夠建立邏輯性的網路裝置群組。這些裝置的行為就像處於各自獨立的網路中,即使它們與其他 VLAN 共用相同的基礎架構。每個 VLAN 都是一個獨立的第 2 層廣播網域,通常會對應到一個唯一的 IP 子網路(第 3 層廣播網域)。VLAN 可以存在於單一交換器上,也可以跨越多台交換器。VLAN 可以包含單一建築物內的裝置(如圖所示),也可以涵蓋跨多棟建築物的基礎架構。
Within the switched network, VLANs can provide segmentation and organizational flexibility. You can design a VLAN structure that lets you group devices by functions, project teams, or applications without regard to the physical location of the users. VLANs also serve as the basis for network segmentation, which is one of the most important parts of implementing network security. They allow you to map Layer 2 broadcast domains to Layer 3 broadcast domains, which later allows you to implement access and security policies for specific groups of users.
在交換式網路中,VLAN 能提供區隔與組織上的彈性。你可以設計一套 VLAN 架構,依照功能、專案團隊或應用程式來將裝置分組,而不必考慮使用者的實體位置。VLAN 也是網路區隔的基礎,而網路區隔是實作網路安全性中最重要的一環。VLAN 讓你能將第 2 層廣播網域對應到第 3 層廣播網域,之後你便可以針對特定使用者群組實作存取與安全性政策。
If a switch port is operating as an access port, it can be assigned to only one VLAN, which adds a layer of security. Multiple ports can be assigned to each VLAN. Ports in the same VLAN share broadcast domain, while ports in different VLANs do not share a broadcast domain. Containing broadcasts within a VLAN improves the overall performance of the network.
若交換器連接埠以存取埠模式運作,它只能被指派給一個 VLAN,這增加了一層安全性。每個 VLAN 可以指派多個連接埠。同一個 VLAN 中的連接埠共用廣播網域,而不同 VLAN 的連接埠則不共用廣播網域。將廣播限制在單一 VLAN 內可提升整體網路效能。
If you want to carry traffic for multiple VLANs across multiple switches, you need a trunk to connect each pair of switches. VLANs can also connect across WANs. It is important to know that traffic cannot pass directly to another VLAN (between broadcast domains) within the switch or between two switches. To interconnect two different VLANs, you must use routers or Layer 3 switches. The process of forwarding network traffic from one VLAN to another VLAN using a router is called inter-VLAN routing. Routers perform inter-VLAN routing by either having a separate router interface for each VLAN, or by using a trunk to carry traffic for all VLANs. The devices on the VLAN send traffic through the router to reach other VLANs.
若你想在多台交換器之間承載多個 VLAN 的流量,就需要一條中繼線來連接每一對交換器。VLAN 也可以跨 WAN 連接。要注意的是,流量無法在交換器內部或兩台交換器之間直接傳遞到另一個 VLAN(廣播網域之間)。若要互連兩個不同的 VLAN,必須使用路由器或第 3 層交換器。利用路由器將網路流量從一個 VLAN 轉送到另一個 VLAN 的程序,稱為 VLAN 間路由。路由器執行 VLAN 間路由的方式,可以是為每個 VLAN 提供各自獨立的路由器介面,或使用一條中繼線來承載所有 VLAN 的流量。VLAN 上的裝置會透過路由器傳送流量,以抵達其他 VLAN。
Usually, subnet numbers are chosen to reflect which VLANs they are associated. The figure shows that VLAN 2 uses subnet 10.0.2.0/24, VLAN 3 uses 10.0.3.0/24, and VLAN 4 uses 10.0.4.0/24. In this example, the third octet clearly identifies the VLAN that the device belongs to. The VLAN design must take into consideration the implementation of a hierarchical, network-addressing scheme.
通常子網路編號的選取會反映其所對應的 VLAN。圖中顯示 VLAN 2 使用子網路 10.0.2.0/24,VLAN 3 使用 10.0.3.0/24,VLAN 4 使用 10.0.4.0/24。在此範例中,第三個八位元組清楚標示了裝置所屬的 VLAN。VLAN 設計時必須考量階層式網路定址方案的實作。
Cisco Catalyst Series switches have a factory default configuration in which various default VLANs are preconfigured to support various media and protocol types. The default Ethernet VLAN is VLAN 1, which contains all ports by default.
Cisco Catalyst 系列交換器出廠時的預設設定中,預先設定了多個預設 VLAN,以支援各種媒介與協定類型。預設的乙太網路 VLAN 是 VLAN 1,預設情況下包含所有連接埠。
If you want to communicate with the Cisco Catalyst switch for management purposes from a remote client that is on a different VLAN, which means it is on a different subnet, then the switch must have an IP address and default-gateway configured. This IP address must be in the management VLAN, which is by default VLAN 1.
若你想從位於不同 VLAN(即不同子網路)的遠端用戶端,出於管理目的與 Cisco Catalyst 交換器通訊,則交換器必須設定 IP 位址與預設閘道。此 IP 位址必須位於管理 VLAN 中,預設情況下該管理 VLAN 為 VLAN 1。