These commands are used in the global configuration mode to configure standard numbered IPv4 ACLs:
以下命令用於在全域設定模式中設定編號標準 IPv4 ACL:
Router(config)# access-list access-list-number permit|deny source [source-wildcard] | host { address | name} | anyThe access-list access-list-number command is used for the numbered access lists. To configure a standard IPv4 ACL, you must choose a number from a range assigned for standard access list. Specifying an ACL number from 1 to 99 or 1300 to 1999 instructs the router to accept numbered standard IPv4 ACL statements. The CLI will allow only the syntax applicable for standard ACL statements.
access-list access-list-number 命令用於編號存取清單。若要設定標準 IPv4 ACL,你必須從分配給標準存取清單的範圍中選擇一個編號。指定 1 到 99 或 1300 到 1999 之間的 ACL 編號,會指示路由器接受編號標準 IPv4 ACL 陳述式,CLI 只會允許適用於標準 ACL 陳述式的語法。
The following commands are used to configure standard named IPv4 ACLs. When adding ACL statements to the configuration, Cisco IOS Software automatically numbers each statement. By default, the numbering starts with 10 and subsequent numbers are incremented by 10. The sequence number determines where the new entry will be placed in the ACL. You can use any number that is not currently assigned, even if it is not a multiple of 10.
以下命令用於設定標準具名 IPv4 ACL。當你將 ACL 陳述式加入設定時,Cisco IOS 軟體會自動為每條陳述式編號,預設從 10 開始,之後每條遞增 10。序號決定了新項目在 ACL 中的放置位置,你可以使用任何目前尚未被使用的編號,即使它不是 10 的倍數也可以。
Router(config)# ip access-list standard access-list-name
Router(config-std-nacl)# [sequence-number] permit | deny source [source-wildcard] | host { address | name} | any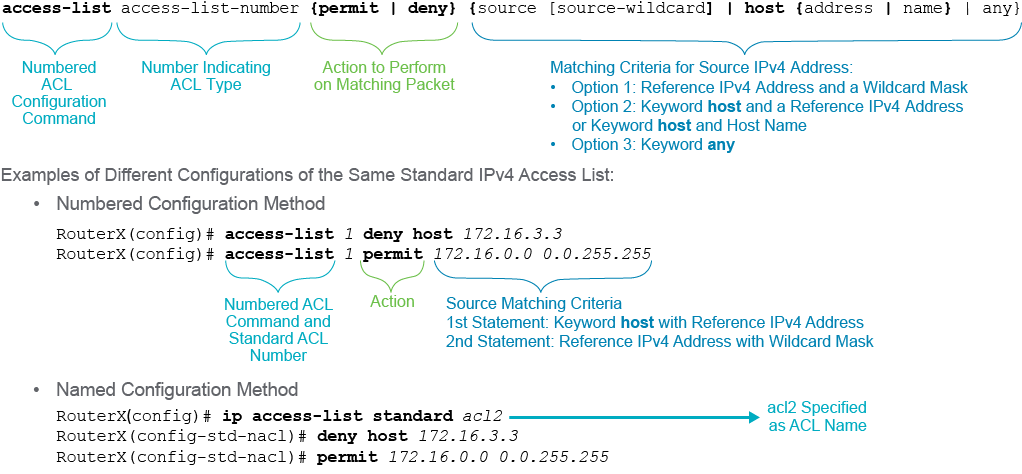
The figure shows the anatomy of a numbered standard ACL statement. A numbered standard ACL statement consists of the access list identification (a number) followed by a keyword indicating the action to be taken, and the matching criteria. Since standard IPv4 access lists allow matching only on source IPv4 address, the matching criteria always refers to the source IPv4 address.
圖中展示了編號標準 ACL 陳述式的組成結構。一條編號標準 ACL 陳述式由存取清單識別碼(一個編號)、指示所要採取動作的關鍵字,以及比對條件組成。由於標準 IPv4 存取清單只能根據來源 IPv4 位址進行比對,因此比對條件永遠是指來源 IPv4 位址。
Each ACL statement includes a keyword indicating an action that a device must take for the packet that matches the criteria. The action is either a permit action, allowing a matching packet to be processed further (forwarded, analyzed, ") or a deny action, which discards the matching packets when using ACL for packet filtering. To specify an action that a device takes for the packet that matches the criteria, use the keywords permit or deny.
每條 ACL 陳述式都包含一個關鍵字,用來指示裝置對符合條件的封包應採取的動作。該動作若不是允許動作(讓符合條件的封包繼續被處理,例如轉送、分析等),就是拒絕動作(在將 ACL 用於封包過濾時,丟棄符合條件的封包)。若要指定裝置對符合條件封包所採取的動作,請使用關鍵字 permit 或 deny。
You specify matching criteria either by using reference IPv4 address and a wildcard mask or its abbreviated keyword. If wildcard mask is not specified, the 0.0.0.0 value is assumed.
你可以透過參考 IPv4 位址與萬用字元遮罩,或其縮寫關鍵字來指定比對條件。若未指定萬用字元遮罩,系統會假設其值為 0.0.0.0。
An example of a standard ACL configuration on RouterX is:
在 RouterX 上設定標準 ACL 的範例如下:
RouterX(config)# access-list 1 deny host 172.16.3.3
RouterX(config)# access-list 1 permit 172.16.0.0 0.0.255.255
If this ACL is used as a traffic filter, it would discard traffic from host 172.16.3.3 and allow traffic from other devices in the network 172.16.0.0. Note that an access list must have at least one permit statement, otherwise it blocks all traffic.
若此 ACL 用作流量過濾器,它會丟棄來自主機 172.16.3.3 的流量,並允許來自 172.16.0.0 網路中其他裝置的流量。請注意,存取清單必須至少包含一條允許陳述式,否則會封鎖所有流量。
The ip access-list standard command is used for named standard IPv4 access lists. Note the ip keyword added at the beginning of the command.
ip access-list standard 命令用於具名標準 IPv4 存取清單。請注意此命令開頭多了 ip 關鍵字。
The name you choose for the access list is an arbitrary descriptive alphanumeric string. Because it is arbitrary, the CLI cannot interpret it unambiguously. You must specify the type of list that you are naming, which is why the keyword standard must be used in the ip access-list command when configuring a named standard IPv4 ACL. Using meaningful descriptive names to identify access lists makes it easier to indicate its purpose. Capitalizing ACL names makes them stand out when viewing device configuration and to distinguish ACL name from actual device CLI command.
你為存取清單選擇的名稱是任意的描述性英數字串。正因為它是任意的,CLI 無法明確解讀其含義,因此你必須指定所命名清單的類型,這也是為什麼在設定具名標準 IPv4 ACL 時,ip access-list 命令中必須使用 standard 關鍵字。使用具意義的描述性名稱來識別存取清單,能更容易表達其用途;將 ACL 名稱大寫,能使其在檢視裝置設定時更加醒目,並與實際的裝置 CLI 命令有所區別。
Using theip access-list standard command takes you to the Named Access List configuration mode, which is indicated by the Router(config-std-nacl)# prompt. Note the abbreviations std and nacl in the prompt, that stand for standard and named ACL, respectively.
使用 ip access-list standard 命令會進入具名存取清單設定模式,以 Router(config-std-nacl)# 提示字元表示。請注意提示字元中的縮寫 std 與 nacl,分別代表 standard(標準)與 named ACL(具名 ACL)。
Once you are in the Named Access List configuration mode, you enter the ACL statements. Each statement has the same elements as its numbered counterpart—it contains the action keyword followed by matching criteria.
進入具名存取清單設定模式後,你就可以輸入 ACL 陳述式。每條陳述式都與其對應的編號版本擁有相同的元素,也就是包含動作關鍵字,接著是比對條件。
The configuration of the same access list used in the previous example using named configuration method is the following:
使用具名設定方式,設定與前一個範例相同存取清單的方式如下:
RouterX(config)# ip access-list standard 1
RouterX(config-std-nacl)# deny host 172.16.3.3
RouterX(config-std-nacl)# permit 172.16.0.0 0.0.255.255
The order of the ACL statements is important. Recall that ACL processing stops after the first match is encountered. Only the matching statement is executed. Other statements are not evaluated. More specific statements, such as those permitting and denying particular hosts, should be placed before the statements matching on a wider range of addresses.
ACL 陳述式的順序非常重要。請記住,ACL 處理會在第一次符合時停止,只有符合的那條陳述式會被執行,其他陳述式不會被評估。像是允許或拒絕特定主機這類較具體的陳述式,應放在比對較廣位址範圍的陳述式之前。
An implicit deny any statement is added to the end of each standard IPv4 access list, denying all other packets that did not match ACL statements.
每個標準 IPv4 存取清單的結尾都會加上一條隱含的 deny any 陳述式,拒絕所有未符合 ACL 陳述式的其他封包。
Router(config)# access-list 20 deny 192.168.1.0 0.0.0.255
Router(config)# access-list 20 permit 192.0.0.0 0.255.255.255關於以下 ACL 陳述式,結果會是什麼?Router(config)# access-list 20 permit 192.168.1.1
Router(config)# access-list 20 deny 192.168.1.0 0.0.0.255
Router(config)# access-list 20 permit 192.0.0.0 0.255.255.255