Introduction
簡介
In this activity, you will explore IPv4 routing focusing on static routing. You will configure and verify static routes and observe the packet-forwarding behavior that is associated with various routing configurations, including the use of a statically defined default route.
在本活動中,你將探索 IPv4 路由,重點放在靜態路由。你將設定並驗證靜態路由,並觀察與各種路由設定相關的封包轉送行為,包括使用靜態定義的預設路由。
The lab is prepared with the devices as represented in the topology diagram and connectivity table. All devices have their basic configurations in place, including host names and IPv4 addresses. Default gateways are defined on PC1, PC2, and SRV1, but no other routing has been configured.
實驗環境已依拓樸圖與連線表準備好裝置。所有裝置都已完成基本設定,包括主機名稱與 IPv4 位址。PC1、PC2 與 SRV1 已定義預設閘道,但尚未設定其他路由。
Topology
拓樸
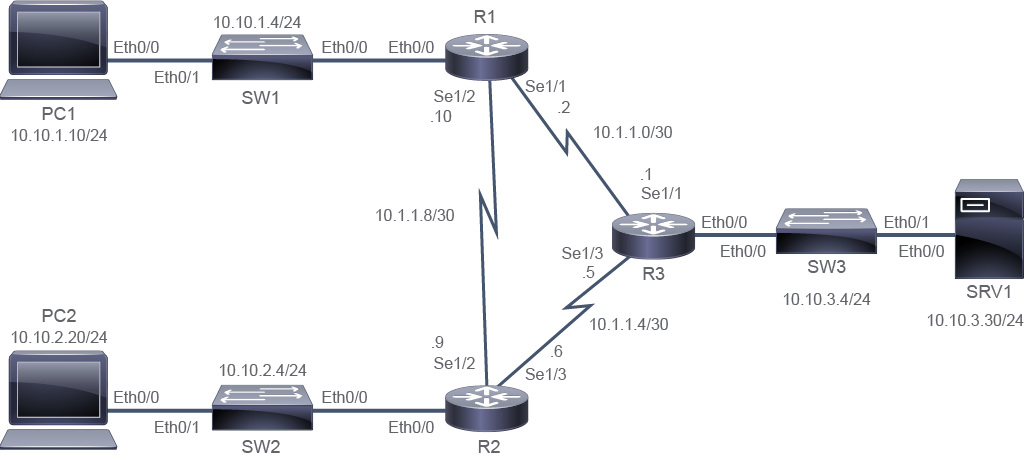
Job Aid
工作輔助資料
Device Information
裝置資訊
Device Information Table
裝置資訊表
Device 裝置 | Characteristic 特性 | Value 值 |
PC1 PC1 | IPv4 address IPv4 位址 | 10.10.1.10/24 10.10.1.10/24 |
PC1 PC1 | Default gateway 預設閘道 | 10.10.1.1 10.10.1.1 |
PC2 PC2 | IPv4 address IPv4 位址 | 10.10.2.20/24 10.10.2.20/24 |
PC2 PC2 | Default gateway 預設閘道 | 10.10.2.1 10.10.2.1 |
SRV1 SRV1 | IPv4 address IPv4 位址 | 10.10.3.30/24 10.10.3.30/24 |
SRV1 SRV1 | Default gateway 預設閘道 | 10.10.3.1 10.10.3.1 |
SW1 SW1 | VLAN 1 IPv4 address VLAN 1 IPv4 位址 | 10.10.1.4/24 10.10.1.4/24 |
SW1 SW1 | Default gateway 預設閘道 | 10.10.1.1 10.10.1.1 |
SW1 SW1 | Ethernet0/0 description Ethernet0/0 描述 | Link to R1 連往 R1 |
SW1 SW1 | Ethernet0/1 description Ethernet0/1 描述 | Link to PC1 連往 PC1 |
SW2 SW2 | VLAN 1 IPv4 address VLAN 1 IPv4 位址 | 10.10.2.4/24 10.10.2.4/24 |
SW2 SW2 | Default gateway 預設閘道 | 10.10.2.1 10.10.2.1 |
SW2 SW2 | Ethernet0/0 description Ethernet0/0 描述 | Link to R2 連往 R2 |
SW2 SW2 | Ethernet0/1 description Ethernet0/1 描述 | Link to PC2 連往 PC2 |
SW3 SW3 | VLAN 1 IPv4 address VLAN 1 IPv4 位址 | 10.10.3.4/24 10.10.3.4/24 |
SW3 SW3 | Default gateway 預設閘道 | 10.10.3.1 10.10.3.1 |
SW3 SW3 | Ethernet0/0 description Ethernet0/0 描述 | Link to R3 連往 R3 |
SW3 SW3 | Ethernet0/1 description Ethernet0/1 描述 | Link to SRV1 連往 SRV1 |
R1 R1 | Ethernet0/0 description Ethernet0/0 描述 | Link to SW1 連往 SW1 |
R1 R1 | Ethernet0/0 IPv4 address Ethernet0/0 IPv4 位址 | 10.10.1.1/24 10.10.1.1/24 |
R1 R1 | Serial1/1 description Serial1/1 描述 | Link to R3 連往 R3 |
R1 R1 | Serial1/1 IPv4 address Serial1/1 IPv4 位址 | 10.1.1.2/30 10.1.1.2/30 |
R1 R1 | Serial1/2 description Serial1/2 描述 | Link to R2 連往 R2 |
R1 R1 | Serial1/2 IPv4 address Serial1/2 IPv4 位址 | 10.1.1.10/30 10.1.1.10/30 |
R2 R2 | Ethernet0/0 description Ethernet0/0 描述 | Link to SW2 連往 SW2 |
R2 R2 | Ethernet0/0 IPv4 address Ethernet0/0 IPv4 位址 | 10.10.2.1/24 10.10.2.1/24 |
R2 R2 | Serial1/2 description Serial1/2 描述 | Link to R1 連往 R1 |
R2 R2 | Serial1/2 IPv4 address Serial1/2 IPv4 位址 | 10.1.1.9/30 10.1.1.9/30 |
R2 R2 | Serial1/3 description Serial1/3 描述 | Link to R3 連往 R3 |
R2 R2 | Serial1/3 IPv4 address Serial1/3 IPv4 位址 | 10.1.1.6/30 10.1.1.6/30 |
R3 R3 | Ethernet0/0 description Ethernet0/0 描述 | Link to SW3 連往 SW3 |
R3 R3 | Ethernet0/0 IPv4 address Ethernet0/0 IPv4 位址 | 10.10.3.1/24 10.10.3.1/24 |
R3 R3 | Serial1/1 description Serial1/1 描述 | Link to R1 連往 R1 |
R3 R3 | Serial1/1 IPv4 address Serial1/1 IPv4 位址 | 10.1.1.1/30 10.1.1.1/30 |
R3 R3 | Serial1/3 description Serial1/3 描述 | Link to R2 連往 R2 |
R3 R3 | Serial1/3 IPv4 address Serial1/3 IPv4 位址 | 10.1.1.5/30 10.1.1.5/30 |
The PCs and SRV in the virtual lab environment are simulated by routers so you should use Cisco IOS commands to configure or for verifications.
在虛擬實驗環境中,PC 與 SRV 是以路由器模擬的,因此設定或驗證時應使用 Cisco IOS 指令。
Task 1: Verify Device Reachability
任務 1:驗證裝置可達性
Activity
活動
Before getting into the configuration of static routes, observe the connectivity when routing is not yet configured on any of the routers. To do that, from PC1 ping SW1 and R1 Ethernet0/0.
在開始設定靜態路由之前,先觀察尚未在任何路由器上設定路由時的連線情況。為此,請從 PC1 對 SW1 和 R1 的 Ethernet0/0 執行 ping。
On PC1, enter the following commands:
在 PC1 上,輸入下列指令:
PC1# ping 10.10.1.4
Type escape sequence to abort.
Sending 5, 100-byte ICMP Echos to 10.10.1.4, timeout is 2 seconds:
.!!!!
Success rate is 80 percent (4/5), round-trip min/avg/max = 1/1/1 ms
PC1# ping 10.10.1.1
Type escape sequence to abort.
Sending 5, 100-byte ICMP Echos to 10.10.1.1, timeout is 2 seconds:
.!!!!
Success rate is 80 percent (4/5), round-trip min/avg/max = 1/1/2 ms
Be sure to take advantage of the Cisco IOS command recall feature when entering similar commands. Use the Up Arrow key to scroll through the command history and use the Right and Left Arrow and Backspace keys to edit commands that are similar to what you need to enter.
在輸入類似指令時,記得善用 Cisco IOS 的指令回叫功能。使用向上箭頭鍵捲動指令歷史紀錄,並使用向右與向左箭頭及Backspace鍵編輯與所需指令類似的內容。
Study the topology diagram whenever it is helpful to clarify the physical layout of the lab.
在有助於釐清實驗環境實體配置時,隨時查看拓樸圖。
You expected to be able to ping these addresses. They are on the same subnet as PC1, so routing is not required. The Address Resolution Protocol (ARP) protocol resolves the MAC address of the peer and communication ensues at Layer 2.
你應該預期能夠 ping 通這些位址。它們與 PC1 位於同一子網路,因此不需要路由。位址解析協定(ARP)會解析對等端的 MAC 位址,通訊便在第 2 層進行。
PCs, and IPv4 end hosts in general, normally have routing tables. They usually consist of a single entry—a default route to their default gateway. View the routing table on PC1 to verify that R1 is its default gateway.
PC 及一般的 IPv4 終端主機通常都有路由表,通常只包含一個項目,也就是通往預設閘道的預設路由。檢視 PC1 的路由表,確認 R1 是其預設閘道。
On PC1, enter the following command:
在 PC1 上,輸入下列指令:
PC1# show ip route
Default gateway is 10.10.1.1

Host               Gateway           Last Use    Total Uses  Interface
ICMP redirect cache is empty
The default gateway for PC1 is the 10.10.1.1 IPv4 address. This IPv4 address is applied on the Ethernet0/0 interface on R1 that is connecting to SW1.
PC1 的預設閘道是 IPv4 位址 10.10.1.1。這個 IPv4 位址設定在 R1 上連接 SW1 的 Ethernet0/0 介面。
From PC1, ping the IPv4 addresses of the remote Serial1/1 and Serial1/2 interfaces of R1.
從 PC1 對 R1 上遠端的 Serial1/1 與 Serial1/2 介面的 IPv4 位址執行 ping。
On PC1, enter these commands:
在 PC1 上,輸入下列指令:
PC1# ping 10.1.1.2
Type escape sequence to abort.
Sending 5, 100-byte ICMP Echos to 10.1.1.2, timeout is 2 seconds:
!!!!!
Success rate is 100 percent (5/5), round-trip min/avg/max = 1/201/1002 ms
PC1# ping 10.1.1.10
Type escape sequence to abort.
Sending 5, 100-byte ICMP Echos to 10.1.1.10, timeout is 2 seconds:
!!!!!
Success rate is 100 percent (5/5), round-trip min/avg/max = 1/1/1 ms
The pings were successful without any routes configured on R1. PC1 was preconfigured to send all remote traffic to R1 and R1 has all the respective subnets (including the subnet of PC1) in its routing table as directly connected networks.
在 R1 上尚未設定任何路由的情況下,ping 卻成功了。PC1 事先設定為將所有遠端流量傳送給 R1,而 R1 的路由表中已將所有相關子網路(包括 PC1 所在的子網路)視為直接連接網路。
Try to ping the R2 Serial1/2 interface, which is a point-to-point neighbor to the Serial1/2 interface of R1, from PC1.
嘗試從 PC1 對 R2 的 Serial1/2 介面執行 ping,該介面與 R1 的 Serial1/2 介面是點對點鄰居。
On PC1, enter this command:
在 PC1 上,輸入下列指令:
PC1# ping 10.1.1.9
Type escape sequence to abort.
Sending 5, 100-byte ICMP Echos to 10.1.1.9, timeout is 2 seconds:
.....
Success rate is 0 percent (0/5)
This ping attempt fails. Interestingly, the Internet Control Message Protocol (ICMP) echo requests actually do make it to R2. PC1 is configured to use R1 as its default gateway, and R1 has 10.1.1.0/30 as a directly connected network in its routing table. So, the forwarding to R2 will function. The problem is that R2 does not have a route back to 10.10.1.0/24 (the network PC1 belongs to) and, as a result, cannot forward the replies to R1. Therefore, R2 drops the ICMP packet.
此次 ping 嘗試失敗。有趣的是,網際網路控制訊息協定(ICMP)回應請求實際上有送達 R2。PC1 設定使用 R1 作為預設閘道,而 R1 的路由表中將 10.1.1.0/30 視為直接連接網路,因此轉送至 R2 是可行的。問題在於 R2 沒有回到 10.10.1.0/24(PC1 所屬網路)的路由,因此無法將回應轉送給 R1。於是 R2 丟棄了這個 ICMP 封包。
Task 2: Configure and Verify Static Routes
任務 2:設定並驗證靜態路由
Activity
活動
It is now time to configure some static routes. On R1, configure routes to 10.10.2.0/24 and 10.10.3.0/24 networks through R2 and R3 as the next-hop, respectively.
現在該設定一些靜態路由了。在 R1 上,設定分別以 R2 與 R3 作為下一跳,通往 10.10.2.0/24 與 10.10.3.0/24 網路的路由。
On R1, enter these commands:
在 R1 上,輸入下列指令:
R1# configure terminal
R1(config)# ip route 10.10.2.0 255.255.255.0 10.1.1.9
R1(config)# ip route 10.10.3.0 255.255.255.0 10.1.1.1
R1(config)# end
R1#On R2, configure routes to 10.10.1.0/24 and 10.10.3.0/24 networks through R1 and R3 as the next-hop, respectively.
在 R2 上,設定分別以 R1 與 R3 作為下一跳,通往 10.10.1.0/24 與 10.10.3.0/24 網路的路由。
On R2, enter these commands:
在 R2 上,輸入下列指令:
R2# configure terminal
R2(config)# ip route 10.10.1.0 255.255.255.0 10.1.1.10
R2(config)# ip route 10.10.3.0 255.255.255.0 10.1.1.5
R2(config)# end
R2#Study the topology diagram and consider the static routes that you just configured. Should PC1 be able to ping PC2? How about SRV1? And how about 10.1.1.6 or 10.1.1.5 (IPv4 addresses in the subnet between R2 and R3)? Explore the current connectivity from PC1 to PC2, R2 and SRV1.
研究拓樸圖,並思考你剛設定的靜態路由。PC1 應該能夠 ping 通 PC2 嗎?那 SRV1 呢?10.1.1.6 或 10.1.1.5(R2 與 R3 之間子網路的 IPv4 位址)又如何?探索 PC1 到 PC2、R2 與 SRV1 目前的連線情況。
On PC1, enter the following command:
在 PC1 上,輸入下列指令:
PC1# ping 10.10.2.20
Type escape sequence to abort.
Sending 5, 100-byte ICMP Echos to 10.10.2.20, timeout is 2 seconds:
.!!!!
Success rate is 80 percent (4/5), round-trip min/avg/max = 1/1/1 ms
PC1 can ping PC2. This fact implies bidirectional connectivity. The forwarding of ICMP echoes from PC1 to PC2 were successful, and the forwarding of ICMP echo replies from PC2 to PC1 was successful as well. The first miss (.) in the output is normal behavior since ARP response time is longer than the timeout for ICMP echo replies. Without knowing the destination MAC address, the ICMP echo request cannot be successful.
PC1 可以 ping 通 PC2,這表示雙向連線都成功。從 PC1 到 PC2 的 ICMP 回應請求轉送成功,且從 PC2 到 PC1 的 ICMP 回應回覆也轉送成功。輸出中第一個未回應(.)是正常現象,因為 ARP 的回應時間比 ICMP 回應回覆的逾時時間長。在不知道目的地 MAC 位址的情況下,ICMP 回應請求無法成功。
On PC1 ping SRV1:
在 PC1 上 ping SRV1:
PC1# ping 10.10.3.30
Type escape sequence to abort.
Sending 5, 100-byte ICMP Echos to 10.10.3.30, timeout is 2 seconds:
.....
Success rate is 0 percent (0/5)
This ping attempt was not successful. With the current route configuration, the ICMP echoes will actually reach SRV1. R1 has a route to 10.10.3.0/24 network using R3, and R3 has an interface that is directly connected to 10.10.3.0/24 network. However, the ICMP echo replies that SRV1 generated will be sent to R3 (the default gateway of SRV1), but R3 does not have a route back to reach 10.10.1.0/24 network of PC1. Therefore, R3 drops the echo replies.
此次 ping 嘗試未成功。以目前的路由設定,ICMP 回應請求實際上會送達 SRV1。R1 有一條經由 R3 通往 10.10.3.0/24 網路的路由,而 R3 有一個直接連接到 10.10.3.0/24 網路的介面。然而,SRV1 產生的 ICMP 回應回覆會傳送給 R3(SRV1 的預設閘道),但 R3 沒有回到 10.10.1.0/24(PC1 所在網路)的路由,因此 R3 丟棄了這些回應回覆。
The period (.) characters in the ping output indicate timeouts on the reply.
ping 輸出中的句點(.)字元表示回覆逾時。
On PC1 ping R2 Serial1/3:
在 PC1 上 ping R2 的 Serial1/3:
PC1# ping 10.1.1.6
Type escape sequence to abort.
Sending 5, 100-byte ICMP Echos to 10.1.1.6, timeout is 2 seconds:
U.U.U
Success rate is 0 percent (0/5)
This ping attempt fails for a different reason. The subnet 10.1.1.4/30 is the point-to-point link between R2 and R3. R1 does not have a route to that subnet. Therefore, it must drop the packets that are destined for that subnet.
此次 ping 嘗試因不同原因而失敗。子網路 10.1.1.4/30 是 R2 與 R3 之間的點對點連結。R1 沒有到該子網路的路由,因此必須丟棄以該子網路為目的地的封包。
The "U" characters in the ping output indicate that a router in the forwarding path returned ICMP Unreachable messages to PC1.
ping 輸出中的「U」字元表示轉送路徑上的某台路由器向 PC1 傳回了 ICMP 無法到達訊息。
Study the topology diagram. There are six subnets. Each router has direct connectivity to three of those subnets with the remaining three subnets being remote to the router. For full connectivity, each router must have a route defined for each of the three remote subnets. Configure the third static route on both R1 and R2 and configure all three routes on R3.
研究拓樸圖。共有六個子網路。每台路由器都直接連接其中三個子網路,其餘三個子網路對該路由器而言是遠端的。為了達到完整連線,每台路由器都必須為這三個遠端子網路各定義一條路由。請在 R1 與 R2 上設定第三條靜態路由,並在 R3 上設定全部三條路由。
On R1, enter these commands:
在 R1 上,輸入下列指令:
R1# configure terminal
R1(config)# ip route 10.1.1.4 255.255.255.252 10.1.1.9
R1(config)# end
R1#
On R1 and R2, if your login session has not timed out, command recall will still function when you enter configuration mode, providing access to the previously entered route commands. But, be careful. The routes have different subnet masks, so you must change them along with the IPv4 addresses. Note, that from R1 perspective there are two paths to reach the 10.1.1.4/30 subnet. Therefore, the next-hop can be either R2 (10.1.1.9) or R3 (10.1.1.1).
在 R1 與 R2 上,如果登入工作階段尚未逾時,進入設定模式後指令回叫功能仍可使用,讓你能存取先前輸入的路由指令。但要小心,這些路由的子網路遮罩不同,所以你必須連同 IPv4 位址一起更改。請注意,從 R1 的角度來看,有兩條路徑可到達 10.1.1.4/30 子網路,因此下一跳可以是 R2(10.1.1.9)或 R3(10.1.1.1)。
On R2, enter these commands:
在 R2 上,輸入下列指令:
R2# configure terminal
R2(config)# ip route 10.1.1.0 255.255.255.252 10.1.1.10
R2(config)# end
R2#
The next-hop (10.1.1.10) that is specified in the static route is the Serial1/2 interface on R1. The 10.1.1.5 IPv4 address applied on Serial1/3 interface on R3 would have been an equivalent option for the next-hop. The choice to use R1 as the next-hop was arbitrary.
靜態路由中指定的下一跳(10.1.1.10)是 R1 上的 Serial1/2 介面。R3 上 Serial1/3 介面所設定的 IPv4 位址 10.1.1.5 原本也是同樣可行的下一跳選項。選擇以 R1 作為下一跳是任意決定的。
On R3, enter these commands:
在 R3 上,輸入下列指令:
R3# configure terminal
R3(config)# ip route 10.10.1.0 255.255.255.0 10.1.1.2
R3(config)# ip route 10.10.2.0 255.255.255.0 10.1.1.6
R3(config)# ip route 10.1.1.8 255.255.255.252 10.1.1.2
R3(config)# end
R3#
The next-hop (10.1.1.2) that is specified in the static route to 10.1.1.8/30 (network between R1 and R2) is the Serial1/1 interface on R1. The 10.1.1.6 IPv4 address applied on Serial1/3 interface on R2 would have been an equivalent option for the next-hop. The choice to use R1 as the next-hop was arbitrary.
在通往 10.1.1.8/30(R1 與 R2 之間的網路)的靜態路由中指定的下一跳(10.1.1.2)是 R1 上的 Serial1/1 介面。R2 上 Serial1/3 介面所設定的 IPv4 位址 10.1.1.6 原本也是同樣可行的下一跳選項。選擇以 R1 作為下一跳是任意決定的。
Now it is appropriate to verify the routing tables on all three routers, R1, R2 and R3. Each router should have a route for each of the three remote subnets in the routing table.
現在該驗證 R1、R2 與 R3 這三台路由器的路由表了。每台路由器的路由表中都應該有通往三個遠端子網路各自的路由。
On R1, enter these commands:
在 R1 上,輸入下列指令:
R1# show ip route
Codes: L - local, C - connected, S - static, R - RIP, M - mobile, B - BGP
       D - EIGRP, EX - EIGRP external, O - OSPF, IA - OSPF inter area
       N1 - OSPF NSSA external type 1, N2 - OSPF NSSA external type 2
       E1 - OSPF external type 1, E2 - OSPF external type 2
       i - IS-IS, su - IS-IS summary, L1 - IS-IS level-1, L2 - IS-IS level-2
       ia - IS-IS inter area, * - candidate default, U - per-user static route
       o - ODR, P - periodic downloaded static route, H - NHRP, l - LISP
       + - replicated route, % - next hop override

Gateway of last resort is not set

      10.0.0.0/8 is variably subnetted, 9 subnets, 3 masks
C        10.1.1.0/30 is directly connected, Serial1/1
L        10.1.1.2/32 is directly connected, Serial1/1
S        10.1.1.4/30 [1/0] via 10.1.1.9
C        10.1.1.8/30 is directly connected, Serial1/2
L        10.1.1.10/32 is directly connected, Serial1/2
C        10.10.1.0/24 is directly connected, Ethernet0/0
L        10.10.1.1/32 is directly connected, Ethernet0/0
S        10.10.2.0/24 [1/0] via 10.1.1.9
S        10.10.3.0/24 [1/0] via 10.1.1.1
R1# show running-config | include route
ip route 10.1.1.4 255.255.255.252 10.1.1.9
ip route 10.10.2.0 255.255.255.0 10.1.1.9
ip route 10.10.3.0 255.255.255.0 10.1.1.1
The manually configured static routes on R1 for each of the three remote subnets are now available in the routing table.
在 R1 上為三個遠端子網路各自手動設定的靜態路由,現已出現在路由表中。
If you perform the same steps on R2 and R3, you should get similar results, with appropriate routes configured.
如果你在 R2 與 R3 上執行相同的步驟,應該會得到類似的結果,且已設定相應的路由。
At this point, all three routers have routes (either directly connected or statically defined) to all six subnets. Full connectivity should be available now. On PC1, verify that IPv4 addresses from the different subnets are reachable by issuing the ping command.
此時,三台路由器都擁有通往全部六個子網路的路由(直接連接或靜態定義)。現在應該可以達成完整連線。在 PC1 上,透過執行 ping 指令驗證不同子網路的 IPv4 位址皆可到達。
On PC1, enter these commands:
在 PC1 上,輸入下列指令:
PC1# ping 10.10.2.20
Type escape sequence to abort.
Sending 5, 100-byte ICMP Echos to 10.10.2.20, timeout is 2 seconds:
!!!!!
Success rate is 100 percent (5/5), round-trip min/avg/max = 1/1/1 ms
PC1# ping 10.10.3.30
Type escape sequence to abort.
Sending 5, 100-byte ICMP Echos to 10.10.3.30, timeout is 2 seconds:
!!!!!
Success rate is 100 percent (5/5), round-trip min/avg/max = 1/1/1 ms
PC1# ping 10.1.1.6
Type escape sequence to abort.
Sending 5, 100-byte ICMP Echos to 10.1.1.6, timeout is 2 seconds:
!!!!!
Success rate is 100 percent (5/5), round-trip min/avg/max = 1/1/2 ms
PC1# ping 10.1.1.5
Type escape sequence to abort.
Sending 5, 100-byte ICMP Echos to 10.1.1.5, timeout is 2 seconds:
!!!!!
Success rate is 100 percent (5/5), round-trip min/avg/max = 1/1/2 ms
All pings executed on PC1 were successful, indicating that R1 uses the correct static routes to remote subnets in the routing table.
PC1 上執行的所有 ping 都成功,顯示 R1 在路由表中使用了正確的靜態路由通往遠端子網路。
Task 3: Demonstrate Static Route Drawbacks
任務 3:展示靜態路由的缺點
Activity
活動
The ping command is used to verify whether there is connectivity between two devices. Additionally, you can use the traceroutecommand to verify the paths that the packet takes between the devices.
ping 指令用來驗證兩台裝置之間是否有連線。此外,你也可以使用 traceroute指令驗證封包在裝置之間所走的路徑。
On PC1, trace the route to PC2:
在 PC1 上,追蹤到 PC2 的路徑:
PC1# traceroute 10.10.2.20
Type escape sequence to abort.
Tracing the route to 10.10.2.20
VRF info: (vrf in name/id, vrf out name/id)
  1 10.10.1.1 1 msec 1 msec 1 msec
  2 10.1.1.9 1 msec 0 msec 1 msec
  3 10.10.2.20 2 msec *  2 msec
The path from PC1 to PC2 goes through R1 and R2.
從 PC1 到 PC2 的路徑會經過 R1 與 R2。
On PC1 trace the route to SRV1:
在 PC1 上追蹤到 SRV1 的路徑:
PC1# traceroute 10.10.3.30
Type escape sequence to abort.
Tracing the route to 10.10.3.30
VRF info: (vrf in name/id, vrf out name/id)
  1 10.10.1.1 1 msec 1 msec 1 msec
  2 10.1.1.1 1 msec 0 msec 0 msec
  3 10.10.3.30 1 msec *  1 msec
The path from PC1 to SRV1 goes through R1 and R3.
從 PC1 到 SRV1 的路徑會經過 R1 與 R3。
It is normal for the middle attempt to the final destination to time out with the traceroute command. The reason for this behavior is because Cisco routers rate limit ICMP Port Unreachable Messages. When a traceroute is started, the router sends out a sequence of UDP datagrams to an invalid port address at the destination host. Three datagrams are sent, each with a TTL value set to 1. As soon as the datagrams hit the first router, they expire and the router responds with an ICMP Time Exceeded Message. For every additional datagram sent, the TTL values increments by 1. When the destination host is reached, it replies with ICMP Port Unreachable messages, because the datagrams are trying to access an invalid port.
使用 traceroute 指令時,最終目的地的中間那次嘗試逾時是正常現象。原因在於 Cisco 路由器會對 ICMP 連接埠無法到達訊息進行速率限制。當開始執行 traceroute 時,路由器會向目的主機的無效連接埠位址送出一系列 UDP 資料包。共送出三個資料包,每個的 TTL 值都設為 1。這些資料包一到達第一台路由器就會過期,該路由器便會回覆 ICMP 逾時訊息。每多送出一個資料包,TTL 值就會遞增 1。當到達目的主機時,由於這些資料包試圖存取無效連接埠,目的主機會回覆 ICMP 連接埠無法到達訊息。
At this point, one of the limitations of static routes should be apparent. They do not scale well. In the lab, there are only six subnets and three routers, with no path being longer than two hops. In this simple environment, nine static routes were required for full connectivity. As the network complexity grows, the number of required static routes grows very fast and quickly becomes unwieldy.
此時,靜態路由的其中一項限制應該已經很明顯了:它們的擴充性不佳。在這個實驗環境中,只有六個子網路和三台路由器,且沒有任何路徑超過兩跳。即使是這麼簡單的環境,也需要九條靜態路由才能達成完整連線。隨著網路複雜度增加,所需的靜態路由數量會快速增加,很快就會變得難以管理。
In the next series of steps, you will experience another limitation of static routes. The static routes do not provide redundancy. You will introduce an interface fault into the network.
在接下來的一系列步驟中,你將體驗靜態路由的另一項限制:靜態路由不提供備援。你將在網路中引入一個介面故障。
On R3, disable the interface Serial1/1, which connects R3 to R1.
在 R3 上,停用連接 R3 與 R1 的 Serial1/1 介面。
On R3, enter these commands:
在 R3 上,輸入下列指令:
R3# configure terminal
R3(config)# interface Serial 1/1
R3(config-if)# shutdown
R3(config-if)# end
R3#
*Oct 15 07:04:28.078: %SYS-5-CONFIG_I: Configured from console by console
R3#
*Oct 15 07:04:29.292: %LINK-5-CHANGED: Interface Serial1/1, changed state to administratively down
*Oct 15 07:04:30.296: %LINEPROTO-5-UPDOWN: Line protocol on Interface Serial1/1, changed state to down
The syslog messages indicate that the state of the Serial1/1 interface changed to "down".
系統紀錄訊息顯示 Serial1/1 介面的狀態已變更為「down」。
Shutting down the Serial1/1 interface on R3 will have effects on R1 and R3. Access the console of R1 and verify that a syslog message is displayed, indicating that the interface Serial1/1 has changed its status to "down". In the lab environment, this status change may take a minute to propagate.
在 R3 上關閉 Serial1/1 介面會對 R1 與 R3 產生影響。存取 R1 的主控台,確認顯示的系統紀錄訊息指出 Serial1/1 介面已將狀態變更為「down」。在實驗環境中,此狀態變更可能需要一分鐘才會傳播。
On R1, observe the syslog messages:
在 R1 上,觀察系統紀錄訊息:
R1#
*Oct 15 07:04:57.975: %LINEPROTO-5-UPDOWN: Line protocol on Interface Serial1/1, changed state to downView the interface status and routing table on R1.
檢視 R1 的介面狀態與路由表。
On R1, enter this command:
在 R1 上,輸入下列指令:
R1# show ip interface brief
Interface                  IP-Address      OK? Method Status                Protocol
Ethernet0/0                10.10.1.1       YES NVRAM  up                    up
Ethernet0/1                unassigned      YES NVRAM  administratively down down
Ethernet0/2                unassigned      YES NVRAM  administratively down down
Ethernet0/3                unassigned      YES NVRAM  administratively down down
Serial1/0                  unassigned      YES NVRAM  administratively down down
Serial1/1                  10.1.1.2        YES NVRAM  up                    down
Serial1/2                  10.1.1.10       YES NVRAM  up                    up
Serial1/3                  unassigned      YES NVRAM  administratively down down
The protocol status of Serial1/1 interface is "down".
Serial1/1 介面的協定狀態為「down」。
On R1 enter this command:
在 R1 上輸入下列指令:
R1# show ip route
Codes: L - local, C - connected, S - static, R - RIP, M - mobile, B - BGP
       D - EIGRP, EX - EIGRP external, O - OSPF, IA - OSPF inter area
       N1 - OSPF NSSA external type 1, N2 - OSPF NSSA external type 2
       E1 - OSPF external type 1, E2 - OSPF external type 2
       i - IS-IS, su - IS-IS summary, L1 - IS-IS level-1, L2 - IS-IS level-2
       ia - IS-IS inter area, * - candidate default, U - per-user static route
       o - ODR, P - periodic downloaded static route, H - NHRP, l - LISP
       + - replicated route, % - next hop override

Gateway of last resort is not set

      10.0.0.0/8 is variably subnetted, 6 subnets, 3 masks
S        10.1.1.4/30 [1/0] via 10.1.1.9
C        10.1.1.8/30 is directly connected, Serial1/2
L        10.1.1.10/32 is directly connected, Serial1/2
C        10.10.1.0/24 is directly connected, Ethernet0/0
L        10.10.1.1/32 is directly connected, Ethernet0/0
S        10.10.2.0/24 [1/0] via 10.1.1.9
There are only two static routes in the routing table. With the Serial1/1 interface being down, there is no path to the 10.1.1.1 IPv4 address on the 10.1.1.0/30 subnet. Therefore, the route to 10.10.3.0/24 that uses the 10.1.1.1 IPv4 address as the next hop is invalid and has been removed from the routing table.
路由表中只剩下兩條靜態路由。由於 Serial1/1 介面處於關閉狀態,沒有路徑可到達 10.1.1.0/30 子網路上的 10.1.1.1 IPv4 位址。因此,使用 10.1.1.1 IPv4 位址作為下一跳、通往 10.10.3.0/24 的路由已失效,並已從路由表中移除。
Note that the ip route command for this static route still exists in the configuration.
請注意,這條靜態路由的 ip route 指令仍然存在於設定中。
Explore the connectivity from the perspective of PC1. Access the console of PC1 and attempt a pingand a tracerouteto 10.10.3.30 IPv4 address that belongs to SRV1.
從 PC1 的角度探索連線情況。存取 PC1 的主控台,嘗試對屬於 SRV1 的 10.10.3.30 IPv4 位址執行 ping與 traceroute。
On PC1, enter this command:
在 PC1 上,輸入下列指令:
PC1# ping 10.10.3.30
Type escape sequence to abort.
Sending 5, 100-byte ICMP Echos to 10.10.3.30, timeout is 2 seconds:
U.U.U
Success rate is 0 percent (0/5)
The ping is not successful. The "U" characters indicate that a router in the path (in this case, R1) is sending an ICMP unreachable message back to PC1.
ping 不成功。「U」字元表示路徑上的某台路由器(在此為 R1)向 PC1 傳回了 ICMP 無法到達訊息。
PC1# traceroute 10.10.3.30
Type escape sequence to abort.
Tracing the route to 10.10.3.30
VRF info: (vrf in name/id, vrf out name/id)
  1 10.10.1.1 1 msec 1 msec 0 msec
  2 10.10.1.1 !H  *  !H
The path gets to R1 (10.10.1.1), but then gets stuck.
路徑到達 R1(10.10.1.1)後就卡住了。
Repair the interface fault by returning to R3 and enabling Serial1/1.
返回 R3 並啟用 Serial1/1,以修復介面故障。
On R3, enter these commands:
在 R3 上,輸入下列指令:
R3# configure terminal
Enter configuration commands, one per line.  End with CNTL/Z.
R3(config)# interface Serial 1/1
R3(config-if)# no shutdown
R3(config-if)# end
R3#
*Oct 15 07:13:12.022: %LINK-3-UPDOWN: Interface Serial1/1, changed state to up
R3#
*Oct 15 07:13:12.747: %SYS-5-CONFIG_I: Configured from console by console
*Oct 15 07:13:13.027: %LINEPROTO-5-UPDOWN: Line protocol on Interface Serial1/1, changed state to up
The syslog messages indicate that the state of the Serial1/1 interface changed to "up".
系統紀錄訊息顯示 Serial1/1 介面的狀態已變更為「up」。
Return to the console of R1 and verify that the display of the syslog message is indicating that Serial1/1 interface has changed back to the "up" state.
返回 R1 的主控台,確認顯示的系統紀錄訊息指出 Serial1/1 介面已恢復為「up」狀態。
On R1, observe the syslog messages:
在 R1 上,觀察系統紀錄訊息:
R1#
*Oct 15 07:13:18.148: %LINEPROTO-5-UPDOWN: Line protocol on Interface Serial1/1, changed state to up
A syslog message indicates that the state of the Serial1/1 interface is "up".
系統紀錄訊息顯示 Serial1/1 介面的狀態為「up」。
The real proof comes by verifying end-to-end connectivity. Return to the console of PC1 and execute a ping command and a traceroute command to SRV1.
真正的證明來自驗證端對端連線。返回 PC1 的主控台,對 SRV1 執行 ping 指令與 traceroute 指令。
On PC1, enter these commands:
在 PC1 上,輸入下列指令:
PC1# ping 10.10.3.30
Type escape sequence to abort.
Sending 5, 100-byte ICMP Echos to 10.10.3.30, timeout is 2 seconds:
!!!!!
Success rate is 100 percent (5/5), round-trip min/avg/max = 10/10/11 ms
PC1# traceroute 10.10.3.30
Type escape sequence to abort.
Tracing the route to 10.10.3.30
VRF info: (vrf in name/id, vrf out name/id)
  1 10.10.1.1 1 msec 1 msec 1 msec  2 10.1.1.1 10 msec 10 msec 9 msec
  3 10.10.3.30 11 msec *  9 msec
Because there is direct connectivity between R1 and R3, the ping from PC1 to SRV1 is successful again and the path is through R1 and R3.
由於 R1 與 R3 之間已恢復直接連線,PC1 到 SRV1 的 ping 再次成功,且路徑經過 R1 與 R3。
Task 4: Configure and Verify the Backup Static Route
任務 4:設定並驗證備援靜態路由
Activity
活動
What has been demonstrated so far in this activity covers the typical usage of static routes. The next series of steps will show an unconventional use of static routes. This task should be considered an academic exercise; it is only feasible because of the simplicity of the lab environment. Add more routers or subnets into the mix and this methodology would quickly become unwieldy.
到目前為止,本活動所展示的是靜態路由的典型用法。接下來的一系列步驟將展示靜態路由的非典型用法。這項任務應視為學術性練習,僅因為實驗環境的簡單性才可行。若加入更多路由器或子網路,這種做法很快就會變得難以管理。
Administrative distance is a property that is used to distinguish the trustworthiness of different routing protocols. Cisco IOS routers prefer routes with a lower administrative distance. By default, static routes have an administrative distance of 1, which all but guarantees that they will be used in the routing table.
管理距離是用來區分不同路由協定可信度的屬性。Cisco IOS 路由器偏好管理距離較低的路由。預設情況下,靜態路由的管理距離為 1,這幾乎能確保它們會被使用在路由表中。
It is optional to specify a different administrative distance on static routes. In this next series of steps, you will define a set of backup (floating) static routes with an administrative distance of 2. The only way that these routes will end up in the routing table is if one of the routes with an administrative distance of 1 becomes unavailable. You will also verify the behavior when an interface fails in the new configuration.
你可以選擇為靜態路由指定不同的管理距離。在接下來的一系列步驟中,你將定義一組管理距離為 2 的備援(浮動)靜態路由。只有當某條管理距離為 1 的路由變得無法使用時,這些路由才會出現在路由表中。你也將驗證在新設定下介面故障時的行為。
Access the console of R1 and add three additional static routes. The new routes will specify the same remote destination networks as in the existing static routes but they will also specify a next hop on the alternate peer router and use an administrative distance of 2.
存取 R1 的主控台,新增三條額外的靜態路由。這些新路由指定的遠端目的網路與現有靜態路由相同,但會指定通往另一個對等路由器的下一跳,並使用管理距離 2。
On R1, enter the following commands:
在 R1 上,輸入下列指令:
R1# configure terminal
R1(config)# ip route 10.10.2.0 255.255.255.0 10.1.1.1 2
R1(config)# ip route 10.10.3.0 255.255.255.0 10.1.1.9 2
R1(config)# ip route 10.1.1.4 255.255.255.252 10.1.1.1 2
R1(config)# end
R1#
The last parameter in the command represents the administrative distance for the static route. All three static routes will have administrative distance of 2, which is worse than previously configured static routes to the same destination networks using the default administrative distance of 1.
指令中的最後一個參數代表該靜態路由的管理距離。這三條靜態路由的管理距離都是 2,比先前設定通往相同目的網路、使用預設管理距離 1 的靜態路由更差(數值愈大優先度愈低)。
Verify that now there are six static routes in the configuration, two for each of the remote networks. The second route to each remote network specifies an alternate next hop and an administrative distance of 2.
驗證現在設定中共有六條靜態路由,每個遠端網路各兩條。每個遠端網路的第二條路由指定了另一個下一跳,並使用管理距離 2。
On R1, enter the following command:
在 R1 上,輸入下列指令:
R1# show running-config | include route
ip route 10.1.1.4 255.255.255.252 10.1.1.9
ip route 10.1.1.4 255.255.255.252 10.1.1.1 2
ip route 10.10.2.0 255.255.255.0 10.1.1.9
ip route 10.10.2.0 255.255.255.0 10.1.1.1 2
ip route 10.10.3.0 255.255.255.0 10.1.1.1
ip route 10.10.3.0 255.255.255.0 10.1.1.9 2
Now, R1 has two static routes per remote network—one with an administrative distance of 1 that will serve as a primary route and another with an administrative distance of 2, serving as a backup if the primary route fails.
現在,R1 針對每個遠端網路都有兩條靜態路由,一條管理距離為 1,作為主要路由,另一條管理距離為 2,作為主要路由失效時的備援。
Verify that only three of the static routes appear in the routing table. Only the routes that have the default administrative distance of 1 are selected for the routing table.
驗證路由表中只出現三條靜態路由。只有具有預設管理距離 1 的路由會被選入路由表。
On R1, enter this command:
在 R1 上,輸入下列指令:
R1# show ip route static
Codes: L - local, C - connected, S - static, R - RIP, M - mobile, B - BGP
       D - EIGRP, EX - EIGRP external, O - OSPF, IA - OSPF inter area
       N1 - OSPF NSSA external type 1, N2 - OSPF NSSA external type 2
       E1 - OSPF external type 1, E2 - OSPF external type 2
       i - IS-IS, su - IS-IS summary, L1 - IS-IS level-1, L2 - IS-IS level-2
       ia - IS-IS inter area, * - candidate default, U - per-user static route
       o - ODR, P - periodic downloaded static route, H - NHRP, l - LISP
       + - replicated route, % - next hop override

Gateway of last resort is not set

      10.0.0.0/8 is variably subnetted, 9 subnets, 3 masks
S        10.1.1.4/30 [1/0] via 10.1.1.9
S        10.10.2.0/24 [1/0] via 10.1.1.9
S        10.10.3.0/24 [1/0] via 10.1.1.1
The values that you see within the brackets are [Administrative Distance / Metric]. These three routes all have an administrative distance of 1. The metric is used by routing protocols to measure paths; it is always 0 for static routes.
你在括號中看到的值是[管理距離/度量值]。這三條路由的管理距離皆為 1。度量值是路由協定用來衡量路徑的依據,靜態路由的度量值一律為 0。
Repeat the respective configuration of static routes on R2 and R3.
在 R2 與 R3 上重複相應的靜態路由設定。
On R2, enter these commands:
在 R2 上,輸入下列指令:
R2# configure terminal
R2(config)# ip route 10.10.1.0 255.255.255.0 10.1.1.5 2
R2(config)# ip route 10.10.3.0 255.255.255.0 10.1.1.10 2
R2(config)# ip route 10.1.1.0 255.255.255.252 10.1.1.5 2
R2(config)# end
R2#
On R3, enter these commands:
在 R3 上,輸入下列指令:
R3# configure terminal
R3(config)# ip route 10.10.1.0 255.255.255.0 10.1.1.6 2
R3(config)# ip route 10.10.2.0 255.255.255.0 10.1.1.2 2
R3(config)# ip route 10.1.1.8 255.255.255.252 10.1.1.6 2
R3(config)# end
R3#Repeat the fault experiment that was performed earlier in the discovery by disabling the Serial1/1 interface on R3.
重複先前在 Discovery 中執行過的故障實驗,停用 R3 上的 Serial1/1 介面。
On R3, enter these commands:
在 R3 上,輸入下列指令:
R3# configure terminal
R3(config)# interface Serial 1/1
R3(config-if)# shutdown
R3(config-if)# end
R3#
*Oct 15 07:29:34.297: %SYS-5-CONFIG_I: Configured from console by console
*Oct 15 07:29:35.080: %LINK-5-CHANGED: Interface Serial1/1, changed state to administratively down
R3#
*Oct 15 07:29:36.084: %LINEPROTO-5-UPDOWN: Line protocol on Interface Serial1/1, changed state to down
The syslog messages indicate that the state of the Serial1/1 interface changed to "down".
系統紀錄訊息顯示 Serial1/1 介面的狀態已變更為「down」。
Access the console of R1 to verify that the display of the syslog message indicates that the Serial1/1 interface of R1 has "changed state to down".
存取 R1 的主控台,確認顯示的系統紀錄訊息指出 R1 的 Serial1/1 介面「狀態已變更為 down」。
On R1, observe the syslog messages:
在 R1 上,觀察系統紀錄訊息:
R1#
*Oct 15 07:29:58.519: %LINEPROTO-5-UPDOWN: Line protocol on Interface Serial1/1, changed state to down
The syslog messages indicate that the state of the Serial1/1 interface changed to "down".
系統紀錄訊息顯示 Serial1/1 介面的狀態已變更為「down」。
View the routing table on R1.
檢視 R1 的路由表。
On R1, enter this command:
在 R1 上,輸入下列指令:
R1# show ip route
Codes: L - local, C - connected, S - static, R - RIP, M - mobile, B - BGP
       D - EIGRP, EX - EIGRP external, O - OSPF, IA - OSPF inter area
       N1 - OSPF NSSA external type 1, N2 - OSPF NSSA external type 2
       E1 - OSPF external type 1, E2 - OSPF external type 2
       i - IS-IS, su - IS-IS summary, L1 - IS-IS level-1, L2 - IS-IS level-2
       ia - IS-IS inter area, * - candidate default, U - per-user static route
       o - ODR, P - periodic downloaded static route, H - NHRP, l - LISP
       + - replicated route, % - next hop override

Gateway of last resort is not set

      10.0.0.0/8 is variably subnetted, 7 subnets, 3 masks
S        10.1.1.4/30 [1/0] via 10.1.1.9
C        10.1.1.8/30 is directly connected, Serial1/2
L        10.1.1.10/32 is directly connected, Serial1/2
C        10.10.1.0/24 is directly connected, Ethernet0/0
L        10.10.1.1/32 is directly connected, Ethernet0/0
S        10.10.2.0/24 [1/0] via 10.1.1.9
S        10.10.3.0/24 [2/0] via 10.1.1.9
There is a route to 10.10.3.0/24 network. The route through R2 (10.1.1.9) with an administrative distance of 2 replaced the route through R3 (10.1.1.1) with an administrative distance of 1 when the connection to the 10.1.1.0/30 network was lost.
現在有一條通往 10.10.3.0/24 網路的路由。當到 10.1.1.0/30 網路的連線中斷時,經由 R2(10.1.1.9)、管理距離為 2 的路由取代了經由 R3(10.1.1.1)、管理距離為 1 的路由。
Access the console of PC1 and verify connectivity between PC1 and SRV1 using the ping and traceroute commands.
存取 PC1 的主控台,使用 ping 與 traceroute 指令驗證 PC1 與 SRV1 之間的連線。
On PC1, enter these commands:
在 PC1 上,輸入下列指令:
PC1# ping 10.10.3.30
Type escape sequence to abort.
Sending 5, 100-byte ICMP Echos to 10.10.3.30, timeout is 2 seconds:
!!!!!
Success rate is 100 percent (5/5), round-trip min/avg/max = 17/17/18 ms

PC1# traceroute 10.10.3.30
Type escape sequence to abort.
Tracing the route to 10.10.3.30
VRF info: (vrf in name/id, vrf out name/id)
  1 10.10.1.1 1 msec 0 msec 1 msec
  2 10.1.1.9 9 msec 9 msec 9 msec
  3 10.1.1.5 17 msec 18 msec 17 msec
  4 10.10.3.30 15 msec *  18 msec
The connectivity between PC1 and SRV1 remains, even with the loss of the link between R1 and R3. However, the path is now longer and traverses R1, R2, and R3.
即使 R1 與 R3 之間的連結中斷,PC1 與 SRV1 之間的連線依然存在。不過,現在的路徑變長了,會經過 R1、R2 與 R3。
Return to R3 to repair the interface fault.
返回 R3 修復介面故障。
On R3, enter these commands:
在 R3 上,輸入下列指令:
R3# configure terminal
R3(config)# interface Serial 1/1
R3(config-if)# no shutdown
R3(config-if)# end
R3#
*Oct 15 07:34:30.570: %SYS-5-CONFIG_I: Configured from console by console
R3#
*Oct 15 07:34:30.968: %LINK-3-UPDOWN: Interface Serial1/1, changed state to up
*Oct 15 07:34:31.972: %LINEPROTO-5-UPDOWN: Line protocol on Interface Serial1/1, changed state to up
The syslog messages indicate that the state of the Serial1/1 interface changed to "up".
系統紀錄訊息顯示 Serial1/1 介面的狀態已變更為「up」。
Access the console of R1 and verify the display of the syslog message indicating that its interface Serial1/1 returns to an "up" state.
存取 R1 的主控台,確認顯示的系統紀錄訊息指出其 Serial1/1 介面恢復為「up」狀態。
On R1, observe the syslog messages:
在 R1 上,觀察系統紀錄訊息:
R1#
*Oct 15 07:34:38.628: %LINEPROTO-5-UPDOWN: Line protocol on Interface Serial1/1, changed state to up
The syslog messages indicate that the state of the Serial1/1 interface changed to "up".
系統紀錄訊息顯示 Serial1/1 介面的狀態已變更為「up」。
View the routing table on R1.
檢視 R1 的路由表。
On R1, enter this command:
在 R1 上,輸入下列指令:
R1# show ip route
Codes: L - local, C - connected, S - static, R - RIP, M - mobile, B - BGP
       D - EIGRP, EX - EIGRP external, O - OSPF, IA - OSPF inter area
       N1 - OSPF NSSA external type 1, N2 - OSPF NSSA external type 2
       E1 - OSPF external type 1, E2 - OSPF external type 2
       i - IS-IS, su - IS-IS summary, L1 - IS-IS level-1, L2 - IS-IS level-2
       ia - IS-IS inter area, * - candidate default, U - per-user static route
       o - ODR, P - periodic downloaded static route, H - NHRP, l - LISP
       + - replicated route, % - next hop override

Gateway of last resort is not set

      10.0.0.0/8 is variably subnetted, 9 subnets, 3 masks
C        10.1.1.0/30 is directly connected, Serial1/1
L        10.1.1.2/32 is directly connected, Serial1/1
S        10.1.1.4/30 [1/0] via 10.1.1.9
C        10.1.1.8/30 is directly connected, Serial1/2
L        10.1.1.10/32 is directly connected, Serial1/2
C        10.10.1.0/24 is directly connected, Ethernet0/0
L        10.10.1.1/32 is directly connected, Ethernet0/0
S        10.10.2.0/24 [1/0] via 10.1.1.9
S        10.10.3.0/24 [1/0] via 10.1.1.1
The original route to 10.10.3.0/24 network using R3 as the next hop and with an administrative distance of 1 has returned to the routing table.
原本以 R3 作為下一跳、管理距離為 1、通往 10.10.3.0/24 網路的路由已恢復到路由表中。
Task 5: Configure and Verify the Default Route
任務 5:設定並驗證預設路由
Activity
活動
A default route is a route to the network 0.0.0.0 with the subnet mask 0.0.0.0. Default routes can be defined statically. Default routes are most commonly used when there is a hierarchy in the network. For example, to get from a branch office network to the headquarters network (and the rest of the world) or to get from the corporate network to the internet.
預設路由是一條通往網路 0.0.0.0、子網路遮罩為 0.0.0.0 的路由。預設路由可以靜態定義。預設路由最常用於網路具有階層結構的情況,例如從分公司網路連往總部網路(以及世界其他地方),或從企業網路連往網際網路。
The lab environment is not hierarchical. In fact, it is perfectly symmetrical. So the use of a default route on R1, R2, or R3 is not very practical but it can be enlightening to explore the behavior of a default route within the lab environment.
本實驗環境並非階層式的,實際上它是完全對稱的。因此在 R1、R2 或 R3 上使用預設路由並不太實用,但探索預設路由在此實驗環境中的行為仍有助於理解。
Access R1 and remove all the static routes that are configured. Unfortunately, removing those routes is a tedious operation. Be sure to make good use of the Cisco IOS command history feature to ease the burden.
存取 R1 並移除所有已設定的靜態路由。可惜的是,移除這些路由是一項繁瑣的操作,請善用 Cisco IOS 的指令歷史紀錄功能以減輕負擔。
On R1, enter these commands:
在 R1 上,輸入下列指令:
R1# configure terminal
R1(config)# no ip route 10.1.1.4 255.255.255.252 10.1.1.9
R1(config)# no ip route 10.1.1.4 255.255.255.252 10.1.1.1 2
R1(config)# no ip route 10.10.2.0 255.255.255.0 10.1.1.9
R1(config)# no ip route 10.10.2.0 255.255.255.0 10.1.1.1 2
R1(config)# no ip route 10.10.3.0 255.255.255.0 10.1.1.1
R1(config)# no ip route 10.10.3.0 255.255.255.0 10.1.1.9 2
R1(config)# end
R1#Verify that there are no route commands left in the configuration and that only local and connected routes appear in the routing table.
驗證設定中已無任何 route 指令殘留,且路由表中只出現本地與直接連接路由。
On R1, enter these commands:
在 R1 上,輸入下列指令:
R1# show running-config | include route
R1# show ip route
Codes: L - local, C - connected, S - static, R - RIP, M - mobile, B - BGP
       D - EIGRP, EX - EIGRP external, O - OSPF, IA - OSPF inter area
       N1 - OSPF NSSA external type 1, N2 - OSPF NSSA external type 2
       E1 - OSPF external type 1, E2 - OSPF external type 2
       i - IS-IS, su - IS-IS summary, L1 - IS-IS level-1, L2 - IS-IS level-2
       ia - IS-IS inter area, * - candidate default, U - per-user static route
       o - ODR, P - periodic downloaded static route, H - NHRP, l - LISP
       + - replicated route, % - next hop override

Gateway of last resort is not set

      10.0.0.0/8 is variably subnetted, 6 subnets, 3 masks
C        10.1.1.0/30 is directly connected, Serial1/1
L        10.1.1.2/32 is directly connected, Serial1/1
C        10.1.1.8/30 is directly connected, Serial1/2
L        10.1.1.10/32 is directly connected, Serial1/2
C        10.10.1.0/24 is directly connected, Ethernet0/0
L        10.10.1.1/32 is directly connected, Ethernet0/0
As you notice, the output from both "show" commands verifies that there are no static routes left on R1.
如你所見,兩個「show」指令的輸出都驗證了 R1 上已無任何靜態路由殘留。
Configure a default route on R1 using 10.1.1.1 (Serial1/1 on R3) as the next-hop.
在 R1 上設定一條預設路由,使用 10.1.1.1(R3 上的 Serial1/1)作為下一跳。
On R1, enter these commands:
在 R1 上,輸入下列指令:
R1# configure terminal
R1(config)# ip route 0.0.0.0 0.0.0.0 10.1.1.1
R1(config)# end
R1#Verify that this route is the only route in the running configuration and that there is a default route in the routing table.
驗證這條路由是執行中設定中唯一的路由,且路由表中有一條預設路由。
On R1, enter these commands:
在 R1 上,輸入下列指令:
R1# show running-config | include route
ip route 0.0.0.0 0.0.0.0 10.1.1.1

R1# show ip route
Codes: L - local, C - connected, S - static, R - RIP, M - mobile, B - BGP
       D - EIGRP, EX - EIGRP external, O - OSPF, IA - OSPF inter area
       N1 - OSPF NSSA external type 1, N2 - OSPF NSSA external type 2
       E1 - OSPF external type 1, E2 - OSPF external type 2
       i - IS-IS, su - IS-IS summary, L1 - IS-IS level-1, L2 - IS-IS level-2
       ia - IS-IS inter area, * - candidate default, U - per-user static route
       o - ODR, P - periodic downloaded static route, H - NHRP, l - LISP
       + - replicated route, % - next hop override

Gateway of last resort is 10.1.1.1 to network 0.0.0.0

S*    0.0.0.0/0 [1/0] via 10.1.1.1
      10.0.0.0/8 is variably subnetted, 6 subnets, 3 masks
C        10.1.1.0/30 is directly connected, Serial1/1
L        10.1.1.2/32 is directly connected, Serial1/1
C        10.1.1.8/30 is directly connected, Serial1/2
L        10.1.1.10/32 is directly connected, Serial1/2
C        10.10.1.0/24 is directly connected, Ethernet0/0
L        10.10.1.1/32 is directly connected, Ethernet0/0
The output indicates that there is only one static default route in the routing table of R1 pointing to 10.1.1.1 (Serial1/1 on R3) as next-hop.
輸出顯示 R1 的路由表中只有一條靜態預設路由,指向以 10.1.1.1(R3 上的 Serial1/1)作為下一跳。
Verify the connectivity between PC1 and other IPv4 addresses in the network by using the ping command.
使用 ping 指令驗證 PC1 與網路中其他 IPv4 位址之間的連線。
On PC1, enter these commands:
在 PC1 上,輸入下列指令:
PC1# ping 10.10.3.30
Type escape sequence to abort.
Sending 5, 100-byte ICMP Echos to 10.10.3.30, timeout is 2 seconds:
!!!!!
Success rate is 100 percent (5/5), round-trip min/avg/max = 10/10/10 ms
PC1# ping 10.10.2.20
Type escape sequence to abort.
Sending 5, 100-byte ICMP Echos to 10.10.2.20, timeout is 2 seconds:
!!!!!
Success rate is 100 percent (5/5), round-trip min/avg/max = 12/13/15 ms
PC1# ping 10.1.1.9
Type escape sequence to abort.
Sending 5, 100-byte ICMP Echos to 10.1.1.9, timeout is 2 seconds:
!!!!!
Success rate is 100 percent (5/5), round-trip min/avg/max = 8/9/10 ms
Replacing specific static routes in the configuration of R1 with a default route to R3 does provide connectivity throughout the network, as long as there are no failed interfaces.
在 R1 的設定中,將特定的靜態路由改為指向 R3 的預設路由,只要沒有介面故障,確實能為整個網路提供連線。
Examine the path from PC1 to PC2 using the traceroute command.
使用 traceroute 指令檢查從 PC1 到 PC2 的路徑。
On PC1, enter this command:
在 PC1 上,輸入下列指令:
PC1# traceroute 10.10.2.20
Type escape sequence to abort.
Tracing the route to 10.10.2.20
VRF info: (vrf in name/id, vrf out name/id)
  1 10.10.1.1 1 msec 0 msec 1 msec
  2 10.1.1.1 9 msec 5 msec 9 msec
  3 10.1.1.6 13 msec 13 msec 13 msec
  4 10.10.2.20 14 msec *  15 msec
R1 is the first hop in the path. R1 no longer has an explicit and efficient static route to 10.10.2.0/24 network, therefore it uses its default route and forwards this traffic to R3. R3 has a static route to the 10.10.2.0/24 network via R2. Therefore, the path from PC1 to PC2 goes through R1, R3, and then R2.
R1 是路徑上的第一跳。R1 已不再有明確且高效的靜態路由通往 10.10.2.0/24 網路,因此它使用預設路由,將此流量轉送給 R3。R3 有一條經由 R2 通往 10.10.2.0/24 網路的靜態路由。因此,從 PC1 到 PC2 的路徑會經過 R1、R3,然後是 R2。
Examine the path from PC1 to 10.1.1.9 (Serial1/2 on R2) using the traceroute command.
使用 traceroute 指令檢查從 PC1 到 10.1.1.9(R2 上的 Serial1/2)的路徑。
On PC1, enter this command:
在 PC1 上,輸入下列指令:
PC1# traceroute 10.1.1.9
Type escape sequence to abort.
Tracing the route to 10.1.1.9
VRF info: (vrf in name/id, vrf out name/id)
  1 10.10.1.1 0 msec 0 msec 0 msec
  2 10.1.1.9 11 msec *  9 msec
R1 did not need to use its default route to reach 10.1.1.9. R1 has a directly connected route to 10.1.1.8/30 network in its routing table. This specific route is preferred over the default route and is used in this case.
R1 不需要使用預設路由就能到達 10.1.1.9。R1 的路由表中有一條直接連接通往 10.1.1.8/30 網路的路由。在這種情況下,這條特定路由優先於預設路由並被使用。
You have examined connectivity and the path from PC1 to PC2. Now, access the console of PC2, and examine the connectivity and the path from PC2 to PC1 using the ping and traceroute commands.
你已經檢查過從 PC1 到 PC2 的連線與路徑。現在,存取 PC2 的主控台,使用 ping 與 traceroute 指令檢查從 PC2 到 PC1 的連線與路徑。
On PC2, enter this command:
在 PC2 上,輸入下列指令:
PC2# ping 10.10.1.10
Type escape sequence to abort.
Sending 5, 100-byte ICMP Echos to 10.10.1.10, timeout is 2 seconds:
!!!!!
Success rate is 100 percent (5/5), round-trip min/avg/max = 12/13/14 ms
The explicit static routes to 10.10.1.0/24 network that are defined on R2 and R3 will sustain connectivity to that subnet within the lab.
在 R2 與 R3 上定義的、通往 10.10.1.0/24 網路的明確靜態路由,將維持該實驗環境中此子網路的連線。
On PC2, enter this command:
在 PC2 上,輸入下列指令:
PC2# traceroute 10.10.1.10
Type escape sequence to abort.
Tracing the route to 10.10.1.10
VRF info: (vrf in name/id, vrf out name/id)
  1 10.10.2.1 1 msec 0 msec 0 msec
  2 10.1.1.10 13 msec 14 msec 13 msec
  3 10.10.1.10 15 msec *  13 msec
R2 is the first hop in this path, and R2 has an explicit and optimized static route to 10.10.1.0/24 network that uses R1 as the next hop. Therefore, the path from PC2 to PC1 traverses R2 and then R1. In this case, R3 is not involved.
R2 是這條路徑上的第一跳,且 R2 有一條明確且經過最佳化、以 R1 作為下一跳、通往 10.10.1.0/24 網路的靜態路由。因此,從 PC2 到 PC1 的路徑會經過 R2,然後是 R1。在這種情況下,R3 並未參與其中。
Contrast to this situation, the path that was previously displayed for PC1 to PC2. That path required the default route on R1. The path traversed R1, R3, and then R2.
與此情況相對比,先前顯示的從 PC1 到 PC2 的路徑則需要用到 R1 上的預設路由,該路徑經過 R1、R3,然後是 R2。
When the path from Host A to Host B is not simply the reverse of the path that is taken from Host B to Host A, it is called asymmetric routing. Asymmetric routing is generally an undesirable behavior.
當從主機 A 到主機 B 的路徑與從主機 B 到主機 A 的路徑並非單純互為反向時,這稱為不對稱路由。不對稱路由通常是不理想的行為。
At this point, you have experimented extensively with static routes. You have configured typical static routes and redundant static routes and a default static route. In each case, you have seen how to verify the status of the configuration and the routing table. You have also examined the packet-forwarding behavior in each case, including scenarios where there is an interface fault in place. Feel free to continue to independently explore the configuration and function of static routes in the lab environment.
此時,你已廣泛實驗了靜態路由,設定過典型的靜態路由、備援靜態路由,以及靜態預設路由。在每種情況下,你都學會如何驗證設定與路由表的狀態,也檢查了每種情況下的封包轉送行為,包括介面發生故障的情境。歡迎繼續自行探索此實驗環境中靜態路由的設定與功能。