An IPS is a system that performs deep analysis of network traffic, searching for signs of suspicious or malicious behavior. If it detects such behavior, the IPS can take protective action. Because it can perform deep packet analysis, an IPS can complement a firewall by blocking attacks that would normally pass through a traditional firewall device. For example, an IPS can detect and block a wide range of malicious files and behavior, including some botnet attacks, malware, and application abuse.
入侵防禦系統(IPS)是一種對網路流量進行深度分析、以搜尋可疑或惡意行為跡象的系統。若偵測到此類行為,IPS 可採取防護行動。由於能執行深度封包分析,IPS 可與防火牆互補,攔截原本會通過傳統防火牆裝置的攻擊。舉例來說,IPS 可偵測並封鎖多種惡意檔案與行為,包括部分殭屍網路(botnet)攻擊、惡意軟體及應用程式濫用。
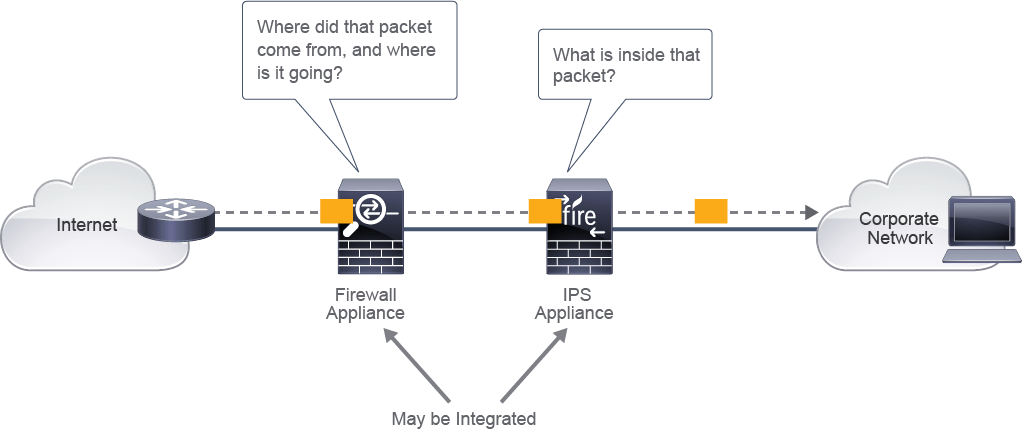
The figure below shows a firewall and an IPS working in conjunction to defend a network. This example shows a network-based IPS, in which IPS devices are deployed at designated network points to address network attacks regardless of the location of the attack target. Network-based IPS technology is deployed in a sensor, which can be a dedicated appliance or a module that is installed in another network device. There are also host-based IPSs that only detect attacks that occur on the hosts on which they are installed.
下圖顯示防火牆與 IPS 協同運作以防護網路。此範例展示的是網路型 IPS,IPS 裝置部署於指定的網路節點,無論攻擊目標位於何處都能因應網路攻擊。網路型 IPS 技術部署於感測器(sensor)中,可以是專用設備,也可以是安裝在其他網路裝置中的模組。此外還有主機型 IPS,只會偵測發生在安裝該系統之主機上的攻擊。
Several methods of traffic inspection are used in various IPS systems:
各種 IPS 系統採用了多種流量檢測方法:
- Signature-based inspection: A signature-based IPS examines the packet headers and data payloads in network traffic and compares the data against a database of known attack signatures. The database must be continually updated to remain effective. A signature might be a sequence or a string of bytes in a certain context. Signature-based inspection is sometimes referred to as rule-based or pattern-matching inspection.簽章式檢測:簽章式 IPS 會檢查網路流量中的封包標頭與資料承載(payload),並將資料與已知攻擊簽章資料庫進行比對。此資料庫必須持續更新才能保持有效。簽章可能是特定情境下的一段位元組序列或字串。簽章式檢測有時也稱為規則式或模式比對式檢測。
- Anomaly-based inspection: Anomaly-based network IPS devices observe network traffic and act if a network event outside normal network behavior is detected.異常-式檢測:異常式網路 IPS 裝置會觀察網路流量,並在偵測到偏離正常網路行為的網路事件時採取行動。
There are two types of anomaly-based network IPS systems:
異常式網路 IPS 系統有兩種類型:
- Statistical anomaly detection (network behavior analysis): Observes network traffic over time and builds a statistical profile of normal traffic behavior based on communication patterns, traffic rate, mixture of protocols, and traffic volume. After a normal profile has been established, statistical anomaly detection systems detect or prevent activity that violates the normal profile.統計異常偵測(網路行為分析):長時間觀察網路流量,並根據通訊模式、流量速率、協定組成及流量大小,建立正常流量行為的統計輪廓。建立正常輪廓後,統計異常偵測系統即可偵測或防止違反該正常輪廓的活動。
- Protocol verification: Observes network traffic and compares network, transport, and application layer protocols that are used inside network traffic protocol to standards. If a deviation from standard-based protocol behavior is detected (such as a malformed IP packet), the system can take appropriate action.協定驗證:觀察網路流量,並將流量中所使用的網路層、傳輸層與應用層協定與標準進行比較。若偵測到偏離標準協定行為的情況(例如格式錯誤的 IP 封包),系統即可採取適當行動。
- Policy-based inspection: A policy-based IPS analyzes network traffic and takes action if it detects a network event outside a configured traffic policy.政策式檢測:政策式 IPS 會分析網路流量,並在偵測到偏離已設定流量政策的網路事件時採取行動。
Modern next-generation IPSs (NGIPSs) combine the benefits of these inspection methods. They utilize technology such as traffic normalization and decode protocols to counter evasive attacker techniques and to improve efficacy. They also utilize newer and more sophisticated technologies such as reputation, context awareness, event correlation, and cloud-based services to provide more robust and flexible protection.
現代次世代 IPS(NGIPS)結合了上述多種檢測方法的優點。它們運用流量正規化與協定解碼等技術,以對抗攻擊者的規避手法並提升效能。它們也運用信譽評等、情境感知、事件關聯及雲端服務等更新且更精密的技術,提供更強大、更具彈性的防護。