An ACL is a sequential list of permit or deny statements, known as access control entries (ACEs) or ACL statements. When network traffic is processed by an ACL, the device compares packet header information against the ACE matching criteria. ACL statements are evaluated one by one, in a sequential order from the first to the last, to determine if the packet matches one of them. This process is called packet filtering.
ACL 是一連串允許或拒絕陳述式,稱為存取控制項目(ACE)或 ACL 陳述式。當網路流量被 ACL 處理時,裝置會將封包標頭資訊與 ACE 的比對條件進行比較。ACL 陳述式會依序逐一評估,從第一條到最後一條,以判斷封包是否符合其中之一,這個過程稱為封包過濾。
IP packet filtering can be based only on information found in Open Systems Interconnection (OSI) Layer 3 header or on both Layer 3 and Layer 4 header information. A device extracts the relevant information from the packet headers and compares the information to the ACE matching rule.
IP 封包過濾可以只根據開放系統互連(OSI)第 3 層標頭中的資訊,也可以同時根據第 3 層與第 4 層標頭資訊。裝置會從封包標頭中擷取相關資訊,並與 ACE 比對規則進行比較。
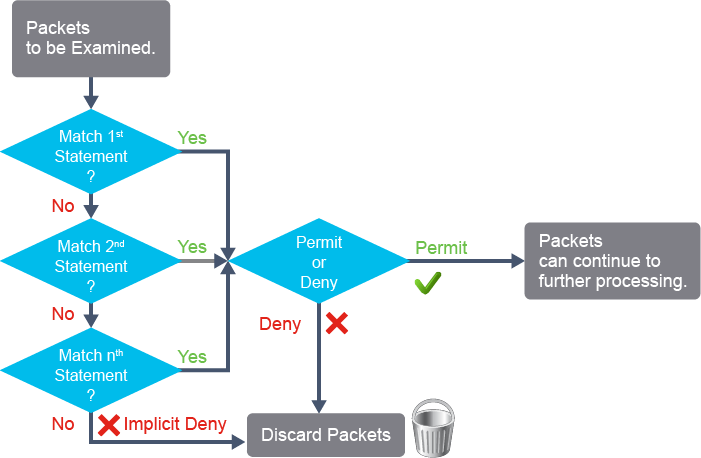
ACL statements operate in a sequential, logical order. When a packet matches a rule in the statement, the corresponding action is executed, and ACL processing stops. For instance, in an access list with 15 statements, if a packet matches the first statement, the packet is not evaluated against other 14 statements. Only the instruction of the first matching statement is executed, even if the packet would match subsequent ones.
ACL 陳述式以循序、邏輯的順序運作。當封包符合陳述式中的規則時,就會執行對應的動作,且 ACL 處理隨即停止。舉例來說,在一個含有 15 條陳述式的存取清單中,若封包符合第一條陳述式,該封包就不會再與其他 14 條陳述式進行評估。即使封包也可能符合後續的陳述式,也只會執行第一條符合陳述式的指令。
The matching process continues until the end of the list. If a match is not found, the packet is processed with a deny action and dropped. The last statement of an ACL is always an implicit deny. This statement is automatically inserted at the end of each ACL even though you do not see it when you view the content of an ACL. If the ACL is used for traffic filtering the implicit deny blocks all traffic. Because of this implicit deny, an ACL that does not have at least one permit statement will deny all traffic.
比對過程會持續進行,直到清單結尾。若找不到符合的項目,該封包就會依拒絕動作處理並被丟棄。ACL 的最後一條陳述式永遠是隱含拒絕(implicit deny)。這條陳述式會自動加入每個 ACL 的結尾,即使你在檢視 ACL 內容時看不到它。若該 ACL 用於流量過濾,隱含拒絕會封鎖所有流量。正因為有這條隱含拒絕,沒有至少一條允許陳述式的 ACL 會拒絕所有流量。
The processing of ACL in traffic filtering is displayed in the figure.
圖中顯示了 ACL 在流量過濾中的處理方式。