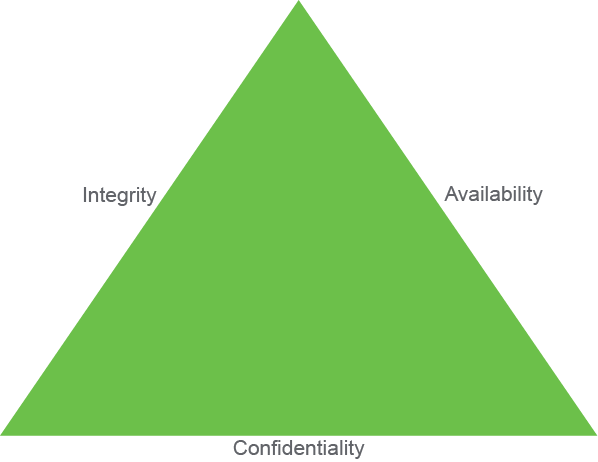
To provide adequate protection of networked resources, the procedures and technologies that you deploy must guarantee three things:
為了對網路資源提供足夠的保護,你所部署的程序與技術必須確保以下三件事:
- Confidentiality:Providing confidentiality of data guarantees that only authorized users can view sensitive information.機密性:提供資料的機密性可確保只有經授權的使用者能檢視敏感資訊。
- Integrity:Providing integrity of data guarantees that only authorized users can change sensitive information. Integrity might also guarantee the authenticity of data.完整性:提供資料的完整性可確保只有經授權的使用者能變更敏感資訊。完整性也可能確保資料的真實性。
- System and data availability:Providing system and data availability guarantees uninterrupted access by authorized users to important computing resources and data.系統與資料可用性:提供系統與資料的可用性,可確保經授權的使用者能不間斷地存取重要的運算資源與資料。
When designing network security, a designer must be aware of the following:
在設計網路安全時,設計者必須留意以下事項:
- The threats (possible attacks) that could compromise security可能危及安全性的威脅(可能發生的攻擊)
- The associated risks of the threats—that is, how relevant those threats are for a particular system威脅所帶來的相關風險,也就是這些威脅對特定系統而言的相關程度
- The cost to implement the proper security countermeasures for a threat為某項威脅實作適當安全對策所需的成本
- The need to perform a cost-benefit analysis to determine if it is worthwhile to implement security countermeasures執行成本效益分析以判斷是否值得實作安全對策的必要性
Security Awareness
安全意識
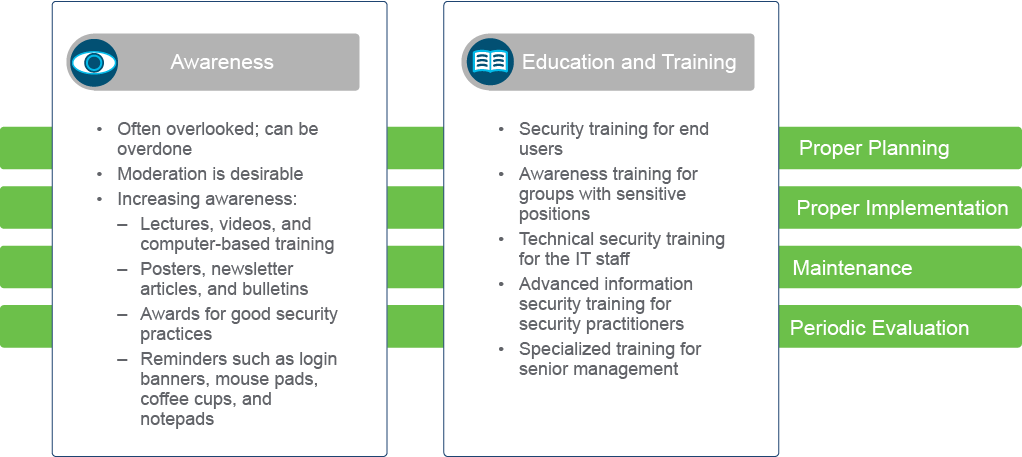
In order to get non-IT staff to think about information security, an organization must regularly attempt to remind staff members about security. Members of the technical staff also need regular reminders, because their jobs tend to emphasize performance rather than secure performance. Therefore, leadership must develop a nonintrusive program that keeps everyone aware of security and how to work together to maintain the security of their data. The three primary components that are used to implement this type of program are awareness, training, and education. As illustrated in the figure below, an effective computer security awareness and training program requires proper planning, implementation, maintenance, and periodic evaluation.
為了讓非 IT 人員也能思考資訊安全,組織必須定期提醒員工留意安全議題。技術人員同樣需要定期提醒,因為他們的工作往往著重於效能而非安全的效能。因此,領導階層必須制定一套不會造成過度干擾的計畫,讓每個人都能持續留意安全,並了解如何共同合作以維護資料安全。實作這類計畫所使用的三個主要元素為:意識、訓練與教育。如下圖所示,一套有效的電腦安全意識與訓練計畫,需要適當的規劃、實作、維護,以及定期評估。
In general, a computer security awareness and training program should encompass the following seven steps:
一般而言,一套電腦安全意識與訓練計畫應涵蓋以下七個步驟:
- Identify program scope, goals, and objectives: The scope of the program should provide training to all of the types of people who interact with IT systems. Because users need training that relates directly to their use of particular systems, you need to supplement a large organizationwide program with more system-specific programs.界定計畫範疇、目標與宗旨:計畫的範疇應涵蓋對所有與 IT 系統互動的人員提供訓練。由於使用者需要與其所使用之特定系統直接相關的訓練,你需要以更具系統針對性的計畫,來補充涵蓋整個組織的大型計畫。
- Identify training staff: It is important that trainers have sufficient knowledge of computer security issues, principles, and techniques. It is also vital that they know how to communicate information and ideas effectively.確認訓練人員:訓練人員必須具備足夠的電腦安全議題、原則與技巧相關知識,這點非常重要;他們也必須懂得如何有效地溝通資訊與想法,這同樣至關重要。
- Identify target audiences: Not everyone needs the same degree or type of computer security information to do their jobs. A computer security awareness and training program that distinguishes between groups of people and presents only the information that is needed by that particular audience, omitting irrelevant information, will obtain the best results.確認目標對象:並非每個人執行其工作所需要的電腦安全資訊程度或類型都相同。若一套電腦安全意識與訓練計畫能區分不同的族群,只呈現該特定對象所需的資訊,省略無關的內容,將能獲得最佳效果。
- Motivate management and employees: To successfully implement an awareness and training program, it is important to gain the support of management and employees. Consider using motivational techniques to show management and employees how their participation in a computer security and awareness program benefits the organization.激勵管理階層與員工:要成功實施一套意識與訓練計畫,取得管理階層與員工的支持非常重要。可以考慮使用激勵技巧,向管理階層與員工展示他們參與電腦安全與意識計畫,將如何為組織帶來益處。
- Administer the program: Several important considerations for administering the program include visibility, selection of appropriate training methods, topics, materials, and presentation techniques.執行計畫:執行計畫時,有幾項重要考量,包括計畫的能見度、適當訓練方法的選擇、主題、教材,以及呈現技巧。
- Maintain the program: The organization should make an effort to keep current with changes in computer technology and security requirements. A training program that meets the needs of an organization today might become ineffective when the organization starts to use a new application or changes its environment,維持計畫:組織應努力隨時掌握電腦技術與安全需求的變化。一套目前能滿足組織需求的訓練計畫,可能會在組織開始使用新應用程式或改變其環境時變得失效。
- Evaluate the program: An evaluation should attempt to ascertain how much information is retained, to what extent computer security procedures are being followed, and general attitudes toward computer security.評估計畫:評估應嘗試釐清員工記住了多少資訊、電腦安全程序被遵循的程度,以及員工對電腦安全的整體態度。