The evolution of phishing provides a good example of how attacks morph over time. The original concept of phishing (sending an email and enticing users to click a link to a malicious website) was clever, and it remains effective. It is easy to send huge numbers of emails. Obtaining a fraction of a percent of positive responses is significant. However, more sophisticated forms of phishing have evolved.
網路釣魚的演變過程,正好說明了攻擊手法會如何隨著時間而變化。網路釣魚最初的概念(傳送電子郵件誘騙使用者點擊連結前往惡意網站)相當巧妙,而且至今依然有效。大量寄送電子郵件並不困難,只要能得到一小部分的正面回應,就已經很有意義。然而,更為精密的網路釣魚形式也隨之演變出現。
- Spear phishing: Emails are sent to smaller, more targeted groups. Spear phishing may even target a single individual. Knowing more about the target community allows the attacker to craft an email that is more likely to deceive the target successfully. For example, an attacker sends an email with the source address of the human resources department to the employees.魚叉式網路釣魚(Spear phishing):電子郵件會寄給範圍較小、鎖定更精準的群體,甚至可能只鎖定單一個人。攻擊者對目標群體了解得越多,就越能設計出更容易騙過目標的電子郵件。舉例來說,攻擊者可能會以人力資源部門的來源位址,寄送電子郵件給員工。
- Whaling: Like spear phishing, whaling uses the concept of targeted emails; however, it targets a high-profile target. The target of a whaling attack is often one or more of the top executives of an organization. The whaling email content is designed to get an executive's attention, such as a subpoena request or a complaint from an important customer.捕鯨式攻擊(Whaling):與魚叉式網路釣魚類似,捕鯨式攻擊同樣運用鎖定式電子郵件的概念,但目標鎖定在知名度高的對象。捕鯨式攻擊的目標通常是組織中的一位或多位高階主管。捕鯨式電子郵件的內容經過設計,目的是吸引高階主管的注意,例如假冒的傳票請求,或來自重要客戶的投訴。
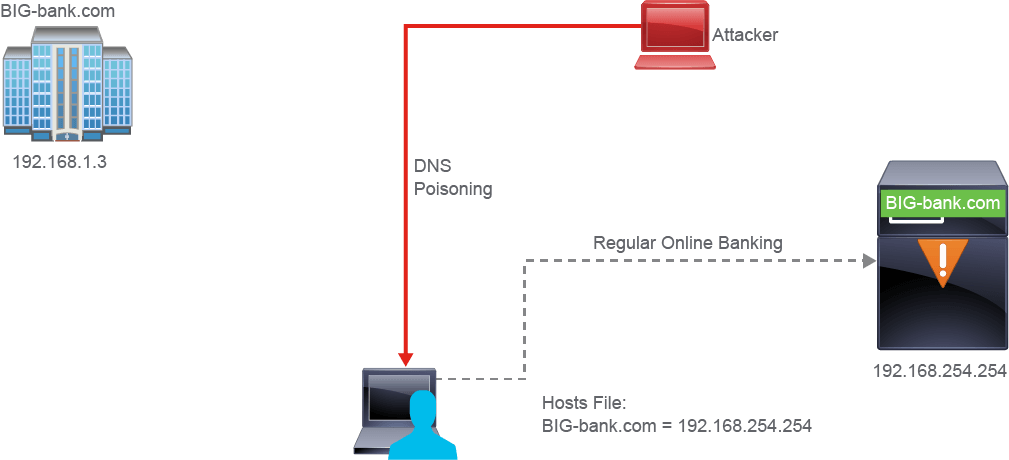
- Pharming: Whereas phishing entices the victim to a malicious website, pharming lures victims by compromising name services. Pharming can be done by injecting entries into localhost files or by poisoning the DNS in some fashion. When victims attempt to visit a legitimate website, the name service instead provides the IP address of a malicious website. In the following figure, an attacker has injected an erroneous entry into the host file on the victim system. As a result, when the victims attempt to do online banking with BIG-bank.com, they are directed to the address of a malicious website instead. Pharming can be implemented in other ways. For example, the attacker may compromise legitimate DNS servers. Another possibility is for the attacker to compromise a DHCP server, causing the DHCP server to specify a rogue DNS server to the DHCP clients. Consumer-market routers acting as DHCP servers for residential networks are prime targets for this form of pharming attack.域欺(Pharming):網路釣魚是誘使受害者前往惡意網站,域欺則是透過破壞名稱解析服務來誘騙受害者。域欺可以藉由在本地端主機檔案中植入項目,或以某種方式對 DNS 下毒來達成。當受害者嘗試造訪合法網站時,名稱解析服務會回傳一個惡意網站的 IP 位址。下圖中,攻擊者已在受害系統的主機檔案中植入一筆錯誤項目,結果當受害者嘗試連上 BIG-bank.com 進行網路銀行交易時,卻被導向一個惡意網站的位址。域欺也可以透過其他方式實現,例如攻擊者可能入侵合法的 DNS 伺服器;另一種可能性是攻擊者入侵 DHCP 伺服器,使其向 DHCP 用戶端指定一台流氓 DNS 伺服器。作為住宅網路 DHCP 伺服器的消費級路由器,正是這種域欺攻擊的絕佳目標。
- Watering hole: A watering hole attack uses a compromised web server to target select groups. The first step of a watering hole attack is determining the websites that the target group visits regularly. The second step is to compromise one or more of those websites. The attacker compromises the websites by infecting them with malware that can identify members of the target group. Only members of the target group are attacked. Other traffic is undisturbed. It makes it difficult to recognize watering holes by analyzing web traffic. Most traffic from the infected website is benign.水坑攻擊(Watering hole):水坑攻擊會利用遭入侵的網頁伺服器來鎖定特定群體。水坑攻擊的第一步是判斷目標群體經常造訪哪些網站;第二步則是入侵其中一個或多個網站。攻擊者會以能識別目標群體成員的惡意程式感染這些網站,只有目標群體的成員會遭到攻擊,其他流量則不受影響,這使得單靠分析網頁流量很難察覺水坑攻擊的存在,因為來自受感染網站的大多數流量看起來都很正常。
- Vishing: Vishing uses the same concept as phishing, except that it uses voice and the phone system as its medium instead of email. For example, a visher may call a victim claiming that the victim is delinquent in loan payments and attempt to collect personal information such as the victim's social security number or credit card information.語音釣魚(Vishing):語音釣魚採用與網路釣魚相同的概念,只不過它以語音與電話系統作為媒介,而非電子郵件。舉例來說,語音釣魚者可能致電受害者,聲稱受害者的貸款繳款已逾期,藉此設法取得受害者的社會安全號碼或信用卡資訊等個人資訊。
- Smishing: Smishing uses the same concept as phishing, except that it uses Short Message Service (SMS) texting as the medium instead of email.簡訊釣魚(Smishing):簡訊釣魚採用與網路釣魚相同的概念,只不過它是以簡訊服務(SMS)作為媒介,而非電子郵件。
Which type of attack uses directed phone calls to employees to obtain relevant information?哪一種攻擊會透過對員工進行有針對性的電話聯繫,來取得相關資訊?