Social engineering is the process of manipulating people to capitalize on expected behaviors. Social engineering often involves utilizing social skills, relationships, or understanding of cultural norms to manipulate people inside a network to provide the information that is needed to access the network. The following are examples of social engineering:
社交工程是一種操縱人們、利用其預期行為的過程。社交工程通常會運用社交技巧、人際關係,或對文化規範的理解,來操縱網路內的人員,使其提供存取網路所需的資訊。以下是社交工程的一些範例:
- Calling users on the phone claiming to be IT and convincing them that they need to set their passwords to particular values in preparation for the server upgrade that will take place tonight.打電話給使用者,謊稱自己是 IT 人員,並說服對方為了今晚即將進行的伺服器升級,需要把密碼設成特定的值。
- An individual without a badge following a badged user into a badge-secured area (tailgating).沒有識別證的人尾隨已刷卡的使用者,跟著進入以識別證管制的區域(尾隨闖入)。
- Sending an infected USB key along with book or magazine samples.隨書籍或雜誌樣本一起寄送已感染惡意程式的 USB 隨身碟。
- Developing fictitious personalities on social networking sites to obtain and abuse "friend" status.在社交網站上打造虛構的人物身分,藉此取得並濫用「好友」身分。
- Sending an email enticing a user to click a link to a malicious website (this is called phishing).傳送電子郵件,誘騙使用者點擊連結前往惡意網站(這稱為網路釣魚)。
- Visual hacking, where the attacker physically observes the victim entering credentials (such as a workstation login, a bank machine PIN, or the combination on a physical lock).視覺型駭客攻擊,攻擊者親自在現場觀察受害者輸入憑證(例如工作站登入資訊、提款機密碼,或實體鎖的號碼組合)。
Phishing is a common social engineering technique. Typically, a phishing email pretends to be from a large, legitimate organization, as in the figure.
網路釣魚是一種常見的社交工程手法。典型的網路釣魚電子郵件會假冒來自某個大型合法組織,如下圖所示。
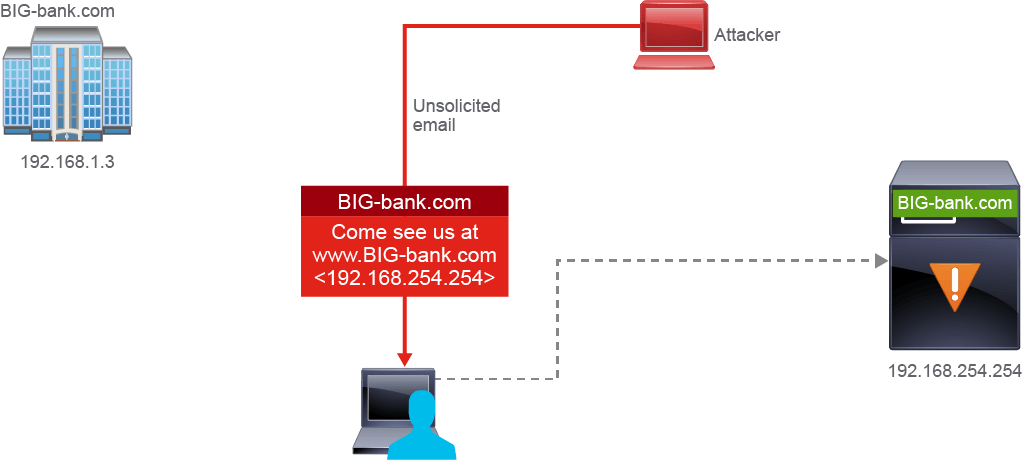
Since the organization from which the phishing email appears to originate is legitimate, the target may have a real account with the organization. The malicious website generally resembles that of the real organization. The goal is to get the victim to enter personal information such as account numbers, social security numbers, usernames, or passwords.
由於網路釣魚電子郵件看似來自的組織是合法的,目標對象可能確實在該組織擁有帳戶。惡意網站通常會做得與真正的組織網站十分相似。其目的是誘使受害者輸入個人資訊,例如帳號、社會安全號碼、使用者名稱或密碼。
Sometimes it is hard to recognize a phishing attack. Can you protect yourself and your company from phishing attacks? Learn more on the following link:
有時候很難辨識出網路釣魚攻擊。你能保護自己與公司免受網路釣魚攻擊嗎?請透過以下連結進一步了解:
Social engineering is a serious threat and may lead to other types of attacks, and therefore organizations should take measures to mitigate the risk from these types of attacks. Hence, an organization should raise user awareness and educate employees to defend against social engineering deceptions that threaten organizational security, conduct training sessions on this subject regularly, ensure that social engineering attackers find it difficult to breach physical security in the organization, and so on.
社交工程是一項嚴重的威脅,可能引發其他類型的攻擊,因此組織應採取措施緩解這類攻擊的風險。組織應提升使用者的意識,教育員工防範威脅組織安全的社交工程手法,定期針對此主題進行訓練,並確保社交工程攻擊者難以突破組織的實體安全,諸如此類。