Introduction
簡介
Imagine you are a network engineer working at a large healthcare company’s IT desk where network security is paramount. The sensitive nature of the data handled, such as patient records and medical information, makes security a top priority. Your colleagues, Alex and Maria, have submitted tickets regarding network issues. Alex needs to restrict access to the patient database so that only authorized healthcare professionals can retrieve patient records, while Maria wants to ensure that communications between the administrative and clinical departments are secure to prevent any unauthorized access or data leaks.
想像你是一家大型醫療保健公司資訊部門的網路工程師,網路安全在這裡至關重要。由於處理的資料性質敏感,例如病患病歷與醫療資訊,安全性是最優先的考量。你的同事 Alex 與 Maria 提交了與網路問題有關的工單。Alex 需要限制對病患資料庫的存取,使只有經授權的醫療專業人員才能取得病患病歷;而 Maria 則希望確保行政部門與臨床部門之間的通訊安全,以防止任何未經授權的存取或資料外洩。
You realize that:
你發現:
- Your company's network is complex and it handles sensitive information that needs to be protected.貴公司的網路相當複雜,且處理著需要受到保護的敏感資訊。
- Access to various resources must be controlled to ensure that only authorized users can access critical systems.必須控管對各種資源的存取,以確保只有經授權的使用者才能存取關鍵系統。
- The current network setup lacks granular control over who can access what, leading to potential security vulnerabilities.目前的網路架構缺乏精細的存取控制,可能導致安全漏洞。
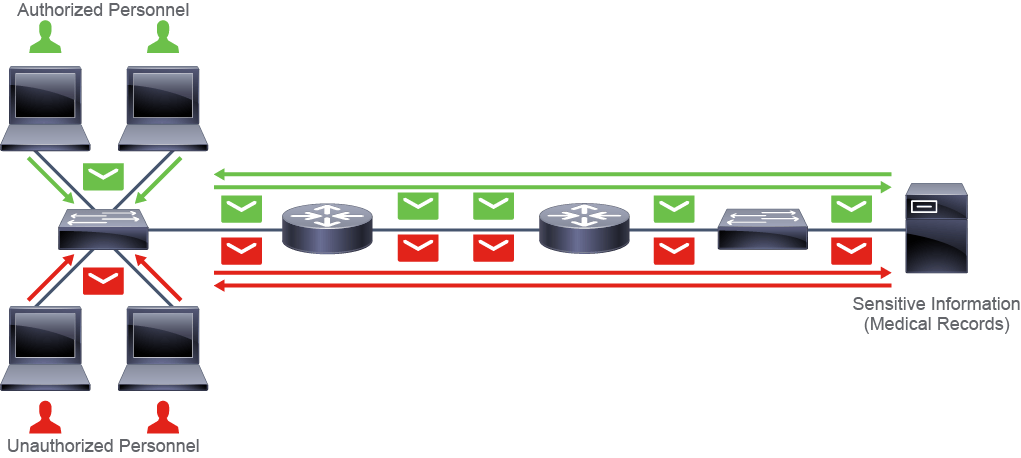
The existing network configuration does not provide specific access controls, leading to possible security risks.
現有的網路設定並未提供明確的存取控制,可能導致安全風險。
 | How do you think you could restrict access for unauthorized users while also allowing secure communications for authorized employees? 你認為該如何限制未經授權的使用者存取,同時又能讓經授權的員工進行安全通訊? |
To address these concerns, network engineers need to implement security measures that control communication between different segments within the company network. Access control lists (ACLs) can provide a solution by controlling which users can connect to specific devices based on their network address. ACLs also filter and manage traffic between different departments, ensuring that only necessary communications are allowed while blocking any unauthorized attempts.
為解決這些問題,網路工程師需要實施安全措施,控管公司網路中不同區段之間的通訊。存取控制清單(ACL)可以根據網路位址控制哪些使用者能連線到特定裝置,藉此提供解決方案。ACL 也能過濾與管理不同部門之間的流量,確保只允許必要的通訊,同時封鎖任何未經授權的嘗試。
In this course, you will learn:
在本課程中,你將學到:
- How ACLs operate and their various uses.ACL 的運作方式及其各種用途。
- The importance of using appropriate wildcard masks when implementing an ACL.在實作 ACL 時使用適當萬用字元遮罩的重要性。
- Different types of ACLs and their specific applications.不同類型的 ACL 及其特定應用。
- How to configure and verify different types of basic ACLs.如何設定與驗證不同類型的基本 ACL。
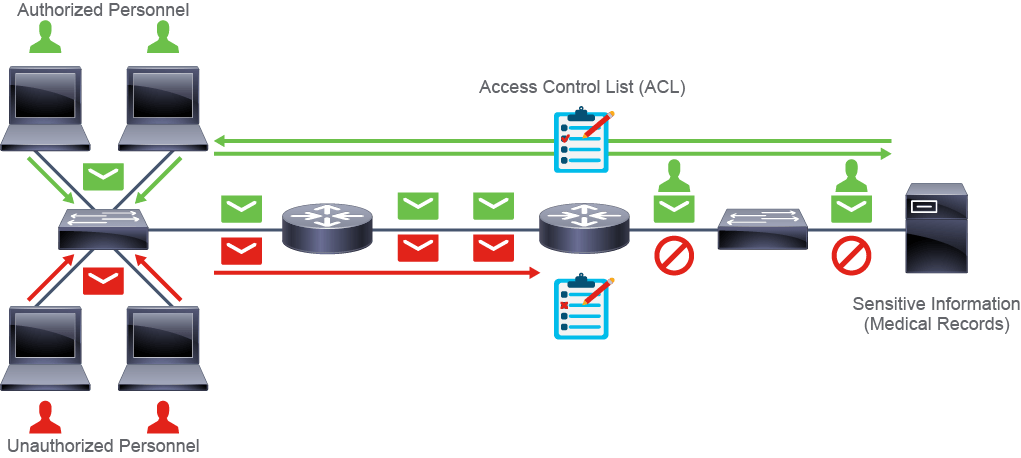
Inside a corporate network, where firewalls do not tend to operate, devices such as routers and multilayer switches can provide basic traffic filtering capabilities and restrictions using ACLs.
在企業網路內部,防火牆通常不會在此運作,路由器與多層交換器等裝置可以透過 ACL 提供基本的流量過濾能力與限制。