The end device connected to the switch has no knowledge of a configured VLAN on the switch. The configuration is only performed on the switch port. The end device has an IP address and subnet mask that associates it with a subnet. This subnet then maps to the VLAN that is configured on the switch port to which the end device is connected.
連接到交換器的終端裝置並不知道交換器上設定了哪個 VLAN。這項設定只在交換器連接埠上進行。終端裝置有一個 IP 位址與子網路遮罩,用來將它與某個子網路建立關聯。這個子網路接著會對應到該終端裝置所連接之交換器連接埠上設定的 VLAN。
The commands that define the VLAN port membership mode and characteristics are the following:
用來定義 VLAN 連接埠成員模式與特性的指令如下:
Command and Variable 指令與變數 | Membership Mode 成員模式 | VLAN Membership Characteristics VLAN 成員特性 |
switchport mode accessswitchport mode access | Static-access 靜態存取(Static-access) | A static-access port can belong to one VLAN and is manually assigned to that VLAN. 靜態存取埠只能屬於一個 VLAN,並手動指派給該 VLAN。 |
switchport mode trunkswitchport mode trunk | Trunk (IEEE 802.1Q) 中繼(Trunk,IEEE 802.1Q) | A trunk port is a member of all VLANs by default, including extended-range VLANs, but membership can be limited by configuring the allowed-VLAN list. 中繼埠預設為所有 VLAN 的成員,包含延伸範圍 VLAN,但可透過設定允許的 VLAN 清單來限制其成員資格。 |
switchport voice vlan vlan-idswitchport voice vlan vlan-id | Voice VLAN 語音 VLAN | A voice VLAN port is an access port attached to a Cisco IP Phone, configured to use one VLAN for voice traffic and another VLAN for data traffic from a device attached to the phone. 語音 VLAN 連接埠是連接到 Cisco IP 電話的存取埠,設定使用一個 VLAN 傳送語音流量,另一個 VLAN 傳送連接到該電話之裝置的資料流量。 |
Assigning a Port to a Data VLAN
將連接埠指派給資料 VLAN
When you connect a host to a switch port, you should associate the port with a VLAN in accordance with the network design and the subnet that it belongs to. To associate a device with a VLAN, assign the switch port to which the device connects to a single VLAN. The switch port, therefore, becomes an access port.
當你將主機連接到交換器連接埠時,應依照網路設計以及該連接埠所屬的子網路,將連接埠與 VLAN 建立關聯。若要將裝置與 VLAN 建立關聯,須將裝置所連接的交換器連接埠指派給單一 VLAN。此交換器連接埠因此成為存取埠。
After creating a VLAN, you can manually assign a port or many ports to this VLAN. A port can belong to only one data VLAN at a time.
建立 VLAN 之後,你可以手動將一個或多個連接埠指派給該 VLAN。一個連接埠一次只能屬於一個資料 VLAN。
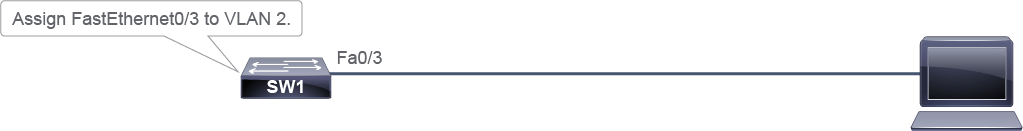
The following example shows how you can assign the previously created VLAN 2 to the FastEthernet0/3 interface.
以下範例說明如何將先前建立的 VLAN 2 指派給 FastEthernet0/3 介面。
SW1# configure terminal
SW1(config)# interface FastEthernet 0/3SW1(config-if)# switchport mode access
SW1(config-if)# switchport access vlan 2The table lists the commands to use when assigning a port to a VLAN.
下表列出將連接埠指派給 VLAN 時使用的指令。
Command and Variable 指令與變數 | Description 說明 |
interface interfaceinterface interface | Enters the interface configuration mode. 進入介面設定模式。 |
switchport mode accessswitchport mode access | Sets the interface to access mode. 將介面設為存取模式。 |
switchport access vlan vlan_numberswitchport access vlan vlan_number | Assigns the single VLAN to the interface. To reset the VLAN to the default VLAN, use the no form of this command. 將單一 VLAN 指派給該介面。若要將 VLAN 重設為預設 VLAN,請使用此指令的 no 形式。 |
The following example shows how you use the interface range global configuration command to enable FastEthernet interfaces 0/1 to 0/3 and assign them to VLAN 2:
以下範例說明如何使用全域設定指令 interface range 啟用 FastEthernet 介面 0/1 到 0/3,並將它們指派給 VLAN 2:
SwitchX# configure terminal
SwitchX# interface range FastEthernet0/1 - 3
SwitchX(config-if-range)# no shutdown
SwitchX(config-if-range)#
*Oct  6 08:24:35: %LINK-3-UPDOWN: Interface FastEthernet0/1, changed state to up
*Oct  6 08:24:35: %LINK-3-UPDOWN: Interface FastEthernet0/2, changed state to up
*Oct  6 08:24:35: %LINK-3-UPDOWN: Interface FastEthernet0/3, changed state to up
*Oct  6 08:24:36: %LINEPROTO-5-UPDOWN: Line protocol on Interface FastEthernet0/2, changed state to up
*Oct  6 08:24:36: %LINEPROTO-5-UPDOWN: Line protocol on Interface FastEthernet0/3, changed state to up
*Oct  6 08:24:36: %LINEPROTO-5-UPDOWN: Line protocol on Interface FastEthernet0/1, changed state to up
SwitchX(config-if-range)# switchport mode access
SwitchX(config-if-range)# switchport access vlan 2The following example shows how you use the default interface global configuration command to set the interface to factory defaults:
以下範例說明如何使用全域設定指令 default interface 將介面重設為出廠預設值:
SwitchX(config)# default interface FastEthernet0/2
Interface FastEthernet0/2 set to default configuration
The table lists the commands to use when configuring a range of interfaces as well as to set the interface to factory defaults.
下表列出設定多個介面範圍,以及將介面重設為出廠預設值時使用的指令。
Command and Variable 指令與變數 | Description 說明 |
interface range interfacesinterface range interfaces | Enables you to configure multiple ports at the same time. 可讓你同時設定多個連接埠。 |
default interface interfacedefault interface interface | Removes all settings from an interface, including VLAN association and membership mode. 移除介面上的所有設定,包括 VLAN 關聯與成員模式。 |
Assigning a Port to a Voice VLAN
將連接埠指派給語音 VLAN
Usually, IP phones are placed next to a computer in the working environment. They use Ethernet and require the same network cables as computers. Hence, you can use two separate connections to the network, the computer and the IP phone.
通常,IP 電話會擺放在工作環境中電腦旁邊。它們使用乙太網路,並需要與電腦相同的網路線。因此,你可以使用兩條分開的連線連接到網路,分別給電腦與 IP 電話使用。
Alternatively, you can connect the computer to an Ethernet port on the IP phone, and then the connection from the IP phone to the network carries the traffic from both the computer and the IP phone. This is enabled on some Cisco Catalyst switches with a unique feature that is called voice VLAN; it lets you overlay a voice topology onto a data network. You can segment phones into separate logical networks, even though the data and voice infrastructure are physically the same.
另一種方式是,你可以將電腦連接到 IP 電話上的乙太網路連接埠,接著由 IP 電話到網路的連線同時承載電腦與 IP 電話的流量。某些 Cisco Catalyst 交換器上有一項獨特功能可支援此作法,稱為語音 VLAN;它讓你可以在資料網路上疊加語音拓樸。即使資料與語音基礎架構在實體上是相同的,你也可以將電話分割到不同的邏輯網路中。
With the IP phones in their own VLANs, network administrators can more easily identify and troubleshoot network problems. Also, network administrators have the ability to prioritize voice traffic over data traffic.
將 IP 電話置於自己的 VLAN 中後,網路管理員可以更輕鬆地識別並排除網路問題。此外,網路管理員也能夠將語音流量的優先權設定得高於資料流量。
The voice VLAN feature allows voice traffic from the attached IP phone and data traffic from an end station to be transmitted on different VLANs.
語音 VLAN 功能可讓來自連接之 IP 電話的語音流量,以及來自終端站的資料流量,在不同的 VLAN 上傳送。
You create a voice VLAN in the same way as you create data VLAN, using the vlan global configuration command. The following example shows how to create VLAN 3 and how to assign this VLAN as a voice VLAN to the FastEthernet0/2 interface.
你建立語音 VLAN 的方式與建立資料 VLAN 相同,都是使用 vlan 全域設定指令。以下範例說明如何建立 VLAN 3,並將此 VLAN 指派為 FastEthernet0/2 介面的語音 VLAN。

- Add VLAN 3 and name it "telephony".新增 VLAN 3 並將其命名為「telephony」。
SW1# configure terminal SW1(config)# vlan 3 SW1(config-vlan)# name telephony - Assign interface FastEthernet0/2 to voice VLAN 3 and data VLAN 2.將介面 FastEthernet0/2 指派給語音 VLAN 3 與資料 VLAN 2。
SW1# configure terminal
SW1(config)# interface FastEthernet0/2SW1(config-if)# switchport mode accessSW1(config-if)# switchport voice vlan 3
SW1(config-if)# switchport access vlan 2
When an IP phone is connected to a switch port, this port should have a voice VLAN associated with it. This process is done by assigning a single voice VLAN to the switch port to which the phone is connected. The previous example shows a data and voice VLAN configured on the same interface.
當 IP 電話連接到交換器連接埠時,此連接埠應與一個語音 VLAN 建立關聯。此程序是透過將單一語音 VLAN 指派給該電話所連接的交換器連接埠來完成。前面的範例展示了在同一介面上同時設定資料 VLAN 與語音 VLAN。
Command 指令 | Description 說明 |
switchport mode accessswitchport mode access | Sets the interface to strict access mode. 將介面設為嚴格存取模式。 |
switchport voice vlanvlan-idswitchport voice vlanvlan-id | Set the voice VLAN to an interface. This action will instruct the Cisco IP phone to forward all voice traffic through the specified VLAN. 為介面設定語音 VLAN。此動作會指示 Cisco IP 電話將所有語音流量透過指定的 VLAN 轉送。 |
Verifying VLANs
驗證 VLAN
After you configure a VLAN, you should validate the parameters for that VLAN.
設定 VLAN 之後,你應該驗證該 VLAN 的參數。
Use the show vlan command to display information on all configured VLANs. The command displays configured VLANs, their names, and the ports on the switch that are assigned to each VLAN. You can observe in the output all information about the VLANs.
使用 show vlan 指令可顯示所有已設定 VLAN 的資訊。此指令會顯示已設定的 VLAN、其名稱,以及交換器上指派給各 VLAN 的連接埠。你可以在輸出中觀察到所有關於 VLAN 的資訊。
To display information on all configured VLANs:
若要顯示所有已設定 VLAN 的資訊:
SW1# show vlan

VLAN Name                             Status    Ports
---- -------------------------------- --------- -------------------------------
1    default                          active    Fa0/1, Fa0/4, Fa0/5, Fa0/6, Fa0/7
2    data                             active    Fa0/2, Fa0/3
3    telephony                        active    Fa0/2
1002 fddi-default                     act/unsup
1003 token-ring-default               act/unsup
1004 fddinet-default                  act/unsup
1005 trnet-default                    act/unsup

VLAN Type  SAID       MTU   Parent RingNo BridgeNo Stp  BrdgMode Trans1 Trans2
---- ----- ---------- ----- ------ ------ -------- ---- -------- ------ ------
1    enet  100001     1500  -      -      -        -    -        0      0
2    enet  100002     1500  -      -      -        -    -        0      0
3   enet  100003     1500  -      -      -        -    -        0      0
1002 fddi  101002     1500  -      -      -        -    -        0      0
1003 tr    101003     1500  -      -      -        -    -        0      0
1004 fdnet 101004     1500  -      -      -        ieee -        0      0
1005 trnet 101005     1500  -      -      -        ibm  -        0      0

Remote SPAN VLANs
------------------------------------------------------------------------------


Primary Secondary Type              Ports
------- --------- ----------------- ------------------------------------------
The example shows that VLAN 2 (data) and VLAN 3 (telephony) are created on the switch. Both are active and are assigned to the FastEthernet0/2. All other interfaces are assigned to the default VLAN—VLAN 1, except for FastEthernet0/3 since it was previously assigned to VLAN 2. Trunk ports that are connected to another device do not appear in the output of the show vlan command.
此範例顯示交換器上建立了 VLAN 2(data)與 VLAN 3(telephony)。兩者皆處於啟用狀態,並指派給 FastEthernet0/2。所有其他介面都指派給預設 VLAN,即 VLAN 1,但 FastEthernet0/3 除外,因為它先前已被指派給 VLAN 2。連接到其他裝置的中繼埠不會出現在 show vlan 指令的輸出中。
Use the show vlan id vlan_number or show vlan namevlan-name command to display information about a particular VLAN. The example shows the output of the show vlan command for the "data" VLAN, which is VLAN 2.
使用 show vlan id vlan_number 或 show vlan namevlan-name 指令可顯示特定 VLAN 的資訊。此範例顯示了「data」VLAN(即 VLAN 2)的 show vlan 指令輸出。
SW1# show vlan id 2

VLAN Name                 Status    Ports
---- -------------------- -------   ---------------------
2    data                active    Fa0/2, Fa0/3

VLAN Type SAID    MTU   Parent RingNo BridgeNo Stp  BrdgMode Trans1 Trans2
---- ---- ------- ----- ------ ------ -------- --- --------- ------ ------
2    enet 100002  1500  -      -      -        -    -        0      0

<... output omitted ...>
On the other hand, you can use the show vlan brief command, which displays one line for each VLAN with the VLAN name, status, and its ports. Connected trunk ports also do not appear in the output of the show vlan briefcommand.
另外,你也可以使用 show vlan brief 指令,此指令會為每個 VLAN 顯示一行,包含 VLAN 名稱、狀態及其連接埠。已連接的中繼埠同樣不會出現在 show vlan briefcommand 的輸出中。
SW1#  show vlan briefVLAN Name                             Status    Ports
---- -------------------------------- --------- -------------------------------
1    default                          active    Fa0/1, Fa0/4, Fa0/5, Fa0/6, Fa0/7
2    data                             active    Fa0/2, Fa0/3
3    telephony                        active    Fa0/2
1002 fddi-default                     act/unsup
1003 token-ring-default               act/unsup
1004 fddinet-default                  act/unsup
1005 trnet-default                    act/unsup
Dynamic Trunking Protocol (DTP) is used by Cisco switches to automatically negotiate whether an interface used for interconnection between two switches should be put into access or trunk mode. When the interface is in trunk mode, DTP also negotiates trunk encapsulation.
動態中繼協定(Dynamic Trunking Protocol,DTP)由 Cisco 交換器用來自動協商兩台交換器之間互連用的介面應設為存取模式或中繼模式。當介面處於中繼模式時,DTP 也會協商中繼封裝方式。
The DTP individual modes are:
DTP 的各個模式如下:
- dynamic auto: the interface will form a trunk only if it receives DTP messages to do so from the other side switch. An interface configured in dynamic auto mode does not generate DTP messages and only listens for incoming DTP messages.dynamic auto:介面只有在收到對端交換器發出要求形成中繼的 DTP 訊息時,才會形成中繼。設定為 dynamic auto 模式的介面不會產生 DTP 訊息,只會監聽傳入的 DTP 訊息。
- dynamic desirable: the interface will negotiate the mode automatically and will actively try to convert the link to a trunk link. An interface configured in dynamic desirable mode generates DTP messages and listens for incoming DTP messages. If the port on the other side switch interface is capable to form a trunk, a trunk link will be formed.dynamic desirable:介面會自動協商模式,並主動嘗試將此連結轉換為中繼連結。設定為 dynamic desirable 模式的介面會產生 DTP 訊息,並監聽傳入的 DTP 訊息。若對端交換器介面能夠形成中繼,則會建立中繼連結。
The individual combinations of interface settings on the switches lead to following results:
交換器上介面設定的各種組合會導致下列結果:
Interface mode on one side 一端的介面模式 | Interface mode on other side 另一端的介面模式 | Resulting operational mode 最終運作模式 |
dynamic auto dynamic auto | dynamic auto dynamic auto | access access |
dynamic auto dynamic auto | dynamic desirable dynamic desirable | trunk trunk |
dynamic desirable dynamic desirable | dynamic desirable dynamic desirable | trunk trunk |
dynamic auto or dynamic desirable dynamic auto 或 dynamic desirable | trunk trunk | trunk trunk |
dynamic auto or dynamic desirable dynamic auto 或 dynamic desirable | access access | access access |
access access | trunk trunk | limited connectivity 連線受限 |
trunk trunk | access access | limited connectivity 連線受限 |
The best practice is to disable the autonegotiation and not use the dynamic auto and dynamic desirable switch port modes. Instead, the best practice is to manually configure the port mode as trunk on both sides. If you do not want the switch to negotiate at all, use the switchport nonegotiate command (necessary only for trunk ports, as the static access ports do not send DTP packets automatically.)
最佳做法是停用自動協商,不要使用 dynamic auto 與 dynamic desirable 這兩種交換器連接埠模式。取而代之的最佳做法是在兩端都手動將連接埠模式設定為 trunk。若你完全不想讓交換器進行協商,可使用 switchport nonegotiate 指令(此指令僅在中繼埠上才需要,因為靜態存取埠本來就不會自動傳送 DTP 封包)。
Note the two modes in the output above: Administrative and Operational. These are related to what is negotiated with DTP. The Administrative mode provides you with information about the DTP mode configured on the specific interface. Operational mode provides you with information about what type of mode has been negotiated and is in use.
請注意上方輸出中的兩種模式:管理(Administrative)與運作(Operational)。這兩者都與 DTP 協商的內容相關。管理模式提供該特定介面上所設定的 DTP 模式資訊。運作模式則提供目前已協商並正在使用的模式類型資訊。
You can also use the show mac address-table command to verify which MAC addresses belong to which port and VLAN. You can also see the MAC addresses that have been learned on a particular VLAN with the show mac address-table vlan vlan-id command.
你也可以使用 show mac address-table 指令來驗證哪些 MAC 位址屬於哪個連接埠與 VLAN。你也可以使用 show mac address-table vlan vlan-id 指令查看特定 VLAN 上已學習到的 MAC 位址。
Switch# show mac address-table
          Mac Address Table
-------------------------------------------

Vlan    Mac Address       Type        Ports
----    -----------       --------    -----
   1    aabb.cc00.2f00    DYNAMIC     Fa0/0
   1    aabb.cc00.3100    DYNAMIC     Fa0/1
2 aabb.cc00.3000 DYNAMIC Fa0/2Each port on a switch belongs to a VLAN. If the VLAN to which the port belongs is deleted, the port becomes inactive. Also, a port becomes inactive if it is assigned to a nonexistent VLAN. All inactive ports are unable to communicate with the rest of the network.
交換器上的每個連接埠都屬於某個 VLAN。若該連接埠所屬的 VLAN 被刪除,該連接埠會變成非啟用狀態。此外,若連接埠被指派給一個不存在的 VLAN,該連接埠也會變成非啟用狀態。所有非啟用的連接埠皆無法與網路其餘部分通訊。
As shown in the following example, you can use the show interface interface switchport command to check whether the port is inactive. If the port is inactive, it will not be functional until you create the missing VLAN using the vlan vlan_id command or until you assign the port to a valid VLAN. In this case, VLAN 10 was deleted from the switch, causing the port to become inactive.
如以下範例所示,你可以使用 show interface interface switchport 指令來檢查連接埠是否處於非啟用狀態。若連接埠處於非啟用狀態,在你使用 vlan vlan_id 指令建立遺失的 VLAN,或將該連接埠指派給有效的 VLAN 之前,它將無法正常運作。在此例中,VLAN 10 已從交換器中刪除,導致該連接埠變成非啟用狀態。
Switch# show interfaces Ethernet0/1 switchport
Name: Et0/1
Switchport: Enabled
Administrative Mode: static access
Operational Mode: static access
Administrative Trunking Encapsulation: dot1q
Operational Trunking Encapsulation: native
Negotiation of Trunking: Off
Access Mode VLAN: 10 (Inactive)
Trunking Native Mode VLAN: 1 (default)
Administrative Native VLAN tagging: enabled
Voice VLAN: none