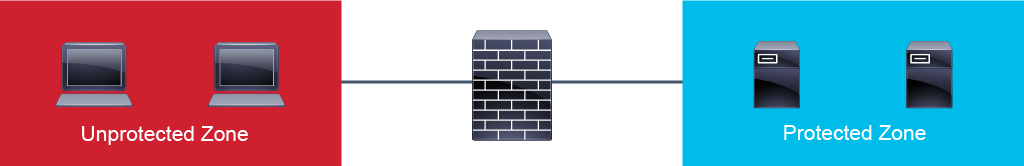
A firewall is a system that enforces an access control policy between two or more security zones. The figure below illustrates the concept.
防火牆(firewall)是在兩個或多個安全區域之間強制執行存取控制政策的系統。下圖說明此概念。
There are several types of firewalls, but all firewalls should have these properties:
防火牆有多種類型,但所有防火牆都應具備以下特性:
- The firewall itself must be resistant to attack—otherwise, it would allow an attacker to disable the firewall or change its access rules.防火牆本身必須能抵禦攻擊,否則攻擊者可能停用防火牆或變更其存取規則。
- All traffic between security domains must flow through the firewall. This requirement prevents a backdoor connection that could be used to bypass the firewall, violating the network access policy.安全網域之間的所有流量都必須通過防火牆。此要求可防止後門連線繞過防火牆,違反網路存取政策。
- A firewall must have traffic-filtering capabilities.防火牆必須具備流量過濾能力。
The simplest type of a firewall is a packet filter. As the name implies, packet filters look at individual packets in isolation. Based on the contents of the packet and the configured policy, they make a permit or deny decision. Packet filters generally have robust options for differentiating desirable and undesirable packets.
最簡單的防火牆類型是封包過濾器(packet filter)。顧名思義,封包過濾器單獨檢視每個封包。根據封包內容與所設定的政策,它會做出允許或拒絕的決定。封包過濾器通常具備強大的選項,可用來區分正常與異常封包。
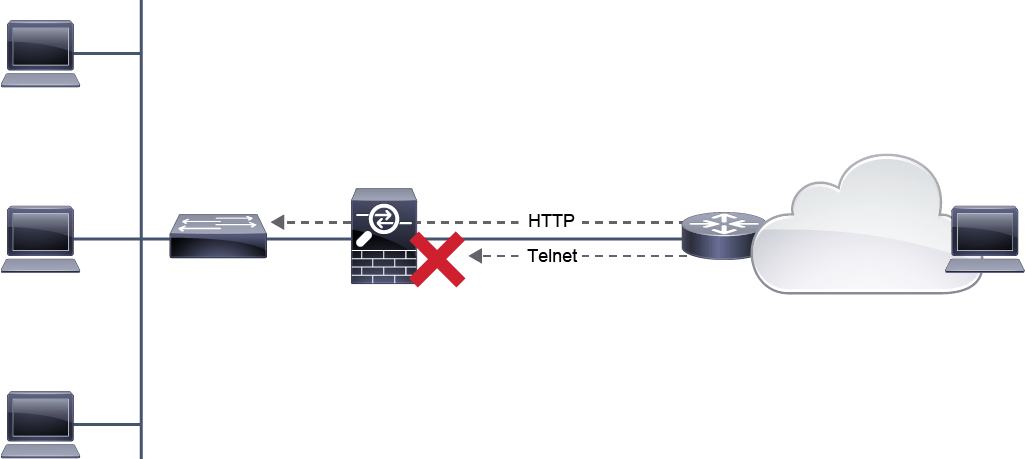
Firewalls commonly control access between the security zones that are based on the packet source and destination IP address and port. The figure below shows a firewall that permits HTTP traffic but denies Telnet traffic to a protected network. In this example, the device providing the firewalling services is a Cisco ASA adaptive security appliance (Cisco ASA)..
防火牆通常根據封包的來源與目的地 IP 位址及連接埠,控制安全區域之間的存取。下圖顯示一個防火牆允許 HTTP 流量、但拒絕 Telnet 流量進入受保護網路。在此範例中,提供防火牆服務的裝置是 Cisco ASA 調適型安全設備(Cisco ASA)。
Where a packet filter controls access on a packet-by-packet basis, stateful firewalls control access on a session-by-session basis. It is called stateful because the firewall is remembering the state of the session. By default, a stateful firewall does not allow any traffic from the outside into the secure inside network, except for reply traffic, because users from the secure inside network first initiated the traffic to the outside destination.
封包過濾器以逐一封包為單位控制存取,而具狀態防火牆(stateful firewall)則以逐一連線階段(session)為單位控制存取。之所以稱為「具狀態」,是因為防火牆會記住連線階段的狀態。預設情況下,具狀態防火牆不允許任何來自外部的流量進入安全的內部網路,唯一的例外是回覆流量,因為這是安全內部網路的使用者先發起連往外部目的地的流量。
A firewall can be a hardware appliance, a virtual appliance, or a software that runs on another device such as a router. Although firewalls can be placed in various locations within a network (including on endpoints), they are typically placed at least at the internet edge, where they provide vital security. Firewall threat controls should be implemented at least at the most exposed and critical parts of enterprise networks. The internet edge is the network infrastructure that provides connectivity to the internet and acts as the gateway for the enterprise to the rest of the cyberspace. Because it is a public-facing network infrastructure, it is particularly exposed to a large array of external threats.
防火牆可以是硬體設備、虛擬設備,或是在路由器等其他裝置上執行的軟體。雖然防火牆可以部署在網路中的各個位置(包括端點上),但通常至少會部署在網際網路邊界,提供關鍵的安全防護。防火牆的威脅防護至少應部署在企業網路中最暴露、最關鍵的部位。網際網路邊界是提供網際網路連線、並作為企業通往網路空間其他部分的閘道之網路基礎架構。由於它是面向公眾的網路基礎架構,因此特別容易暴露於大量的外部威脅之下。
Firewalls are also often used to protect data centers. The data center houses most of the critical applications and data for an enterprise. The data center is primarily inward facing and most clients are on the internal network. The intranet data center is still subject to external threats, but must also be guarded against threat sources inside the network perimeter.
防火牆也經常用來保護資料中心。資料中心存放企業大部分的關鍵應用程式與資料。資料中心主要是面向內部,大多數用戶端都位於內部網路。內部網路(intranet)資料中心仍然會受到外部威脅,但也必須防範來自網路邊界內部的威脅來源。
Many firewalls also provide a suite of additional services such as Network Address Translation (NAT) and multiple security zones. Another important service that is also frequently provided by firewalls is Virtual Private Network (VPN) termination.
許多防火牆還提供一套額外服務,例如網路位址轉換(NAT)與多個安全區域。防火牆經常提供的另一項重要服務是虛擬私人網路(VPN)終止。
Firewall products have evolved to meet the needs of borderless networks of today. From simple perimeter security with access control lists (ACLs), based on IP addresses and ports, firewalls have evolved to offer some advanced security services. The hard outer shell that firewalls provided in the past is now superseded by security capabilities that are integrated into the very fiber of the network to defend against multivector and persistent threats. Because of the current threat landscape, Cisco Secure Firewalls (formerly Cisco Next Generation Firewalls [NGFWs]) are needed.
防火牆產品已演進以因應現今無邊界網路的需求。從早期以 IP 位址與連接埠為基礎的存取控制清單(ACL)所構成的簡單邊界安全,防火牆已演進為提供一些進階安全服務。過去防火牆提供的堅硬外殼,如今已被整合到網路核心結構中的安全能力所取代,用以防禦多向量且持續存在的威脅。由於當前的威脅態勢,因此需要 Cisco Secure Firewall(前身為 Cisco 次世代防火牆[NGFW])。
In addition to the standard first-generation firewall capabilities, Cisco Secure Firewalls also have these capabilities:
除了標準第一代防火牆的能力外,Cisco Secure Firewall 還具備以下能力:
- Integrate security functions tightly to provide highly effective threat and advanced malware protection緊密整合安全功能,提供高效的威脅與進階惡意軟體防護
- Implement policies that are based on application visibility instead of transport protocols and ports根據應用程式可視性(而非傳輸協定與連接埠)實施政策
- Provide URL filtering and other controls over web traffic提供 URL 過濾及其他對網頁流量的控制
- Provide actionable indications of compromise to identify malware activity提供可採取行動的入侵指標(indication of compromise),以識別惡意軟體活動
- Offer comprehensive network visibility提供全面的網路可視性
- Help reduce complexity協助降低複雜度
- Integrate and interface smoothly with other security solutions與其他安全解決方案順暢地整合並互通