You can limit access to vty lines to specific IP addresses or subnets to control remote administration of network devices. Remote administration is commonly run over a Telnet or an SSH connection, where the SSH connection is an encrypted communication channel between the administrator workstation and the device.
你可以將 vty 線路的存取限制為特定的 IP 位址或子網路,以控制網路裝置的遠端管理。遠端管理通常透過 Telnet 或 SSH 連線進行,其中 SSH 連線是管理員工作站與裝置之間的加密通訊通道。
There are usually two steps that you must complete to limit remote access with ACLs:
使用 ACL 限制遠端存取通常需要完成兩個步驟:
- Configure an ACL:The following example shows a standard IPv4 numbered ACL, ACL 1, being configured with two lines. The first line permits addresses in the 10.1.1.0/24 subnet. The second line is not mandatory because there is an implicit deny statement at the end of every ACL. However, creating an explicit deny statement and appending the
logkeyword allows you to monitor attempts of unauthorized sources trying to access the device.設定 ACL:以下範例顯示一個標準 IPv4 編號 ACL(ACL 1),以兩行進行設定。第一行允許 10.1.1.0/24 子網路中的位址。第二行並非必要,因為每個 ACL 的結尾都隱含一條拒絕陳述式。不過,明確建立拒絕陳述式並加上log關鍵字,可讓你監控未授權來源嘗試存取裝置的情形。
Use an ACL to permit Telnet access from 10.1.1.0/24, but deny everyone else.
使用 ACL 允許來自 10.1.1.0/24 的 Telnet 存取,並拒絕其他所有來源。
Router(config)# access-list 1 permit 10.1.1.0 0.0.0.255
Router(config)# access-list 1 deny any log Router(config)# line vty 0 15Router(config-line)# access-class 1 in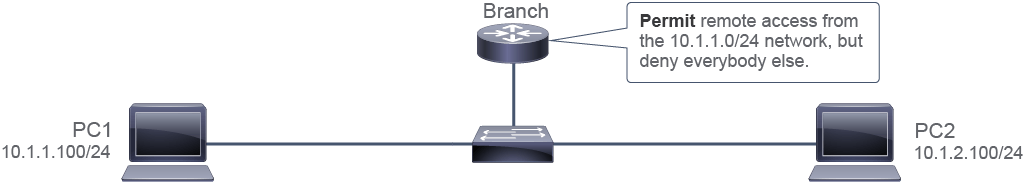
- Apply the ACL to the lines:The
access-classcommand applies the ACL on vty lines. Using theinkeyword after the name of the ACL tells the router to limit vty connections that are coming into the network device. It only allows Telnet connections from the addresses permitted by the ACL, in this case, devices on the 10.1.1.0/24 subnet.將 ACL 套用至線路:access-class指令會將 ACL 套用到 vty 線路上。在 ACL 名稱後使用in關鍵字,會告訴路由器限制進入該網路裝置的 vty 連線,僅允許 ACL 所允許位址(在此範例中為 10.1.1.0/24 子網路上的裝置)建立 Telnet 連線。
The example uses 16 vty lines (range 0 to 15). In the configuration output, it will appear in two vty line ranges, first from 0 to 4 and second from 5 to 15. If there is no need for more than five vty lines, you can configure only the first range.
此範例使用 16 條 vty 線路(範圍 0 到 15)。在設定輸出中,會分為兩個 vty 線路範圍呈現,第一個是 0 到 4,第二個是 5 到 15。如果不需要超過五條 vty 線路,你可以只設定第一個範圍。